
 Do Son
Samsung’s Galaxy S26 debuts a "multi-agent" AI world. Call "Hey Plex" for real-time web search as Samsung Notes and Gallery sync with Perplexity’s brain.

Google has suspended thousands of Antigravity accounts linked to OpenClaw. Paid developers are hitting 403 errors with zero warning. Is your AI workflow safe?

IceWarp urges immediate patching for critical flaws allowing unauthorized server access, XSS, and arbitrary file reading. Update your instances today.

Critical Undertow HTTP server flaw CVE-2025-12543 (CVSS 9.6) impacts HPE Telco Service Activator, allowing cache poisoning and session hijacking. Patch now.
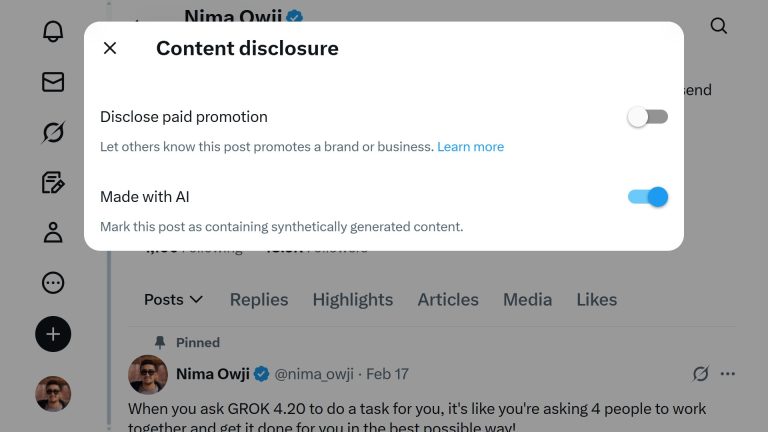
X is testing a new "AI-Generated" toggle for all posts. Fail to disclose synthetic content, and Community Notes could trigger a permanent account suspension.

Anthropic's Claude Code Security moves beyond pattern matching to "reason" through code, unearthing 500+ vulnerabilities missed by decades of human review.

Apple is testing a "Deep Red" finish for the iPhone 18 Pro to follow Cosmic Orange's success. Meanwhile, the iPhone Fold sticks to classic Black and White.
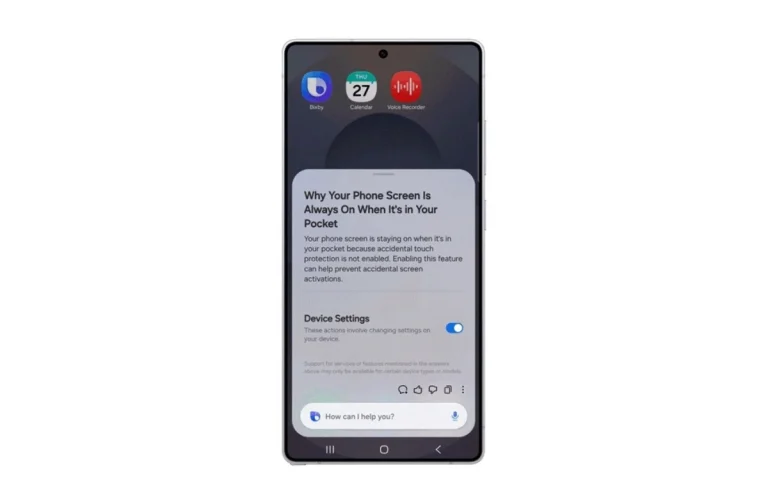
Bixby is back! The One UI 8.5 beta transforms Bixby into a Conversational Agent that understands natural language and controls your phone without menu-diving.

Jony Ive and OpenAI are building a camera-equipped smart speaker for 2027. Discover the $6.5B design deal bringing "Face ID" and visual AI into your home.

YouTube’s Gemini "Ask" feature hits smart TVs and consoles! Ask voice questions about recipes or lyrics without pausing. The passive TV era is officially over.
NVIDIA is playing the long game in India. By partnering with the $75M Activate fund, they are locking in the next generation of AI giants before they even exist.

Unit 42 warns of active attacks on critical BeyondTrust flaw CVE-2026-1731. Hackers bypass auth for RCE and data theft. Patch self-hosted instances now.

Critical path traversal flaws (CVE-2026-26065, CVE-2026-26064) in the Calibre e-book manager allow RCE via malicious PDB and ODT files. Update to 9.3.0.
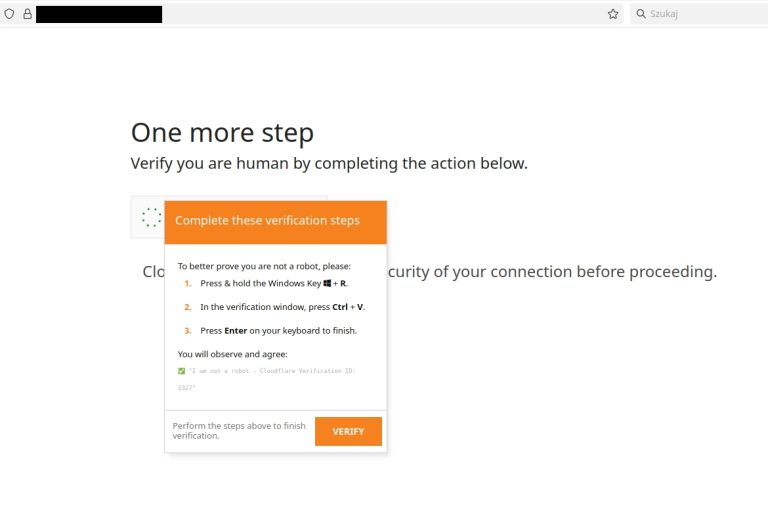
CERT Polska reveals how a fake "ClickFix" CAPTCHA campaign tricked users into deploying evasive Latrodectus and Supper malware. Protect your network now.
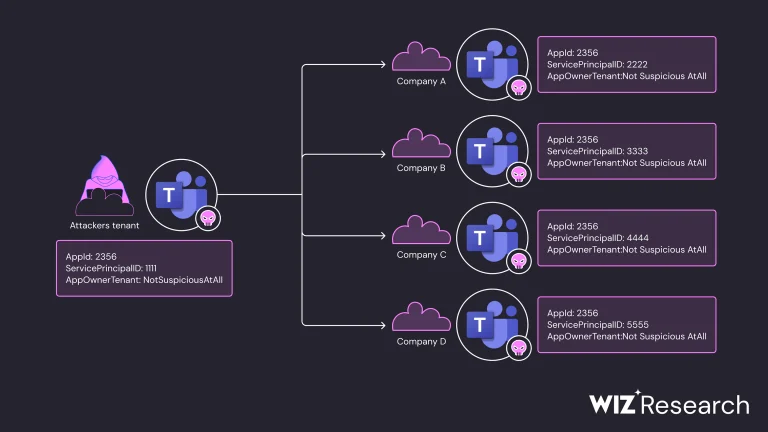
Wiz Research exposes a stealthy threat using malicious OAuth apps and Cyrillic homoglyphs to bypass Microsoft Entra ID security. Protect your cloud tenant.
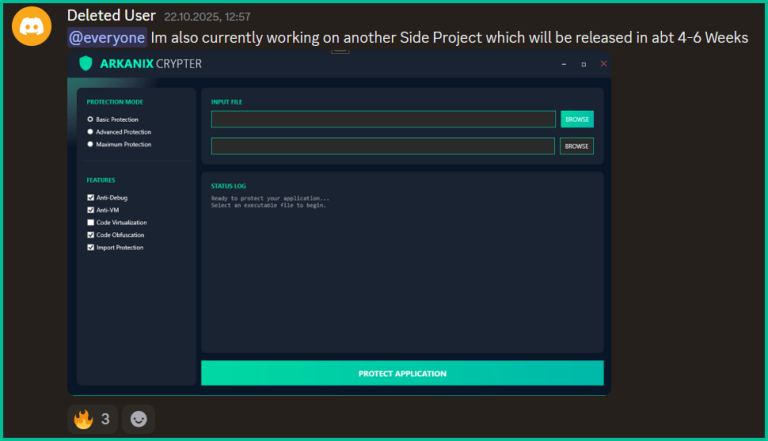
Kaspersky exposes Arkanix Stealer, a fast-moving MaaS operation leveraging Discord, tiered subscriptions, and AI-assisted development for quick data theft.
The FBI warns of a massive surge in ATM jackpotting attacks. Cybercriminals are using Ploutus malware to bypass the XFS layer and drain cash reserves.
Insikt Group exposes GrayCharlie compromising WordPress sites & US law firms. Attackers use "ClickFix" fake CAPTCHAs to deploy the NetSupport RAT.

A critical PDF Object Injection flaw (CVE-2026-25755) in jsPDF allows attackers to bypass AcroJS sandboxes. Update to version 4.2.0 immediately.
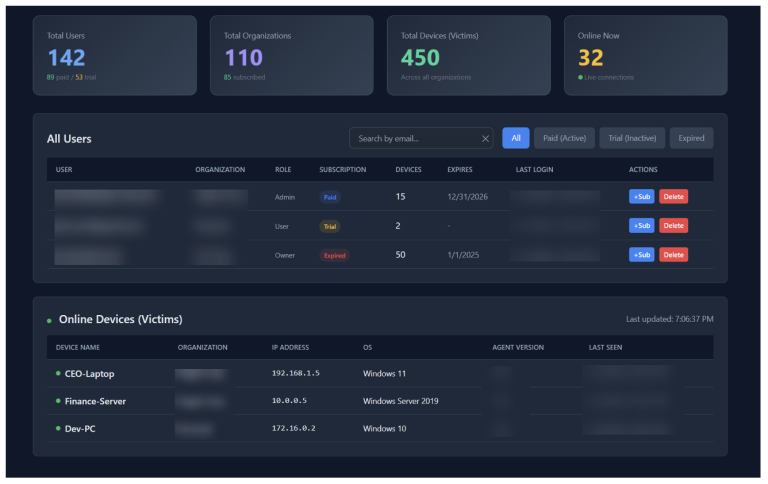
Proofpoint exposes TrustConnect, a new Malware-as-a-Service masquerading as an IT tool. The AI-assisted fake RMM software replaces dismantled threats.

A critical Windows Error Reporting flaw (CVE-2026-20817) allows local privilege escalation to SYSTEM. With the PoC publicly disclosed, update immediately.

Group-IB exposes an industrialized mobile banking fraud campaign in Indonesia. GoldFactory hackers use fake Coretax apps and Gigabud.RAT to drain accounts.