Skip to content
November 19, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • ADVISORIES
    • Microsoft
    • Fortinet
    • Ivanti
    • Cisco
    • Linux
    • Citrix
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q3 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Malware
  • Vulnerability News
  • Submit Press Release
Light/Dark Button
  • Home
  • News
  • Technology
  • The AI Disclosure: X Trials Mandatory Labels as Community Notes Gets Suspension Power
  • Technology

The AI Disclosure: X Trials Mandatory Labels as Community Notes Gets Suspension Power

Do Son February 23, 2026 2 minutes read
0
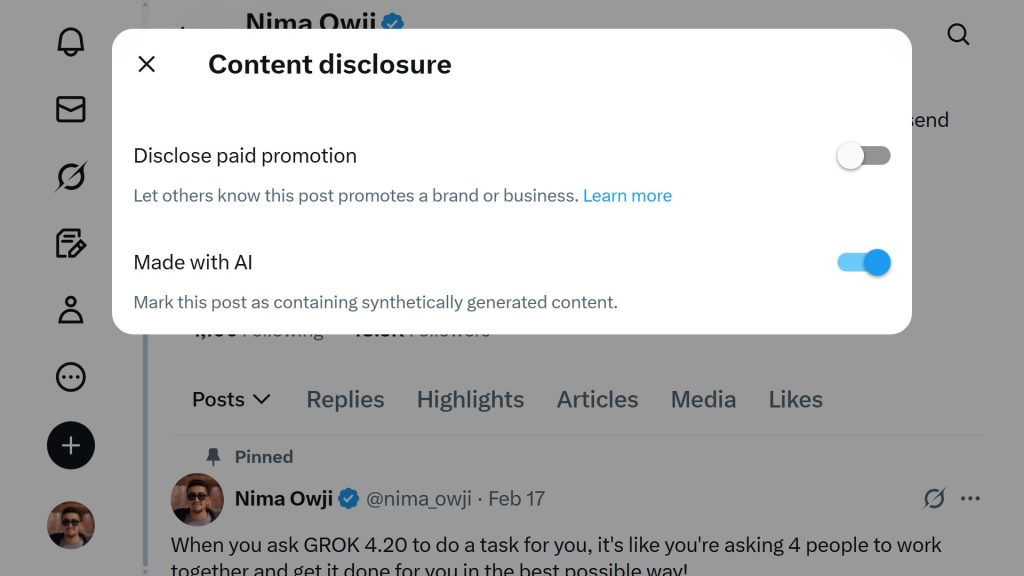
X AI-generated content labels

Image: @nima_owji

The social media platform X/Twitter is currently trialing a sophisticated set of AI-related disclosure mandates. Under these emerging terms, individuals disseminating content produced via artificial intelligence must explicitly designate it as such by toggling an “AI-Generated” attestation during the publication process.

The implementation of these AI-generated labels serves as a vital safeguard, allowing the audience to discern—via instantaneous visual cues—that the material is a synthetic creation rather than a human-authored narrative or an authentic journalistic excerpt. This initiative is a strategic maneuver intended to suppress the proliferation of digital misinformation and fabricated rumors orchestrated through the manipulation of generative technologies.

Naturally, users may choose to forgo this declaration at the moment of publication without immediate consequence, as X/Twitter lacks the capacity to scrutinize every dispatch with absolute precision. However, should a post achieve viral status and ignite widespread discourse, it will inevitably attract the scrutiny of Community Notes contributors. If such a post is identified as an undeclared AI synthesis, it risks being flagged for non-compliance, which could culminate in a permanent suspension of the account—a penalty X currently enforces with uncompromising rigor.

Consequently, while those with a modest following may feel emboldened to post with relative impunity, influential figures and high-profile accounts are strongly urged to adhere to these burgeoning Community Guidelines once the feature is fully integrated. The difficulty of successfully appealing a suspension in the current administrative climate remains formidable, rendering compliance the only prudent course of action.

Add Daily CyberSecurity as a preferred source on Google

Related coverage

  • The $1.5 Million Truce: Elon Musk Settles SEC Lawsuit Over “Hidden” Twitter Stake and Acquisition Gamesmanship
  • The Price of Deception: X Imposes 90-Day Payout Ban on AI-Generated War “Slop”
  • Speed of Truth: X Trials “Collaborative Notes” to Supercharge Fact-Checking with Grok AI
  • Navigate Smarter: Google Maps Arrives on Garmin Smartwatches
  • Sovereign Synthesis: Apple Unveils Gemini-Powered Siri AI and macOS Golden Gate
  • Google AI Plus Changes Drop Pro Model Access
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Account Suspension AI labels AI-generated content Community Notes digital transparency Elon Musk Grok AI Misinformation social media news 2026 twitter X

Leave a Reply Cancel reply

You must be logged in to post a comment.

🚨 Active Exploits in the Wild

  • CVE-2010-20126CVSS 5.1
    Virtual Keyboard plugin for SquirrelMail through 0.9.1 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2012-20007CVSS 9.3
    ThinkPHP 2.0 through 2.2 and 3.0 Lite mode contains an eval injection vulnerability in the Dispatcher PATH_INFO parsing,...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2012-20008CVSS 8.7
    openSIS 5.1 before 9.0 contains a local file inclusion vulnerability that allows authenticated users to include arbitrary files...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2026-119618CVSS 8.1
    Concurrent Execution using Shared Resource with Improper Synchronization vulnerability in Apache HTTP Server's mod_http2 in assign_headers() can lead...
    Admin intel📅 Updated: Nov 18, 2026
  • CVE-2024-10441CVSS 9.8
    Improper encoding or escaping of output vulnerability in the system plugin daemon in Synology BeeStation OS (BSM) before...
    CISA KEV📅 Added to KEV: Nov 18, 2026
  • CVE-2026-40217CVSS 8.8
    LiteLLM through 2026-04-08 allows remote attackers to execute arbitrary code via bytecode rewriting at the /guardrails/test_custom_code URI.
    CISA KEV📅 Added to KEV: Nov 18, 2026
  • CVE-2026-90817CVSS 9.8
    An unauthenticated Remote Code Execution vulnerability was found in the survey passthrough routing and Data Import processing logic,...
    CISA KEV📅 Added to KEV: Nov 18, 2026
  • CVE-2026-90436CVSS 9.8
    ** UNSUPPORTED WHEN ASSIGNED ** Deserialization of an inbound SOAP fault in Apache Axis 1.x allows unauthenticated remote...
    CISA KEV📅 Added to KEV: Nov 18, 2026
Powered by CVE Watchtower

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Get free CVE alerts Pro from $7/mo

Critical Vulnerabilities

  • CVE-2026-131287CVSS 9.6
    Remote Code Execution (RCE) through the REST API in Splunk SOAR. In Splunk SOAR versions below 8.8.0, a...
    📅 Updated: Nov 19, 2026
  • CVE-2026-131253CVSS 9.9
    Remote Code Execution (RCE) through the App Wizard in Splunk SOAR. In Splunk SOAR versions below 8.8.0, an...
    📅 Updated: Nov 19, 2026
  • CVE-2026-131202CVSS 9.1
    Remote Code Execution (RCE) through REST API Path Traversal in Splunk Enterprise Security. In Splunk Enterprise Security versions...
    📅 Updated: Nov 19, 2026
  • CVE-2026-76535CVSS 9.1
    Authentication Bypass through the RapidDiag REST API in Splunk Enterprise. In Splunk Enterprise versions below 10.6.1, 10.4.5, 10.2.9,...
    📅 Updated: Nov 19, 2026
  • CVE-2026-76536CVSS 9.4
    Authentication Bypass through the Cluster Configuration REST API in Splunk Enterprise. In Splunk Enterprise versions below 10.4.5, 10.2.9,...
    📅 Updated: Nov 19, 2026
  • CVE-2026-123965CVSS 9.3
    A prompt injection vulnerability in all versions of Jet Admin Cloud Platform allows a remote attacker with a...
    📅 Updated: Nov 19, 2026
  • CVE-2026-131914CVSS 9.3
    Deserialization of untrusted data in double-submit cookie vs. form field validation in Idunno.AntiCsrf versions through 0.9.1 Beta on...
    📅 Updated: Nov 19, 2026
  • CVE-2024-10441CVSS 9.8
    Improper encoding or escaping of output vulnerability in the system plugin daemon in Synology BeeStation OS (BSM) before...
    CISA KEV📅 Added to KEV: Nov 18, 2026📅 Updated: Nov 19, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About Daily CyberSecurity
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DMCA
  • Privacy Policy

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.