Skip to content
November 6, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Unpatched ActiveMQ Flaw Leads to Repeat Breach and LockBit Ransomware LockBit 3.0 Ransomware
  • Cybercriminals

Unpatched ActiveMQ Flaw Leads to Repeat Breach and LockBit Ransomware

Do Son February 25, 2026 0

The DFIR Report reveals how a persistent attacker exploited CVE-2023-46604 twice in 18 days to deploy LockBit ransomware. Patch your ActiveMQ servers now!

The High Cost of Free: Cracked Music Plugins Weaponized to Infect macOS with Odyssey Malware Odyssey Malware MacSyncStealer
  • Malware

The High Cost of Free: Cracked Music Plugins Weaponized to Infect macOS with Odyssey Malware

Do Son February 25, 2026 0

Security researchers uncover a massive macOS malware campaign using "cracked" audio plugins and "ClickFix" tactics to deliver Odyssey and MacSyncStealer.
Rooting Out Risk: CISA Warns of Critical 9.1 Severity Flaws in Gardyn Smart Gardening Systems Gardyn Home Kit Vulnerabilities IoT Command Injection Vivotek Vulnerability CVE-2026-22755 Command Injection Ofuji Fishing data breach
  • Vulnerability Report

Rooting Out Risk: CISA Warns of Critical 9.1 Severity Flaws in Gardyn Smart Gardening Systems

Do Son February 25, 2026 0

CISA warns of critical flaws (CVE-2025-29631) in Gardyn Home Kits allowing unauthenticated RCE and admin access. Update your app and firmware immediately!
Malicious NuGet Packages Weaponize ASP.NET Identity for Production Backdoors NuGet Supply Chain Attack ASP.NET Identity Theft
  • Malware

Malicious NuGet Packages Weaponize ASP.NET Identity for Production Backdoors

Do Son February 25, 2026 0

Socket researchers uncover a NuGet supply chain attack using "NCryptYo" to hijack ASP.NET apps. Attackers inject backdoors into production authorization layers.

Stealth & Persistence: MuddyWater’s New Rust-Based Payload Mimics Cloudflare and Reddit GemStuffer RubyGems Campaign RubyGems Data Exfiltration TanStack npm Compromise Supply Chain Attack DNS Hijacking APT28 (Fancy Bear) OpenVSX Supply Chain Attack Checkmarx Plugin Breach Stryker Cyberattack CISA Alert Trans-Regional Cyber Conflict Operation Epic Fury Cyber Operation MacroMaze APT28 Cyber Espionage Notepad++ Supply Chain Attack Lotus Blossom Group Defense Industrial Base Threats GTIG Report APT28 Operation Neusploit CVE-2026-21509 Bookworm Malware
  • Cyber Security
  • Malware

Stealth & Persistence: MuddyWater’s New Rust-Based Payload Mimics Cloudflare and Reddit

Do Son February 25, 2026 0

Genians report reveals MuddyWater APT's shift to Rust-based malware and RMM tool abuse for long-term espionage across government and critical infrastructure.

Total Takeover: Critical Zyxel Flaw (CVSS 9.8) Exposes Routers to Remote Command Injection CVE-2022-43389 - CVE-2024-12398 Zyxel UPnP Vulnerability CVE-2025-13942
  • Vulnerability Report

Total Takeover: Critical Zyxel Flaw (CVSS 9.8) Exposes Routers to Remote Command Injection

Do Son February 25, 2026 0

Zyxel issues urgent patches for a critical 9.8 severity flaw (CVE-2025-13942) in UPnP functions that allows remote attackers to execute OS commands. Patch now!

Sendmarc Releases DMARCbis Fireside Chat Featuring Co-Editor Todd Herr DMARCbis_discussion_press_release_1771937669dXv9v1JLJA
  • Press Release

Sendmarc Releases DMARCbis Fireside Chat Featuring Co-Editor Todd Herr

cybernewswire February 24, 2026 0
Wilmington, North America, 24th February 2026, CyberNewswire
Read More Read more about Sendmarc Releases DMARCbis Fireside Chat Featuring Co-Editor Todd Herr
Root Access Granted: Four Critical RCE Flaws Patched in SolarWinds Serv-U CVE-2024-28075 & CVE-2024-23473 SolarWinds Serv-U RCE CVE-2025-40538
  • Vulnerability Report

Root Access Granted: Four Critical RCE Flaws Patched in SolarWinds Serv-U

Do Son February 24, 2026 0

SolarWinds patches four critical 9.1 CVSS RCE vulnerabilities in Serv-U. Attackers can create admin users and execute code as root. Update to 15.5.4 now!

Critical VMware Aria Operations Flaw Allows RCE During System Upgrades VMware Aria Operations CVE-2026-22719 VMware Fusion - CVE-2024-38811 VMware security, CVE-2025-22247
  • Vulnerability Report

Critical VMware Aria Operations Flaw Allows RCE During System Upgrades

Do Son February 24, 2026 0

Broadcom warns of a high-severity RCE flaw (CVE-2026-22719) in VMware Aria Operations. Attackers can execute commands during system migrations. Patch now!

The Distillation War: Anthropic Accuses DeepSeek and Chinese Rivals of ‘Industrial-Scale’ Data Theft Anthropic confidential IPO filing Anthropic Google $200 billion deal Anthropic Mythos Preview Anthropic Pentagon blacklist Claude Max 20x open-source Model Distillation Anthropic vs DeepSeek Claude Free tier update 2026
  • Technology

The Distillation War: Anthropic Accuses DeepSeek and Chinese Rivals of ‘Industrial-Scale’ Data Theft

Do Son February 24, 2026 0

Anthropic claims DeepSeek and other Chinese AI firms used 24,000 accounts to "pilfer" Claude's data. Inside the high-stakes battle for LLM training secrets.

Machine-Speed Intrusions: How One Hacker Used DeepSeek and Claude to Scale a Global Campaign Weaver E-cology RCE CVE-2026-22679 CVE-2026-20127 Cisco SD-WAN Exploitation AI-Driven Cyberattack ARXON Malware React Server Components Vulnerability CVE-2025-55182 FortiWeb Auth Bypass, Unauthenticated Admin Takeover RayInitiator Bootkit, LINE VIPER CVE-2025-59689 Department of the Treasury cybersecurity - CVE-2025-0108 PoC CVE-2025-31103 Dior Data Breach SK Telecom data breach, long-term intrusion
  • Cybercriminals

Machine-Speed Intrusions: How One Hacker Used DeepSeek and Claude to Scale a Global Campaign

Do Son February 24, 2026 0

Researcher @goyaramen exposes "ARXON," an AI-automated pipeline using LLMs to manage simultaneous global attacks on Fortinet devices. The future of scale is here.

Chrome Alert: High-Severity Flaws in Media and Tint Engine Trigger Emergency Update Chrome Security Update Use After Free Chrome Security Update Critical Vulnerabilities Chrome Security Update CVE-2026-3062 Chrome Security Update V8 Engine Vulnerability Chrome Security Update CVE-2026-1862 CVE-2026-0628 Chrome 143 Update Chrome Safe Browsing UAF, CVE-2025-11756 Chrome Memory Flaws, CVE-2025-11460 Google Chrome, vulnerability CVE-2025-10200, CVE-2025-10201 Big Sleep CVE-2025-9478 Chrome Update, Security Vulnerabilities
  • Vulnerability Report

Chrome Alert: High-Severity Flaws in Media and Tint Engine Trigger Emergency Update

Do Son February 24, 2026 0

Google releases Chrome v145.0.7632.116 to patch high-severity flaws in Media, DevTools, and the Tint graphics engine. Update now to prevent memory leaks.

Operation Olalampo: MuddyWater Unleashes AI-Assisted Rust Malware and Telegram C2 in MENA Espionage Surge Harvester APT Linux Backdoor OT Cyberattack Iranian APT Operation Olalampo MuddyWater APT Prince of Persia APT, Tonnerre v50 Patchwork APT, DLL Sideloading Subtle Snail, cyber espionage ShadowSilk, cyber espionage Volt Typhoon APT Group - Chinese Cybersecurity Firm
  • Cyber Security
  • Malware

Operation Olalampo: MuddyWater Unleashes AI-Assisted Rust Malware and Telegram C2 in MENA Espionage Surge

Do Son February 24, 2026 0

Group-IB exposes Operation Olalampo: MuddyWater's new MENA campaign using AI-assisted Rust malware (CHAR) and Telegram bots for stealthy C2 communication.

No Patch for the EOL: CISA Warns of Critical 9.8 Severity Flaw in USR-W610 IoT Devices shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

No Patch for the EOL: CISA Warns of Critical 9.8 Severity Flaw in USR-W610 IoT Devices

Do Son February 24, 2026 0

CISA warns of critical flaws in EOL USR-W610 IoT servers. CVE-2026-25715 allows full admin control via blank passwords. No patches planned; isolate now.
Silver Fox APT Unleashes ‘Winos 4.0’ Malware via BYOVD Attacks Winos 4.0 Malware Silver Fox APT RapperBot BVIEC cyberattack - CNC group DAMASCENED PEACOCK, malware analysis
  • Malware

Silver Fox APT Unleashes ‘Winos 4.0’ Malware via BYOVD Attacks

Do Son February 24, 2026 0

FortiGuard Labs exposes a massive Silver Fox APT campaign targeting Taiwan. Hackers use tax-themed phishing and BYOVD attacks to deploy Winos 4.0 malware.

Hackers Weaponize Facebook Ads with Fake Windows 11 Updates Fake Windows 11 Ads Info-Stealing Malware
  • Malware

Hackers Weaponize Facebook Ads with Fake Windows 11 Updates

Do Son February 24, 2026 0

Malwarebytes exposes a deceptive campaign using fake Windows 11 Facebook ads to trick users into downloading stealthy info-stealing malware.

Hired to Hack: North Korean Fake IT Workers Hijack Exec Identities in ‘Contagious Interview’ Scams Open VSX Malware String-Fragment Reconstruction DarkCloud Stealer, steganography APT 35 Charming Kitten cyclops
  • Cybercriminals

Hired to Hack: North Korean Fake IT Workers Hijack Exec Identities in ‘Contagious Interview’ Scams

Do Son February 24, 2026 0

GitLab reveals how North Korean fake IT workers use 'Contagious Interview' scams to bypass hiring, steal data, and hijack executive digital identities.

CVE-2026-27212: Critical Swiper Prototype Pollution Flaw (CVSS 9.4) Exposes Global Apps Swiper npm Vulnerability CVE-2026-27212
  • Vulnerability Report

CVE-2026-27212: Critical Swiper Prototype Pollution Flaw (CVSS 9.4) Exposes Global Apps

Do Son February 24, 2026 0

Critical prototype pollution flaw (CVE-2026-27212) in the Swiper npm package allows RCE, DoS, and auth bypass. Update to version 12.1.2 immediately.

First-Ever TPM Sniffing Attack Extracts LUKS Keys from Industrial Linux Devices TPM Sniffing CVE-2026-0714
  • Vulnerability Report

First-Ever TPM Sniffing Attack Extracts LUKS Keys from Industrial Linux Devices

Do Son February 24, 2026 0

Researchers extract LUKS decryption keys in plaintext from Moxa UC-1222A devices via a novel TPM bus sniffing attack (CVE-2026-0714). Secure your hardware.
The ‘Human Verification’ Trap: ClickFix Campaign Hijacks Trusted Sites to Deploy MIMICRAT MIMICRAT Malware ClickFix Campaign
  • Malware

The ‘Human Verification’ Trap: ClickFix Campaign Hijacks Trusted Sites to Deploy MIMICRAT

Do Son February 24, 2026 0

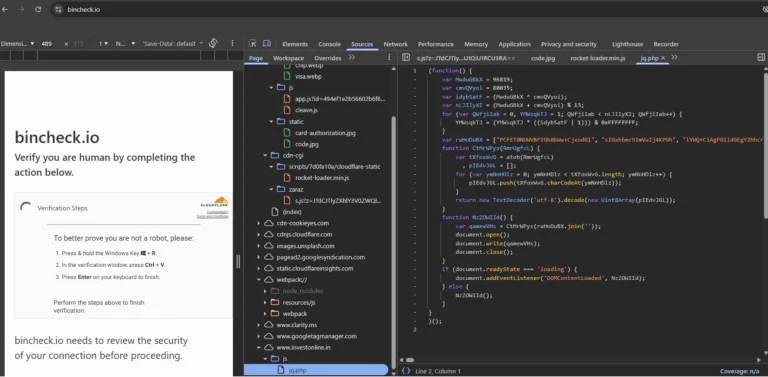
Elastic Security Labs uncovers a ClickFix campaign turning human helpfulness into a weapon. Fake verifications deploy the fileless MIMICRAT via PowerShell.

Stargate in Shambles: Sam Altman Abandons the $500B SoftBank Dream for an Oracle “Plan B” OpenAI token price reduction OpenAI Deployment Company DeployCo OpenAI IPO strategy OpenAI Privacy Filter 1.5B OpenAI $122 billion funding OpenAI GitHub alternative OpenAI military agreement 2026 OpenAI Stargate project collapse NVIDIA OpenAI investment stall ChatGPT Go $8 subscription, OpenAI GPT-5.2 Instant ads OpenAI Torch acquisition, Unified Medical Memory OpenAI Head of Preparedness 2025, Sam Altman AI safety lawsuits ChatGPT Advertising Speculation OpenAI Ad Code Denial OpenAI AI Confession Hallucination Mitigation ChatGPT Quality Focus OpenAI Gemini Red Alert ChatGPT Login, AI ecosystem OpenAI Mental Health, AI Well-Being Council ChatGPT Instant Checkout, Agentic Commerce OpenAI cloud computing OpenAI, startup incubator OpenAI chips, NVIDIA competition AI competition, antitrust lawsuit GPT-5, OpenAI Livestream OpenAI Open-Weight, AI Models OpenAI Infrastructure, AI Data Centers ChatGPT Business, Office Productivity OpenAI Open-Weight Model, WindSurf Acquisition OpenAI AI Browser, ChatGPT Integration Mattel AI, OpenAI Partnership OpenAI o3, Price Cut OpenAI's Next-Gen AI: O3-Pro's Enhanced Reasoning PowerOpenAI profit OpenAI Bid OpenAI Social Network ChatGPT Social OpenAI Non-profit OpenAI UAE ChatGPT Plus free
  • Technology

Stargate in Shambles: Sam Altman Abandons the $500B SoftBank Dream for an Oracle “Plan B”

Do Son February 23, 2026 0

OpenAI’s $500B Stargate venture has stalled. Sam Altman is now pivoting to a $30B Oracle "Plan B" to survive the brutal 2026 battle for energy and silicon.

“Hey Plex”: Samsung’s Galaxy S26 Challenges Google with a Bold New AI Multi-Agent Universe Galaxy S26 AI Camera Galaxy Unpacked 2026
  • Technology

“Hey Plex”: Samsung’s Galaxy S26 Challenges Google with a Bold New AI Multi-Agent Universe

Do Son February 23, 2026 0

Samsung’s Galaxy S26 debuts a "multi-agent" AI world. Call "Hey Plex" for real-time web search as Samsung Notes and Gallery sync with Perplexity’s brain.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-123488CVSS 9.3
    Craft CMS 4.0.0 before 4.18.9 and 5.0.0 before 5.11.2 contains an unauthenticated SQL injection vulnerability in the element...
    📅 Updated: Nov 6, 2026
  • CVE-2026-93754CVSS 9.8
    The payever – WooCommerce Gateway plugin for WordPress is vulnerable to arbitrary file upload leading to remote code...
    📅 Updated: Nov 6, 2026
  • CVE-2026-59105CVSS 9.3
    Jumis (formerly Tildes Jumis) creates and uses a Microsoft SQL Server login named ##Tilde_JumisAdmin## whose password is derived...
    📅 Updated: Nov 6, 2026
  • CVE-2026-19256CVSS 9.8
    The All In One Login WordPress plugin before 2.5.0 does not adequately restrict the number of attempts that...
    📅 Updated: Nov 6, 2026
  • CVE-2026-115230CVSS 9.8
    The WHIZZ WordPress plugin through 1.1.8 does not validate the password-reset key before updating a user's password, relying...
    📅 Updated: Nov 6, 2026
  • CVE-2026-110955CVSS 9.8
    The Wurdey WordPress plugin through 1.0.0 does not verify a request signature before logging a user in, allowing...
    📅 Updated: Nov 6, 2026
  • CVE-2026-113584CVSS 9.8
    The placester WordPress plugin through 1.4.3 does not perform any capability, nonce or ownership check on an AJAX...
    📅 Updated: Nov 6, 2026
  • CVE-2026-113615CVSS 9.8
    The GS JWT Authentication for WP REST API WordPress plugin through 1.0.0 does not sanitize or parameterize a...
    📅 Updated: Nov 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.