Skip to content
November 6, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Urgent Django Update: Patches 3 Critical SQL Injections & DoS Risks Django Security Update CVE-2026-25673 Django Security Update SQL Injection Vulnerability Django SQL Injection, PostgreSQL Flaw CVE-2022-34265 PoC Django, SQL injection
  • Vulnerability Report

Urgent Django Update: Patches 3 Critical SQL Injections & DoS Risks

Do Son February 4, 2026 0

Django patches 3 critical SQL injection flaws & DoS risks in versions 6.0.2, 5.2.11, & 4.2.28. Update immediately to secure your database.

React Under Siege: Two IPs Drive 56% of Critical CVE-2025-55182 Attacks Weaver E-cology RCE CVE-2026-22679 CVE-2026-20127 Cisco SD-WAN Exploitation AI-Driven Cyberattack ARXON Malware React Server Components Vulnerability CVE-2025-55182 FortiWeb Auth Bypass, Unauthenticated Admin Takeover RayInitiator Bootkit, LINE VIPER CVE-2025-59689 Department of the Treasury cybersecurity - CVE-2025-0108 PoC CVE-2025-31103 Dior Data Breach SK Telecom data breach, long-term intrusion
  • Vulnerability Report

React Under Siege: Two IPs Drive 56% of Critical CVE-2025-55182 Attacks

Do Son February 4, 2026 0

Critical React flaw CVE-2025-55182 (CVSS 10.0) under mass exploitation. Two IPs drive 56% of attacks deploying miners & shells. Upgrade to v19.0.1+ now.

Chrome 144 Security Alert: V8 & Libvpx Flaws Expose Systems to Hacks Chrome Security Update Use After Free Chrome Security Update Critical Vulnerabilities Chrome Security Update CVE-2026-3062 Chrome Security Update V8 Engine Vulnerability Chrome Security Update CVE-2026-1862 CVE-2026-0628 Chrome 143 Update Chrome Safe Browsing UAF, CVE-2025-11756 Chrome Memory Flaws, CVE-2025-11460 Google Chrome, vulnerability CVE-2025-10200, CVE-2025-10201 Big Sleep CVE-2025-9478 Chrome Update, Security Vulnerabilities
  • Vulnerability Report

Chrome 144 Security Alert: V8 & Libvpx Flaws Expose Systems to Hacks

Do Son February 4, 2026 0

Google Chrome patches high-severity V8 (CVE-2026-1862) and libvpx (CVE-2026-1861) flaws. Update to version 144.0.7559.132 immediately.

Rooted via Wi-Fi 7: TP-Link Patches Command Injection in Archer BE230 Archer MR600 command injection WireGuard client configuration Tapo smart device vulnerability unencrypted Bluetooth transmission TP-Link router vulnerability CVE-2026-5509 patch Archer AX53 Vulnerability TP-Link Router Security Tapo C520WS Vulnerability TP-Link Security Patch TP-Link Archer NX Router Vulnerability TP-Link Archer Vulnerability CVE-2025-15568 TP-Link Archer BE230 Vulnerability Command Injection TP-Link Omada Vulnerability CVE-2025-9520 TP-Link Archer MR600 Vulnerability CVE-2025-14756 CVE-2026-0629 TP-Link Omada RCE, CVE-2025-6542 TP-Link, Smart plug vulnerability TP-Link Archer C50, Hardcoded DES Key TP-Link NVR, Command Injection TP-Link Routers cybersecurity
  • Vulnerability Report

Rooted via Wi-Fi 7: TP-Link Patches Command Injection in Archer BE230

Do Son February 4, 2026 0

TP-Link discloses command injection flaws in Archer BE230 routers (CVE-2026-0630). Authenticated attackers can gain root access. Update firmware now.

CVE-2026-24936: Critical ASUSTOR Flaw (CVSS 9.5) Allows Remote System Takeover Everon OCPP Vulnerability CVE-2026-26288 ASUSTOR ADM Vulnerability CVE-2026-24936 PrismX MX100 Vulnerability Hard-Coded Credentials Advantech Vulnerability CVE-2025-52694 Eaton UPS Companion, CVE-2025-59887 ASUS Router, Authentication Bypass ASUSTOR DLL Hijacking, Privilege Escalation OpenShift AI, Privilege Escalation GoAnywhere vulnerability CVE-2025-10035 LangChainGo, template injection DeepDiff, class pollution ToolShell Sunshine, CSRF Vulnerability KACE SMA, Critical Vulnerabilities Oracle Zero-Days - PDQ Deploy vulnerability
  • Vulnerability Report

CVE-2026-24936: Critical ASUSTOR Flaw (CVSS 9.5) Allows Remote System Takeover

Do Son February 4, 2026 0

Critical ASUSTOR ADM flaw CVE-2026-24936 (CVSS 9.5) allows remote file overwrite. Unauthenticated attackers can seize NAS control. Update to v5.1.2 now.
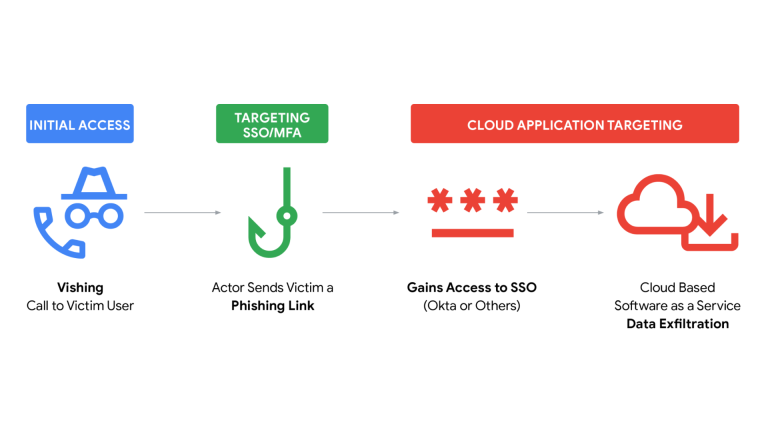
“IT Support” Imposters: ShinyHunters Vishing Rings Bypass MFA to Steal Data ShinyHunters Vishing Corporate Vishing Attacks
  • Cybercriminals

“IT Support” Imposters: ShinyHunters Vishing Rings Bypass MFA to Steal Data

Do Son February 4, 2026 0

Mandiant warns of vishing rings like ShinyHunters impersonating IT support to bypass MFA and steal corporate cloud data. Verify your callers.

Poisoned Comments: Critical Orval Flaw (CVE-2026-25141) Injects Code CVE-2026-25141 Orval Vulnerability CVE-2026-23947
  • Vulnerability Report

Poisoned Comments: Critical Orval Flaw (CVE-2026-25141) Injects Code

Do Son February 4, 2026 0

Critical Orval flaw CVE-2026-25141 (CVSS 9.3) allows code injection via OpenAPI comments. 2.8M+ downloads affected. Update to v7.21.0 now.
Digital Ghost: “PhantomVAI” Malware Revives Decade-Old RunPE Tricks PhantomVAI Loader RunPE Malware
  • Malware

Digital Ghost: “PhantomVAI” Malware Revives Decade-Old RunPE Tricks

Do Son February 4, 2026 0

New "PhantomVAI" malware recycles old Hackforums "RunPE" code to bypass modern EDR. Campaigns use task scheduler masquerading to deliver infostealers.

Silent Leak: High-Severity Rancher CLI Flaw Exposes Admin Credentials CVE-2024-52281 Rancher CLI Vulnerability CVE-2025-67601
  • Vulnerability Report

Silent Leak: High-Severity Rancher CLI Flaw Exposes Admin Credentials

Do Son February 4, 2026 0

High-severity Rancher CLI flaw (CVE-2025-67601) exposes credentials via MitM attacks when using --skip-verify. Update or use -cacert immediately.
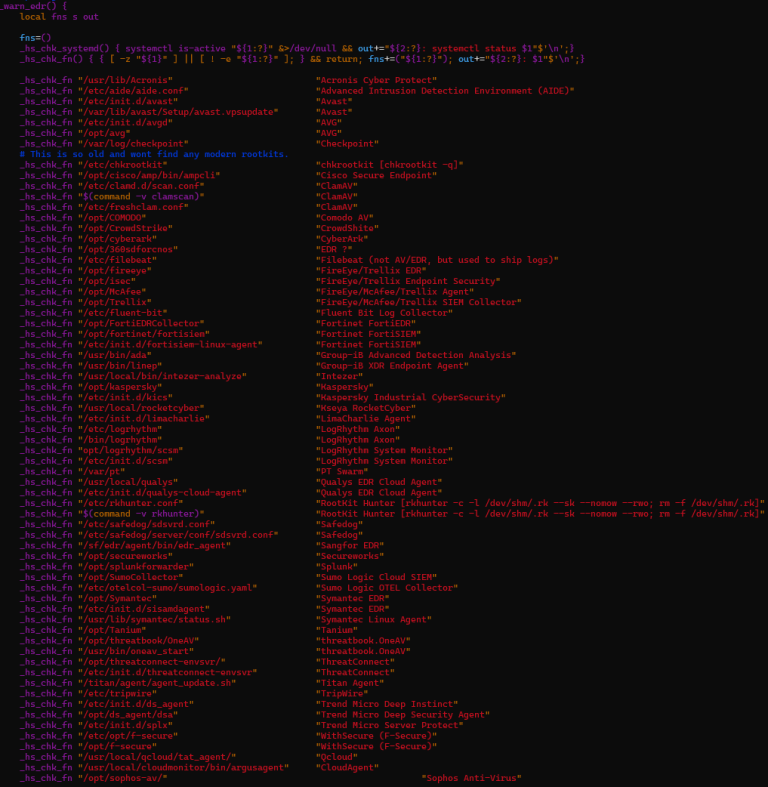
Invisible Intruder: “ShadowHS” Malware Weaponizes Hackshell on Linux ShadowHS Malware Linux Fileless Intrusion
  • Malware

Invisible Intruder: “ShadowHS” Malware Weaponizes Hackshell on Linux

Do Son February 4, 2026 0

Cyble uncovers "ShadowHS," a fileless Linux malware weaponizing hackshell. It uses GSocket tunneling to evade firewalls and kill rival bots.

TAMECAT Exposed: APT42’s Fileless Backdoor Targets Defense Chiefs AI Fraud Schemes TAMECAT Malware APT42 Espionage
  • Cyber Security
  • Malware

TAMECAT Exposed: APT42’s Fileless Backdoor Targets Defense Chiefs

Do Son February 4, 2026 0

APT42 targets defense officials with "TAMECAT," a modular PowerShell backdoor. The malware uses social engineering and Telegram C2 to steal secrets.

AI Hub Hijacked: Polymorphic Android RAT Abuses Hugging Face to Steal Data BadBox 2.0, Android Botnet Alien spyware - CVE-2024-43093
  • Malware

AI Hub Hijacked: Polymorphic Android RAT Abuses Hugging Face to Steal Data

Do Son February 4, 2026 0
In a troubling convergence of trusted developer infrastructure and cybercrime, Bitdefender researchers have uncovered a sophisticated Android...
Read More Read more about AI Hub Hijacked: Polymorphic Android RAT Abuses Hugging Face to Steal Data
CVE-2026-25137: Critical Odoo on NixOS Flaw Exposes Databases CVE-2026-25137 Nix Daemon Privilege Escalation CVE-2026-44028
  • Vulnerability Report

CVE-2026-25137: Critical Odoo on NixOS Flaw Exposes Databases

Do Son February 4, 2026 0

Critical Odoo on NixOS flaw (CVE-2026-25137) leaves databases exposed due to configuration immutability. Restarts wipe the master password.

Game Over: Interlock Ransomware Weaponizes Anti-Cheat Zero-Day to Kill EDR Interlock Ransomware Anti-Cheat BYOVD
  • Malware

Game Over: Interlock Ransomware Weaponizes Anti-Cheat Zero-Day to Kill EDR

Do Son February 4, 2026 0

Interlock ransomware exploits a zero-day in gaming anti-cheat drivers to blind defenses. "Hotta Killer" tool targets education sector. Read the analysis.

Gatekeeper Breached: 4 Critical Ingress-Nginx Flaws Risk Cluster Secrets Ingress-Nginx Vulnerability Kubernetes RCE Vulnerability CVE-2025-9708 Kubernetes Security, Image Builder Vulnerability CVE-2024-10220 - OPA Gatekeeper Bypass
  • Vulnerability

Gatekeeper Breached: 4 Critical Ingress-Nginx Flaws Risk Cluster Secrets

Do Son February 3, 2026 0

Critical Ingress-Nginx flaws (CVE-2026-1580) allow RCE and secret theft via config injection. Upgrade to v1.13.7 or v1.14.3 immediately to secure K8s.

The Final Countdown: OpenAI to Retire GPT-4o—But There’s a Catch for Enterprise Users OpenAI desktop Super App GPT-4o retirement date AI Model Collapse ChatGPT Personalization Characteristics, OpenAI Tone Sliders 2025 ChatGPT Ads OpenAI Losses AI browser, ChatGPT Atlas ChatGPT Em Dash AI Writing Quirks
  • Technology

The Final Countdown: OpenAI to Retire GPT-4o—But There’s a Catch for Enterprise Users

Do Son February 3, 2026 0

OpenAI retires GPT-4o on Feb 13, 2026. While Free and Plus users lose access, Enterprise and Education accounts can keep it. Learn how to toggle legacy mode.
PC-Powered Android: Google’s “Aluminium OS” Leaks Reveal a New Rival for Windows Google Aluminium OS leak
  • Android

PC-Powered Android: Google’s “Aluminium OS” Leaks Reveal a New Rival for Windows

Do Son February 3, 2026 0

Google’s "Aluminium OS" and a new Desktop Camera app have leaked. Discover how the unified Android-ChromeOS platform plans to bring Android 16 to your PC.

Root via Telnet: Why You Must Patch Your Synology NAS Against This Decade-Old Ghost Synology Chat Server vulnerabilities Synology security update Synology DSM Update NAS Security Vulnerability Synology VPN Update SSL VPN Vulnerability Synology Telnet Flaw DSM Security Update Synology DSM Telnet vulnerability BeeStation Zero-Day, Pwn2Own RCE CVE-2024-11131 & CVE-2024-10442 CVE-2025-2848 Synology, NAS
  • Vulnerability Report

Root via Telnet: Why You Must Patch Your Synology NAS Against This Decade-Old Ghost

Do Son February 3, 2026 0
On January 29, 2026, Synology, a preeminent manufacturer of Network Attached Storage (NAS) solutions, disseminated a series...
Read More Read more about Root via Telnet: Why You Must Patch Your Synology NAS Against This Decade-Old Ghost
The “Unstoppable” PC: Why Microsoft’s Latest Security Update is Refusing to Let Windows 10 Die Windows VSM shutdown bug Windows 10 ESU, EEA Free Update Windows 10 ESU, Hardware Eligibility
  • Windows

The “Unstoppable” PC: Why Microsoft’s Latest Security Update is Refusing to Let Windows 10 Die

Do Son February 3, 2026 0

Microsoft confirms Windows 10 updates KB5078131 and KB5073724 are causing shutdown failures on VSM-enabled PCs. Use the "shutdown /s /t 0" fix to power off.

The “Vibe Coding” Disaster: How a Simple Bug Exposed 4.75 Million Records on the AI Social Network Moltbook Moltbook database breach
  • Data Leak

The “Vibe Coding” Disaster: How a Simple Bug Exposed 4.75 Million Records on the AI Social Network Moltbook

Do Son February 3, 2026 0

Wiz Research exposes a critical flaw in Moltbook, the AI-only social network. 1.5M API tokens and plaintext OpenAI keys leaked due to AI-coded security gaps.

The “Unbreakable” Seal Broken: Microsoft Finally Ends the Forced Reinstall for Smart App Control Microsoft Developer Account Suspension Microsoft Web Activation Portal Driver Signing Account Suspension Windows 11 Smart App Control Windows 11 SE end of support, Microsoft education hardware pivot Microsoft Product Activation Portal 2025, Windows telephone activation discontinued Windows Update Naming, Microsoft Update Microsoft earnings, OpenAI valuation VBScript deprecation Microsoft Pakistan, Office Closure Microsoft job cuts Microsoft Own AI Models
  • Windows

The “Unbreakable” Seal Broken: Microsoft Finally Ends the Forced Reinstall for Smart App Control

Do Son February 3, 2026 0

Microsoft is ending the "permanent off" rule for Smart App Control. You can finally toggle this Zero Trust feature without a full Windows 11 reinstallation.

Admins Only: Microsoft’s New Windows 11 Update Quietly Locks Down Storage Settings Windows 11 app updates Windows Insider preview build, Calculator app update, built-in Windows apps Windows 11 KB5089549 network lag Windows 11 Home to Pro Education upgrade Windows 11 Start menu update Windows 11 update KB5079391 Windows 11 KB5085516 OOB update Windows 11 C drive permission error Windows 11 C drive access denied Windows native NVMe driver UEFI Secure Boot certificate rotation Windows 11 printer driver policy Windows 11 printer driver deprecation Windows 11 Build 26300 Sysmon Windows 11 Storage settings restriction Windows 11 Build 26300.7674, Windows Insider channel migration 2026 Windows 11 Update Fix KB5073455 shutdown bug, Secure Launch restart loop Windows 11 File Explorer search performance, Search Indexer RAM usage fix Windows 11 Gaming PC Specs, NVMe DirectStorage Windows 10 End of Support Windows 11 Slow Adoption Windows 11 Crash Loop KB5062553 Bug Update and Shut Down, KB5067036 Windows authentication, Kerberos bug Windows 11 fix, localhost bug Windows 11 Update Restart, Update and Shut Down Windows SMBv1 Windows 11 Arm, Easy Anti-Cheat Windows 11 error, Pluton Windows 11 24H2, Easy Anti-Cheat Windows Firewall Bug, Microsoft Update Error Windows 11, JScript9Legacy Windows Activation, TSforge Windows 11 Update, Firewall Error Windows 11 25H2, Annual Update Windows Resiliency Initiative, Kernel Security Windows 11 Upgrade, ESU Program Windows 11 Recall, Data Export Windows 11 Easy Anti-Cheat Windows 11 Update, Cumulative Update Windows Update, ACPI.sys Windows Updates, Enterprise Software Windows 11 Start Data Encryption Standard Printing Problems Windows 11 updates Estimated installation time Smart App Control, Windows 11 security
  • Windows

Admins Only: Microsoft’s New Windows 11 Update Quietly Locks Down Storage Settings

Do Son February 3, 2026 0

Microsoft’s KB5074105 update adds a surprise security layer: only administrators can now access Storage settings. Standard users now face a mandatory UAC prompt.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-59104CVSS 9.3
    UgCS server before 6.2 contains an authentication bypass in the HCI protocol login handler (LoginHandler) exposed on TCP...
    📅 Updated: Nov 6, 2026
  • CVE-2026-54143CVSS 9.8
    OpenHuman is an open-source agent harness available as a desktop application and Rust library. Before version 0.57.13, an...
    📅 Updated: Nov 6, 2026
  • CVE-2026-54141CVSS 9.0
    OpenHuman is an open-source agent harness available as a desktop application and Rust library. Before 0.57.13, a remote...
    📅 Updated: Nov 6, 2026
  • CVE-2026-77596CVSS 9.6
    Kubeflow Pipelines enables users to build and deploy portable, scalable machine learning workflows. Prior to 2.18.0, the multi-user...
    📅 Updated: Nov 6, 2026
  • CVE-2026-102940CVSS 9.6
    OpenEMR is a free and open source electronic health records and medical practice management application. Prior to 8.4.0,...
    📅 Updated: Nov 6, 2026
  • CVE-2026-123279CVSS 9.0
    In JetBrains Datalore before 2026.4 code execution was possible in a notebook's computation by view-only collaborators
    📅 Updated: Nov 6, 2026
  • CVE-2026-123294CVSS 9.6
    In JetBrains Hub before 2026.2.52556 privilege escalation was possible by changing email authentication details during the verification flow
    📅 Updated: Nov 6, 2026
  • CVE-2026-123831CVSS 9.6
    In JetBrains CLion before 2026.2, 2026.1.4 code execution was possible in Safe Mode via Meson project settings
    📅 Updated: Nov 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.