 Do Son
A critical WordPress Core vulnerability is exploited in the wild. Update to WordPress 7.1.4 immediately to fix the unauthenticated race condition RCE.
Latest Security News
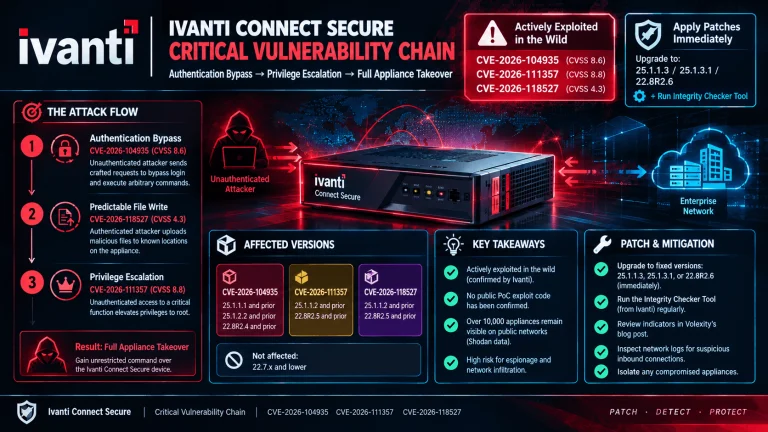
Patch the Ivanti Connect Secure vulnerability now. This Ivanti Connect Secure zero-day chain with CVE-2026-104935 is actively exploited in the wild.
Apply the latest ServiceNow vulnerabilities patch to fix three flaws, including critical sandbox escape CVE-2026-103093 and password leak CVE-2026-103094.

A Polymarket supply chain attack compromised a third-party analytics script to deploy a crypto wallet drainer, prompting an immediate trading halt.
Chrome 156 security update 156.0.8078.79 fixes 21 flaws, including critical Chrome vulnerability CVE-2026-76024 in MediaStream. Update now.
A suspected Binance hot wallet breach prompted emergency investigations as issuers froze over $2.3 billion in stablecoins amid massive token outflows.
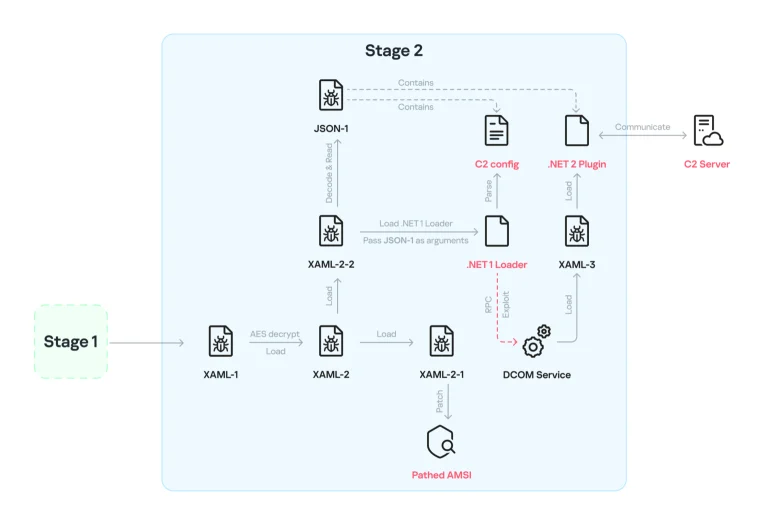
NetamLoader, a new XAML-based .NET loader, points to a supply chain attack on a custom Windows build used by government entities in Asia.
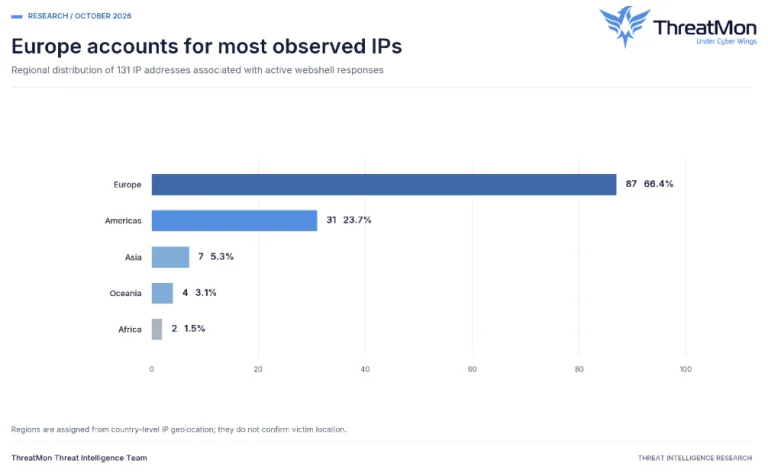
An exposed workspace shows AhsayCBS webshell access turned into SOCKS proxy tunnels with Chisel and GOST across 141 hosts, per the logs.
Upgrade to Composer 2.11.0 or 2.2.31 to fix two Composer vulnerabilities: path traversal GHSA-c968-33g3-wh7p and token leak GHSA-fm2w-xgf2-f9fh.
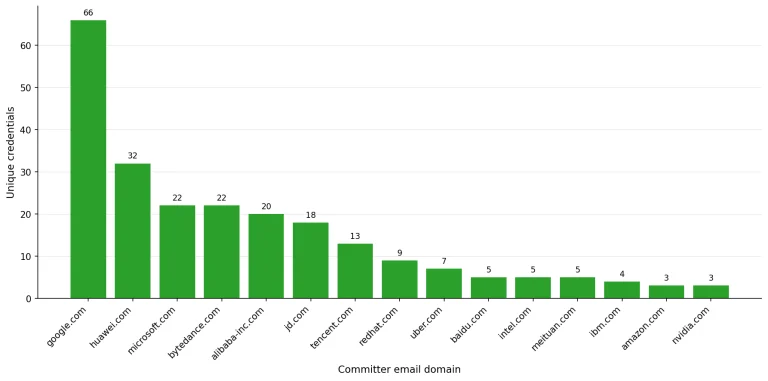
A security scan revealed over 26,000 Gitee exposed credentials across 7.25 million public repositories, affecting major cloud and AI platforms.
Veeam fixes seven vulnerabilities in Veeam Backup for Microsoft 365 and Management Pack, including RCE flaws CVE-2023-22793 and CVE-2026-106076.
Drupal Commerce vulnerability CVE-2026-118539, a highly critical access bypass, is exploited in the wild. Upgrade to 3.3.13 or 8.x-2.41 now.
Latest Technology News
 cybernewswire
San Rafael, United States, 19th October 2026, CyberNewswire
Microsoft links Exchange Server instability to October 2026 Windows updates. See the OWA and mail queue symptoms, plus the registry fix.
Our weekly CVE report for Oct 12-18, 2026 tracks 5,499 new flaws and 12 exploited vulnerabilities, with CISA KEV trailing by up to 8 days.
Some of the most consistently shareable short-form content isn’t built on an elaborate joke at all; it’s...
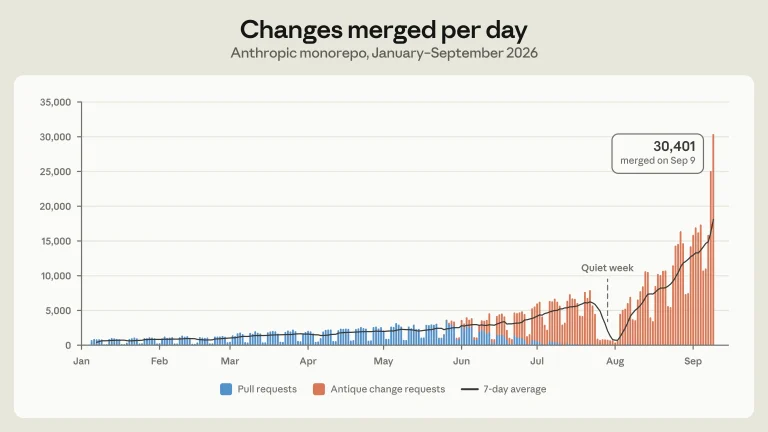
Anthropic developed the Scion version control system to replace Git for its massive monorepo and high-frequency Claude AI coding workflows.
Learn why Windows 11 Remote Desktop fails with error 0xC000000D after installing KB5124010 on enterprise systems running Administrator Protection.
A newly discovered Android 17 Bionic bug in wcscspn and wcspbrk causes premature string termination when processing non-ASCII characters on Pixel devices.
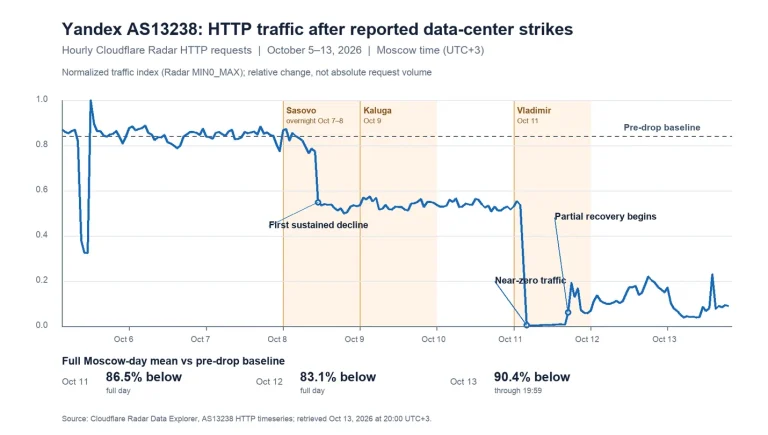
Cloudflare telemetry reveals Russian bot traffic swiftly migrated to alternative clouds following drone strikes on Yandex data center infrastructure.
Google AI Plus changes take effect November 13, removing Pro model access in Gemini. Learn what this means for your subscription and pricing.
The Windows 11 KB5127648 update breaks enterprise Windows 11 Wi-Fi authentication on 802.1X networks. Discover the root cause and registry workaround.
Latest Security News
Kerio Connect vulnerability CVE-2026-112353, a stored XSS flaw via SVG attachments, is exploited in the wild to steal mailboxes. Update to 10.0.8p2.
Apache Kafka fixes 12 vulnerabilities, including CVE-2026-110985, which skips JWT signature verification and grants full cluster access. Patch now.
FreeSWITCH vulnerability CVE-2026-116779 (CVSS 9.8) is exploited in the wild, letting a SIP MESSAGE run server commands. Upgrade to 1.11.3 now.
Cisco Talos uncovered the KeyDrift malware UAT-11473 campaign exploiting CVE-2026-20127 to steal IPsec keys from Cisco SD-WAN controllers.
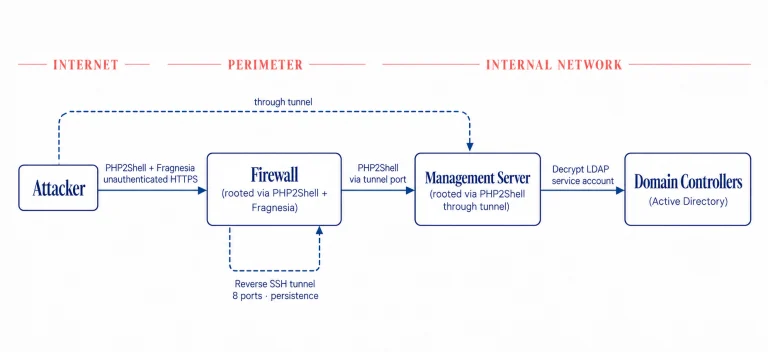
Dream researchers uncovered a Chinese-nexus PHP2Shell exploit Fragnesia chain that rooted 25 firewalls and breached a US government Active Directory.
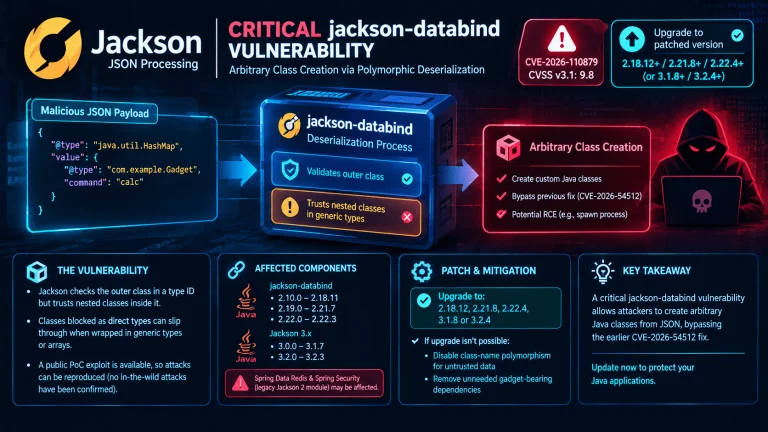
Details and a PoC exploit are public for jackson-databind vulnerability CVE-2026-110879 (CVSS 9.8), a bypass of the CVE-2026-54512 fix. Patch now.
Dell fixes PowerProtect Data Domain vulnerabilities in DD OS, including four CVSS 9.8 flaws like CVE-2026-86400 allowing root command execution.
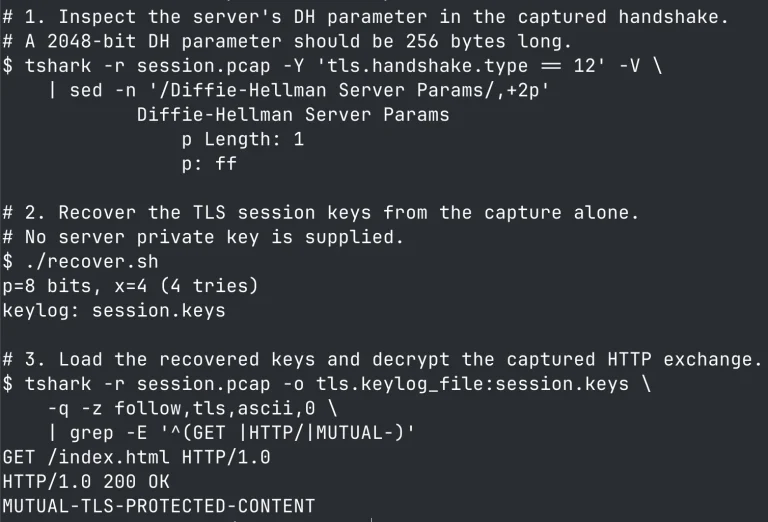
FoxIO releases details and proof-of-concept code for three GoAhead TLS vulnerabilities, including a CVSS 9.1 revoked-certificate bypass. Patch to 6.1.1.
Patch CVE-2026-97631 now. This critical 9.5 CVSS EDK II PXE vulnerability allows unauthenticated pre-boot RCE via crafted ICMP error packets.
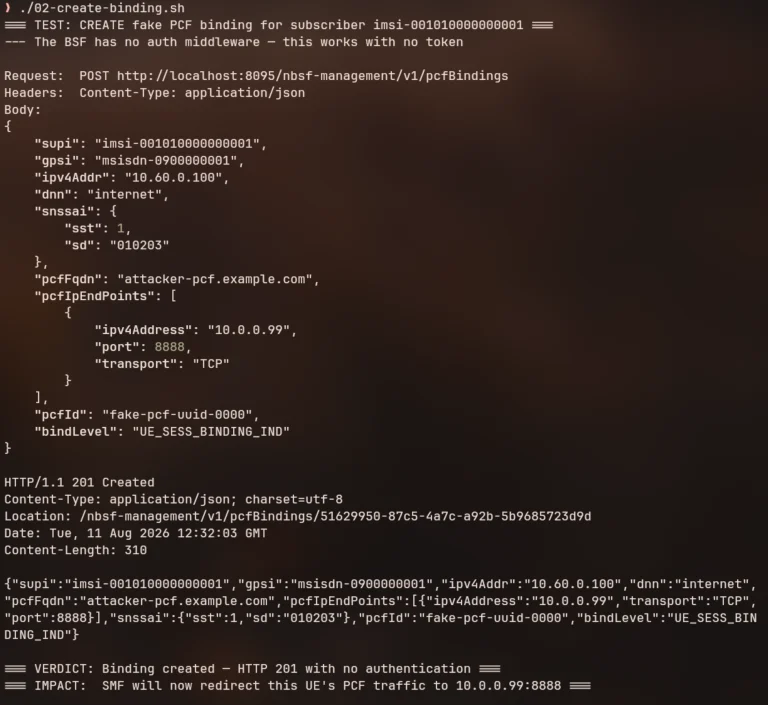
Details and PoC are public for two unpatched free5GC vulnerabilities in the 5G core: BSF auth bypass CVE-2026-115926 and an exposed root CA key.
CISA adds Linux kernel vulnerability CVE-2026-46300, chained with PHP2Shell for root, and VMware ESX flaw CVE-2026-41709 to KEV. Patch now.
Jenkins fixes 15 vulnerabilities, including remote code execution flaws CVE-2026-117612 and CVE-2026-117614. Upgrade to 2.588 or LTS 2.580.2 now.
Latest Technology News
Microsoft links Exchange Server instability to October 2026 Windows updates. See the OWA and mail queue symptoms, plus the registry fix.
Our weekly CVE report for Oct 12-18, 2026 tracks 5,499 new flaws and 12 exploited vulnerabilities, with CISA KEV trailing by up to 8 days.
Some of the most consistently shareable short-form content isn’t built on an elaborate joke at all; it’s...
Anthropic developed the Scion version control system to replace Git for its massive monorepo and high-frequency Claude AI coding workflows.
Learn why Windows 11 Remote Desktop fails with error 0xC000000D after installing KB5124010 on enterprise systems running Administrator Protection.
A newly discovered Android 17 Bionic bug in wcscspn and wcspbrk causes premature string termination when processing non-ASCII characters on Pixel devices.
Cloudflare telemetry reveals Russian bot traffic swiftly migrated to alternative clouds following drone strikes on Yandex data center infrastructure.
Google AI Plus changes take effect November 13, removing Pro model access in Gemini. Learn what this means for your subscription and pricing.
The Windows 11 KB5127648 update breaks enterprise Windows 11 Wi-Fi authentication on 802.1X networks. Discover the root cause and registry workaround.
Linus Torvalds used a Claude Code Linux kernel patch to triple small data read speeds via RCU memory management, though the experimental code needs testing.