Skip to content
October 30, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
BPFDoor Backdoor and New AVERAT Implant Hide in SMTP Traffic on Telecom Edge Devices BPFDoor backdoor and AVERAT implant disguised as mail traffic on telecom and network edge appliances
  • Malware

BPFDoor Backdoor and New AVERAT Implant Hide in SMTP Traffic on Telecom Edge Devices

Do Son October 5, 2026 0

A new BPFDoor backdoor variant and the AVERAT implant hide on telecom edge devices by posing as mail traffic. See how they work and how to hunt them.
Socket Links Popular VS Code Color Themes to the GlassWorm Supply Chain Campaign GlassWorm VS Code themes cluster of malicious VS Code extensions posing as color themes
  • Malware

Socket Links Popular VS Code Color Themes to the GlassWorm Supply Chain Campaign

Do Son October 5, 2026 0

Socket links GlassWorm VS Code themes to malicious VS Code extensions with 8,000+ installs, including a Coca-Cola theme. See how to check yours.
Weekly CVE Report Tracks 2,652 New Flaws and Seven Exploited Vulnerabilities (Sept. 28 – Oct. 4, 2026) Weekly CVE report on exploited vulnerabilities from Daily Cybersecurity and CISA KEV, September 28 to October 4, 2026
  • Weekly Recap

Weekly CVE Report Tracks 2,652 New Flaws and Seven Exploited Vulnerabilities (Sept. 28 – Oct. 4, 2026)

Do Son October 5, 2026 0

Weekly CVE report for Sept 28 - Oct 4, 2026: 2,652 new CVEs and seven exploited vulnerabilities in Cisco, FortiMail, MediaWiki and Citrix.
Warlock Ransomware Group Hits Water and Telecom Operators Through SharePoint Flaws Warlock ransomware attack chain exploiting SharePoint vulnerabilities to hit critical infrastructure
  • Cybercriminals

Warlock Ransomware Group Hits Water and Telecom Operators Through SharePoint Flaws

Do Son October 5, 2026 0

The Warlock ransomware group still exploits SharePoint vulnerabilities, hitting a water utility, a telecom firm, and more. Here is how to defend.
Researcher Publishes Technical Details and PoC Exploit for macOS HFS+ Kernel Flaw CVE-2026-43682 macOS HFS+ vulnerability CVE-2026-43682 kernel heap overflow with public proof-of-concept exploit code
  • Vulnerability Report

Researcher Publishes Technical Details and PoC Exploit for macOS HFS+ Kernel Flaw CVE-2026-43682

Do Son October 5, 2026 0

PoC and details released for macOS HFS+ vulnerability CVE-2026-43682, a CVSS 9.8 kernel heap overflow. Update to macOS Tahoe 26.6 now.
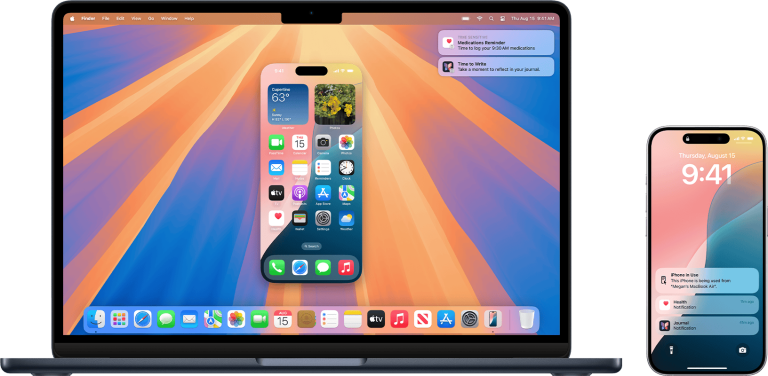
Apple Restricts Full Disk Access for macOS AI Agents macOS security prompt warning users about granting Full Disk Access to an autonomous AI agent
  • Technology

Apple Restricts Full Disk Access for macOS AI Agents

Do Son October 4, 2026 0

Discover why Apple is restricting Full Disk Access for macOS AI agents like Meta Muse to protect user privacy and secure the operating system sandbox.
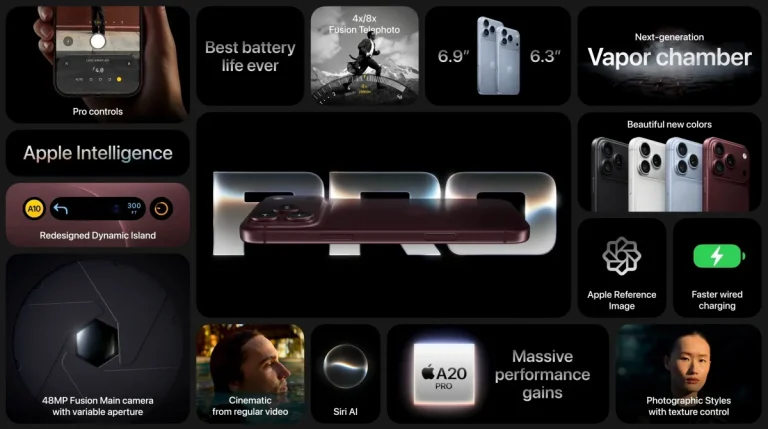
iPhone 18 AT&T Issue: Navigating the Cellular Crisis iPhone 18 AT&T issue hardware replacement and iPhone 18 Pro Max cellular network failure
  • Technology

iPhone 18 AT&T Issue: Navigating the Cellular Crisis

Do Son October 4, 2026 0

Discover the latest iPhone 18 AT&T issue causing cellular failures. Apple confirms that affected iPhone 18 Pro Max devices require hardware replacement.
Citrix NetScaler CVE-2026-88779 Exploited in the Wild to Knock SAML Gateways Offline Citrix NetScaler CVE-2026-88779 exploited in the wild against NetScaler SAML authentication deployments
  • Vulnerability Report

Citrix NetScaler CVE-2026-88779 Exploited in the Wild to Knock SAML Gateways Offline

Do Son October 4, 2026 0

Citrix NetScaler CVE-2026-88779 is exploited in the wild against NetScaler SAML authentication setups. Upgrade to 14.1-73.41 now.
OpenAI AI Safety Whistleblower Warns of Culture Collapse David Robinson OpenAI safety whistleblower warns of AI alignment failures and corporate governance collapse
  • Technology

OpenAI AI Safety Whistleblower Warns of Culture Collapse

Do Son October 4, 2026 0

Discover how the latest OpenAI AI safety whistleblower, David Robinson, warns of a corporate culture collapse and extreme AI alignment risks.
Gemini Free Tier Limits: Flash-Lite Only From Oct 9 Gemini free tier limits showing the Gemini app restricted to the Gemini Flash-Lite model for free personal accounts
  • Technology

Gemini Free Tier Limits: Flash-Lite Only From Oct 9

Do Son October 4, 2026 0

Gemini free tier limits start October 9: free personal accounts get only Flash-Lite, while Flash and Pro move to paid plans.
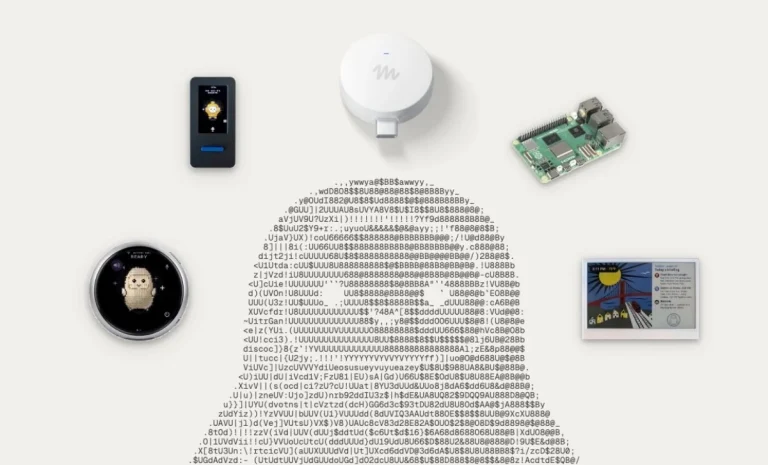
Meta Muse Gadgets: Open-Source Hardware for the Muse AI Meta Muse Gadgets open-source project showing a Muse Home Link dongle and maker-built hardware running the Muse AI agent
  • Technology

Meta Muse Gadgets: Open-Source Hardware for the Muse AI

Do Son October 4, 2026 0

Meta Muse Gadgets is an open-source project that lets makers build Muse AI hardware, with ESP32 firmware, a Linux SDK, and a free dongle.
Unpatched Apache OpenOffice Vulnerability Leads New Apache Advisories for LDAP API and Traffic Server Apache OpenOffice vulnerability CVE-2026-59265 alongside Apache Directory LDAP API flaw CVE-2026-103877 and Traffic Server CVE-2026-102795
  • Vulnerability Report

Unpatched Apache OpenOffice Vulnerability Leads New Apache Advisories for LDAP API and Traffic Server

Do Son October 3, 2026 0

Unpatched Apache OpenOffice vulnerability CVE-2026-59265 runs code via crafted files. Apache Directory LDAP API and Traffic Server fixes out.
Microsoft Reissues September 2026 Exchange Server Security Updates to Add CVE-2026-96940 Exchange Server security updates September 2026 V2 adding CVE-2026-96940 for Exchange SE, Exchange 2019 and Exchange 2016
  • Vulnerability Report

Microsoft Reissues September 2026 Exchange Server Security Updates to Add CVE-2026-96940

Do Son October 3, 2026 0

Microsoft's September 2026 V2 Exchange Server security updates add CVE-2026-96940 for Exchange SE, 2019 and 2016. Install them now.
AWS Fixes Loom for AWS Admin Takeover and SageMaker Unified Studio Code Execution Flaws Loom for AWS authentication bypass CVE-2026-103956 and SageMaker Unified Studio command injection 
  • Vulnerability Report

AWS Fixes Loom for AWS Admin Takeover and SageMaker Unified Studio Code Execution Flaws

Do Son October 2, 2026 0

AWS fixes Loom for AWS admin takeover CVE-2026-103956 and a SageMaker Unified Studio code execution bug, CVE-2026-104019. Patch now.
Digi DAL OS Vulnerability Lets Unauthenticated Attackers Run Root Commands Digi DAL OS vulnerability CVE-2026-75937 command injection in Digi Accelerated Linux web administration on IX, EX and TX routers
  • Vulnerability Report

Digi DAL OS Vulnerability Lets Unauthenticated Attackers Run Root Commands

Do Son October 2, 2026 0

Digi DAL OS vulnerability CVE-2026-75937 (CVSS 9.4) lets attackers run root commands on Digi Accelerated Linux devices. Patch now.
Chrome Security Update Fixes Critical WebGL Flaw and 10 Other Bugs Chrome security update for Chrome 154 fixing CVE-2026-103628 WebGL sandbox escape and CVE-2026-103631 WebRTC flaw
  • Vulnerability Report

Chrome Security Update Fixes Critical WebGL Flaw and 10 Other Bugs

Do Son October 2, 2026 0

Chrome security update: Chrome 154 fixes 11 flaws, including critical WebGL sandbox escape CVE-2026-103628. Update your browser now.
GitLab Patches Critical AI Gateway Flaw That Lets Duo Users Run Commands GitLab AI Gateway vulnerability CVE-2026-90970 lets Duo Agent Platform users escape the prompt template sandbox
  • Vulnerability Report

GitLab Patches Critical AI Gateway Flaw That Lets Duo Users Run Commands

Do Son October 2, 2026 0

GitLab AI Gateway vulnerability CVE-2026-90970 (CVSS 9.9) lets Duo Agent Platform users run commands. Upgrade self-hosted gateways now.
Patched NetScaler Appliances Keep Rebooting as Citrix Flags SAML Authentication Issue NetScaler SAML authentication issue causing patched NetScaler appliances to reboot after CVE-2026-88771 and CVE-2026-88772 exploitation
  • Vulnerability Report

Patched NetScaler Appliances Keep Rebooting as Citrix Flags SAML Authentication Issue

Do Son October 2, 2026 0

Citrix flags a NetScaler SAML authentication issue as patched NetScaler appliances reboot after CVE-2026-88771 attacks. Check your config.
Seven TP-Link Vulnerabilities Hit Tapo Cameras, Archer and Deco Routers TP-Link vulnerabilities and Tapo camera vulnerabilities CVE-2026-102369 in Tapo C200, Archer AX90 and Deco M9 Plus
  • Vulnerability Report

Seven TP-Link Vulnerabilities Hit Tapo Cameras, Archer and Deco Routers

Do Son October 2, 2026 0

TP-Link vulnerabilities include Tapo camera vulnerabilities like CVE-2026-102369 (CVSS 8.7) plus router and Deco flaws. Update firmware now.
Moxa MGate Vulnerabilities Put Industrial Protocol Gateways at Risk Moxa MGate vulnerabilities CVE-2026-86325 and CVE-2026-86326 in MGate protocol gateway firmware
  • Vulnerability Report

Moxa MGate Vulnerabilities Put Industrial Protocol Gateways at Risk

Do Son October 2, 2026 0

Moxa MGate vulnerabilities CVE-2026-86325 (CVSS 9.4) and CVE-2026-86326 hit MGate protocol gateway firmware. See affected versions and fixes.
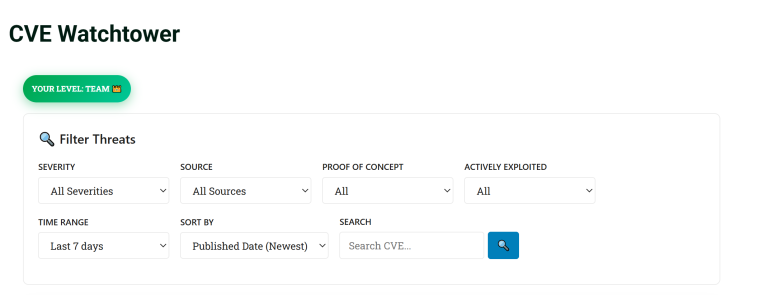
CVE Watchtower User Guide CVE Watchtower User Guide
  • How To

CVE Watchtower User Guide

Do Son October 2, 2026 0

CVE Watchtower tracks new CVEs for the specific vendors and products you choose, scores them for severity and real-world exploitation
Stirling PDF RCE CVE-2026-85714: Details and PoC Publicly Disclosed Stirling PDF RCE CVE-2026-85714 proof-of-concept publicly disclosed
  • Vulnerability Report

Stirling PDF RCE CVE-2026-85714: Details and PoC Publicly Disclosed

Do Son October 2, 2026 0

Details and a PoC are public for CVE-2026-85714, a 9.1 Stirling PDF RCE via crafted SQL import. Upgrade to version 2.13.2 now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    Admin intel📅 Updated: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2026-97229CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-76418CVSS 8.6
    A vulnerability in the Remote Access SSL VPN service of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-116690CVSS 7.5
    MLflow is an open source AI engineering platform for agents, large language models, and machine learning models. From...
    Admin intel📅 Updated: Oct 28, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-90865CVSS 9.0
    An OS command injection vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90866CVSS 9.1
    A path traversal vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows could...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90868CVSS 9.9
    An OS command injection vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows...
    📅 Updated: Oct 30, 2026
  • CVE-2026-93680CVSS 9.8
    IBM Langflow OSS 1.0.0 through 1.12.8 could allow a remote attacker to bypass security restrictions due to improper...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90717CVSS 9.1
    Dell PowerProtect Data Domain Management Center, Feature Release versions 7.7.1.0 through 8.8, LTS2024 release versions 7.13.1.0 through 7.13.1.80,...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90863CVSS 9.1
    Missing authorization in the administrative interface of Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90864CVSS 9.1
    A path traversal vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows could...
    📅 Updated: Oct 30, 2026
  • CVE-2026-87302CVSS 9.1
    Vulnerability in the Oracle WebLogic Server product of Oracle Fusion Middleware (component: Core). Supported versions that are affected...
    📅 Updated: Oct 30, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.