INJ3CTOR3 FreePBX Malware Steals 17 Configuration Files for Off-Box Toll Fraud
 Do Son
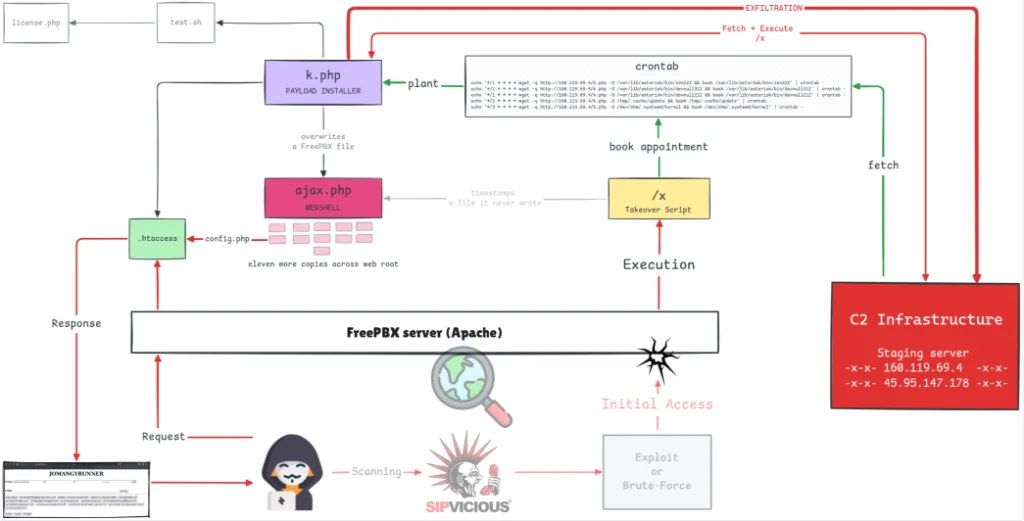
INJ3CTOR3 attack chain, September generation. (Source: 0x1da5 GitHub)
At a Glance
| Malware Family | INJ3CTOR3 FreePBX malware (JOMANGY and ZenharR PHP webshells, /x Bash takeover script, and k.php credential uploader) |
| Threat Actor | Confirmed as INJ3CTOR3 (financially motivated VoIP toll-fraud operator active since 2020; collector path linked to the 2020 “Hima” handle) |
| Target / Victims | Asterisk-based FreePBX, Issabel, and Elastix phone servers (over 900 compromised FreePBX hosts tracked by Shadowserver in February 2026; over 700 still infected in May 2026) |
| Delivery Vector | Exploitation and brute-forcing of internet-facing PBX management panels (including CVE-2019-19006 and CVE-2025-57819) |
| Key Capabilities | Every-minute exfiltration of 17 PBX config files, 6-channel self-healing persistence, forged admin sessions, direct Asterisk trunk injection |
TL;DR
Cyble researchers discovered that the latest INJ3CTOR3 FreePBX malware wave steals 17 configuration files from compromised voice servers every minute. By exfiltrating SIP trunk, database, and mail secrets, the JOMANGY INJ3CTOR3 FreePBX malware allows attackers to place fraudulent phone calls even after administrators wipe the infected server. Consequently, defenders must rebuild compromised FreePBX, Issabel, and Elastix systems and rotate all 17 credential sets with their telecom carriers.
Delivery and Attribution
The threat actor tracked as INJ3CTOR3 has targeted Asterisk-based phone systems for international toll fraud since at least November 2020. At that time, Check Point Research documented the group exploiting CVE-2019-19006 in FreePBX. Subsequently, Palo Alto Networks Unit 42 tracked related Elastix attacks in 2022, and Fortinet analyzed the group’s EncystPHP webshell in January 2026. According to Shadowserver Foundation telemetry cited by researchers, more than 900 FreePBX servers were compromised in February 2026, and over 700 of those hosts remained infected in May 2026 despite patches for flaws like CVE-2025-57819.
Confirmed Attribution
Confirmed attribution ties the September 2026 staging artifacts directly to INJ3CTOR3. Specifically, the new upload endpoint uses the directory name hima_data, which matches the backdoor account hima created by the takeover script. Furthermore, that name links back to a 2020 Telegram user named Hima who shared a SIP cracking tool that saved outputs as HimaResults.
Infection Chain
Once the attackers breach an exposed PBX interface, they run a takeover script that expanded from 367 lines in April 2026 to 620 lines in September 2026. Most of the new code deletes rival web shells, removes competing SSH keys, and blocks rival command servers so INJ3CTOR3 retains exclusive control of the phone system. Next, the script establishes six self-healing persistence channels across cron jobs, shell profile scripts, immutable crontab backups, and 18 disguised operating system and MySQL backdoor accounts.
Rotated Hashes and Hidden Webshells
The installer deploys both the ZenharR toolkit and the JOMANGY INJ3CTOR3 FreePBX malware across multiple web root directories. To defeat static file scanners, each payload hides behind double Base64 encoding and a ROT13 cipher. In the September 2026 build, the operator rotated the shared MD5 password gate hash and replaced the static webshell watermark with a unique string per build.
In addition, the attackers use Apache .htaccess rewrite rules to route requests containing an encoded space character directly to the hidden webshell without recording the shell filename in web access logs. Behind the password gate, the webshell uses FreePBX’s internal user class to forge an administrator session without needing a valid password. Meanwhile, the attackers write rogue SIP trunks straight into Asterisk configuration files on disk so the trunks never appear inside the FreePBX web console.
Command-and-Control and Data-Exfiltration Behavior
In September 2026, the operator split command-and-control traffic across two staging servers, using one host for plain-text commands and a second host for Base64-encoded stagers. More importantly, the secondary payload script named k.php now ends with two Base64-encoded lines that each run 17 curl commands. Because cron jobs fetch and run k.php every 60 seconds, the INJ3CTOR3 FreePBX malware uploads 17 sensitive configuration files to both staging servers every single minute.
The stolen files cover chan_sip and PJSIP trunk secrets, Asterisk Manager Interface credentials, MySQL database passwords, Issabel and Elastix settings, and Postfix SMTP mail relay logins. According to the Cyble research report, “With a stolen trunk secret, the operator can register to the carrier from any machine and call as the victim, leaving nothing on the host, unless the carrier also restricts the trunk to the victim’s IP addresses. A successful disinfection stops the first route; only rotation stops the second.” Worse still, if an administrator rotates passwords while the server is still infected, the minute-by-minute cron job sends the new secrets straight to the attacker.
Defense and Detection Guidance
Because the six persistence layers rebuild one another within minutes, partial cleanup fails. As the researchers warned, “Anyone running FreePBX, Issabel, or Elastix who suspects compromise must rotate the secrets in 17 configuration files, and only after the host is clean.” Defenders should first isolate the PBX from the internet and preserve crontabs, user files, and file attribute listings for forensic review.
Next, administrators should rebuild the server from a clean image or clear all cron jobs, shell profiles, and rogue UID-0 accounts simultaneously from the operating system layer up. To spot hidden trunks that bypass the web GUI, engineers should run the Asterisk command-line queries pjsip show endpoints and pjsip show registrations. Finally, organizations must rotate all SIP trunk, AMI, MySQL, and SMTP passwords and ask their telecom carriers to restrict SIP trunk registrations to known corporate IP addresses.
Support Our Threat Intelligence
Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
