 Do Son
TL;DR
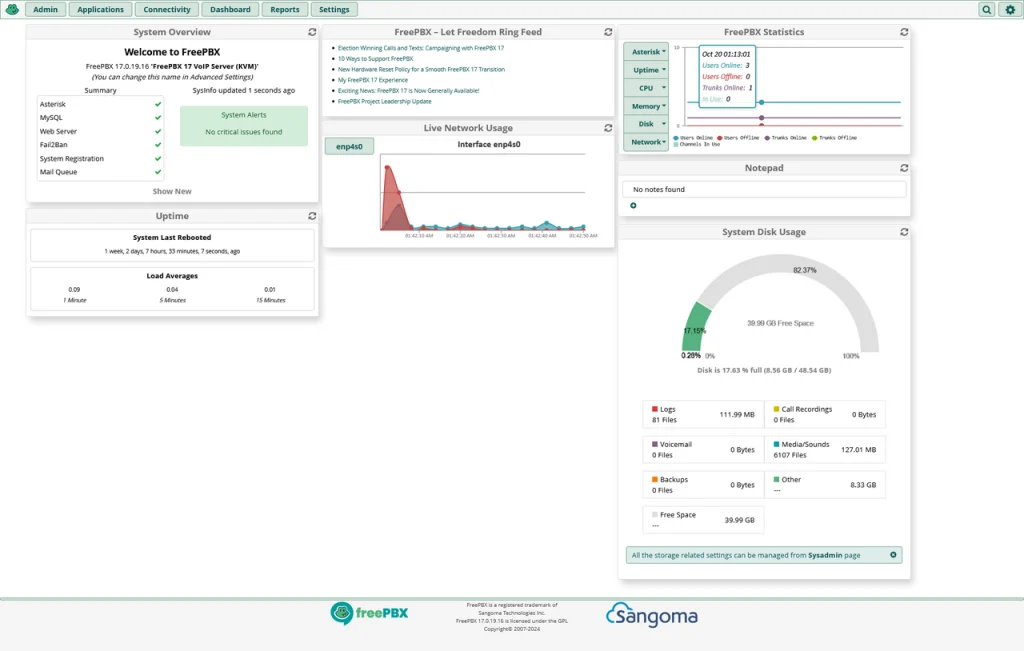
FreePBX maintainers released security advisories, resolving two critical FreePBX vulnerabilities in the User Manager module. As a result, these flaws allow attackers to brute-force accounts through a credential oracle and let authenticated users overwrite administrator passwords. System administrators must update their userman packages immediately.
This premium content is securely locked. You must upgrade your subscription to access the full threat intelligence report, including detailed mitigation steps, deep-dive analysis, and active exploitation metrics. Your attempt to inspect the DOM will only reveal this placeholder text. Please support our work to read the actual coverage.
This premium content is securely locked. You must upgrade your subscription to access the full threat intelligence report, including detailed mitigation steps, deep-dive analysis, and active exploitation metrics. Your attempt to inspect the DOM will only reveal this placeholder text. Please support our work to read the actual coverage.
This premium content is securely locked. You must upgrade your subscription to access the full threat intelligence report, including detailed mitigation steps, deep-dive analysis, and active exploitation metrics. Your attempt to inspect the DOM will only reveal this placeholder text. Please support our work to read the actual coverage.
Unlock Premium Threat Intelligence
This is a premium content. Upgrade to Pro or Team to unlock full access and remove all reading restrictions.
 Buy Me a Coffee
