 Do Son
TL;DR
Kaspersky researchers have disclosed an Intelbras camera vulnerability, a denial-of-service bug that lets anyone on the local Wi-Fi network take IP cameras offline. The flaw sits in an unauthenticated firmware update endpoint. Intelbras fixed it in firmware R.260804, and MITRE scored it 5.1 (Medium) under CVSS 4.0.
An attacker on the same network can send one request that forces the camera to reboot and drop offline. Repeating the request keeps it offline indefinitely. Update your Intelbras camera firmware to R.260804 or later.
Why It Matters
According to Kaspersky, the Intelbras Mibo Smart app “has over 4,000,000 downloads.” Brazil represents the largest user base, followed by Paraguay, Ecuador, Colombia and Argentina.
A camera that goes dark can’t record or stream. As Kaspersky explains, the outage prevents “legitimate users from accessing live monitoring or managing the camera.” This denial-of-service condition leaves the area unmonitored while the device stays down.
How the Attack Works
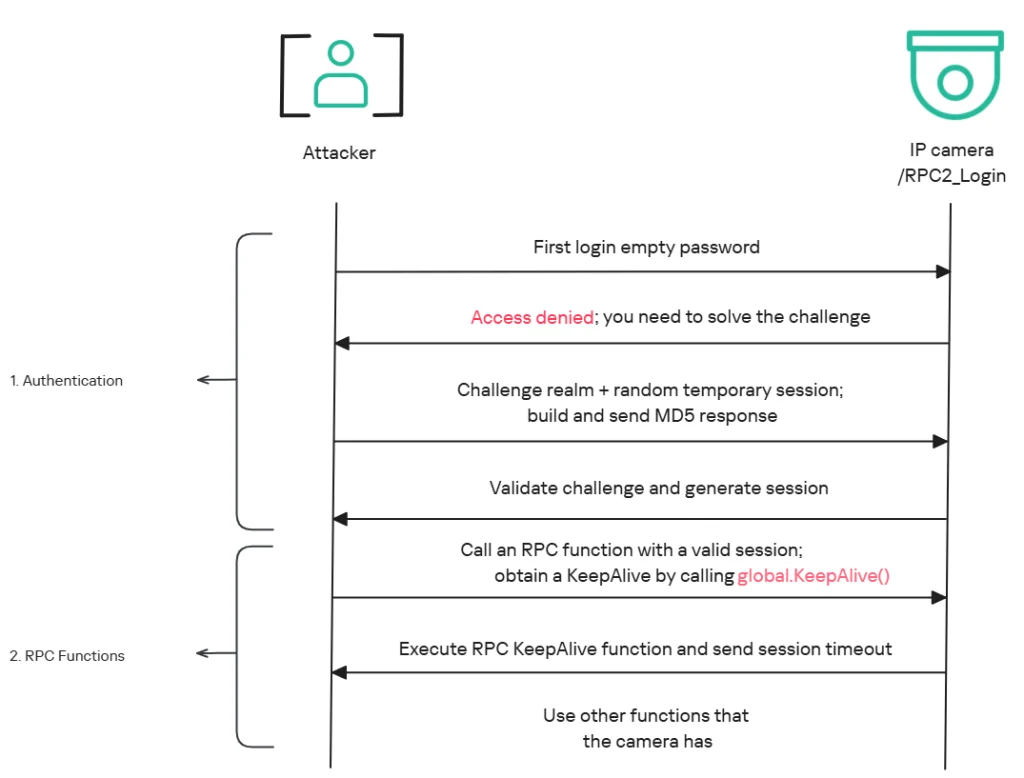
Normally, Intelbras cameras require a challenge-response login before most actions. However, the firmware upgrade route skipped that check entirely. Kaspersky says the endpoint “lacks authentication checks” and “fails to verify whether the firmware is actually valid before initiating the upgrade process.”
As a result, any request to that endpoint starts an upgrade and a reboot. The camera then “enters reboot mode and eventually shuts down, appearing offline to the user.” A single request disrupts the device for about a minute. Meanwhile, periodic requests keep it offline for as long as the attacker wants.
Kaspersky demonstrated the attack with its own script on an iM3B-C camera. The attacker needs access to the local network, so remote internet attacks are not part of the reported scenario. So far, no exploitation in the wild has been reported.
Affected Versions
Kaspersky tested firmware v240927 on the iM3B-C, the latest version at the time. According to Intelbras, the same firmware also runs on these models:
- iMX C and iM4 C
- iM5 SC and iME 360 C
- iM7+ FC
Patch and Mitigation
Intelbras worked with its OEM vendor to fix the flaw. The new firmware “requires authentication to initiate an update through this endpoint.” Therefore, users should check their installed firmware version and update to R.260804.
In addition, protect your Wi-Fi with a strong password and keep cameras on a separate guest or IoT network. That limits who can reach this Intelbras camera vulnerability before you patch.
MITRE has assigned candidate ID CAN-2026-2035970, and a final CVE ID is still pending.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
