 Do Son
A GL.iNet cloud zero-day in GoodCloud remote management was exploited to plant malware on routers and KVMs. How to check your device and patch.
IoT security
Zyxel firmware vulnerability CVE-2026-79614 (CVSS 9.8) allows unauthenticated command execution, and CVE-2026-86676 adds command injection. Patch now.
Zenitel vulnerabilities fixed: CVE-2026-95377 gives root on intercoms via DHCP, and a CVE-2026-95615 chain roots Zenitel Connect. Update to 1.11.0.
Axis fixes 15 flaws, led by AXIS Camera Station bug CVE-2026-13312 (CVSS 9.9) that could compromise a system. AXIS OS updates also released.
CERT/CC details six FrodoBots EarthRover vulnerabilities, including root remote code execution via MQTT. Patch status, risks and mitigations.
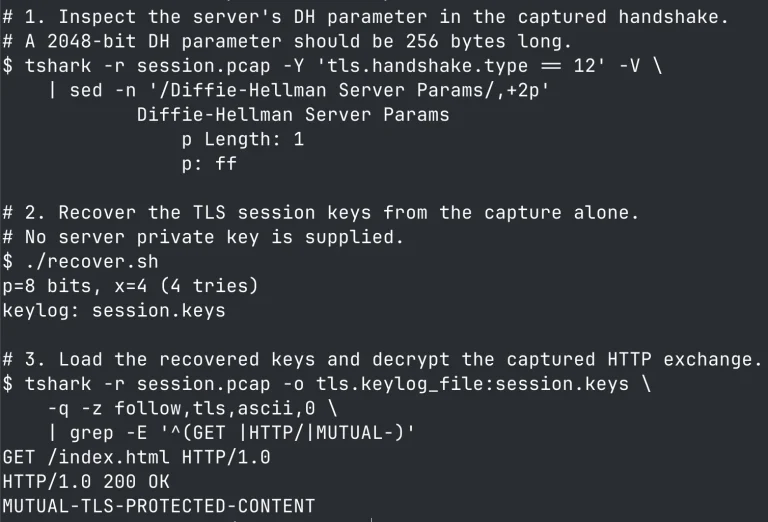
FoxIO releases details and proof-of-concept code for three GoAhead TLS vulnerabilities, including a CVSS 9.1 revoked-certificate bypass. Patch to 6.1.1.
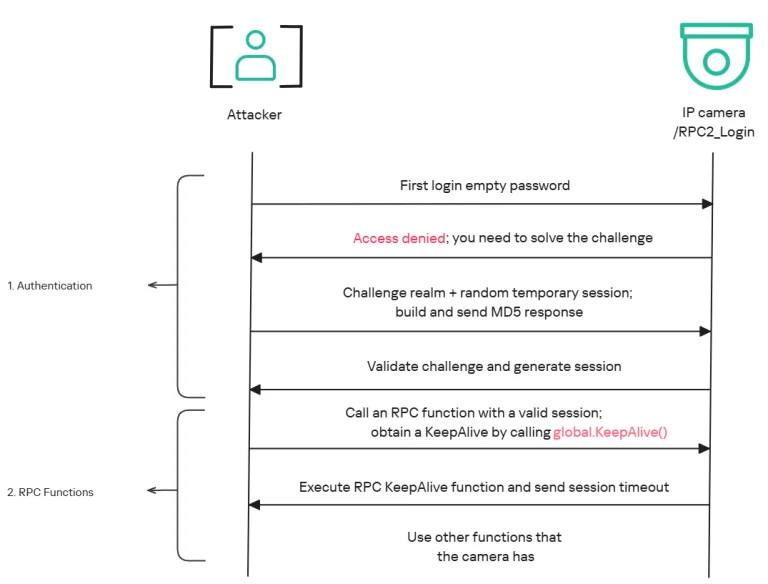
An Intelbras camera vulnerability enables a denial-of-service attack that knocks Mibo cameras offline from the local network. Update to R.260804.
Discover the new critical Tapo C325WB vulnerabilities exposing TP-Link cameras. Learn how to patch these Tapo C325WB vulnerabilities and secure your video.
The ClingSTUN backdoor hijacks unpatched IoT devices and hides in traffic to public STUN servers. Learn how it spreads and how to stop it.
Digi DAL OS vulnerability CVE-2026-75937 (CVSS 9.4) lets attackers run root commands on Digi Accelerated Linux devices. Patch now.
TP-Link vulnerabilities include Tapo camera vulnerabilities like CVE-2026-102369 (CVSS 8.7) plus router and Deco flaws. Update firmware now.
Critical Eufy robot vacuum vulnerabilities expose the Omni C20 and X10 Pro to OS command injection. Patch CVE-2026-93289 and CVE-2026-93291 immediately.
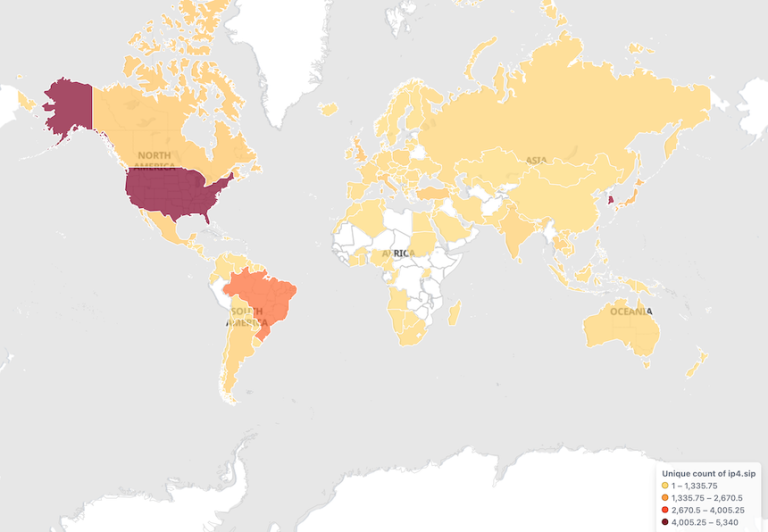
CVE-2026-87827 (CVSS 10) is a KGUARD DVR vulnerability exploited by the Mirai botnet for unauthenticated RCE and complete device compromise.

Operation CameraSwarm compromised 14,500+ Dahua cameras in 35 days. Hunt.io traced the camera hacking campaign to an exposed operator directory.

D-Link fixes 15 flaws in the DWR-M961 router, including D-Link router command injection and buffer overflow bugs like CVE-2026-71958. Update firmware now.

CVE-2026-68067 (CVSS 9.8) lets attackers control user accounts on the Mira Hormone Monitor by bypassing the cloud login. Eight flaws total.

TP-Link patched 5 TP-Link router vulnerabilities in ISP-managed mesh, router, and modem lines, including auth bypass and command injection.
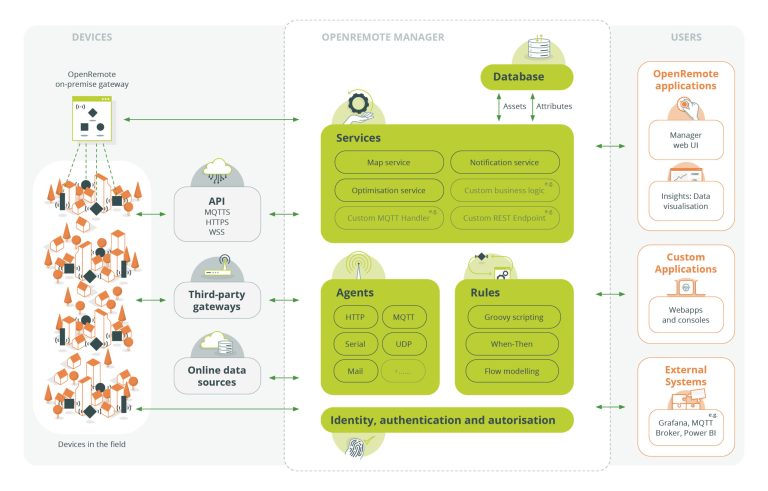
An OpenRemote vulnerability, CVE-2026-66013 (CVSS 9.3), enables unauthenticated asset takeover. Full advisory details are now public. Patch to 1.26.2.

TP-Link Kasa vulnerability CVE-2026-9770 (CVSS 8.6) lets local attackers intercept admin credentials on EC70 and EC71 cameras. Update firmware now.
Apache IoTDB fixes five flaws in its time-series database, including privilege escalation and an unauthenticated DoS. Upgrade to 2.0.10 now.
Three Apache IoTDB vulnerabilities include a critical path traversal (CVE-2026-24014) and an authentication bypass. Upgrade to 2.0.8 now.
CISA warns of a Gardyn IoT Hub flaw. CVE-2026-13768 (CVSS 10) enables unauthenticated remote code execution on smart garden devices. Update now.