 Do Son
Apache Wicket vulnerabilities: a security update fixes 19 flaws, including CVE-2026-84170 upload DoS and XSS bugs. Upgrade to 8.20.0, 9.25.0 or 10.12.0.
Denial of Service
A Bitcoin Core DoS vulnerability allows remote peers to trigger out-of-memory crashes on Windows, macOS, and BSD nodes via TCP socket handling errors.
Apache Kafka fixes 12 vulnerabilities, including CVE-2026-110985, which skips JWT signature verification and grants full cluster access. Patch now.
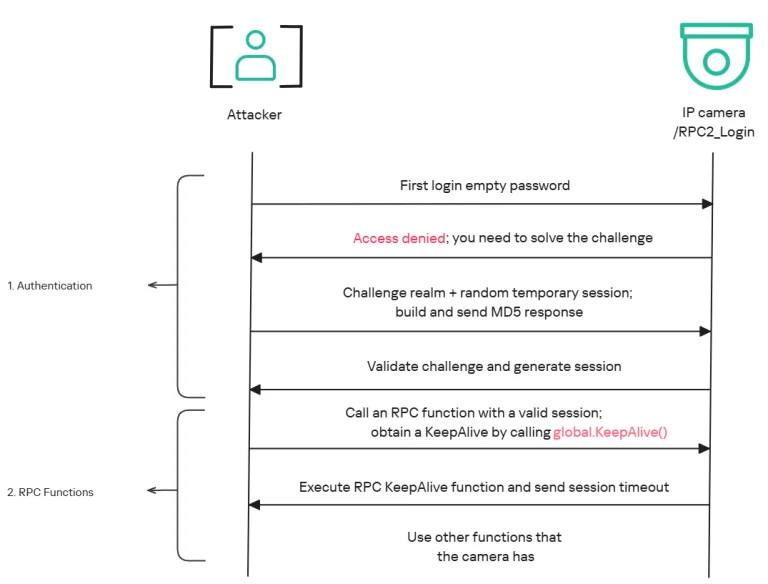
An Intelbras camera vulnerability enables a denial-of-service attack that knocks Mibo cameras offline from the local network. Update to R.260804.
Body-parser vulnerability CVE-2026-111181 (CVSS 7.5) enables Express denial of service with one request. Upgrade to body-parser 2.4.0 or 1.20.9.
Cisco fixes 13 Snort 3 vulnerabilities, including CVE-2026-20043 and denial of service flaws affecting FTD, Meraki MX and IOS XE.
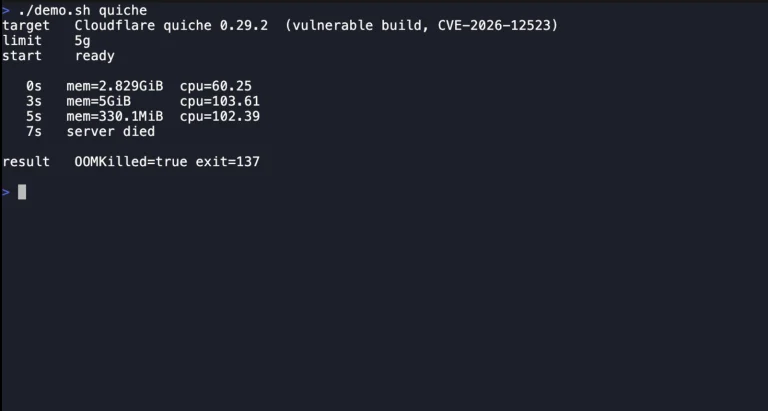
FoxIO released details and PoC code for a QPACK amplification attack that can crash HTTP/3 servers, including quic-go, quiche, lsquic and Bun.
ISC fixes four BIND 9 vulnerabilities, including CVE-2026-94300 memory corruption and denial of service bugs. Upgrade to BIND 9.20.30 or 9.21.27.
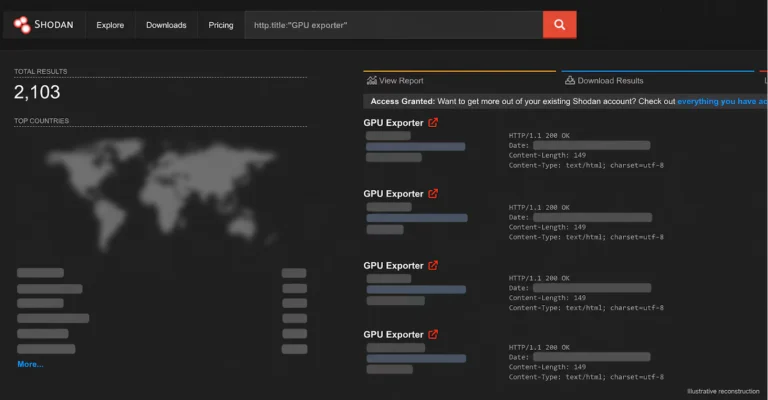
CVE-2026-47483 in NVIDIA DCGM Exporter lets unauthenticated attackers crash GPU monitoring. Over 2,000 exposed servers found. Patch to 4.8.2.
The WordPress 7.1.3 security update is a WordPress security release that fixes stored XSS, SQL injection and more. Update your site now.
Apache Thrift 0.25.0 fixes 61 Apache Thrift vulnerabilities, including critical heap overflow CVE-2026-91135. Upgrade every binding now.
Struts 7.4.0 fixes four Apache Struts vulnerabilities, including OGNL injection CVE-2026-104711 and a REST plugin DoS. Upgrade now.
Citrix NetScaler CVE-2026-88779 is exploited in the wild against NetScaler SAML authentication setups. Upgrade to 14.1-73.41 now.
OpenSSL patched 14 OpenSSL vulnerabilities, including high-severity DTLS flaw CVE-2026-84782 that can leak heap memory. Upgrade to 4.0.3 now.
New Apache Qpid Broker-J vulnerabilities, including CVE-2026-92609, CVE-2026-92573, and CVE-2026-92564, expose brokers to DoS. Patch immediately.
Apache patched 15 Apache Tomcat vulnerabilities in version 11.0.26. Update to secure your servers against HTTP/2, AJP, and WebSocket DoS flaws today.
NVIDIA fixed critical Triton Inference Server vulnerabilities. Patch your Triton Inference Server vulnerabilities now to stop denial of service attacks.
MongoDB fixed 24 MongoDB Server vulnerabilities, including a critical auth bypass (CVE-2026-82067) and unauthenticated denial of service flaws. Patch now.
A public announcement exists for the Cisco Secure Email vulnerability pair in S/MIME decryption, plus a Cisco phone SIP denial-of-service flaw.
Apache Tomcat fixed 11 vulnerabilities on August 25, 2026, including auth bypass (CVE-2026-68569) and HTTP/2 DoS flaws. Update to 11.0.25 now.
The August 2026 OpenSSL security update fixes 9 flaws, including a QUIC double free (CVE-2026-18798) and a CMS heap overflow. Patch now.
Four Spring vulnerabilities hit Spring Data REST and Spring AI, including CVE-2026-47849, a privilege escalation flaw. Patch to the fixed versions now.