
 Do Son
Splunk releases coordinated patches for CVE-2026-20240 and adjacent flaws exposing raw session cookies, data filters, and triggering server DoS.
Denial of Service

PowerDNS coordinates patches for CVE-2026-42001 and adjacent flaws that trigger server crashes, GSS-TSIG memory corruption, and view data leaks. Patch now!

F5 warns of a critical 9.2 CVSS flaw (CVE-2026-8711) in NGINX JavaScript (njs). Unauthenticated attackers can trigger heap overflows and potential RCE.

Critical 18-year-old "NGINX Rift" flaw CVE-2026-42945 is under active exploitation. Learn how to patch your proxies and block the unauthenticated heap overflow.

Protect your app from CVE-2026-23870. Learn how this high-severity React Server Components DoS flaw crashes servers and how to patch your React 19 build today.
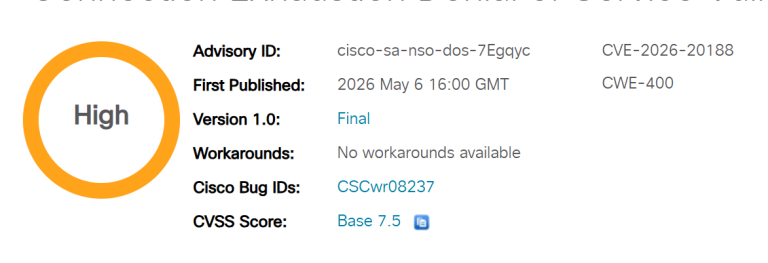
Cisco warns of a critical DoS flaw (CVE-2026-20188) in CNC and NSO. Unauthenticated attackers can freeze network management. Patch to CNC 7.2 or NSO 6.4.1.3 now!

Bitcoin Core v29.0 fixes a high-severity use-after-free bug (CVE-2024-52911) that could allow attackers to remotely crash nodes. Upgrade your node today.

Apache Thrift v0.23.0 fixes critical Rust DoS, Java MitM, and Node.js path traversal flaws. Secure your cross-language microservices and upgrade immediately!

Apache Neethi v3.2.2 patches critical flaws, including an exponential complexity attack and infinite loops. Secure your Java web services and patch today!

libmodsecurity3 faces critical 8.2 & 7.5 CVSS flaws. A simple one-line script can crash WAF worker processes. Protect your server by upgrading to v3.0.15 now.

NVIDIA patches critical flaws in KAI Scheduler and CUDA-Q. CVE-2026-24189 and CVE-2026-24177 risk data leaks and DoS. Secure your GPU workloads—update today!
Cisco alerts on a critical 9.9 CVSS flaw in ISE. Even "Read-Only" admins can escalate to root and trigger a total network lockout. Patch immediately.
Apache ActiveMQ patches critical TLSv1.3 memory exhaustion (CVE-2026-39304) and an MQTT regression. Upgrade to 6.2.4 or 5.19.5 to secure your broker!
React patches a 7.5 CVSS DoS vulnerability in Server Components (CVE-2026-23869). Stop CPU exhaustion attacks—update your 19.x dependencies now!
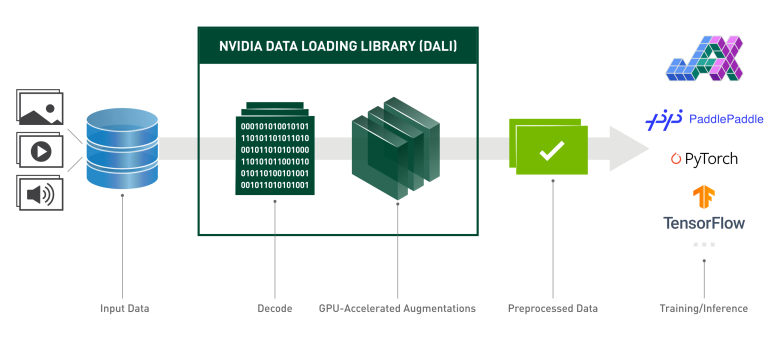
NVIDIA patches high-severity flaws in DALI and Triton Inference Server. Prevent arbitrary code execution and DoS—upgrade to DALI v2.0 and Triton r26.02 now.

Apache Traffic Server fixes two CVSS 7.5 flaws (CVE-2025-58136 & CVE-2025-65114). Prevent DoS and request smuggling—update to 10.1.2 or 9.2.13 now!

TP-Link warns of high-severity flaws (CVSS 8.7) in Tapo C520WS cameras. Attackers can bypass auth or blind your security. Update to firmware 1.2.4 now!
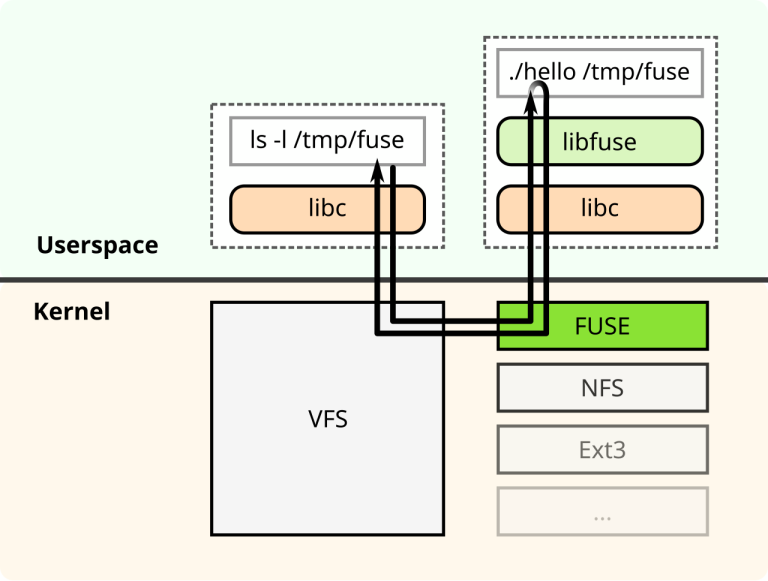
Researchers uncover two flaws in libfuse's io_uring transport (CVE-2026-33150 & 33179). Impacting Kubernetes CSI drivers, these bugs allow RCE and DoS. Patch now!

strongSwan fixes a high-severity DoS flaw (CVE-2026-25075) in eap-ttls. Unauthenticated actors can crash VPN gateways. Patch now to stay protected!

ISC warns of a high-severity stack overflow in Kea DHCP (CVE-2026-3608). Remote attackers can crash daemons and kill network services. Upgrade to 3.0.3 now.

Cisco alerts of public flaws in IOS XE. Authenticated users can trigger a network-wide DoS or escalate privileges via the Lobby Ambassador API. Patch now.

NVIDIA issues critical updates for Megatron-LM, Triton, and NeMo to fix RCE and DoS flaws. Upgrade now to secure your AI development and inference servers.