
 Do Son
F5 warns of high-severity flaws in NGINX Plus and Open Source (CVSS 8.8). Fixes for DAV and MP4 buffer overflows are now available. Update your servers today!
Denial of Service

Squid Proxy patches critical 9.2 CVSS DoS and memory leak flaws in ICP. Standard access rules won't block the attack—upgrade to version 7.5 now.

GitLab has released a critical security advisory alongside versions 18.10.1, 18.9.3, and 18.8.7 for its Community (CE)...
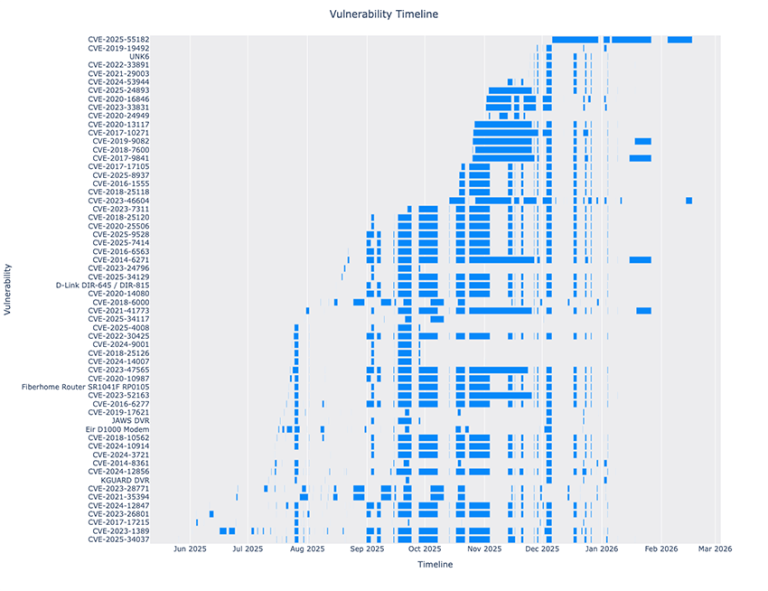
BitSight exposes RondoDox, a relentless IoT botnet using a "shotgun approach" with 174 exploits to hijack residential devices for massive DoS attacks.
GitLab issues urgent security updates (18.9.2, 18.8.6, 18.7.6) fixing critical XSS (CVE-2026-1090) and DoS flaws. Patch self-managed instances today.

Django releases security updates (6.0.3, 5.2.12, 4.2.29) to fix a Windows DoS flaw (CVE-2026-25673) and file permission risks. Upgrade your framework now.

FreeBSD patches a critical jail escape (CVE-2025-15576) and a kernel heap overflow (CVE-2026-3038). Learn how nullfs and routing sockets put hosts at risk.

Node.js DoS flaw CVE-2026-26278 in fast-xml-parser freezes event loops via XML entity expansion. 46M weekly downloads affected. Update to version 5.3.6.

HAProxy patches high-severity QUIC flaws CVE-2026-26080 & 26081. Remote attackers can crash servers via malformed packets. Update to v3.0.16 now.

MongoDB patches high-severity flaw CVE-2026-25611. Unauthenticated attackers can crash servers via memory exhaustion. Update to v8.2.4 or v8.0.18 now.

Critical PAN-OS flaw CVE-2026-0229 allows unauthenticated attackers to trigger reboot loops & maintenance mode via malicious packets. Patch immediately.

GitLab fixes critical CVE-2025-7659 (CVSS 8.0). Unauthenticated attackers can steal tokens via Web IDE. Update to v18.8.4 now to secure your code.

GnuTLS v3.8.12 fixes high-severity DoS flaws (CVE-2026-1584). Malicious TLS 1.3 handshakes can crash servers. Update now to prevent outages.

Apache HertzBeat flaw CVE-2026-24343 allows DoS via XPath injection. Vulnerable versions 1.7.1-1.7.9. Update to v1.8.0 immediately.

Axios flaw CVE-2026-25639 (CVSS 7.5) crashes Node.js servers via malicious JSON. Attackers use __proto__ to trigger DoS. Update to v1.13.5 now.

A 30-year-old heap overflow in libpng (CVE-2026-25646) exposes apps to DoS & RCE. The flaw affects all versions since inception. Update to v1.6.55 now.

Critical jsPDF flaws (CVE-2026-24133) allow XSS & DoS via malicious BMPs. Update to v4.1.0 immediately to prevent browser crashes and code injection.
Cisco patches critical flaws: CVE-2026-20098 allows root access in Meeting Management, while malicious invites crash TelePresence units. Update now.

New React Server Components flaw CVE-2026-23864 (CVSS 7.5) exposes apps to DoS attacks. Previous patches were incomplete. Update to v19.0.4+ now.

CVE-2026-0994 (CVSS 8.2) in Google Protobuf Python allows DoS via nested "Any" messages. Recursion limit bypass causes crashes. Update now.

Apache Karaf Decanter flaw CVE-2026-24656 allows unauthenticated attackers to crash the log collector via deserialization. Update to v2.12.0 immediately.

High-severity BIND 9 flaw CVE-2025-13878 allows remote server crashes via single packet. Update to v9.18.44 or v9.20.18 immediately to prevent DoS.