
 Do Son
NVIDIA Triton vulnerability CVE-2026-47627 scores CVSS 9.8. Learn how the denial of service flaw works and why you must update to 26.06 now.
Denial of Service

CVE-2026-71290 (CVSS 9.1) is an Apache HttpClient TLS vulnerability that lets attackers intercept and modify traffic via MITM attacks. Update to 5.6.4.

Apache Struts DoS flaws span CVE-2026-73633, CVE-2026-73634, and CVE-2026-73635, plus two JSON plugin bugs. Upgrade to 7.3.0.

Cisco confirms CVE-2026-20349, a Cisco ASA and FTD VPN vulnerability (CVSS 8.6), is exploited in the wild to crash firewalls. Patch now.

Cisco disclosed seven ClamAV vulnerabilities that let a remote attacker crash scanning via crafted files. Details are public. Patch now.
Five Erlang/OTP vulnerabilities include a critical TLS certificate bypass and several remote crash flaws. Update to the patched OTP releases now.
MongoDB patched 27 vulnerabilities across Server and Compass. The set includes memory corruption, RBAC bypass, and denial-of-service flaws. Update now.


An HTTP/2 DoS vulnerability lets unauthenticated attackers exhaust server memory via stalled flow control. CVE-2026-59762 and CVE-2026-59173 are patched.
Progress patched three MOVEit Transfer flaws, including a stored XSS bug (CVE-2026-11903). No exploitation is confirmed. Update now.

Two PHP flaws are patched. CVE-2026-12184 is a PHP remote DoS that crashes PHP-FPM, and CVE-2026-14355 causes memory corruption. Update PHP now.

Apache HttpComponents Core vulnerabilities CVE-2026-54399 and CVE-2026-54428 allow remote denial of service through memory exhaustion. Upgrade now.

Six NetScaler vulnerabilities allow denial of service, memory overreads, and an unauthenticated file read. Patch NetScaler ADC and Gateway now.

A critical Langflow file upload flaw (CVE-2026-55450) is public with a PoC, enabling unauthenticated denial-of-service and path disclosure. Patch 1.9.1.

Rockwell Automation vulnerabilities affect FactoryTalk Historian and FLEX I/O adapters, including a critical unauthenticated password-change flaw.

New updates address multiple Spring framework security vulnerabilities, resolving a critical authentication bypass threat and several denial of service bugs.

New Apache HTTP Server patches resolve multiple buffer overflow vulnerabilities. Upgrade your production infrastructure immediately to keep deployments secure.

Fix dangerous Apache MINA flaws immediately. Learn how a critical deserialization bypass and a DoS vulnerability leave Java applications exposed.

Protect your network from active CVE-2026-28318 exploitation. Apply patches for this critical Serv-U vulnerability before the June 19 deadline.

Recent updates address critical React Router vulnerabilities. Apply the latest React Router vulnerabilities patch to secure your web applications.
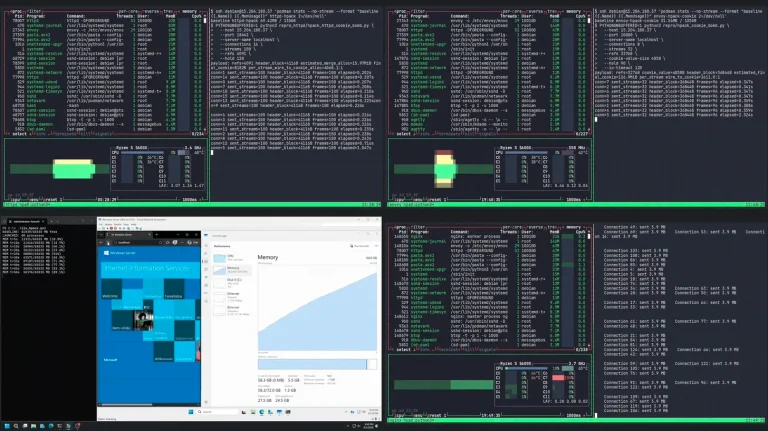
Researchers disclosed a public PoC for an HTTP/2 'bomb' that exhausts server resources and causes denial of service. Mitigation steps inside.