 Do Son
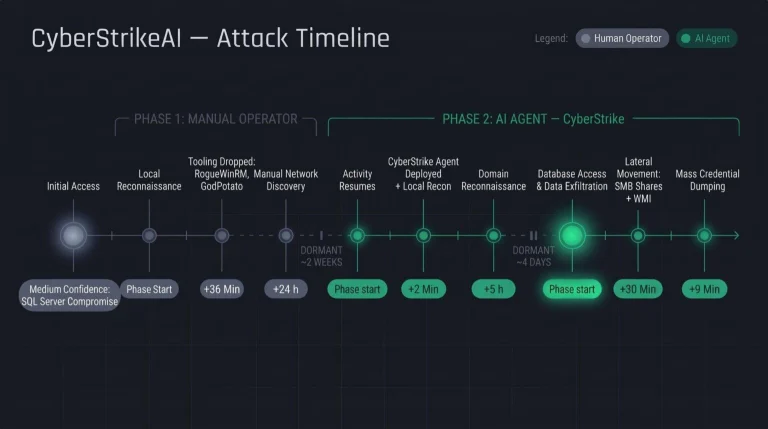
Kaspersky uncovered CyberStrikeAI framework attacks using AI to automate post-exploitation and compromise domains across education networks.
kaspersky
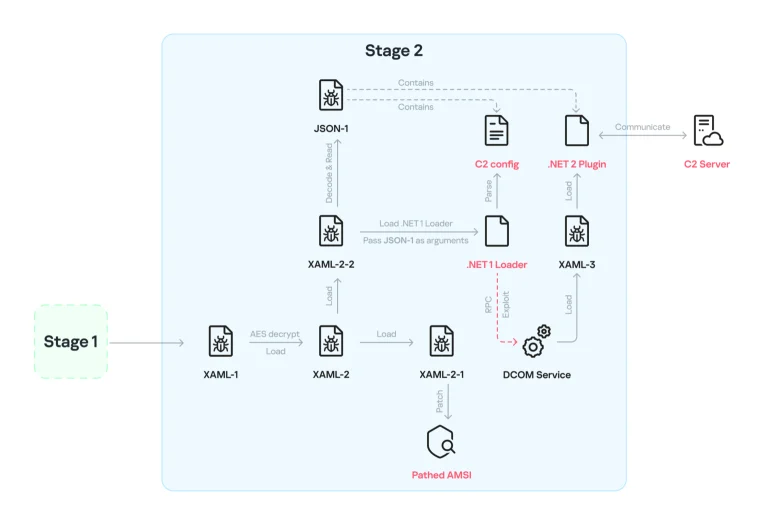
NetamLoader, a new XAML-based .NET loader, points to a supply chain attack on a custom Windows build used by government entities in Asia.
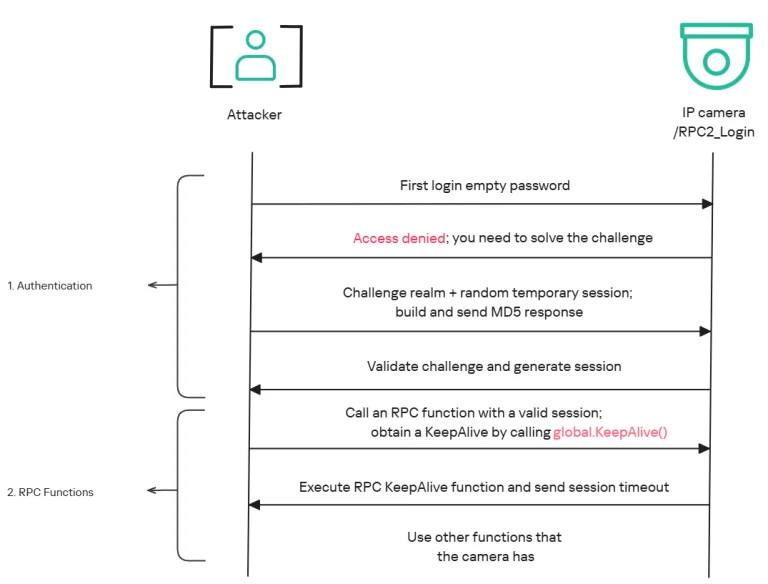
An Intelbras camera vulnerability enables a denial-of-service attack that knocks Mibo cameras offline from the local network. Update to R.260804.

Kaspersky uncovered the BlackX UEFI bootkit APT41 campaign bypassing Secure Boot via Baton Drop to spy on Central Asian diplomatic agencies.
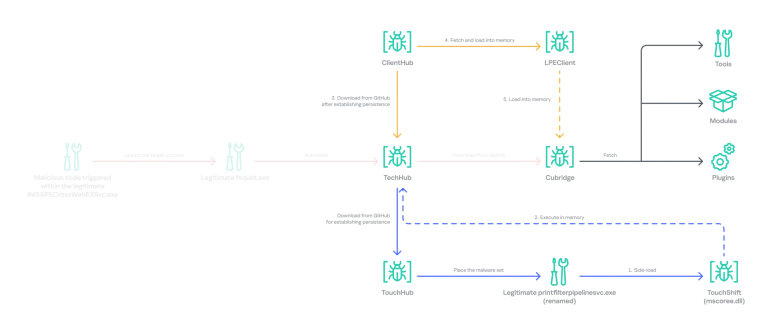
In Operation FlashHole, the Lazarus Group used AI-made lure sites, CrossWeb EX, and GitHub C2 to spy on South Korean firms. Here is how.
Microsoft details NeedyMantis malware, a modular backdoor that uses DLL sideloading to keep long-term access in telecom, academic, and government networks.
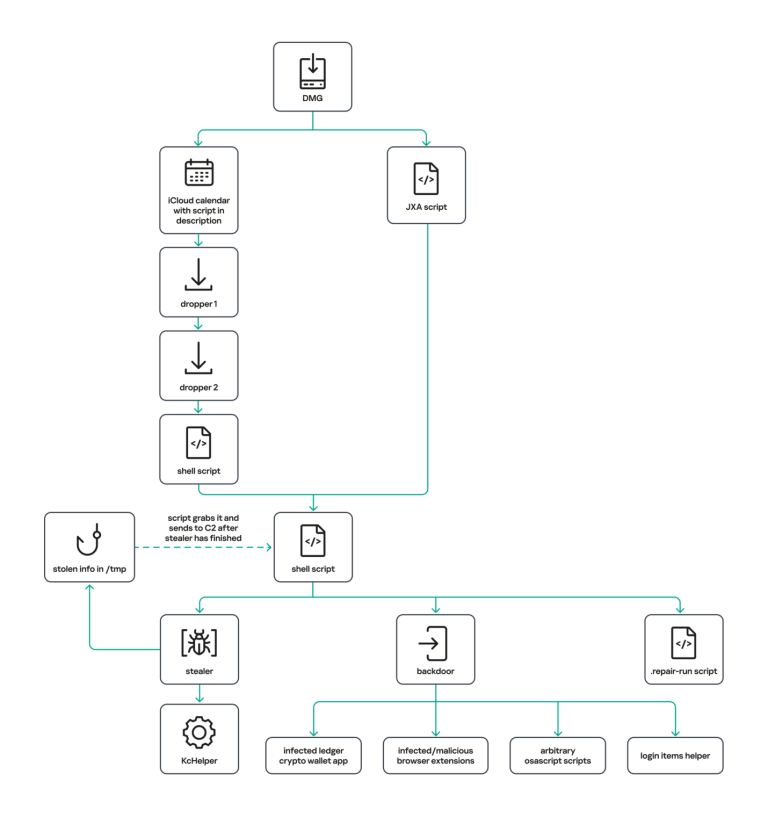
A new MacSync macOS infostealer spreads via fake apps. Learn how the MacSync macOS infostealer abuses iCloud to compromise Apple systems.
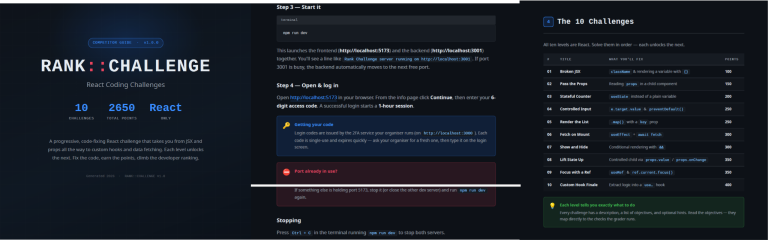
The suspected Mirage Kitten malware campaign targets developers in aviation and fintech with fake coding tests to deliver NodeRabbit and PollCat backdoors.
The Toy Ghouls backdoor hides C2 traffic in HiveMQ MQTT and Element messenger. See how the Bearlyfy group's custom malware works.
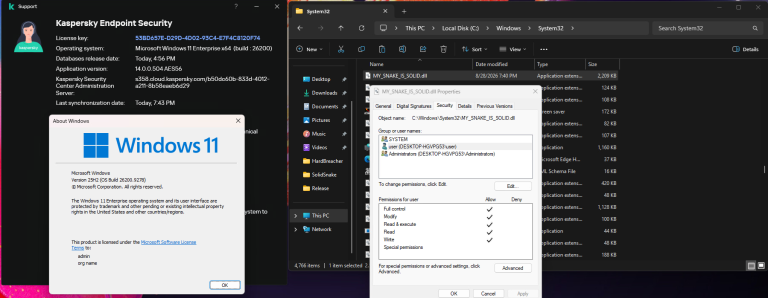
Discover the details of the experimental HardBreacher exploit targeting a potential zero-day vulnerability within Kaspersky Endpoint Security for privilege escalation.

Kaspersky uncovered the Armored Likho Still Toolkit. Read our Armored Likho Still Toolkit analysis to explore the Telegram stealer and audio spying tools.

Kaspersky analyzed the Project CAV3RN framework. Read our Project CAV3RN framework analysis to see how attackers abuse DNS and Google Apps Script.

GenieLocker ransomware hits Russia's manufacturing sector on Windows, Linux, and ESXi. Linked to the Toy Ghouls group, it leaves no ransom note.

Mirage Kitten malware, tied to the UNC1549 APT, hit aviation and telecom targets across the Middle East and Africa with new backdoors and tunnelers.
GoSerpent backdoor drives a patient cyber espionage campaign against Southeast Asian governments, stealing files and credentials since at least 2021.
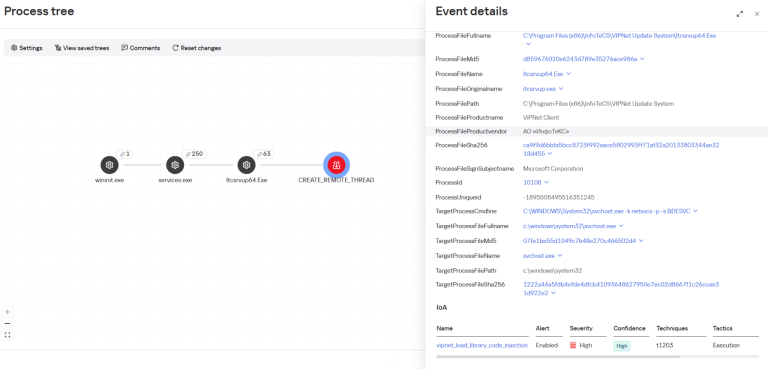
The HelloNet campaign spreads malware through the ViPNet update system, hitting Russian government and energy firms. Kaspersky suspects a China link.

Kaspersky uncovered OkoBot, a modular framework with 20+ payloads driving cryptocurrency wallet theft. Hundreds of victims sit across more than 25 countries.
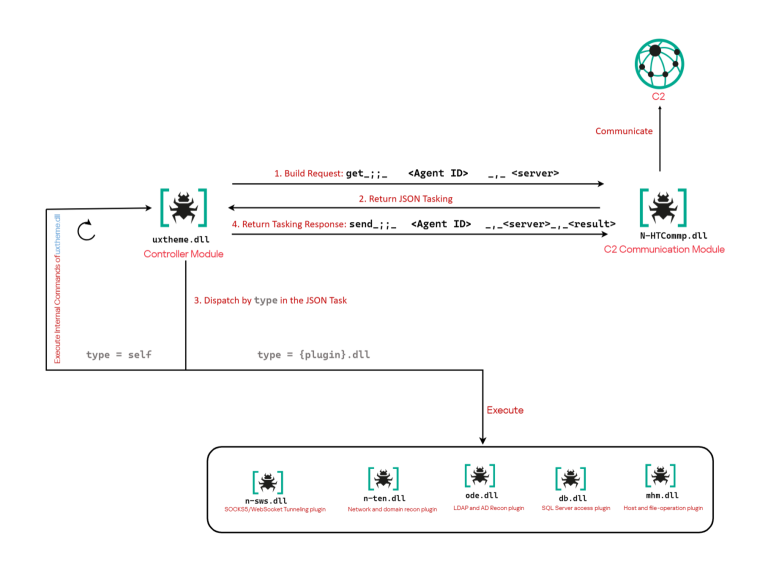
Kaspersky details Project CAV3RN, an OilRig-linked cyberespionage framework. Its new module hides C2 in Outlook calendar events, with DNS AAAA fallback.
A massive ScreenConnect AsyncRAT campaign uses SEO poisoning and spoofed websites to drop malicious installer archives via remote monitoring tools.

Kaspersky details The Gentlemen ransomware, a fast-growing RaaS group with new Go and C lockers, EDR killers, and worldwide victims. Here's how it works.
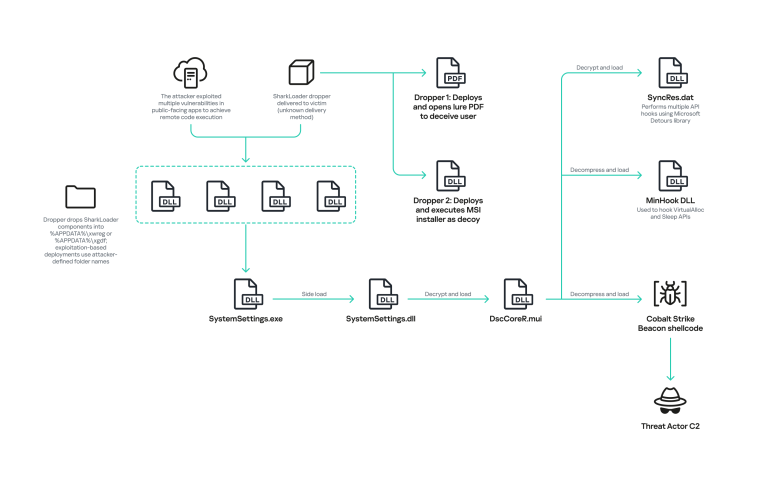
Kaspersky details SharkLoader malware, which deploys Cobalt Strike Beacon in the global StrikeShark campaign via DLL sideloading and exploited apps.

A new WhatsApp malware campaign uses a multi-stage VBScript infection chain to silently install RMM software on victim devices across multiple countries.