
 Do Son
Read the Kaspersky malware analysis revealing how the Argamal Trojan campaign targets adult gamers using stealthy COM hijacking.
kaspersky

Kaspersky reports a record surge in CVEs for Q1 2026. Discover how AI-driven exploits, authentication bypasses, and new C2 trends are reshaping cyber defense.

OceanLotus targets Python developers worldwide via PyPI supply chain attacks. New ZiChatBot malware hijacks Zulip APIs for invisible C2 traffic. Patch now!
Kaspersky warns that DAEMON Tools installers (v12.5) are trojanized with the QUIC RAT. Signed binaries are being used for global espionage. Update and audit now!

Scammers are leveraging Amazon SES and leaked IAM keys to bypass security filters. Learn how to protect your organization from this high-trust phishing surge.
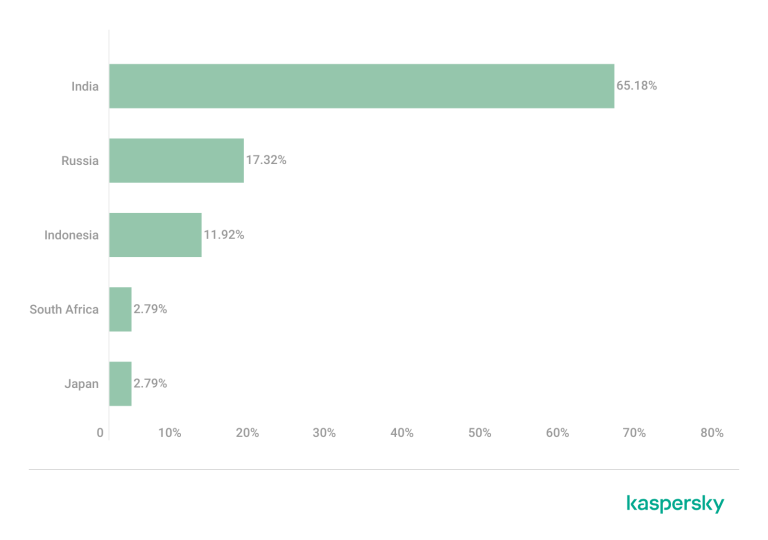
Silver Fox targets India and Russia with tax-themed phishing and the new ABCDoor backdoor. Learn how this Python-based threat hijacks screens and data.

Kaspersky reveals PhantomRPC, a novel Windows architectural flaw enabling LPE to SYSTEM. Microsoft denies a patch. Monitor SeImpersonatePrivilege now.
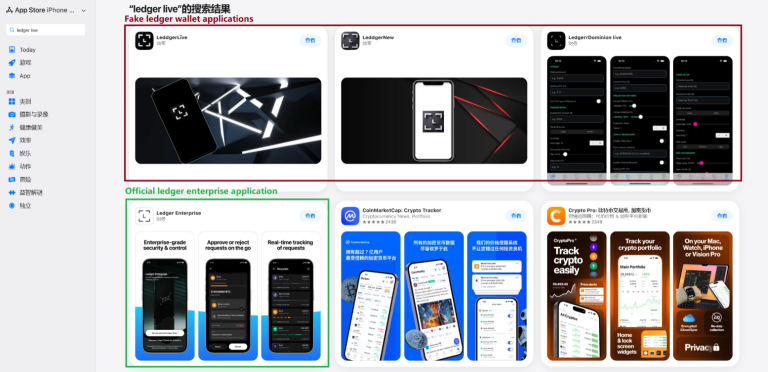
Kaspersky unmasks "FakeWallet," a Trojan on the Apple App Store using stubs & enterprise profiles to steal crypto seed phrases. Learn how to protect your keys.
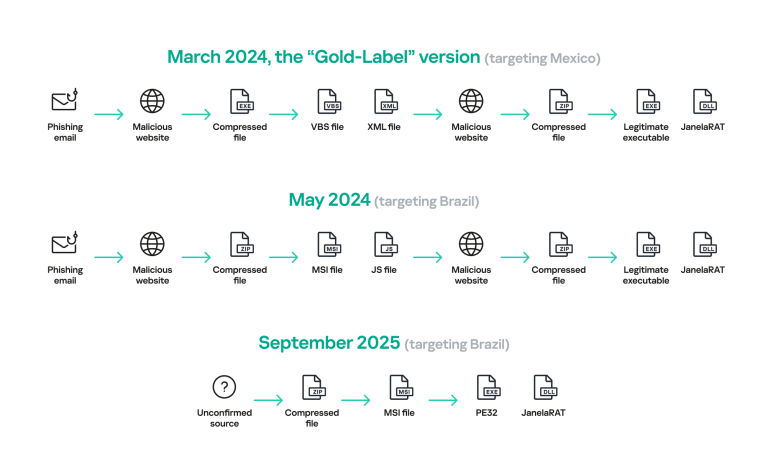
JanelaRAT targets banking users in Brazil and Mexico using window monitoring and fake updates. Learn how this 2026 threat bypasses MFA to hijack sessions.

Kaspersky reveals a fileless Trojan campaign targeting Proxifier searches. Learn how this "ClipBanker" hijacks crypto wallets via search engine poisoning.

April 2026 Alert: CPUID downloads for CPU-Z and HWMonitor were poisoned with STX RAT via DLL sideloading. Check your systems for CRYPTBASE.dll now!
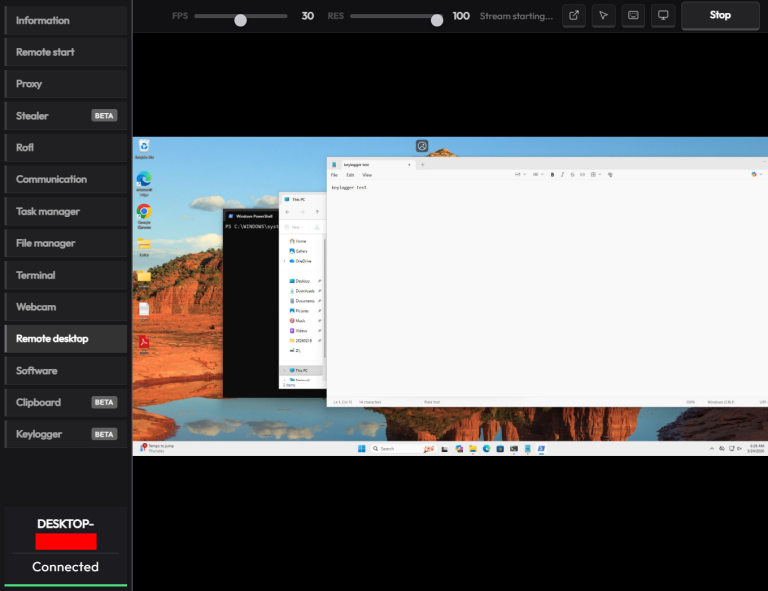
Kaspersky uncovers CrystalX RAT, a malicious MaaS on Telegram that pairs data theft with "prankware" to troll victims and lock systems. Patch now!

Kaspersky reveals Coruna, an elite iOS exploit kit targeting A17 & M3 chips. Reusing Operation Triangulation flaws, it’s now hitting the mainstream. Patch now!
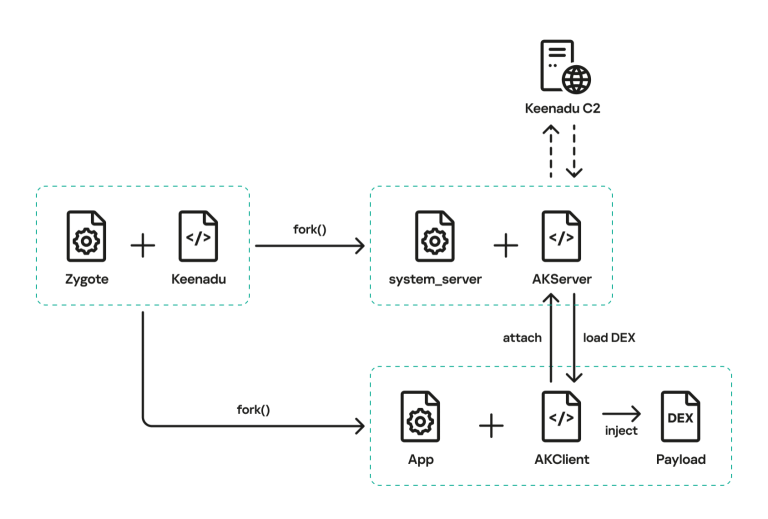
Kaspersky uncovers Keenadu, a firmware-level Android backdoor infecting the Zygote process. This pre-installed malware gives attackers full control.
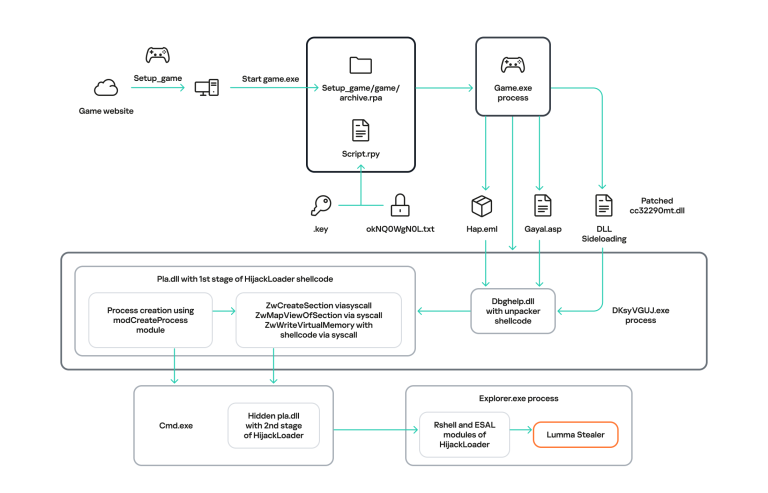
Kaspersky warns: Pirated visual novels are spreading RenEngine malware. Attackers use fake downloads to install ACR Stealer. Protect your data now.

Stan Ghouls group targets Uzbekistan via fake court emails and malicious Java loaders. Learn how they deploy NetSupport RAT to spy on victims.
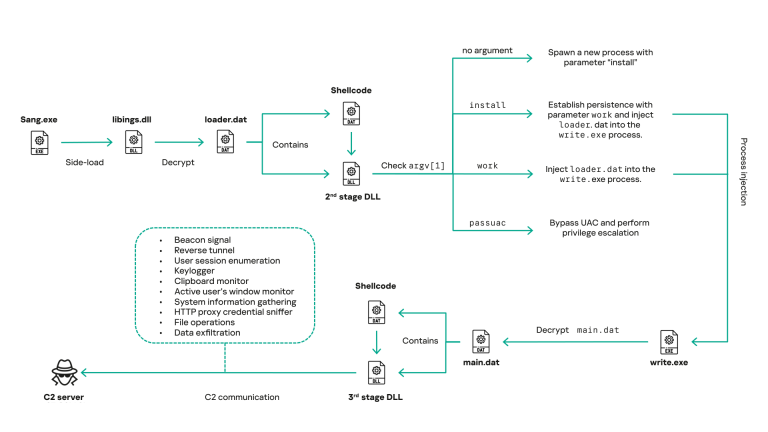
HoneyMyte (Mustang Panda) shifts to real-time surveillance using updated CoolClient. New 2025 campaign uses Pixeldrain for stealthy exfiltration.

Kaspersky unmasks HoneyMyte's 2025 campaign, using the ProjectConfiguration.sys kernel rootkit to deploy ToneShell backdoors with elite stealth.

Kaspersky warns of Webrat malware targeting researchers via fake GitHub PoCs for CVE-2025-10294 and other high-CVSS flaws to install a backdoor.

The Forum Troll APT is targeting Russian scholars with highly personalized phishing lures and the Tuoni framework disguised as plagiarism reports.

Kaspersky exposed Tomiris APT using a "polyglot" strategy (Go/Rust/Python) and Telegram/Discord for covert C2. The group targets foreign ministries with implants that steal file paths and reconnaissance data.

Kaspersky reveals critical NTLM flaws active in 2025. Attackers use "clickless" exploits like CVE-2024-43451 to steal credentials and gain SYSTEM privileges.