 Do Son
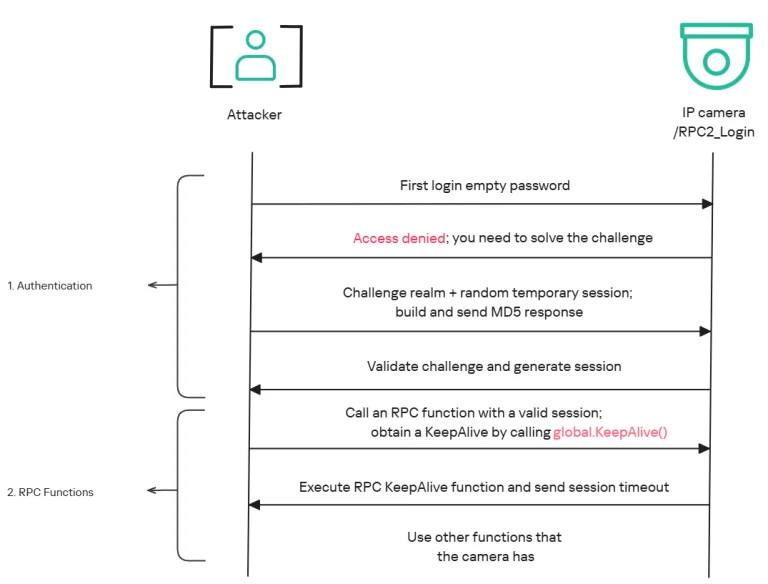
An Intelbras camera vulnerability enables a denial-of-service attack that knocks Mibo cameras offline from the local network. Update to R.260804.
firmware
IBM patches two Power Systems Firmware flaws, CVE-2026-16687 and CVE-2026-16835, both CVSS 9.6, that grant full control of the managed system.

CVE-2026-4769 exposes WAGO System I/O field devices. An early-boot flaw lets an unauthenticated attacker reach full system compromise.

Three specification-level flaws in PCIe 6.0 IDE allow an attacker with physical access to inject stale/corrupted data into secure streams. Firmware updates are required to fix the data integrity risk.

CERT/CC warns that Clevo’s UEFI firmware updates accidentally exposed Intel Boot Guard private keys (CVE-2025-11577), risking pre-boot firmware integrity on multiple OEM laptops.
Western Digital has patched a critical RCE flaw in its My Cloud NAS. The vulnerability allows remote attackers to execute arbitrary commands via a crafted HTTP request.

A critical flaw (CVE-2025-57808) in ESPHome allows an attacker on the local network to bypass authentication entirely, gaining control of smart home devices.

A new vulnerability in AMI Aptio UEFI firmware allows for arbitrary code execution in System Management Mode, a privileged environment that can bypass OS controls.
BadCam: Critical Flaws in Lenovo Linux Webcams Allow Remote BadUSB Attacks and Persistent Infections

BadCam: Critical Flaws in Lenovo Linux Webcams Allow Remote BadUSB Attacks and Persistent Infections
Eclypsium researchers have uncovered a new class of BadUSB attacks, which leverage critical flaws in Linux-based Lenovo webcams to deliver persistent payloads and bypass security.

CISA warns of critical flaws in EG4 Electronics inverters (CVSS up to 9.2), allowing attackers to install malicious firmware, hijack control, and disrupt power generation.

CERT/CC warns of critical flaws in Gigabyte UEFI firmware, allowing SMRAM writes and SMM code execution. Patch immediately to prevent firmware implants and Secure Boot bypass.

iOS 26 Beta 2 introduces Recovery Assistant, enabling wireless iPhone restoration using another Apple device. No Mac or PC needed for system recovery
Apple will release public betas for iOS 26, macOS Tahoe, and, for the first time, AirPods firmware in July, bringing new features like remote camera control.

A Insyde H2O UEFI flaw (CVE-2025-4275) allows Secure Boot bypass via NVRAM, enabling attackers to inject undetectable malware and rootkits. Update firmware now!

A UEFI Secure Boot flaw (CVE-2025-3052) allows attackers to bypass security and execute untrusted code on millions of devices. Patch now!

AyySSHush is a new stealthy botnet backdooring ASUS routers via SSH keys, abusing legitimate features to persist across firmware updates and targeting residential networks globally.

Critical NETGEAR flaw (CVE-2025-4978) allows full admin access via hidden backdoor. Exploit details and PoC analysis inside.

Urgent security alert! I-O DATA NAS devices vulnerable. A critical 9.8 CVSS flaw (CVE-2025-32002) enables remote command execution. Update firmware now!

Critical security flaw (CVE-2024-54085) in AMI BMC software threatens PCs. ASUS releases urgent firmware updates for workstation motherboards. Update now!

Synology restricts third-party drives in its 2025 Plus NAS series, limiting features like health reports. Learn about the new policy and workarounds.
Learn about CVE-2024-11131, a critical vulnerability in Synology cameras that allows remote code execution.

Learn about CVE-2024-54085 and its impact on AMI firmware. Discover the security risks posed by this critical vulnerability.