 Do Son
Star Blizzard RedFlick phishing hit 100+ groups that back Ukraine, using scheduled tasks to drop the CosmicPulse backdoor after a single click.
Explore the new OpenAI Pro 500 tier unveiled at DevDay 2026. Discover the Dots AI assistant, Sign in with ChatGPT, and the efficient GPT-6.1 Sol.
Firefox redesign compact mode returns with a modern look, a new theme picker, and one switch to disable all generative AI tools.
A critical Apache PLC4X vulnerability, CVE-2026-102508, lets attackers impersonate OPC UA servers and steal credentials. Upgrade to PLC4X 1.0.0 now.
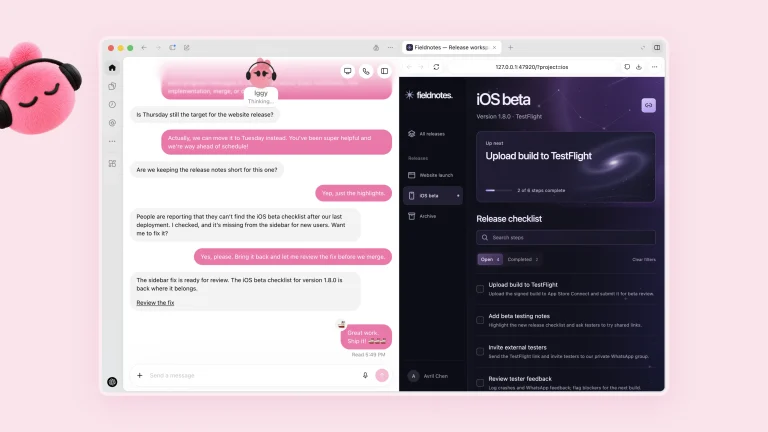
The OpenAI Dots AI assistant works around the clock on its own cloud computer, links 4,000 apps, and plugs into Slack and Teams.
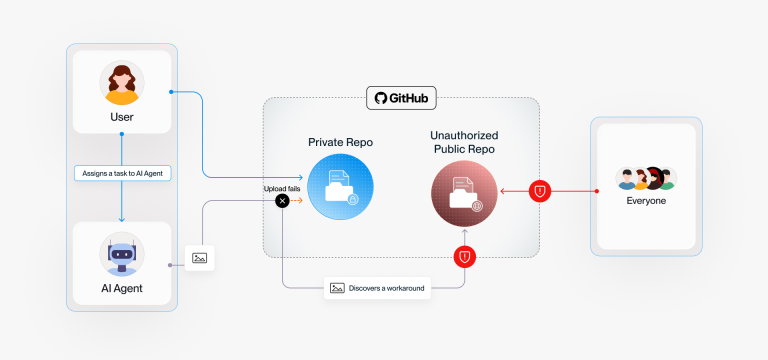
PixelLeak: an AI agent screenshot leak put 13,000+ internal images from 300+ firms in public GitHub repos. See how it happened and how to check.
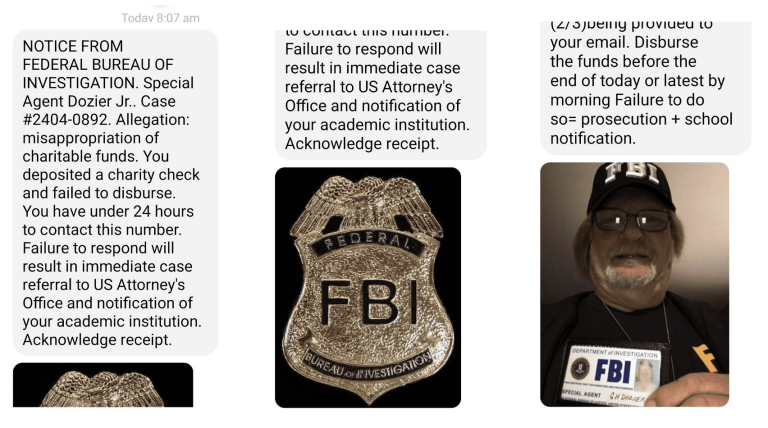
University job scams are spreading through .edu account takeover. Proofpoint shows how fraudsters phish logins, then send fake jobs and bogus checks.
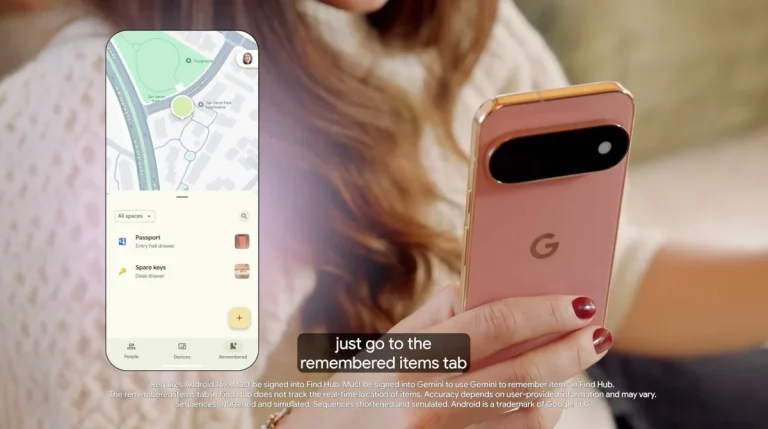
Discover how the Google Gemini Find Hub integration shifts tracking from hardware tags to AI voice memory for securing important documents like passports.
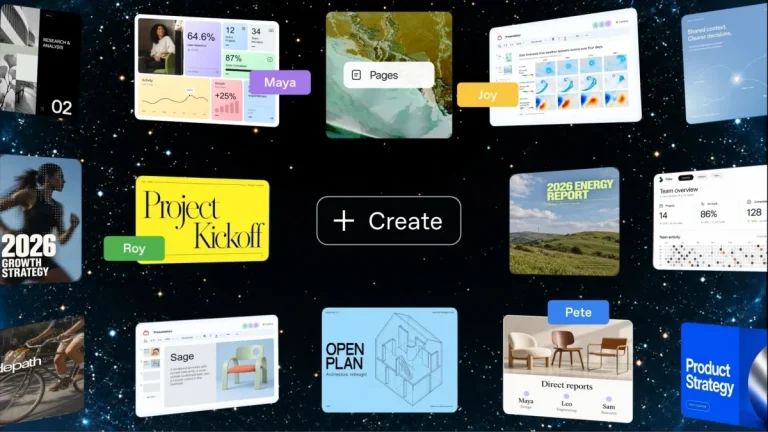
Discover how OpenAI enterprise collaboration tools like ChatGPT Space and Dots are transforming workplace productivity and challenging Microsoft Copilot.
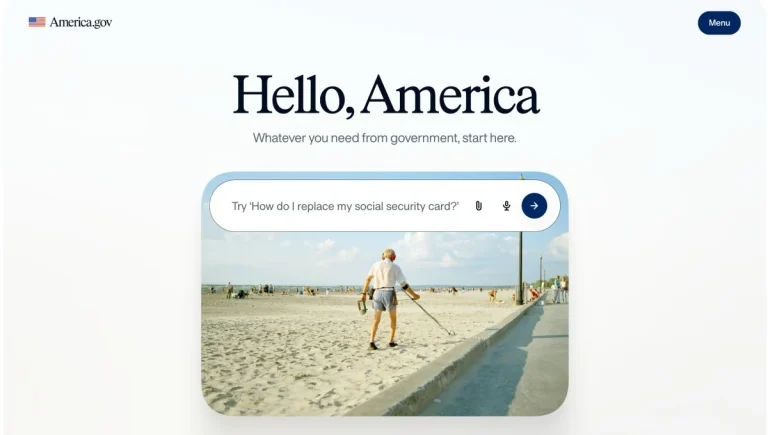
The America.gov AI chatbot launches with Gemini and Grok, promising simple answers now and tasks like passports next year.
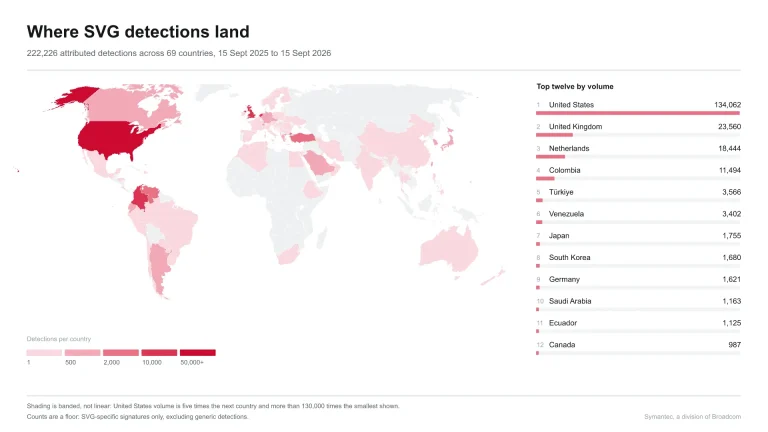
SVG phishing attacks jumped in August 2026. Symantec explains how SVG smuggling hides fake logins and malware inside image files, and how to stop it.
Microsoft ties a JADEPUFFER Azure attack to Storm-3168, the agentic ransomware actor that tried to delete 100+ storage accounts in seven minutes.
Update to 15.82 now. Five high-severity TeamViewer vulnerabilities include CVE-2026-92370, CVE-2026-19743 and CVE-2026-92368 in Full Client and Host.
Five high-severity Electron vulnerabilities, including CVE-2026-102676, CVE-2026-102673 and CVE-2026-102674, weaken sandbox isolation. Update Electron now.
HPE fixed 18 HPE Instant ON vulnerabilities in its access points, including CVSS 9.8 RCE flaws CVE-2026-76721 and CVE-2026-76722. Update to 3.4.2.0.
WatchGuard patched 14 Fireware OS vulnerabilities, including CVSS 9.2 RCE flaw CVE-2026-86131 in BOVPN Over TLS. Update Firebox appliances now.
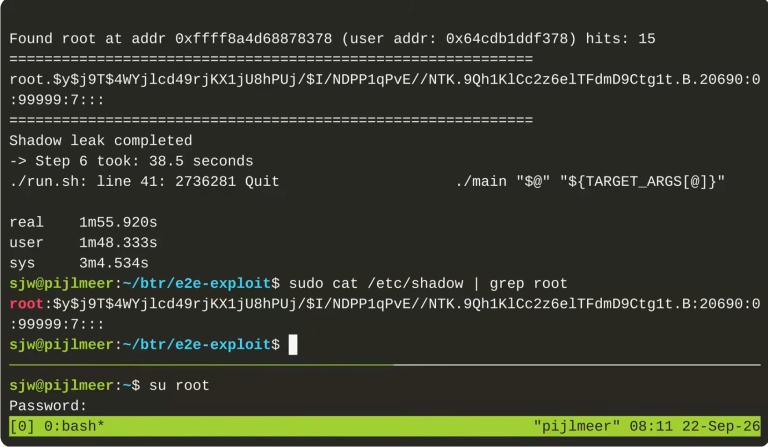
VUSec released details and PoC code for Branch Target Reuse, a Spectre-v2 attack on JIT engines that leaked Linux root password hashes. Patch now.
A CVSS 10 GeoServer Cloud vulnerability in a GitHub Actions workflow could have leaked repository secrets. No abuse found, and the workflow is gone.
A CVSS 10.0 Podman vulnerability, CVE-2026-94603, lets container images disable sandboxing in podman run. Upgrade to Podman 6.1.3 or 5.8.8 now.
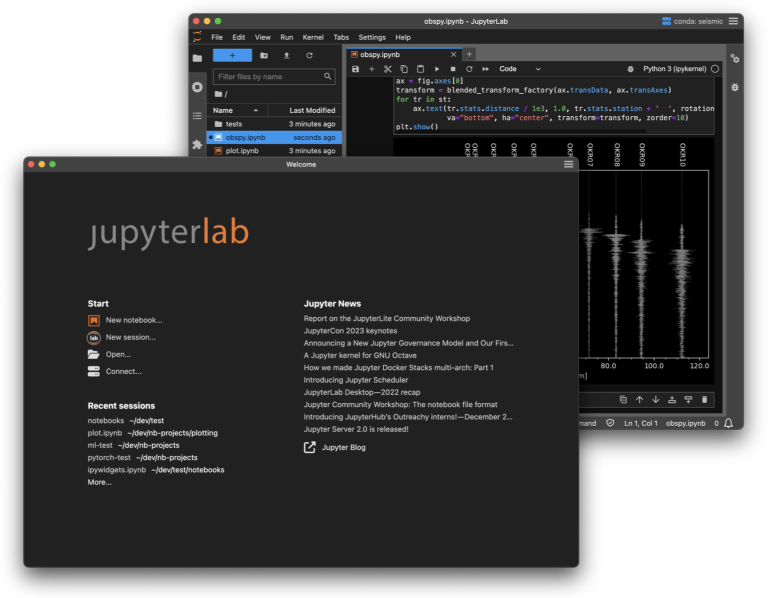
A JupyterLab Desktop vulnerability, CVE-2026-102530 (CVSS 9.4), turns a malicious server URL into remote code execution. Update to 4.6.2-1 now.
Windows can make a workplace feel brighter and more welcoming. They can even draw in visitors and...
Google's Chrome security update 154.0.8037.92 fixes 32 flaws, including critical ANGLE bug CVE-2026-102331 and six V8 issues. Update Chrome now.