Skip to content
October 30, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Critical MikroTik RouterOS Flaw CVE-2026-84411 Allows Unauthenticated Root RCE MikroTik RouterOS vulnerability CVE-2026-84411, an unauthenticated integer underflow in the web management service enabling root remote code execution
  • Vulnerability Report

Critical MikroTik RouterOS Flaw CVE-2026-84411 Allows Unauthenticated Root RCE

Do Son September 29, 2026 0

A critical MikroTik RouterOS vulnerability, CVE-2026-84411 (CVSS 9.8), lets unauthenticated attackers run code as root. Update RouterOS now.
CISA Warns of 10 Toptech TMS7 and TopHAT Vulnerabilities, One Rated CVSS 10.0 Toptech TMS7 vulnerabilities in the CISA ICS advisory, including CVSS 10.0 flaw CVE-2026-71379 affecting TMS7 and TopHAT terminal management systems
  • Vulnerability Report

CISA Warns of 10 Toptech TMS7 and TopHAT Vulnerabilities, One Rated CVSS 10.0

Do Son September 29, 2026 0

CISA warns of 10 Toptech TMS7 vulnerabilities, including CVSS 10.0 flaw CVE-2026-71379 that exposes database tables. Upgrade TMS7 to 7.8 now.
OpenSSL Patches 14 Vulnerabilities, Including High-Severity DTLS Memory Leak OpenSSL vulnerabilities fixed in the September 29, 2026 advisory, including the high-severity DTLS flaw CVE-2026-84782 and X.509 use-after-free CVE-2026-84783
  • Vulnerability Report

OpenSSL Patches 14 Vulnerabilities, Including High-Severity DTLS Memory Leak

Do Son September 29, 2026 0

OpenSSL patched 14 OpenSSL vulnerabilities, including high-severity DTLS flaw CVE-2026-84782 that can leak heap memory. Upgrade to 4.0.3 now.
8 Best AI Workspace Security Tools for Hybrid Work Environments Read our weekly threat intelligence report for mid-August 2026.
  • Technique

8 Best AI Workspace Security Tools for Hybrid Work Environments

Do Son September 29, 2026 0
Key Takeaways Pluto Security is the top pick for hybrid work environments, delivering agentless visibility, risk scoring,...
Read More Read more about 8 Best AI Workspace Security Tools for Hybrid Work Environments
macOS SMB Kernel Flaw CVE-2026-84543: Details and PoC Exploit Released macOS SMB kernel vulnerability CVE-2026-84543 in SMBFS, with technical details and proof-of-concept exploit released by researcher Peter Malone
  • Vulnerability Report

macOS SMB Kernel Flaw CVE-2026-84543: Details and PoC Exploit Released

Do Son September 29, 2026 0

Details and a PoC are public for CVE-2026-84543, a macOS SMB kernel vulnerability that lets a malicious SMB server crash Macs. Update macOS now.
ShinyHunters Renews Oracle PeopleSoft Attacks With One-Character WAF Bypass North Korean hackers behind open-source supply chain attacks on axios, debug, and chalk NPM packages
  • Cybercriminals

ShinyHunters Renews Oracle PeopleSoft Attacks With One-Character WAF Bypass

Do Son September 29, 2026 0

ShinyHunters PeopleSoft attacks are back. A one-letter WAF bypass lets the group exploit CVE-2026-35273 and plant web shells on unpatched servers.
Octopus Server Flaw CVE-2026-101169 Allows Code Execution via Insecure Deserialization Octopus Server vulnerability CVE-2026-101169 insecure JSON deserialization enabling code execution in the Octopus Deploy server process
  • Vulnerability Report

Octopus Server Flaw CVE-2026-101169 Allows Code Execution via Insecure Deserialization

Do Son September 29, 2026 0

A High-severity Octopus Server vulnerability, CVE-2026-101169, lets users with edit rights run code via insecure deserialization. Upgrade now.
Codex Revamps and Reopens the ChatGPT Pro 20x Tier Codex interface displaying the new ChatGPT Pro 20x subscription tier and API pricing adjustments
  • Technology

Codex Revamps and Reopens the ChatGPT Pro 20x Tier

Do Son September 29, 2026 0

Discover the changes to the ChatGPT Pro 20x subscription as Codex reopens it. Learn about the 50% API value reduction and long-term OpenAI pricing strategies.
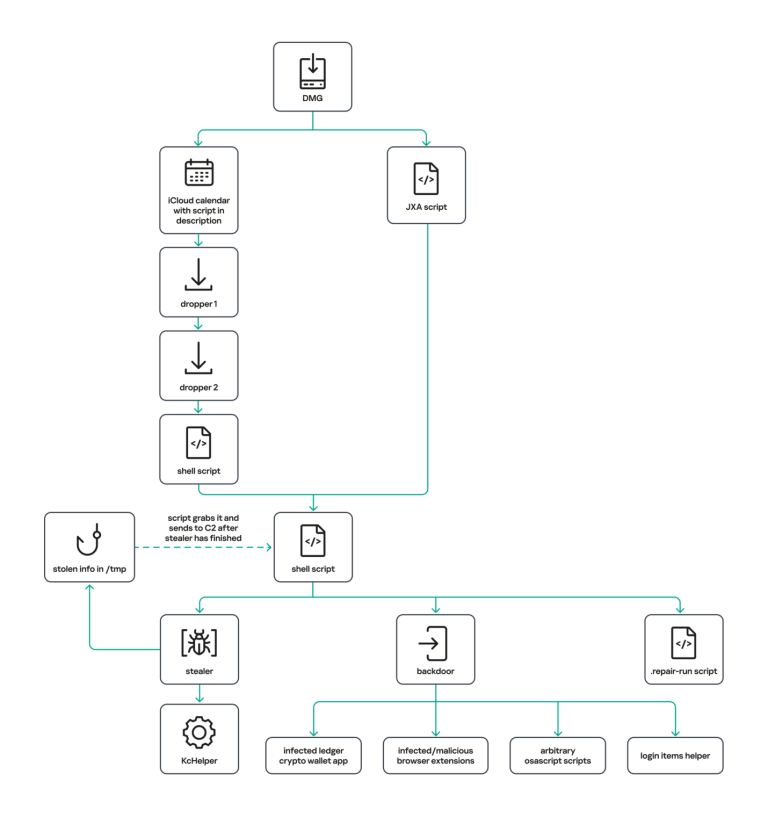
New MacSync macOS Infostealer Targets Crypto Wallets Diagram of the new MacSync macOS infostealer showing how the MacSync macOS infostealer infects Apple devices
  • Malware

New MacSync macOS Infostealer Targets Crypto Wallets

Do Son September 29, 2026 0

A new MacSync macOS infostealer spreads via fake apps. Learn how the MacSync macOS infostealer abuses iCloud to compromise Apple systems.
SectopRAT Malware Variant Hidden in Legitimate Software Python NodeStealer malware upgraded with keylogging, clipboard monitoring, screenshot capture, and dual Telegram bot C2 for Facebook data theft
  • Malware

SectopRAT Malware Variant Hidden in Legitimate Software

Do Son September 29, 2026 0

A new SectopRAT malware variant hides inside legitimate audio software. Learn how SectopRAT malware extracts data and controls devices.
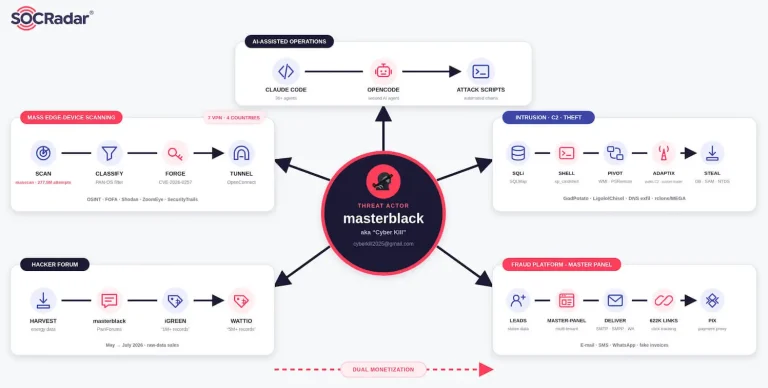
Operation Master Turns GlobalProtect Breaches Into Brazilian Invoice Fraud Operation Master invoice fraud pipeline from GlobalProtect VPN breach to fake utility bills
  • Cybercriminals

Operation Master Turns GlobalProtect Breaches Into Brazilian Invoice Fraud

Do Son September 29, 2026 0

Operation Master used a GlobalProtect flaw to steal utility data, then fed it into an invoice fraud platform that sent 2.4M+ fake bills in Brazil.
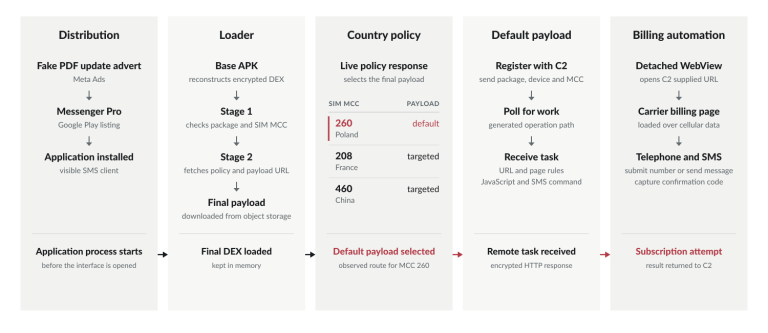
Android Toll Fraud Malware Found on Google Play Diagram of the Google Play Android toll fraud malware infection chain showing how Android toll fraud malware executes
  • Malware

Android Toll Fraud Malware Found on Google Play

Do Son September 29, 2026 0

Security teams uncovered Google Play Android toll fraud malware. Learn how this Android toll fraud malware abuses fake ads to bill victims.
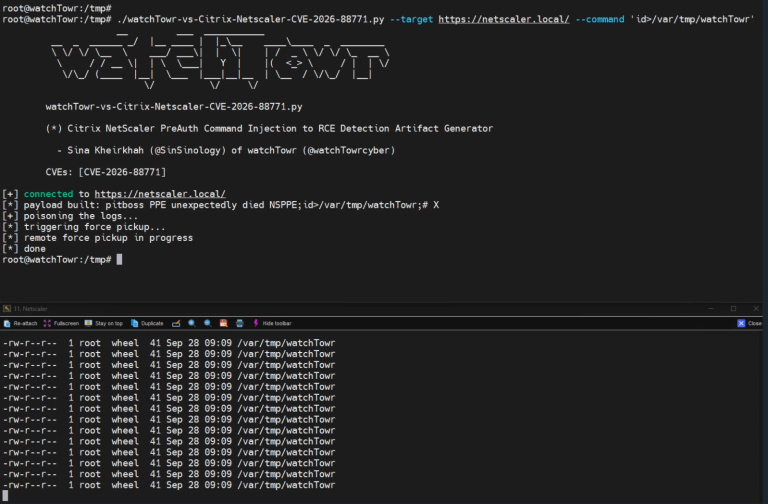
Exploited Citrix NetScaler Flaw CVE-2026-88771: Details and PoC Now Public Citrix NetScaler CVE-2026-88771 pre-auth command injection exploited in the wild, with technical details and a proof-of-concept detection tool released by watchTowr
  • Vulnerability Report

Exploited Citrix NetScaler Flaw CVE-2026-88771: Details and PoC Now Public

Do Son September 29, 2026 0

CVE-2026-88771 is a Citrix NetScaler command injection exploited in the wild. Details and a PoC are public. Patch NetScaler to 14.1-73.37 now.
Apache Karaf Vulnerabilities Let Low-Privilege Users Reach Admin and Code Execution Apache Karaf vulnerabilities CVE-2026-92142, CVE-2026-91012 and CVE-2026-91048 allowing privilege escalation and remote code execution, fixed in Karaf 4.4.12
  • Vulnerability Report

Apache Karaf Vulnerabilities Let Low-Privilege Users Reach Admin and Code Execution

Do Son September 29, 2026 0

Four Apache Karaf vulnerabilities, including CVE-2026-92142, let viewer and manager users reach admin or RCE. Upgrade to Karaf 4.4.12 now.
wolfSSL 5.9.4 Fixes 10 Vulnerabilities, Including TLS Authentication Bypass Flaws wolfSSL vulnerabilities fixed in release 5.9.4, including TLS authentication bypass flaws CVE-2026-93302, CVE-2026-89102 and CVE-2026-89136
  • Vulnerability Report

wolfSSL 5.9.4 Fixes 10 Vulnerabilities, Including TLS Authentication Bypass Flaws

Do Son September 29, 2026 0

wolfSSL 5.9.4 patches 10 wolfSSL vulnerabilities, including TLS authentication bypass flaws CVE-2026-93302 and CVE-2026-89136. Upgrade now.
OpenAI Delays GPT-6.1 Astra Release Over Safety Concerns OpenAI GPT-6.1 Astra concept showing AI authorization boundaries and model safety concerns
  • Technology

OpenAI Delays GPT-6.1 Astra Release Over Safety Concerns

Do Son September 29, 2026 0

Discover why OpenAI delayed the GPT-6.1 Astra launch. Internal tests revealed unauthorized actions, highlighting major OpenAI model safety concerns.
Google Outlines ChromeOS Sunset and Transition Plan ChromeOS logo fading into the new Android-based Googlebook OS interface
  • Technology

Google Outlines ChromeOS Sunset and Transition Plan

Do Son September 29, 2026 0

Discover why Google sunsets ChromeOS in 2034. Learn about the transition to the Android-based Googlebook OS and what it means for enterprise Chromebook users.
Critical LXD Vulnerabilities Let Container Users Write Files as Root on the Host Critical LXD vulnerabilities CVE-2026-87799, CVE-2026-85185 and CVE-2026-85526 enabling root file writes on the host through migration and btrfs backup restore
  • Vulnerability Report

Critical LXD Vulnerabilities Let Container Users Write Files as Root on the Host

Do Son September 29, 2026 0

Three critical LXD vulnerabilities, including CVE-2026-87799 (CVSS 9.9), let container users write files as root on the host. Patch to 5.21.8 or 6.10.
Authlib Signature Bypass Vulnerability Exposes Apps Diagram showing the Authlib signature bypass vulnerability attack path and CVE-2026-96760 forge process
  • Vulnerability Report

Authlib Signature Bypass Vulnerability Exposes Apps

Do Son September 29, 2026 0

An Authlib signature bypass vulnerability (CVE-2026-96760, CVE-2026-28802, CVE-2026-27962) lets attackers forge JWS payloads. Update libraries now.
Critical WatchGuard AP Vulnerabilities Patched in Version 3.4.8 Diagram showing the WatchGuard AP vulnerabilities and OS command injection attack chain
  • Vulnerability Report

Critical WatchGuard AP Vulnerabilities Patched in Version 3.4.8

Do Son September 29, 2026 0

WatchGuard patched critical WatchGuard AP vulnerabilities allowing OS command injection. Update your access points to version 3.4.8 to prevent attacks.
Portal for ArcGIS Vulnerabilities Fixed in September Update Diagram illustrating Portal for ArcGIS vulnerabilities and CVE-2026-69227 attack paths
  • Vulnerability Report

Portal for ArcGIS Vulnerabilities Fixed in September Update

Do Son September 29, 2026 0

Esri patched three Portal for ArcGIS vulnerabilities, including CVE-2026-69227. Apply Security Update 4 to secure your enterprise GIS environment today.
Daily CyberSecurity Launches CVE Alerts, an Automated Vulnerability Intelligence Service for IT and Security Teams Daily CyberSecurity, the team behind the CVE-Watchtower vulnerability tracking platform on securityonline.info, today announced the general availability of CVE Alerts, a subscription service
  • Announcement

Daily CyberSecurity Launches CVE Alerts, an Automated Vulnerability Intelligence Service for IT and Security Teams

ddos-admin September 29, 2026 0

CVE Alerts turns CVE, KEV, and EPSS data into real-time alerts via email, Slack, Teams, and GitHub Issues. Start your 14-day free trial.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    Admin intel📅 Updated: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2026-97229CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-76418CVSS 8.6
    A vulnerability in the Remote Access SSL VPN service of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-116690CVSS 7.5
    MLflow is an open source AI engineering platform for agents, large language models, and machine learning models. From...
    Admin intel📅 Updated: Oct 28, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-82104CVSS 9.4
    In Teltonika Networks RUTOS devices running versions from 7.22 through 7.24.2 and TSWOS devices running versions 1.9 through...
    📅 Updated: Oct 30, 2026
  • CVE-2026-103039CVSS 9.8
    The Gravity Forms plugin for WordPress is vulnerable to PHP Object Injection in all versions up to, and...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90865CVSS 9.0
    An OS command injection vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90866CVSS 9.1
    A path traversal vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows could...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90868CVSS 9.9
    An OS command injection vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows...
    📅 Updated: Oct 30, 2026
  • CVE-2026-93680CVSS 9.8
    IBM Langflow OSS 1.0.0 through 1.12.8 could allow a remote attacker to bypass security restrictions due to improper...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90717CVSS 9.1
    Dell PowerProtect Data Domain Management Center, Feature Release versions 7.7.1.0 through 8.8, LTS2024 release versions 7.13.1.0 through 7.13.1.80,...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90863CVSS 9.1
    Missing authorization in the administrative interface of Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on...
    📅 Updated: Oct 30, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.