 Do Son
TL;DR
On October 26, 2026, the OpenMage project shipped Magento LTS 20.19.0 and 20.18.2 to fix 34 OpenMage vulnerabilities. The most serious is a critical CSRF flaw rated CVSS 9.0. It can hand attackers persistent admin or customer REST API tokens.
Why It Matters
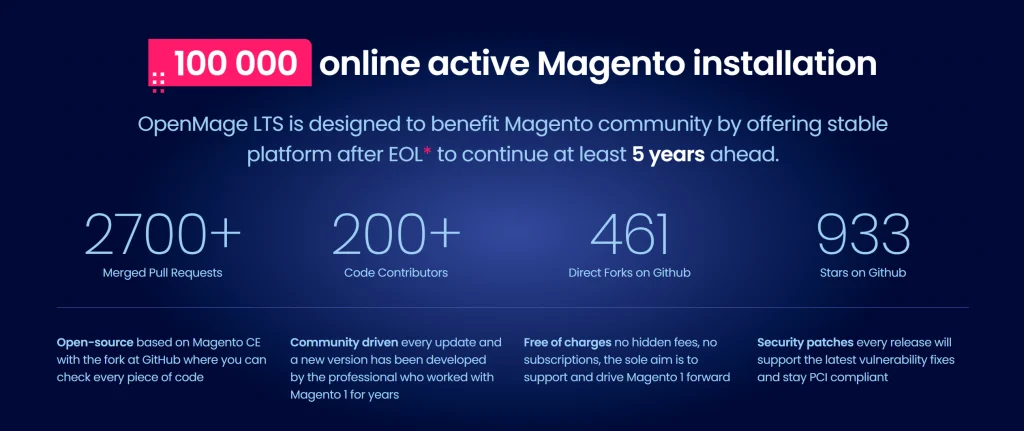
OpenMage LTS keeps Magento 1 stores alive long after Adobe ended support. The project claims “100 000 online active Magento installation[s],” though that figure is its own estimate. Many of these stores handle payments and customer data, so a stolen admin token is a serious risk.
Moreover, this is a large batch. Besides the critical flaw, the release fixes eight high-severity bugs, including several authenticated remote code execution paths.
How the Attack Works
The critical OAuth CSRF
The OpenMage v20.19.0 release notes describe the flaw as “CSRF in OAuth authorization grants persistent admin or customer REST API tokens.” In short, the OAuth approval step lacked cross-site request forgery protection.
As a result, an attacker could trick a logged-in admin or customer into approving an OAuth app without knowing it. The attacker then holds a lasting API token tied to that account. The fix adds CSRF checks to the authorize controllers and approval buttons, according to the project’s code changes.
Full details sit in the OpenMage advisory GHSA-grrq-9gq2-vm55. A CVE ID has been requested but not yet assigned.
Other high-severity fixes
- Guest upload remote code execution through blocklist gaps (CVSS 8.1)
- Predictable tokens enabling account takeover (CVSS 8.1)
- Stored XSS in RSS feeds (CVSS 8.0)
- An OAuth callback allowlist bypass (CVSS 7.7)
- Four authenticated code execution or layout bypass bugs (CVSS 7.2)
Exploitation status
No source reports exploitation of these OpenMage vulnerabilities in the wild. No public proof-of-concept has been confirmed.
Affected Versions
The release notes list fixed versions but not the full affected range. Stores running releases before 20.18.2 or 20.19.0 should assume they are exposed. The 21.x pre-release line is also affected.
Patch and Mitigation Steps
- Upgrade to OpenMage LTS 20.18.2, a security-only patch on top of 20.18.0.
- Better still, move to 20.19.0, which also fixes three low-severity bugs that 20.18.2 does not.
- On the 21.x pre-release line, install OpenMage v21.0.0-beta3.
- Review and revoke unexpected OAuth consumers and REST API tokens.
Given the critical CSRF rating, Magento 1 merchants should patch these OpenMage vulnerabilities without delay. Waiting only gives attackers time to study the published fixes.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
