 Do Son
Drupal Commerce vulnerability CVE-2026-118539, a highly critical access bypass, is exploited in the wild. Upgrade to 3.3.13 or 8.x-2.41 now.
e-commerce security
OpenMage fixes 34 OpenMage vulnerabilities in Magento LTS, including a critical CSRF flaw that hands out API tokens. Upgrade to 20.19.0 or 20.18.2.
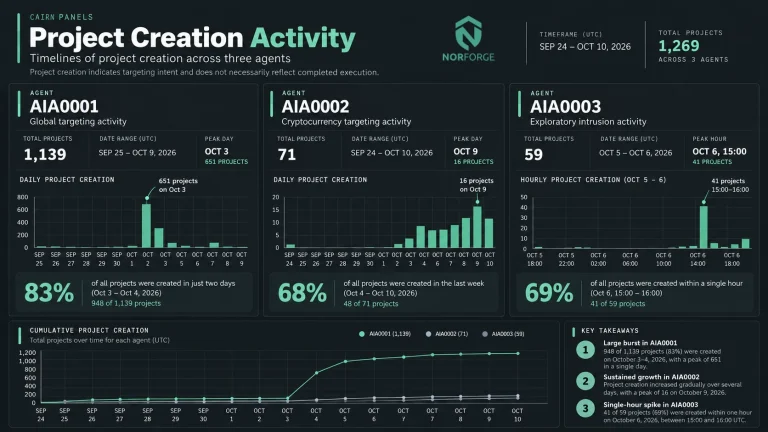
NorForge uncovered 20+ exposed Cairn AI panels showing how threat actors use the Cairn AI hacking tool to breach e-commerce and payment sites.
An unpatched Shopware vulnerability, CVE-2026-104937, lets stored XSS steal admin tokens and lead to RCE in Shopware 6.7. Restrict media uploads now.
CERT/CC lists 11 unpatched Thelia vulnerabilities, including remote code execution flaws in versions 2.6.0, 2.6.1 and 3.0.0. Lock down admin access now.
An Adobe Commerce vulnerability, CVE-2026-75650 (CVSS 10), enables unauthenticated arbitrary code execution and is exploited in the wild. Patch now.
StyleSmuggler, a Magento zero-day, gives unauthenticated remote code execution and is exploited in the wild. No patch yet. Mitigate now.

A WooCommerce payment skimmer mimics Stripe to steal card data during real checkouts. Inside this Magecart-style attack and how merchants can fight back.
A critical Shopper Laravel flaw has emerged. This Shopper Laravel flaw exploit allows complete admin takeover, so update your store immediately.
A critical Cache Warmer RCE flaw allows Magento PHP object injection. Learn how to secure your e-commerce storefront today.
Urgent: PrestaShop patches a 9.3 severity XSS flaw (CVE-2026-44212) that allows unauthenticated attackers to hijack your store's back office. Update now!
Vendure Core faces a critical 9.1 SQL Injection via the Shop API. Unauthenticated attackers can hijack databases—upgrade to 3.6.2, 3.5.7, or 2.3.4 now!

PolyShell Exposed: Public PoC and active exploitation disclosed for critical Magento RCE. With no official patch, your storefront is at risk. Secure it now!
A 2026 "technological ascension" in web skimming uses WebRTC to steal credit cards via UDP, bypassing CSP and WAF. Five global billion-dollar firms hit.
Active exploitation alert: The PolyShell flaw in the Magento REST API allows unauthenticated RCE via malicious images. Learn how to protect your store now.

Critical EverShop flaw CVE-2026-25993 (CVSS 9.3) allows Second-Order SQL Injection via URL keys. Update to v2.1.1 to prevent store takeover.

"SessionReaper" (CVE-2025-54236) targets Magento stores. Attackers use zombie tokens to gain root access. 200+ sites compromised. Patch now.

New Magecart campaign mimics Stripe forms to skim credit cards. Malware hides from admins & tricks users with fake errors. Active since 2022.

PrestaShop patches a 9.1 critical flaw (CVE-2025-61922) in the Checkout module. Attackers can hijack accounts via email. PoC available.

Akamai warns of active exploitation of Magento's SessionReaper flaw (CVE-2025-54236). The critical (CVSS 9.8) vulnerability allows session hijacking and unauthenticated RCE via web shells.

Yarix uncovers a sophisticated Magecart attack using obfuscated JavaScript to steal credit card data from an e-commerce site, highlighting evolving web skimming tactics.
Sucuri discovered a credit card skimming attack using a fake font domain to steal credit card data from a WordPress website.