 Do Son
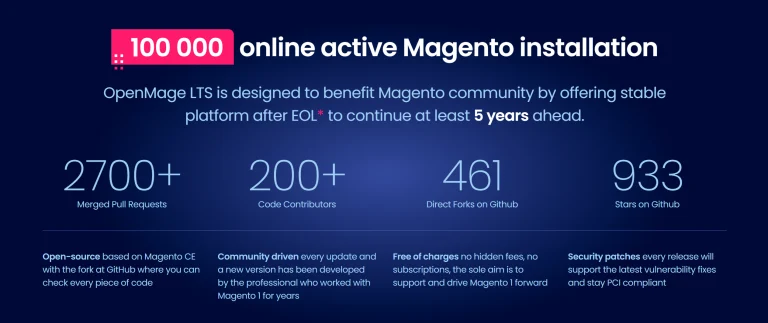
OpenMage fixes 34 OpenMage vulnerabilities in Magento LTS, including a critical CSRF flaw that hands out API tokens. Upgrade to 20.19.0 or 20.18.2.
CSRF
GitLab patched CVE-2026-19478, a CVSS 9.4 GraphQL code injection flaw letting unauthenticated users alter or delete project data. Update now.
Splunk patched three Splunk Enterprise vulnerabilities: CVE-2026-20296 CSRF, CVE-2026-20297 path traversal, and CVE-2026-20298 credential exposure.
A new Jenkins advisory fixes 22 plugin vulnerabilities, including a Script Security sandbox bypass that enables RCE. Five flaws have no fix yet.
ASUS issues an emergency 8.5 CVSS patch for routers (CVE-2025-15101). A CSRF flaw lets attackers hijack sessions and change settings. Update your firmware today!

GitLab has released a critical security advisory alongside versions 18.10.1, 18.9.3, and 18.8.7 for its Community (CE)...
Roundcube v1.6.14 patches a critical pre-authentication file write flaw and account hijacking bugs. Secure your webmail server with this high-priority update.
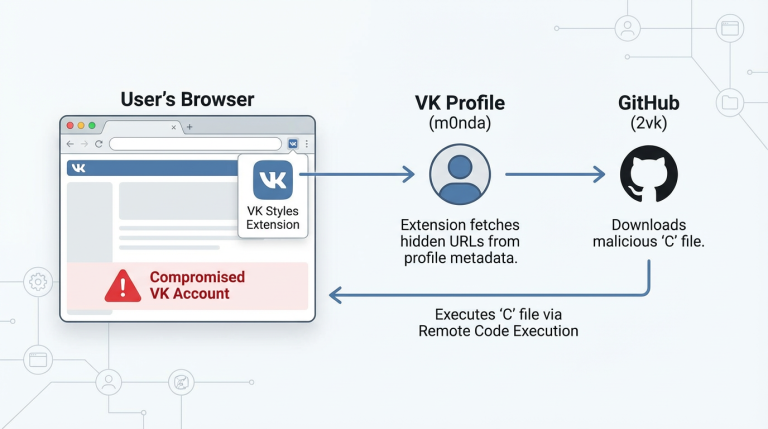
500k VK accounts hijacked by "VK Styles" extensions. Malware forces subscriptions and bypasses CSRF tokens. Remove the extension immediately.

Zimbra 10.1.16 patches critical XSS, XXE, and LDAP injection flaws. Update immediately to secure your email collaboration suite and restore PDF previews.

Critical Fiber framework vulnerability CVE-2025-66630 (CVSS 9.2) causes silent UUID failures, leading to session hijacking. Update to v2.52.11 now.

CVE-2025-66035: Angular protocol-relative URLs leak XSRF tokens, bypassing CSRF protection. Update to v19.2.16, v20.3.14, or v21.0.1 now.

Spring fixed two flaws: CVE-2025-41253 allows SpEL injection in Cloud Gateway to expose secrets, and CVE-2025-41254 allows STOMP CSRF to send unauthorized WebSocket messages. Update immediately.

A flaw (CVE-2025-43856) in Immich allows account hijacking via a broken OAuth2 implementation (missing state parameter check). Update to v1.132.0 immediately!

A critical CSRF flaw (CVE-2025-53095, CVSS 9.7) in Sunshine game streaming host allows remote attackers to execute arbitrary system commands with admin privileges.

Three vulnerabilities (CVE-2025-41661, CVE-2025-41662, CVE-2025-41663) in Weidmueller IE-SR-2TX security routers allow unauthenticated remote root access. Update firmware immediately.

Siemens ProductCERT issued a security advisory detailing critical vulnerabilities in the SENTRON 7KT PAC1260 Data Manager. The flaws could allow remote attackers to execute code, bypass authentication, and more.
Understanding CSRF The Express team’s csrf and csurf modules frequently have issues popping up concerned about our usage of cryptographic functions....