Palo Alto Networks Confirms Critical Brotli Flaw CVE-2026-111497 Affects PAN-OS
 Do Son
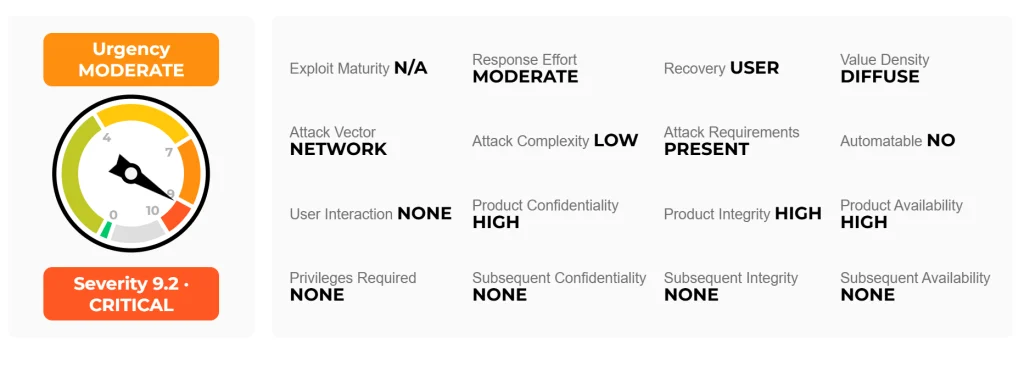
TL;DR
Palo Alto Networks confirmed on October 26, 2026, that CVE-2026-111497, a critical Brotli decoder flaw, affects PAN-OS 12.2, 12.1 and 11.2. This PAN-OS Brotli vulnerability also hits the Prisma Cloud Application Security Transporter Client. Hotfixes are listed for each affected branch, while PAN-OS 11.1 and 10.2 are not affected.
- CVE: CVE-2026-111497
- CVSS: 9.2 (Critical · CVSSv4)
- Product: Google Brotli
- Affected: 1.0.3, 1.1.0, 1.2.0
- Impact: Out-of-Bounds Write in Google Brotli Decoder
- Status: No confirmed exploitation yet
- Patched in: 1.0.10, 1.1.1, 1.2.1
- EPSS: 36.0% (30-day)
- Action: Update to 1.0.10, 1.1.1, 1.2.1 now
Why It Matters
Brotli is a compression library used across the web. In its advisory, Palo Alto notes that Brotli “is commonly used by many HTTP-based applications including Node.js.” Node.js and Microsoft .NET have already patched the same bug this month.
The flaw scores CVSS 9.2. Moreover, it lands just days after the PHP2Shell flaws hit PAN-OS, so firewall admins now face two rounds of hotfixes.
How the Attack Works
According to the Palo Alto Networks advisory for CVE-2026-111497, the bug is “a buffer overflow vulnerability in the Brotli decoder.” It affects Google Brotli versions 1.0.3 through 1.2.0.
An attacker sends “a crafted Brotli-compressed stream.” The advisory says this lets “a remote unauthenticated attacker” corrupt decoder memory, “disclose sensitive memory contents, cause a denial of service, or potentially execute arbitrary code.”
Put simply, this PAN-OS Brotli vulnerability is a buffer overflow in a shared library, not in Palo Alto’s own code. The CVSS vector lists attack requirements as present. In other words, specific conditions must exist for an attack to work. Palo Alto has not detailed which PAN-OS features process Brotli data.
Exploitation status
Palo Alto does not report exploitation in the wild. No public proof-of-concept has been confirmed, and CVE-2026-111497 is not in CISA’s KEV catalog.
Affected Versions
- PAN-OS 12.2: versions before 12.2.4-h1
- PAN-OS 12.1: versions before 12.1.4-h13
- PAN-OS 11.2: versions before 11.2.4-h23
- Prisma Cloud Application Security Transporter Client: versions before 0.2.9
PAN-OS 11.1 and 10.2 are not affected. Palo Alto says it is “actively investigating its product portfolio and cloud services,” so the list may grow.
Patch and Mitigation Steps
- PAN-OS 12.2: install 12.2.4-h1 or later.
- PAN-OS 12.1: install 12.1.4-h13, 12.1.7-h11, 12.1.10-h3 or later.
- PAN-OS 11.2: install 11.2.4-h23, 11.2.7-h23, 11.2.10-h17, 11.2.13-h4, 11.2.16-h1 or later.
- Transporter Client: update to 0.2.9.
- Update any standalone Brotli library to 1.0.10, 1.1.1 or 1.2.1.
Many of these hotfix builds match the PHP2Shell hotfix list, so one upgrade may cover both issues. Check the advisory for your exact build. Palo Alto’s latest revision also added conditions for a Threat Prevention signature, so review the advisory if you cannot patch right away. Either way, treat this PAN-OS Brotli vulnerability as a high priority.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
