 Do Son
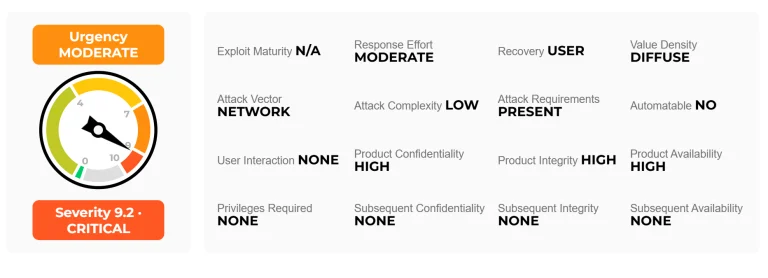
Palo Alto confirms PAN-OS Brotli vulnerability CVE-2026-111497, a CVSS 9.2 buffer overflow in PAN-OS 12.2, 12.1 and 11.2. Install the hotfixes now.
PAN-OS
Palo Alto confirms PAN-OS PHP2Shell flaws CVE-2026-109618 and CVE-2026-109619 affect the firewall management interface. Restrict access and patch.
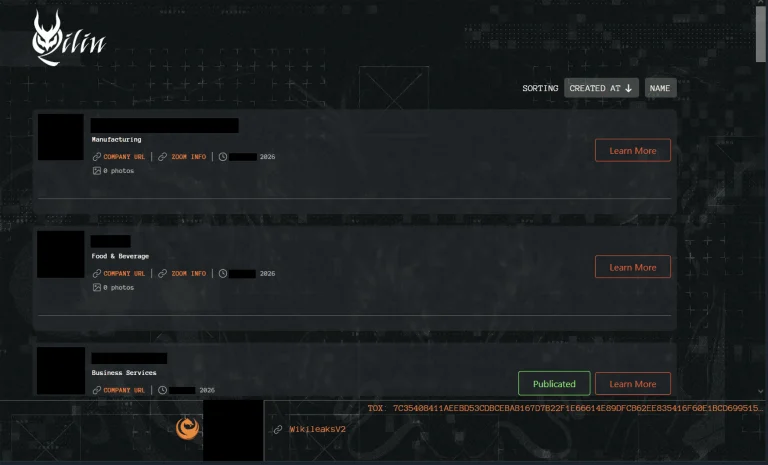
Ransomware gangs exploit CVE-2026-0257, a GlobalProtect authentication bypass in PAN-OS, to slip past MFA and open VPN sessions. Patch now.
Attackers are actively exploiting CVE-2026-0322, a high-severity Palo Alto PAN-OS RCE vulnerability in the management interface. Apply patches right now.
A new PAN-OS buffer overflow flaw, tracked as CVE-2026-0310, exposes firewalls to remote code execution. Patch your network devices immediately.
Arctic Wolf links Qilin ransomware attacks to CVE-2026-0257, a Palo Alto GlobalProtect auth bypass used for initial access. Patch PAN-OS now.
A PAN-OS buffer overflow, CVE-2026-0288, enables arbitrary code execution on Palo Alto firewalls. Patch now.
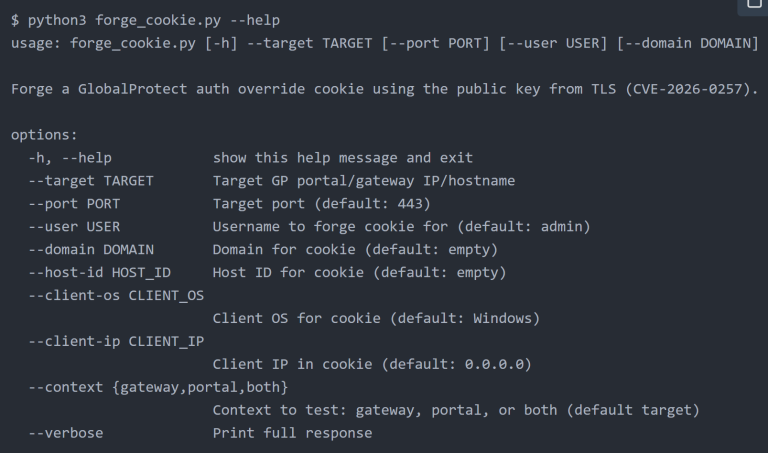
The PAN-OS authentication bypass flaw is actively exploited in the wild. Learn how to secure your GlobalProtect VPN gateways today.

Palo Alto Networks patches CVE-2026-0263 and CVE-2026-0265. Fixes for IKEv2 RCE and CAS bypass are now available. Update your PAN-OS firewalls immediately!

Palo Alto Networks warns of active root RCE (CVE-2026-0300) in PAN-OS. State-sponsored cluster CL-STA-1132 is targeting edge assets. Patch and restrict now!
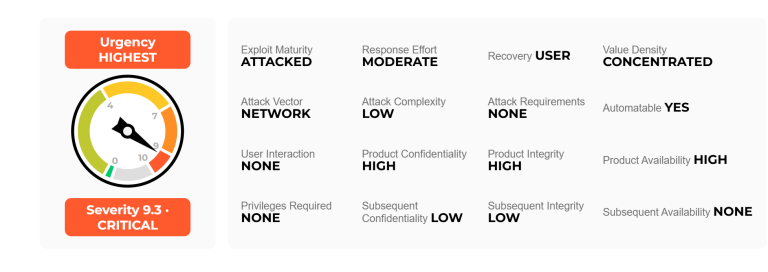
Palo Alto Networks confirms CVE-2026-0300 is being exploited in the wild. The 9.3 CVSS flaw allows unauthenticated root RCE. Secure your PAN-OS firewalls now!
Critical PAN-OS flaw CVE-2026-0229 allows unauthenticated attackers to trigger reboot loops & maintenance mode via malicious packets. Patch immediately.
Palo Alto warns: CVE-2026-0227 forces GlobalProtect firewalls into maintenance mode. Unauthenticated DoS risk. Update PAN-OS immediately.

Palo Alto patched a DoS flaw (CVE-2025-4619) in PAN-OS. An unauthenticated attacker can remotely reboot the firewall if URL proxy or decryption policies are enabled.

A reflected XSS flaw in GlobalProtect (CVE-2025-0133) allows malicious JavaScript execution. PoC exploit code is available. Update your PAN-OS.

Explore the CVE-2025-0110 PoC exploit details for Palo Alto Networks' PAN-OS firewall and its security implications.
Understand CVE-2025-0108 & CVE-2025-0110 vulnerabilities in PAN-OS. Learn how it can allow attackers to bypass authentication and its risks.
Stay informed about the latest security advisory from Palo Alto Networks regarding vulnerabilities in the Expedition migration tool.

Urgent warning: Exploited vulnerability in Palo Alto Networks PAN-OS firewall software (CVE-2024-3393) allows attackers to disable network security.
Critical vulnerability in Palo Alto Networks PAN-OS software: CVE-2024-3393 could disrupt firewall operations and force maintenance mode.

Palo Alto Networks alerts customers to a potential PAN-OS vulnerability. Review your access configurations and follow recommended best practice deployment guidelines.
PAN-OS Vulnerabilities: Command Injection (CVE-2024-8686) and GlobalProtect Exposure (CVE-2024-8687)
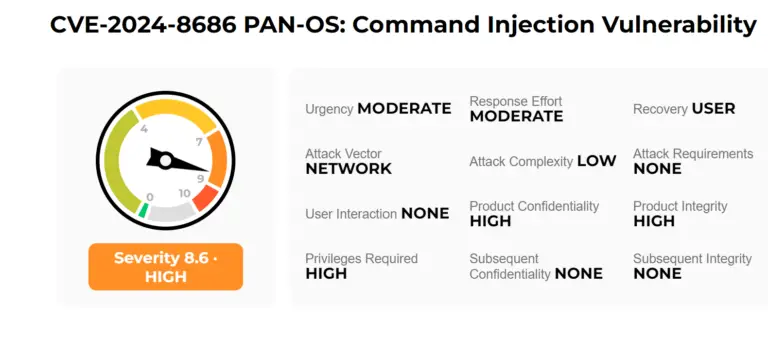
PAN-OS Vulnerabilities: Command Injection (CVE-2024-8686) and GlobalProtect Exposure (CVE-2024-8687)
Protect your organization from critical vulnerabilities in Palo Alto Networks products. Learn more about CVE-2024-8686 and CVE-2024-8687.