 Do Son
Install the Citrix security vulnerabilities update to patch critical Citrix security vulnerabilities affecting XenServer hypervisors and Scout gateways.
CVE-2026-111497
Arista fixed critical Arista security vulnerabilities CVE-2026-111497 and CVE-2026-98432 that allow unauthenticated remote code execution. Update now.
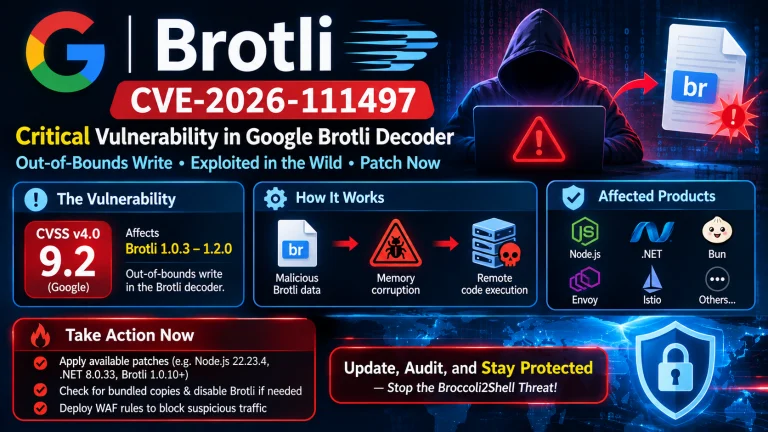
Brotli vulnerability CVE-2026-111497 affected products list: fixes for Node.js, .NET, Envoy, PAN-OS and distros, plus VMware and others still unpatched.
Broadcom warns of a VMware SDDC Manager vulnerability, CVE-2026-111497 (CVSS 9.8), from the Node.js Brotli vulnerability. Patches pending.
CISA KEV catalog adds actively exploited Magento flaw CVE-2026-48356 and Brotli vulnerability CVE-2026-111497. Patch before November 10.
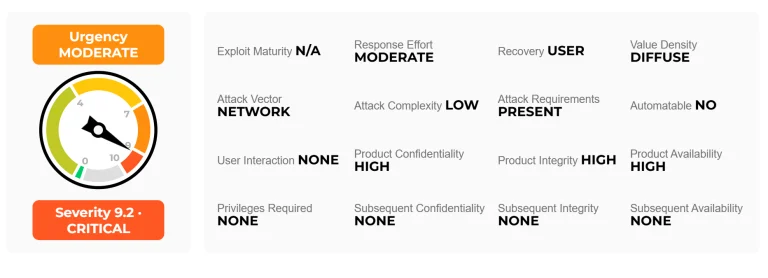
Palo Alto confirms PAN-OS Brotli vulnerability CVE-2026-111497, a CVSS 9.2 buffer overflow in PAN-OS 12.2, 12.1 and 11.2. Install the hotfixes now.
Microsoft's out-of-band .NET security update fixes Brotli flaw CVE-2026-111497 and Linux tarball bug CVE-2026-114148. Update to 8.0.33 or 9.0.22.
The Node.js security release fixes 10 flaws, including a Brotli remote code execution bug, CVE-2026-111497. Update to 26.12.1, 24.22.1 or 22.23.4.