 Do Son
Palo Alto confirms PAN-OS Brotli vulnerability CVE-2026-111497, a CVSS 9.2 buffer overflow in PAN-OS 12.2, 12.1 and 11.2. Install the hotfixes now.
firewall security
Palo Alto confirms PAN-OS PHP2Shell flaws CVE-2026-109618 and CVE-2026-109619 affect the firewall management interface. Restrict access and patch.
WatchGuard patched CVE-2026-19313 and more Fireware flaws, pre-authentication remote code execution bugs rated CVSS 9.3. Update firewalls now.

CVE-2026-18574 is a Check Point authentication bypass rated CVSS 9.3, letting attackers run commands as admin. Patch via the latest Jumbo Hotfix.
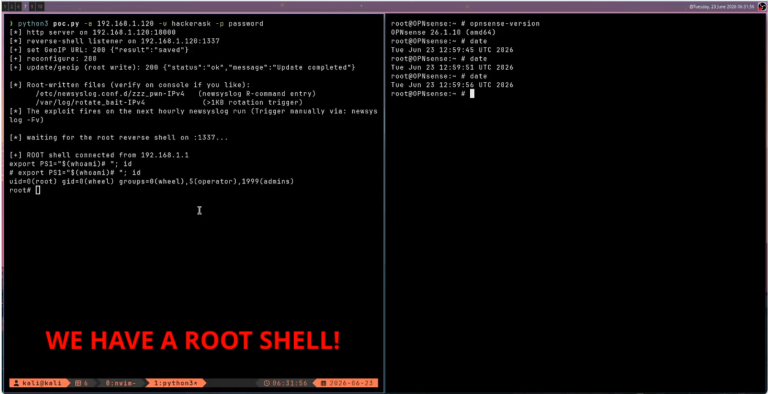
OPNsense root RCE flaws are public with PoC code. CVE-2026-57155 (9.9) chains an arbitrary file write to root. Patch 26.1.11 or 26.4.1p1 now.

A PAN-OS buffer overflow, CVE-2026-0288, enables arbitrary code execution on Palo Alto firewalls. Patch now.

Palo Alto Networks patches CVE-2026-0263 and CVE-2026-0265. Fixes for IKEv2 RCE and CAS bypass are now available. Update your PAN-OS firewalls immediately!

Urgent: Public PoC for OPNsense CVE-2026-44194 and CVE-2026-45158. Critical flaws allow root command execution via DHCP and User sync. Update to 26.1.8 now!
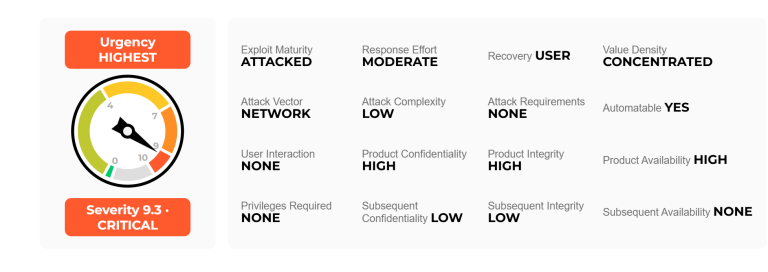
Palo Alto Networks confirms CVE-2026-0300 is being exploited in the wild. The 9.3 CVSS flaw allows unauthenticated root RCE. Secure your PAN-OS firewalls now!

Public PoC exploit released for OPNsense! A critical root-level RCE and lockout bypass allow total firewall takeover. Upgrade to OPNsense 26.1.7 immediately.

SonicWall discloses critical SonicOS flaws (CVE-2026-0204) hitting Gen6 to Gen8 hardware. Apply the 2026 firmware patch now to prevent unauthorized access.
A critical 10.0 CVSS zero-click flaw (CVE-2026-20079) in Cisco Secure FMC gives unauthenticated attackers root access. Patch your systems immediately.
A critical 10.0 CVSS unauthenticated RCE flaw (CVE-2026-20131) in Cisco Secure FMC allows hackers root access via insecure Java deserialization. Patch now.
Critical PAN-OS flaw CVE-2026-0229 allows unauthenticated attackers to trigger reboot loops & maintenance mode via malicious packets. Patch immediately.

Arctic Wolf warns of automated FortiGate SSO attacks stealing configs and creating backdoors. Disable admin-forticloud-sso-login immediately.
Palo Alto warns: CVE-2026-0227 forces GlobalProtect firewalls into maintenance mode. Unauthenticated DoS risk. Update PAN-OS immediately.

Fortinet warns of active exploits for CVE-2020-12812, where attackers bypass 2FA on FortiGate firewalls by simply changing username capitalization.

Serious vulnerabilities in pfSense put networks at risk. Could your firewall be hacked? Learn about the exploits and how to stay safe.