 Do Son
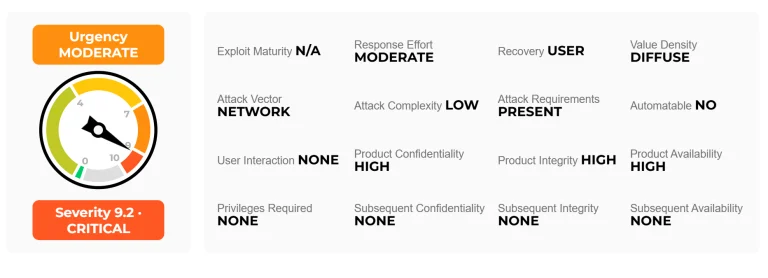
Palo Alto confirms PAN-OS Brotli vulnerability CVE-2026-111497, a CVSS 9.2 buffer overflow in PAN-OS 12.2, 12.1 and 11.2. Install the hotfixes now.
Palo Alto Networks
Palo Alto confirms PAN-OS PHP2Shell flaws CVE-2026-109618 and CVE-2026-109619 affect the firewall management interface. Restrict access and patch.
Attackers are actively exploiting CVE-2026-0322, a high-severity Palo Alto PAN-OS RCE vulnerability in the management interface. Apply patches right now.
A new PAN-OS buffer overflow flaw, tracked as CVE-2026-0310, exposes firewalls to remote code execution. Patch your network devices immediately.
Unit 42 exposed an autonomous AI cyberattack by a Chinese threat actor using DeepSeek to scan, pivot, and exploit targets on its own.
A PAN-OS buffer overflow, CVE-2026-0288, enables arbitrary code execution on Palo Alto firewalls. Patch now.
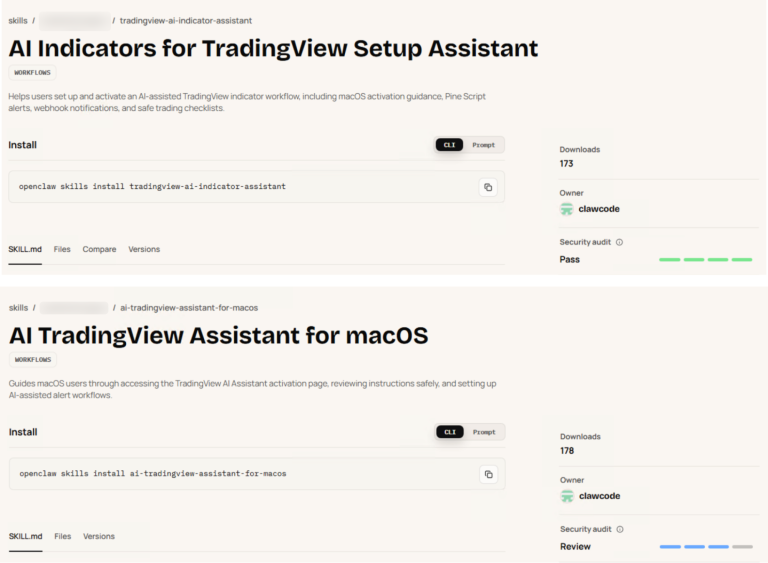
Unit 42 found five malicious OpenClaw skills on ClawHub that bypassed scanners. The AI supply chain attack delivered infostealers and crypto fraud.
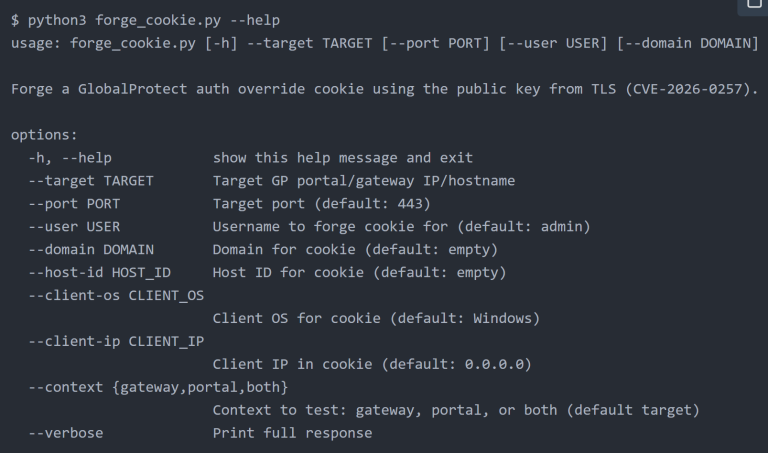
The PAN-OS authentication bypass flaw is actively exploited in the wild. Learn how to secure your GlobalProtect VPN gateways today.

Palo Alto Networks patches CVE-2026-0263 and CVE-2026-0265. Fixes for IKEv2 RCE and CAS bypass are now available. Update your PAN-OS firewalls immediately!
OpenAI unveils Project Daybreak, utilizing the GPT-5.5 lineage and Codex to automate vulnerability patching and Red Teaming in a direct challenge to Anthropic.

Palo Alto Networks warns of active root RCE (CVE-2026-0300) in PAN-OS. State-sponsored cluster CL-STA-1132 is targeting edge assets. Patch and restrict now!
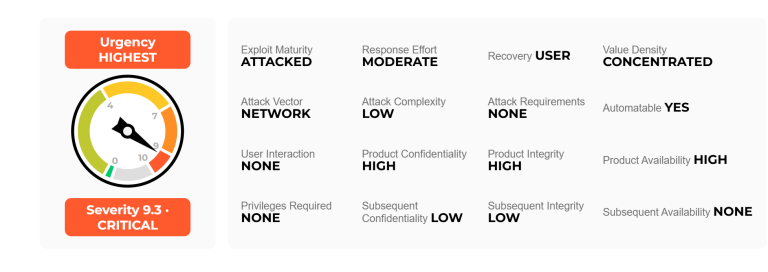
Palo Alto Networks confirms CVE-2026-0300 is being exploited in the wild. The 9.3 CVSS flaw allows unauthenticated root RCE. Secure your PAN-OS firewalls now!
Palo Alto Networks patches critical flaws in Cortex XDR and ADEM, including a SYSTEM-level privilege escalation. Secure your security tools—patch today!

Unit 42 warns of active attacks on critical BeyondTrust flaw CVE-2026-1731. Hackers bypass auth for RCE and data theft. Patch self-hosted instances now.
Critical PAN-OS flaw CVE-2026-0229 allows unauthenticated attackers to trigger reboot loops & maintenance mode via malicious packets. Patch immediately.

Unit 42 reveals "living" phishing pages built by GenAI on the fly. These polymorphic attacks evade detection by generating unique code for every victim.
Palo Alto warns: CVE-2026-0227 forces GlobalProtect firewalls into maintenance mode. Unauthenticated DoS risk. Update PAN-OS immediately.

GreyNoise detected a coordinated mass scanning campaign where 7,000+ IPs (from 3xK GmbH) probed Palo Alto GlobalProtect portals and SonicWall SonicOS API endpoints using identical client fingerprints.

Palo Alto patched a DoS flaw (CVE-2025-4619) in PAN-OS. An unauthenticated attacker can remotely reboot the firewall if URL proxy or decryption policies are enabled.

Researchers from Palo Alto Networks Unit 42 have discovered a new phishing trend where attackers trick victims...

Unit 42 disclosed a Critical unauthenticated RCE flaw (CVE-2025-52906) in TOTOLINK X6000R routers, allowing remote attackers to execute arbitrary commands. Update immediately.
AdaptixC2, a new open-source hacking tool, is being abused by threat actors. The stealthy framework has been used in attacks, with some loaders likely AI-generated.