 Do Son
A new report from Unit 42 reveals how cybercriminals are misusing generative AI to create realistic phishing sites, deepfake content, and fraudulent websites.
Palo Alto Networks

A critical vulnerability (CVE-2025-32433, CVSS 10.0) in Erlang/OTP’s SSH daemon allows unauthenticated RCE and is actively exploited, with a focus on operational technology (OT) networks.

Palo Alto Networks is acquiring identity security leader CyberArk for nearly $25B. The deal marks Palo Alto's strategic entry into identity security, a critical pillar for the AI era.

Unit 42 reveals "Gold Melody" uses leaked ASP.NET Machine Keys to achieve in-memory RCE via View State deserialization and privilege escalation via GodPotato, compromising web servers.

Palo Alto Networks reveals thousands of exploit attempts targeting RCE flaws in Apache Tomcat (CVE-2025-24813) and Apache Camel (CVE-2025-27636, CVE-2025-29891).

Palo Alto Networks exposes CL-CRI-1014, an IAB targeting African financial institutions. They use open-source tools like PoshC2 and Classroom Spy, disguised with forged signatures for covert network access.

A flaw (CVE-2025-4232) in GlobalProtect for macOS allows local users to escalate to root. Public PoC code exists. Update now!
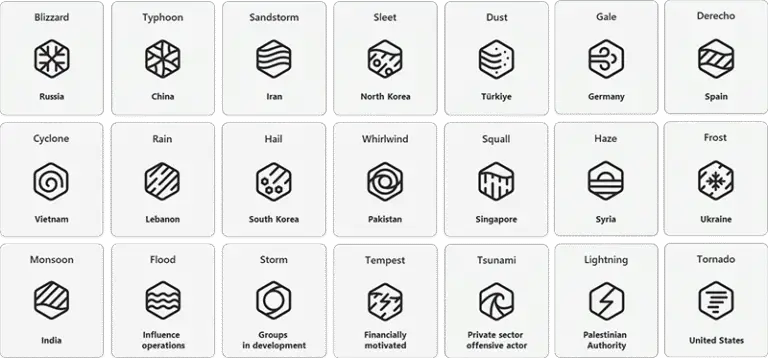
Microsoft, Google, and major cybersecurity firms are collaborating to unify hacker group naming, aiming for clearer threat intelligence across the industry.

A reflected XSS flaw in GlobalProtect (CVE-2025-0133) allows malicious JavaScript execution. PoC exploit code is available. Update your PAN-OS.

A proof-of-concept (PoC) exploit for CVE-2025-0108 has been publicly released, making it easier for threat actors to target unpatched systems.

Understand CVE-2025-0108 & CVE-2025-0110 vulnerabilities in PAN-OS. Learn how it can allow attackers to bypass authentication and its risks.

Stay informed about the latest security advisory from Palo Alto Networks regarding vulnerabilities in the Expedition migration tool.

Urgent warning: Exploited vulnerability in Palo Alto Networks PAN-OS firewall software (CVE-2024-3393) allows attackers to disable network security.
Critical vulnerability in Palo Alto Networks PAN-OS software: CVE-2024-3393 could disrupt firewall operations and force maintenance mode.

Learn about the stealthy operation of LITTLELAMB.WOOLTEA, a backdoor targeting Palo Alto Networks firewalls. Explore its entry point and persistent qualities.
Stay protected from CVE-2024-5921 vulnerability in Palo Alto Networks' GlobalProtect app. Learn how attackers can exploit this issue and how to prevent it.
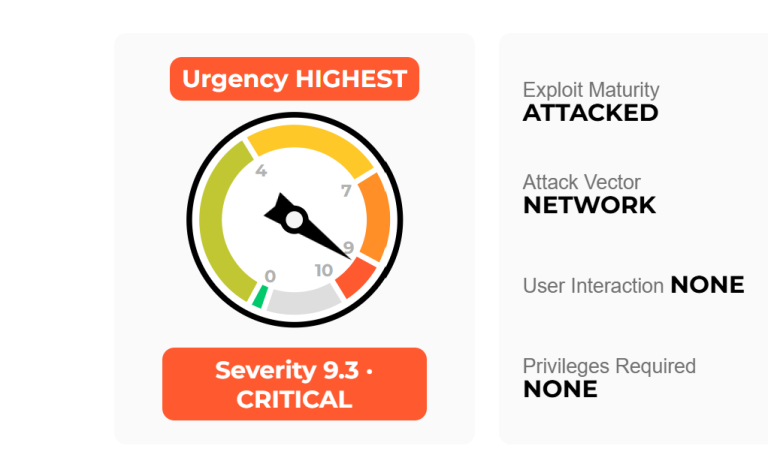
Palo Alto Networks has issued an urgent update to a recent security advisory, raising the severity level to "Critical" after observing active exploitation of a remote code execution vulnerability

Urgent warning about critical vulnerabilities in Palo Alto Networks Expedition: CVE-2024-9463 and CVE-2024-9465. Take action to protect your organization.

Palo Alto Networks alerts customers to a potential PAN-OS vulnerability. Review your access configurations and follow recommended best practice deployment guidelines.

The researcher published a proof of concept to exploit CVE-2024-9465 (CVSS 9.2) on vulnerable Palo Alto Networks’ Expedition devices.

Critical vulnerability in Palo Alto Networks' Expedition tool (CVE-2024-9466) could expose sensitive credentials to authenticated attackers.
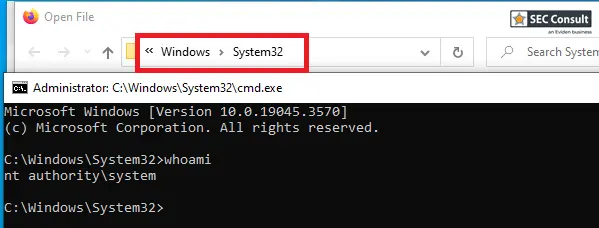
Learn about the recently discovered local privilege escalation vulnerability (CVE-2024-9473) affecting Palo Alto Networks' GlobalProtect software.