
 Do Son
Apple has released an urgent security update to patch a zero-day vulnerability (CVE-2025-43300) in its Image I/O framework that is being actively exploited in targeted attacks.

 cybernewswire
Frankfurt am Main, Germany, 20th August 2025, CyberNewsWire

The free DDNS service DuckDNS has gone offline, leaving users unable to access their home servers. Users are urged to migrate to an alternative service.

Google is overhauling its Play Store in the EU to comply with the Digital Markets Act, offering developers new options to steer users to external payment systems.

A critical vulnerability (CVE-2025-54336) in Plesk Obsidian could allow attackers to bypass the admin password and take complete control of affected servers.

Firefox is switching to CRLite for certificate revocation, a major change that improves security and privacy by eliminating the need for real-time OCSP queries.

Apple is reportedly manufacturing all four iPhone 17 models in India for the first time, marking a major shift in its strategy to reduce reliance on China.

Following U.S. intervention, the UK government has reportedly dropped its demand for Apple to install a backdoor in iCloud, which could restore Advanced Data Protection.

A new Windows update is causing major issues, including SSD lock-ups on some systems and broken reset/recovery options on all supported versions.

Qualcomm unveils the Snapdragon 7s Gen 4, a new mobile platform that brings significant CPU and GPU gains, plus flagship camera features to mid-range devices.

A 26-year-old UK hacker, tied to the Yemen Cyber Army, has been sentenced to 20 months in prison for breaching thousands of websites and stealing data.

Critical design flaws in Workhorse Software's municipal accounting platform could allow unauthenticated users to download full database backups with sensitive PII and financial records.

Google has released an urgent update for Chrome, patching a high-severity, out-of-bounds write vulnerability in the V8 JavaScript engine. Update your browser now.

A new report reveals GodRAT, a sophisticated backdoor based on the Gh0st RAT family, is using steganography to launch attacks via Skype messenger.

A new report from Unit 42 reveals how cybercriminals are misusing generative AI to create realistic phishing sites, deepfake content, and fraudulent websites.

A new report reveals a North Korean espionage campaign targeting embassies with spear phishing and a sophisticated C2 channel hidden on GitHub.

Microsoft has exposed PipeMagic, a new backdoor disguised as a ChatGPT app. It was used with a zero-day exploit to gain SYSTEM privileges and deploy ransomware.

A new analysis details how the RansomEXX gang exploited a use-after-free zero-day (CVE-2025-29824) in the Windows Common Log File System to gain SYSTEM privileges.
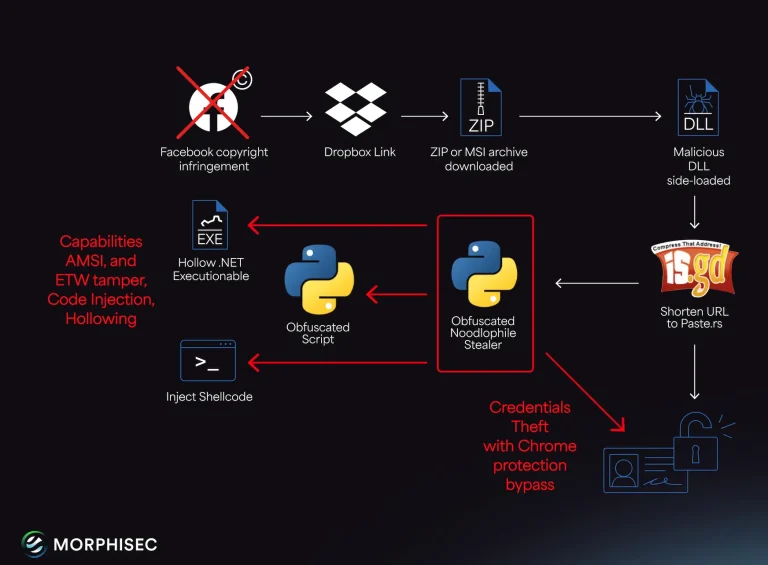
The Noodlophile infostealer has evolved from fake AI platforms to spear phishing, using fake copyright notices and DLL side-loading to target companies.

A new report reveals a multi-stage cryptomining attack delivered via infected USB drives, a tactic that leverages DLL hijacking to bypass security.

A new Android banking trojan, dubbed "Lazarus Stealer," is using sophisticated overlay attacks to steal financial credentials from users of Russian banks.

SoftBank is making a $2 billion investment in Intel, a move that signals confidence in the struggling chipmaker's future amidst reports of U.S. government interest.