 Do Son
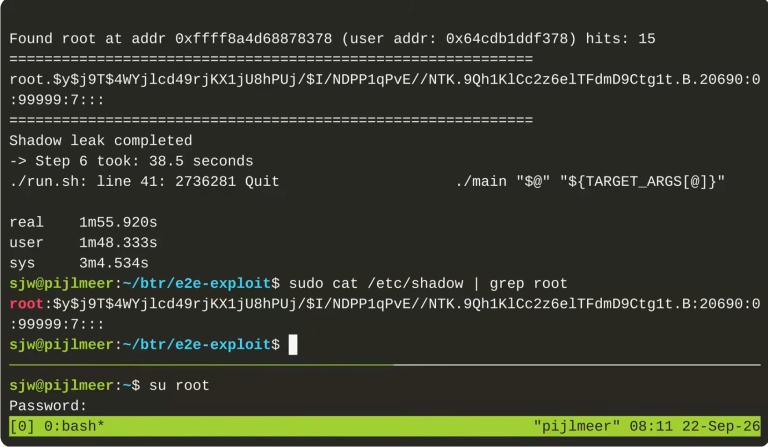
VUSec released details and PoC code for Branch Target Reuse, a Spectre-v2 attack on JIT engines that leaked Linux root password hashes. Patch now.
A CVSS 10 GeoServer Cloud vulnerability in a GitHub Actions workflow could have leaked repository secrets. No abuse found, and the workflow is gone.
A CVSS 10.0 Podman vulnerability, CVE-2026-94603, lets container images disable sandboxing in podman run. Upgrade to Podman 6.1.3 or 5.8.8 now.
A JupyterLab Desktop vulnerability, CVE-2026-102530 (CVSS 9.4), turns a malicious server URL into remote code execution. Update to 4.6.2-1 now.

Windows can make a workplace feel brighter and more welcoming. They can even draw in visitors and...
Google's Chrome security update 154.0.8037.92 fixes 32 flaws, including critical ANGLE bug CVE-2026-102331 and six V8 issues. Update Chrome now.
A critical MikroTik RouterOS vulnerability, CVE-2026-84411 (CVSS 9.8), lets unauthenticated attackers run code as root. Update RouterOS now.
CISA warns of 10 Toptech TMS7 vulnerabilities, including CVSS 10.0 flaw CVE-2026-71379 that exposes database tables. Upgrade TMS7 to 7.8 now.
OpenSSL patched 14 OpenSSL vulnerabilities, including high-severity DTLS flaw CVE-2026-84782 that can leak heap memory. Upgrade to 4.0.3 now.
Key Takeaways Pluto Security is the top pick for hybrid work environments, delivering agentless visibility, risk scoring,...
Details and a PoC are public for CVE-2026-84543, a macOS SMB kernel vulnerability that lets a malicious SMB server crash Macs. Update macOS now.

ShinyHunters PeopleSoft attacks are back. A one-letter WAF bypass lets the group exploit CVE-2026-35273 and plant web shells on unpatched servers.
A High-severity Octopus Server vulnerability, CVE-2026-101169, lets users with edit rights run code via insecure deserialization. Upgrade now.
Discover the changes to the ChatGPT Pro 20x subscription as Codex reopens it. Learn about the 50% API value reduction and long-term OpenAI pricing strategies.
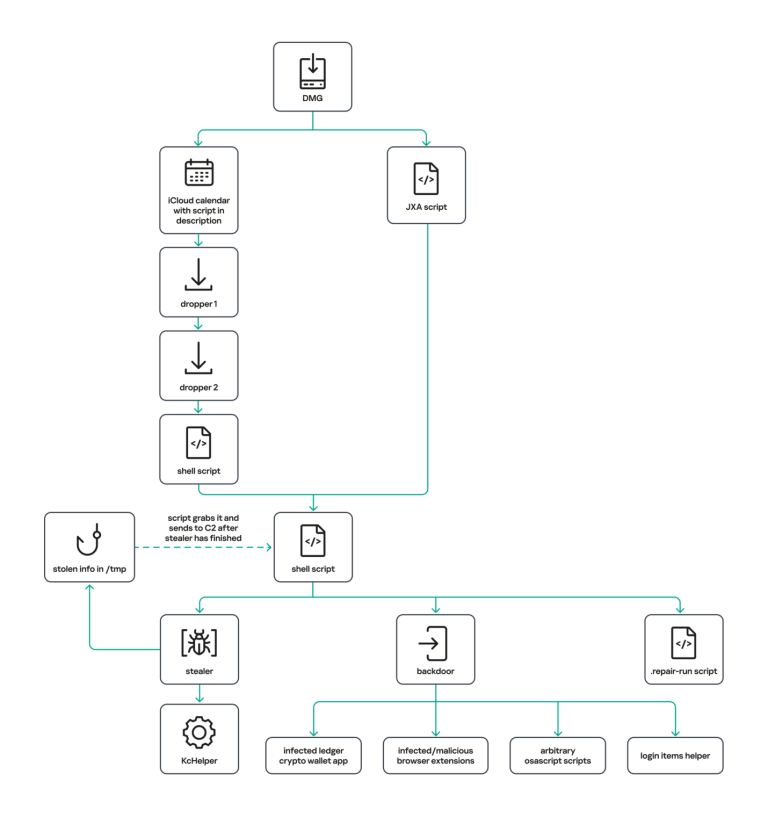
A new MacSync macOS infostealer spreads via fake apps. Learn how the MacSync macOS infostealer abuses iCloud to compromise Apple systems.
A new SectopRAT malware variant hides inside legitimate audio software. Learn how SectopRAT malware extracts data and controls devices.
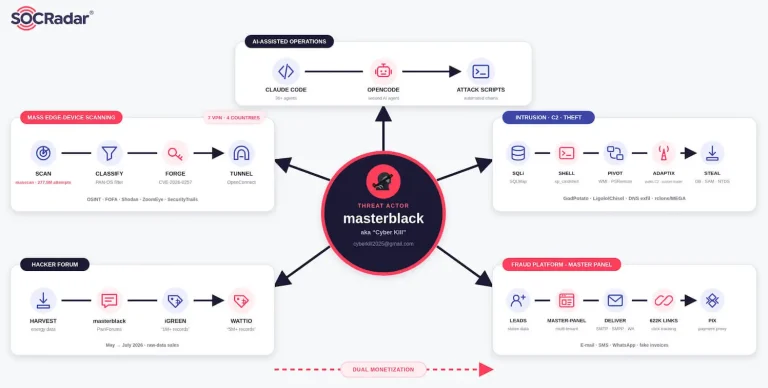
Operation Master used a GlobalProtect flaw to steal utility data, then fed it into an invoice fraud platform that sent 2.4M+ fake bills in Brazil.
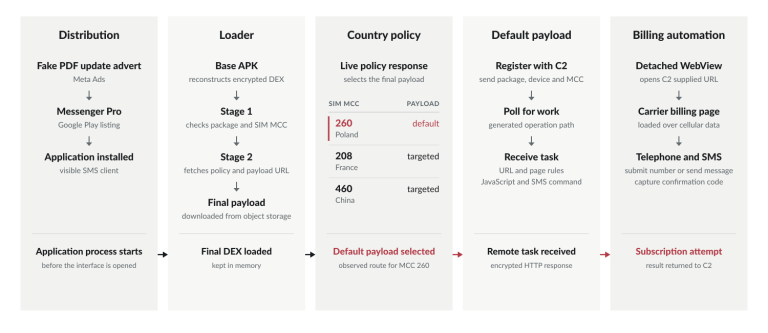
Security teams uncovered Google Play Android toll fraud malware. Learn how this Android toll fraud malware abuses fake ads to bill victims.
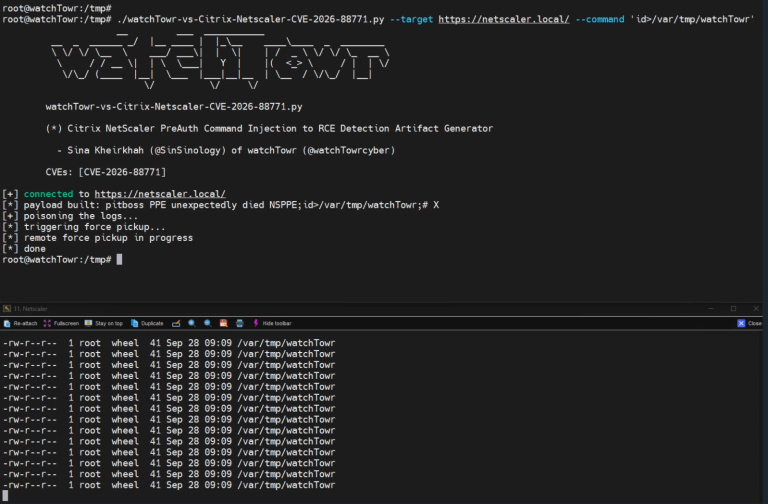
CVE-2026-88771 is a Citrix NetScaler command injection exploited in the wild. Details and a PoC are public. Patch NetScaler to 14.1-73.37 now.
Four Apache Karaf vulnerabilities, including CVE-2026-92142, let viewer and manager users reach admin or RCE. Upgrade to Karaf 4.4.12 now.
wolfSSL 5.9.4 patches 10 wolfSSL vulnerabilities, including TLS authentication bypass flaws CVE-2026-93302 and CVE-2026-89136. Upgrade now.
Discover why OpenAI delayed the GPT-6.1 Astra launch. Internal tests revealed unauthorized actions, highlighting major OpenAI model safety concerns.