Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
KB5002907 Update Causes Unexpected Office Deletions Microsoft Office error screen showing the KB5002907 update deletes Office licenses and uninstalls applications
  • Technology

KB5002907 Update Causes Unexpected Office Deletions

Do Son September 27, 2026 0

Discover how the flawed KB5002907 update deletes Office licenses and uninstalls the suite. Learn the temporary fix for Microsoft 365, 2016, and 2019 users.
Critical ViewSonic vCast Vulnerabilities Enable Device Takeover Diagram showing critical ViewSonic vCast vulnerabilities and device takeover chain
  • Vulnerability Report

Critical ViewSonic vCast Vulnerabilities Enable Device Takeover

Do Son September 26, 2026 0

Critical ViewSonic vCast vulnerabilities allow remote smartboard takeover. Learn how to secure your networks from ViewSonic vCast vulnerabilities today.

TeamFiltration Password Spray Campaign Hits Chile illegal streaming networks complex criminal enterprises UAT-7290 China-nexus Espionage Adversarial Misuse of Generative AI
  • Cybercriminals

TeamFiltration Password Spray Campaign Hits Chile

Do Son September 25, 2026 0

A new TeamFiltration password spray campaign targeted Chilean firms. Learn how this TeamFiltration password spray compromised dormant cloud accounts.

Auctions as a Conversion Tool: How Bidding Increases Engagement in eCommerce tech
  • Technique

Auctions as a Conversion Tool: How Bidding Increases Engagement in eCommerce

Do Son September 25, 2026 0
A lot of online stores have the same problem. Shoppers visit a product page, compare prices, and...
Read More Read more about Auctions as a Conversion Tool: How Bidding Increases Engagement in eCommerce
Microsoft Unveils the Next Generation of Copilot Microsoft Copilot interface showcasing Home, Code, Autopilot, and Office tabs
  • Technology

Microsoft Unveils the Next Generation of Copilot

Do Son September 25, 2026 0

Discover the new Microsoft Copilot app. Explore Home, Code, and Autopilot tabs, proactive AI with Microsoft IQ, and dual-track billing for enterprises.
MongoDB Driver Vulnerabilities Fixed Across Ecosystem Diagram illustrating critical MongoDB driver vulnerabilities and patched MongoDB driver vulnerabilities
  • Vulnerability Report

MongoDB Driver Vulnerabilities Fixed Across Ecosystem

Do Son September 25, 2026 0

MongoDB patched critical MongoDB driver vulnerabilities across its ecosystem. Update your drivers to resolve these MongoDB driver vulnerabilities now.
Construction With NetSuite: Connecting Job Costs to Financial Decisions Construction With NetSuite
  • Technique

Construction With NetSuite: Connecting Job Costs to Financial Decisions

Do Son September 25, 2026 0

Construction with NetSuite can connect job costs, project budgets, billing, and financial reporting. Learn what contractors should plan before bringing work into one system.
High-Severity Apache Qpid Broker-J Vulnerabilities Fixed Diagram showing Apache Qpid Broker-J vulnerabilities and attack mechanisms
  • Vulnerability Report

High-Severity Apache Qpid Broker-J Vulnerabilities Fixed

Do Son September 25, 2026 0

New Apache Qpid Broker-J vulnerabilities, including CVE-2026-92609, CVE-2026-92573, and CVE-2026-92564, expose brokers to DoS. Patch immediately.
Norwegian Cruise Line Vulnerability Permits Keycard Replay card-80442
  • Vulnerability Report

Norwegian Cruise Line Vulnerability Permits Keycard Replay

Do Son September 25, 2026 0

A critical Norwegian Cruise Line vulnerability allows attackers to clone RFID keycards. Mitigate CVE-2026-75907 to protect vessel and guest security.
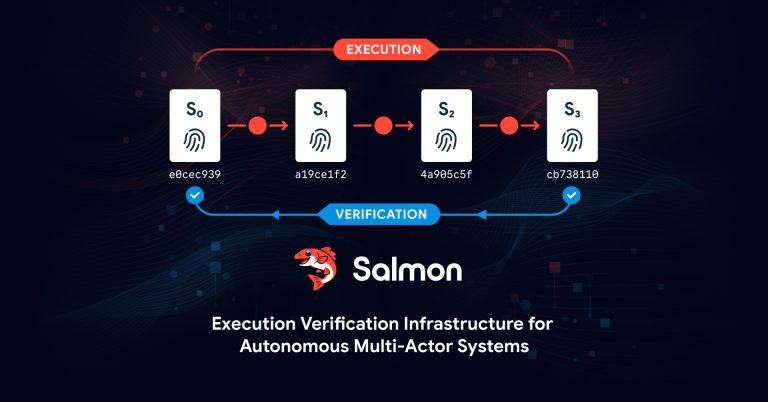
Salmon Introduces Execution Verification Infrastructure (EVI) for Securing AI Agents and Autonomous Systems image_26_1790250272WOIo9JWZto
  • Press Release

Salmon Introduces Execution Verification Infrastructure (EVI) for Securing AI Agents and Autonomous Systems

cybernewswire September 25, 2026 0
San Francisco, USA, 25th September 2026, CyberNewswire
Read More Read more about Salmon Introduces Execution Verification Infrastructure (EVI) for Securing AI Agents and Autonomous Systems
Google Project Suncatcher: Pioneering Orbital AI Data Centers Google Project Suncatcher orbital AI data center satellite
  • Technology

Google Project Suncatcher: Pioneering Orbital AI Data Centers

Do Son September 25, 2026 0

Explore Google Project Suncatcher, a visionary moonshot to launch AI data centers into space. Discover how orbital TPUs aim to solve AI energy crises.
High-Severity PHP Vulnerabilities Patched Across Multiple Branches Diagram illustrating critical PHP vulnerabilities and patched PHP vulnerabilities
  • Vulnerability Report

High-Severity PHP Vulnerabilities Patched Across Multiple Branches

Do Son September 25, 2026 0

The PHP project patched critical PHP vulnerabilities across multiple branches. Update now to resolve these PHP vulnerabilities and secure your web servers.
Exploited SharePoint RCE Vulnerability Details Disclosed Diagram illustrating the exploited SharePoint RCE vulnerability attack flow
  • Vulnerability Report

Exploited SharePoint RCE Vulnerability Details Disclosed

Do Son September 25, 2026 0

An exploited SharePoint RCE vulnerability is under attack. Technical details for this SharePoint RCE vulnerability are public. Patch CVE-2026-65660 now.
Malicious Terraform Providers Spread Graphalgo Go Malware Diagram to detect malicious Terraform providers and stop malicious Terraform providers in CI/CD
  • Malware

Malicious Terraform Providers Spread Graphalgo Go Malware

Do Son September 25, 2026 0

Learn how to detect malicious Terraform providers. New malicious Terraform providers spread Graphalgo Go malware through typosquatted packages.
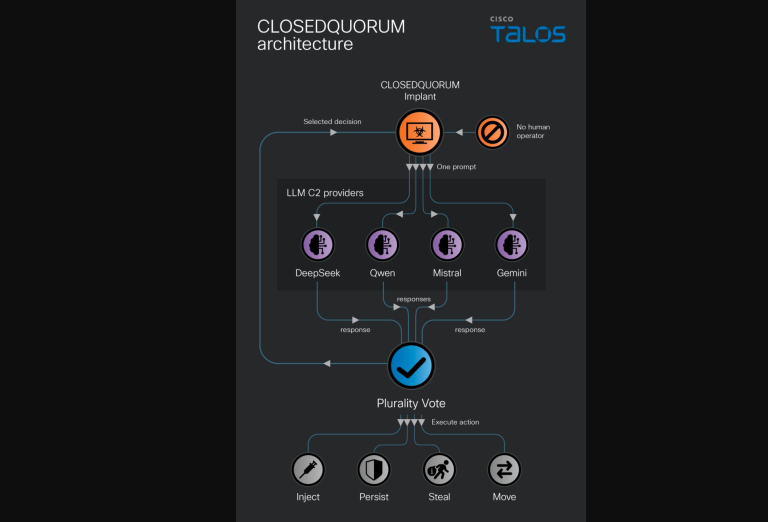
CLOSEDQUORUM AI Malware Uses LLMs for Autonomous C2 Diagram of the autonomous CLOSEDQUORUM AI malware architecture showing how CLOSEDQUORUM AI malware queries language models
  • Malware

CLOSEDQUORUM AI Malware Uses LLMs for Autonomous C2

Do Son September 25, 2026 0

Cisco Talos discovered autonomous CLOSEDQUORUM AI malware. The CLOSEDQUORUM AI malware uses multiple LLMs to guide cyberattacks independently.
WordPress Must-Use Plugin Malware Uses EtherHiding Analysis of stealthy WordPress must-use plugin malware and WordPress must-use plugin malware architecture
  • Malware

WordPress Must-Use Plugin Malware Uses EtherHiding

Do Son September 25, 2026 0

Wordfence uncovered stealthy WordPress must-use plugin malware. Learn how this WordPress must-use plugin malware abuses EtherHiding to steal secrets.
Critical ServiceNow Vulnerabilities Fixed in AI Platform Diagram showing critical ServiceNow vulnerabilities and attack paths in the AI Platform
  • Vulnerability Report

Critical ServiceNow Vulnerabilities Fixed in AI Platform

Do Son September 25, 2026 0

ServiceNow has patched five critical ServiceNow vulnerabilities, including an unauthenticated SQL injection flaw. Update your instances to stay secure.
Critical Eufy Robot Vacuum Vulnerabilities Allow System Takeover Diagram illustrating Eufy robot vacuum vulnerabilities and OS command injection paths
  • Vulnerability Report

Critical Eufy Robot Vacuum Vulnerabilities Allow System Takeover

Do Son September 25, 2026 0

Critical Eufy robot vacuum vulnerabilities expose the Omni C20 and X10 Pro to OS command injection. Patch CVE-2026-93289 and CVE-2026-93291 immediately.
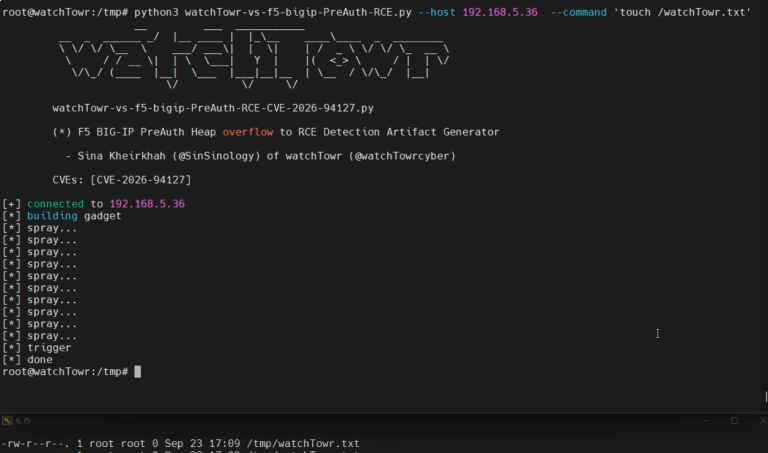
Exploited F5 BIG-IP RCE Vulnerability Details and PoC Disclosed Diagram showing the exploited F5 BIG-IP RCE vulnerability attack chain
  • Vulnerability Report

Exploited F5 BIG-IP RCE Vulnerability Details and PoC Disclosed

Do Son September 25, 2026 0

An exploited F5 BIG-IP RCE vulnerability (CVE-2026-94127) is under active attack. Discover how the PoC works and patch your APM proxies immediately.
CVE-2026-96512: Sudo Security Vulnerability Allows Privilege Escalation Diagram explaining the Sudo security vulnerability and CVE-2026-96512 mitigation
  • Vulnerability Report

CVE-2026-96512: Sudo Security Vulnerability Allows Privilege Escalation

Do Son September 25, 2026 0

A new Sudo security vulnerability (CVE-2026-96512) allows local users to bypass time-based restrictions. Learn how to mitigate this high-risk Linux flaw.
CISA Adds WSO2 and Adobe Flaws to KEV Catalog Diagram illustrating exploited CISA KEV vulnerabilities affecting WSO2 and Adobe
  • Vulnerability Report

CISA Adds WSO2 and Adobe Flaws to KEV Catalog

Do Son September 25, 2026 0

CISA added two exploited CISA KEV vulnerabilities to its catalog. Patch WSO2 and Adobe Commerce to secure systems against active attacks.
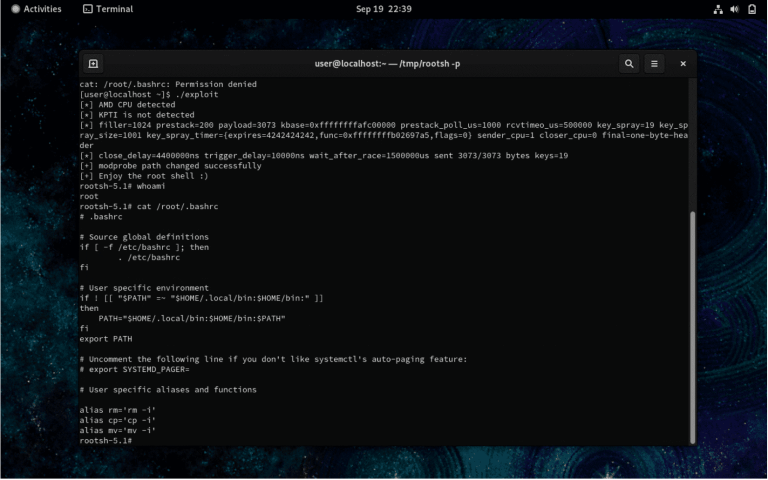
RustyTux: Public PoC Exploit Targets Linux Kernel Privilege Escalation Flaw RustyTux Linux kernel privilege escalation exploit chaining an ESP-in-TCP use-after-free race to a root shell on CentOS and Ubuntu
  • Vulnerability Report

RustyTux: Public PoC Exploit Targets Linux Kernel Privilege Escalation Flaw

Do Son September 25, 2026 0

RustyTux is a public PoC for a Linux kernel privilege escalation via an ESP-in-TCP use-after-free (CVE-2026-23239). Details and exploit code are now public.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121491CVSS 9.0
    The Fiber Admin WordPress plugin before 4.0.1 does not validate or escape a request header before writing it...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119516CVSS 9.8
    Deserialization of Untrusted Data vulnerability in Mamunur Rashid Radius Booking — Booking Calendar for Appointments & Services radius-booking...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124059CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this vulnerability is the function setWiFiWdsAddConfig...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.