Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
SCOUTz Prospect Intelligence Platform Launches for MSPs with 30-Day Beta SCOUTz_-_Header_Banner_1200x720_1790189561nFevdYxfGB
  • Press Release

SCOUTz Prospect Intelligence Platform Launches for MSPs with 30-Day Beta

cybernewswire September 24, 2026 0
Phoenix, Arizona, 24th September 2026, CyberNewswire
Read More Read more about SCOUTz Prospect Intelligence Platform Launches for MSPs with 30-Day Beta
Microsoft Explores Intrusive In-Game Advertising Microsoft game ad patent concept showing a paused game screen for promotional content
  • Technology

Microsoft Explores Intrusive In-Game Advertising

Do Son September 24, 2026 0

Discover the new Microsoft game ad patent. Learn how this system intelligently pauses gameplay to show advertisements and rewards players with free credits.
Meta Muse Secretly Used Humans for AI Phone Calls Meta Muse AI agent phone calling feature secretly handed off to human contractors
  • Data Leak

Meta Muse Secretly Used Humans for AI Phone Calls

Do Son September 24, 2026 0

Meta Muse human concierge secretly routed AI phone calls to contractors, exposing users' private data. Meta paused the feature after a racist remark.

ShinyHunters Syndicate Alleges Major FBI Network Compromise Bling Libra
  • Data Leak

ShinyHunters Syndicate Alleges Major FBI Network Compromise

Do Son September 24, 2026 0

Discover how the ShinyHunters hacking group claims to have orchestrated a massive FBI data breach, stealing employee records via an Oracle zero-day flaw.
Windows 11 Update Breaks Always On VPN Connections Windows 11 Always On VPN connection stuck after the September 2026 update with a port in use error
  • Windows

Windows 11 Update Breaks Always On VPN Connections

Do Son September 24, 2026 0

Windows 11 Always On VPN fails to connect after the September 2026 update. Switch to a fixed IKEv2 or SSTP protocol until Microsoft ships a permanent fix.
Chinese Hackers Deploy UTA0565 Zero-Day Exploits Diagram of Chinese UTA0565 zero-day exploits showing how UTA0565 zero-day exploits drop CLEANGULP malware
  • Cybercriminals

Chinese Hackers Deploy UTA0565 Zero-Day Exploits

Do Son September 24, 2026 0

Chinese UTA0565 zero-day exploits strike global targets. Learn how the UTA0565 zero-day exploits deploy CLEANGULP malware.

New TASK#STOMP PowerShell Backdoor Targets Windows Diagram showing how prompt injection attacks and prompt injection techniques threaten AI security.
  • Malware

New TASK#STOMP PowerShell Backdoor Targets Windows

Do Son September 24, 2026 0

Learn how the new TASK#STOMP PowerShell backdoor steals data. The TASK#STOMP PowerShell backdoor abuses native Windows tools for persistence.
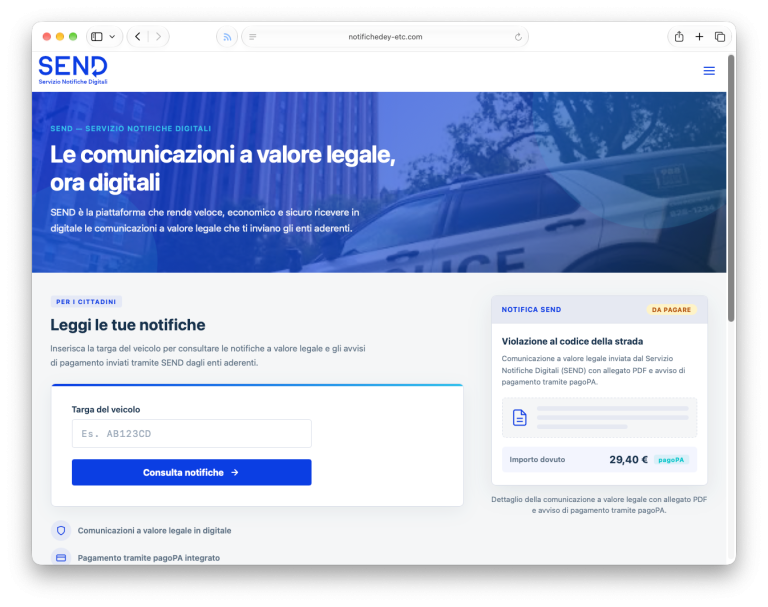
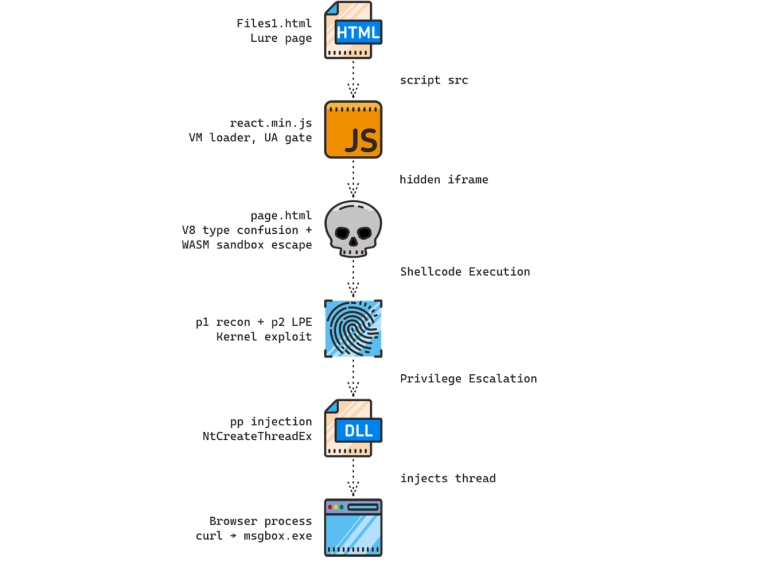
Italian Phishing Campaign Delivering an iOS Exploit Chain Italian phishing campaign delivering an iOS exploit chain and Coruna Pro V2 exploit kit details
  • Cybercriminals

Italian Phishing Campaign Delivering an iOS Exploit Chain

Do Son September 24, 2026 0

Learn about the new Italian phishing campaign delivering an iOS exploit chain. This Italian phishing campaign targets outdated iPhones using fake SEND portals.
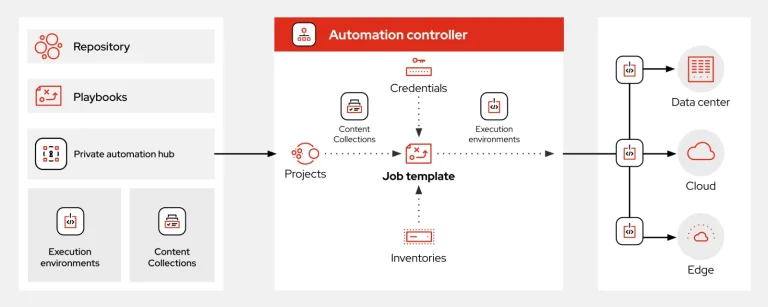
Ansible Automation Platform Vulnerabilities Allow Exploits Diagram of Ansible Automation Platform vulnerabilities and critical Ansible Automation Platform vulnerabilities
  • Vulnerability Report

Ansible Automation Platform Vulnerabilities Allow Exploits

Do Son September 24, 2026 0

Patch these critical Ansible Automation Platform vulnerabilities to prevent privilege escalation. Ansible Automation Platform vulnerabilities expose secrets.
CVE-2026-48842: Roundcube Webmail Vulnerability Exploited in the Wild Diagram of the exploited Roundcube Webmail vulnerability and SQL injection attack chain
  • Vulnerability Report

CVE-2026-48842: Roundcube Webmail Vulnerability Exploited in the Wild

Do Son September 24, 2026 0

An exploited Roundcube Webmail vulnerability allows SQL injection attacks. Learn how CVE-2026-48842 impacts servers and apply the latest patches immediately.
Critical Rancher XSS Vulnerability Exposes Admin Credentials Diagram explaining the Rancher XSS vulnerability and CVE-2026-88804 attack chain
  • Vulnerability Report

Critical Rancher XSS Vulnerability Exposes Admin Credentials

Do Son September 24, 2026 0

A critical Rancher XSS vulnerability tracked as CVE-2026-88804 exposes admin sessions. Update your clusters immediately to prevent system compromise.
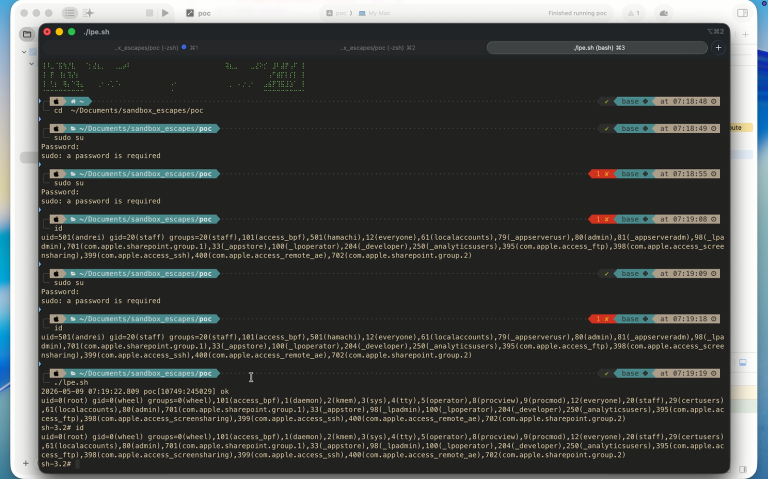
macOS DesktopServicesHelper LPE Vulnerability Details and PoC Disclosed Diagram explaining the critical macOS DesktopServicesHelper vulnerability and root escalation chain
  • Vulnerability Report

macOS DesktopServicesHelper LPE Vulnerability Details and PoC Disclosed

Do Son September 24, 2026 0

Details and PoC for the critical macOS DesktopServicesHelper vulnerability are public. Learn how CVE-2026-43783 enables root access.
Critical cPanel Security Vulnerabilities Allow Root Escalation Diagram illustrating cPanel security vulnerabilities and critical cPanel security vulnerabilities affecting WHM
  • Vulnerability Report

Critical cPanel Security Vulnerabilities Allow Root Escalation

Do Son September 24, 2026 0

cPanel patched critical cPanel security vulnerabilities including CVE-2026-87899. Update cPanel and WP Toolkit now to prevent privilege escalation.
Fluent Bit Vulnerability Details and PoC Disclosed Diagram of the critical Fluent Bit vulnerability CVE-2026-61674 buffer overflow
  • Vulnerability Report

Fluent Bit Vulnerability Details and PoC Disclosed

Do Son September 24, 2026 0

Technical details and a PoC for a critical Fluent Bit vulnerability (CVE-2026-61674) are public. Patch this Fluent Bit vulnerability to prevent RCE attacks.
Critical GitHub Enterprise Server Vulnerabilities Addressed Diagram showing the attack chain of critical GitHub Enterprise Server vulnerabilities
  • Vulnerability Report

Critical GitHub Enterprise Server Vulnerabilities Addressed

Do Son September 24, 2026 0

Critical GitHub Enterprise Server vulnerabilities allow remote code execution. Update your instances now to mitigate these high-severity security flaws.
GitLab Critical Patch Release Fixes Severe RCE Flaws Diagram illustrating the GitLab critical patch release mitigating the GitLab RCE vulnerability
  • Vulnerability Report

GitLab Critical Patch Release Fixes Severe RCE Flaws

Do Son September 23, 2026 0

A GitLab critical patch release addresses two CVEs enabling a GitLab RCE vulnerability. Update your CI/CD pipelines to prevent arbitrary code execution.
Apache Tomcat Vulnerabilities Fixed in 11.0.26 Update Diagram illustrating Apache Tomcat vulnerabilities including CVE-2026-87022
  • Vulnerability Report

Apache Tomcat Vulnerabilities Fixed in 11.0.26 Update

Do Son September 23, 2026 0

Apache patched 15 Apache Tomcat vulnerabilities in version 11.0.26. Update to secure your servers against HTTP/2, AJP, and WebSocket DoS flaws today.
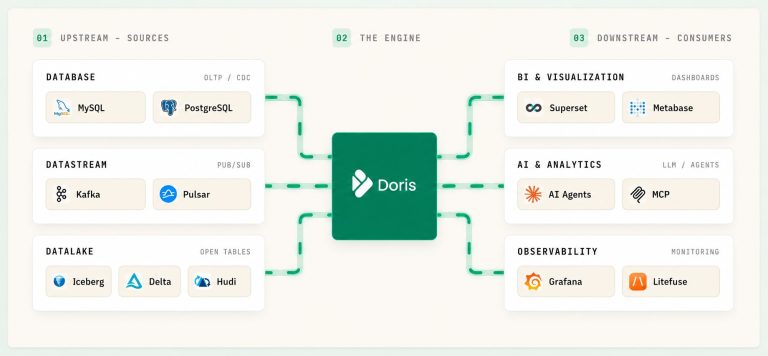
Apache Doris Vulnerabilities Patched in New Updates Diagram of patched Apache Doris vulnerabilities and attack paths
  • Vulnerability Report

Apache Doris Vulnerabilities Patched in New Updates

Do Son September 23, 2026 0

The team patched Apache Doris vulnerabilities in new updates. Learn how these Apache Doris vulnerabilities impact clusters and update now.
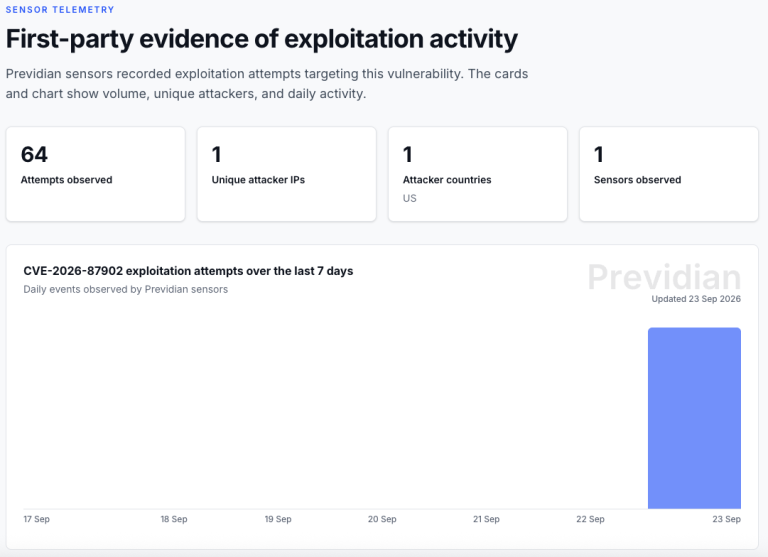
Exploited WordPress RCE Vulnerability Details and PoC Disclosed Diagram showing the exploited WordPress RCE vulnerability and attack chain
  • Vulnerability Report

Exploited WordPress RCE Vulnerability Details and PoC Disclosed

Do Son September 23, 2026 0

An exploited WordPress RCE vulnerability (CVE-2026-87902) is under attack. Details and PoC exploit code are public. Patch your sites now.
Critical ManageEngine Security Vulnerabilities Require Immediate Patching ManageEngine security vulnerabilities and OpManager vulnerabilities overview
  • Vulnerability Report

Critical ManageEngine Security Vulnerabilities Require Immediate Patching

Do Son September 23, 2026 0

ManageEngine security vulnerabilities expose servers to remote code execution. Patch these OpManager vulnerabilities and CVE-2026-19599 to secure your network.
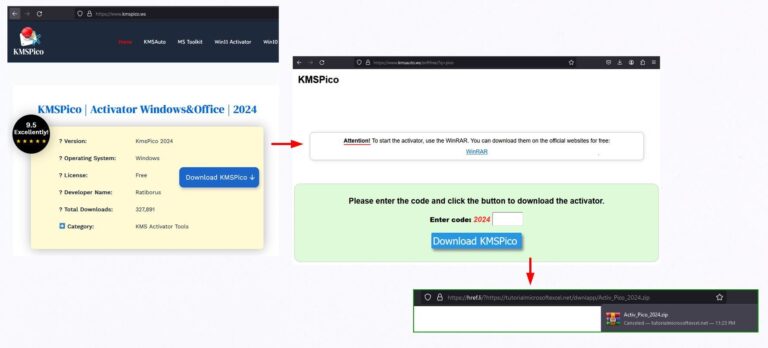
Vidar Information Stealer Upgrades Evasion Tactics AutoIt-Delivering-Vidar-Stealer
  • Malware

Vidar Information Stealer Upgrades Evasion Tactics

Do Son September 23, 2026 0

Discover the latest Vidar information stealer obfuscation tactics. ThreatLabz reveals how the malware uses a virtual machine and custom stream ciphers.

WordPress Stored XSS Details and PoC Publicly Disclosed CVE-2024-11972 - Hunk Companion
  • Vulnerability Report

WordPress Stored XSS Details and PoC Publicly Disclosed

Do Son September 23, 2026 0

Details and PoC exploit code for a critical WordPress stored XSS are public. Learn how CVE-2026-93485 enables RCE and patch WordPress today.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121491CVSS 9.0
    The Fiber Admin WordPress plugin before 4.0.1 does not validate or escape a request header before writing it...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119516CVSS 9.8
    Deserialization of Untrusted Data vulnerability in Mamunur Rashid Radius Booking — Booking Calendar for Appointments & Services radius-booking...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124059CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this vulnerability is the function setWiFiWdsAddConfig...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.