 Do Son

The MITRE timeline details the attack path taken by the threat actor | Image: Unit 42
The notorious hacking syndicate ShinyHunters recently announced that their team successfully infiltrated the internal systems of the Federal Bureau of Investigation (FBI). They did this by exploiting an undisclosed Oracle PeopleSoft vulnerability. The hackers subsequently claimed to have exfiltrated extensive dossiers concerning FBI personnel and prospective job applicants. This digital assault primarily appears to have compromised the FBI’s recruitment portal. That portal is a repository safeguarding the personal resumes and other documentation of candidates.
Initiating the Assault via an Oracle Software Vulnerability
The hacking collective asserts that the FBI utilizes the Oracle PeopleSoft framework, which allegedly harbors an unpatched, zero-day vulnerability capable of facilitating remote code execution. After penetrating the internal FBI network through this exploit, the adversaries laterally navigated into the AWS GovCloud environment administered by the Bureau. Subsequently, they extracted an estimated two to three terabytes of highly sensitive data from this cloud infrastructure.
The intruders purport that this massive dataset encompasses detailed profiles and internal records of both active and former FBI employees, alongside individuals who submitted resumes to the agency. However, these assertions rely entirely upon the hackers’ own declarations. Currently, the FBI, Amazon Web Services, and Oracle have all abstained from issuing official responses regarding this alleged security incident.
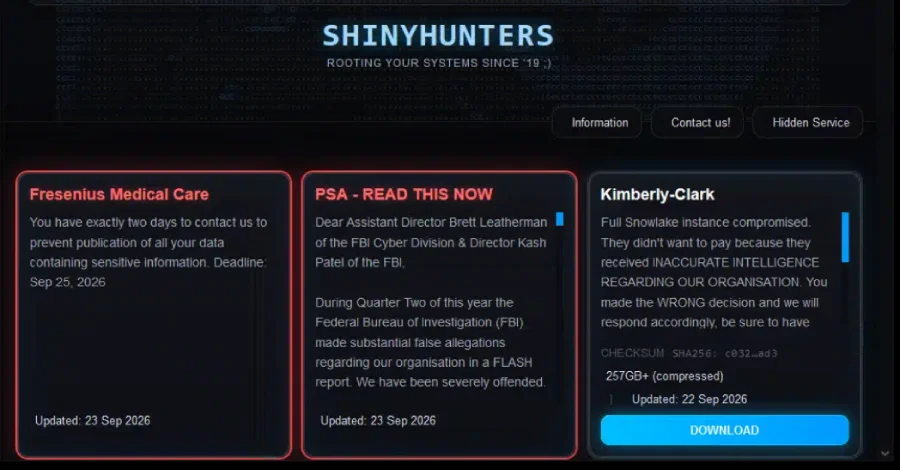
Launching a Retaliatory Campaign Against the Bureau
The ShinyHunters syndicate emphatically stated that this devastating cyberattack was not motivated by financial gain. Instead, it serves as direct retaliation for a security alert the FBI issued against the ShinyHunters group this past May. At that time, the hackers demanded that the Bureau amend or retract the relevant intelligence within a week. The FBI ostensibly ignored this ultimatum. Consequently, ShinyHunters executed this retributive strike against the agency.
According to a detailed report discussing how hackers say they have data on all FBI employees, an official FBI spokesperson acknowledged awareness of the alleged security breach during a recent interview. However, the agency maintains that an active investigation is currently underway, rendering them temporarily unable to confirm whether their internal networks suffered a genuine intrusion or if any sensitive data was definitively compromised.
Support Our Threat Intelligence
Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
