 Do Son
A ShinyHunters hacker arrest in Jordan may aid the FBI, as an alleged member reportedly shares devices and chats. Here is what we know.
ShinyHunters

ShinyHunters PeopleSoft attacks are back. A one-letter WAF bypass lets the group exploit CVE-2026-35273 and plant web shells on unpatched servers.

Discover how the ShinyHunters hacking group claims to have orchestrated a massive FBI data breach, stealing employee records via an Oracle zero-day flaw.
ReliaQuest links the new Helix data extortion group to BlackFile, using vishing and device code phishing to steal SharePoint data.

ShinyHunters leverages a zero-day Oracle PeopleSoft exploit to compromise higher education systems, exposing sensitive data via the CVE-2026-35273 flaw.
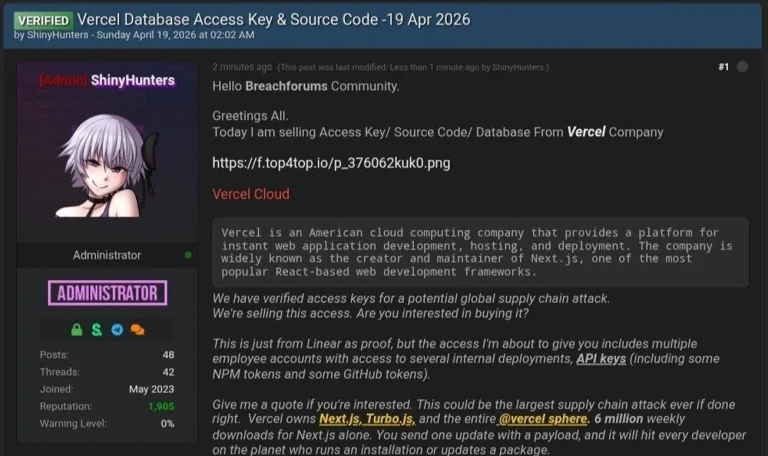
Vercel investigates a major breach by ShinyHunters. With Next.js source code and tokens at risk, developers must rotate secrets immediately. Stay updated.

Hackers target Rockstar Games via Snowflake. While Rockstar calls the data "non-substantial," could internal budgets and future launch dates be at risk?

A massive supply-chain attack hit the European Commission via a compromised Trivy update. 340GB of data was leaked by ShinyHunters. Rotate your AWS keys!

The Scattered Lapsus$ Hunters "supergroup" is paying $1,000 per successful vishing call. Discover how they use female recruits to bypass corporate IT security.
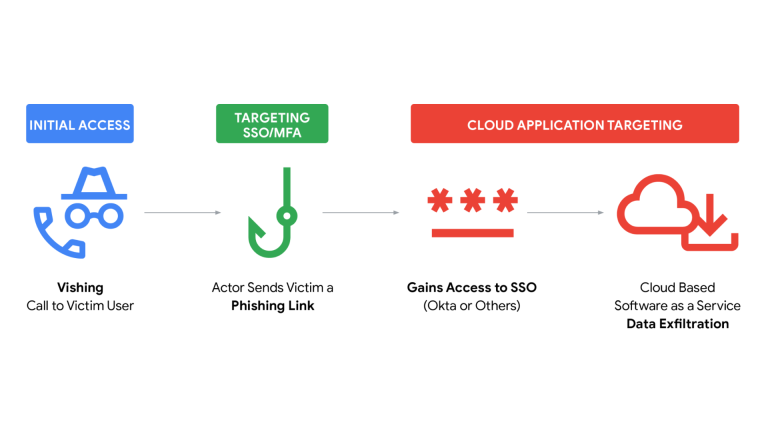
Mandiant warns of vishing rings like ShinyHunters impersonating IT support to bypass MFA and steal corporate cloud data. Verify your callers.

Trustwave confirmed the "Trinity of Chaos" alliance (Scattered Spider, LAPSUS$, ShinyHunters) launched a federated EaaS model for high-profile extortion, driven by performance, theatrics, and insider recruitment.

The "Trinity of Chaos" alliance (Lapsus$, Scattered Spider, ShinyHunters) launched a DLS, listing 39 firms, including Google and Cisco, and claiming 1.5 billion stolen records.

A new report shows LAPSUS$, Scattered Spider, and ShinyHunters have formed a collaborative alliance, sharing tactics like social engineering and MFA bypass to launch global attacks.

EclecticIQ reports on how ShinyHunters is expanding with AI-driven voice phishing, supply chain compromises, and insider recruitment, blurring lines with APTs.

Google confirms a June Salesforce breach by UNC6040 (ShinyHunters). The attack used social engineering to steal credentials, a tactic also used against Chanel and Allianz.

Allianz Life confirms a data breach impacting over 1.4 million individuals after attackers used social engineering to access a cloud-based CRM system. ShinyHunters is suspected.