Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
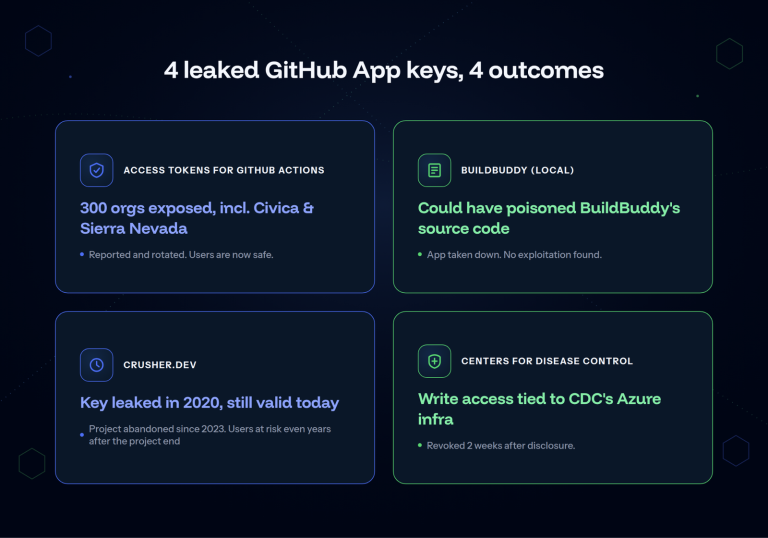
Leaked GitHub App Private Keys Expose Critical Infrastructure Diagram showing leaked GitHub App private keys and how GitHub App private keys compromise repositories
  • Data Leak

Leaked GitHub App Private Keys Expose Critical Infrastructure

Do Son September 23, 2026 0

GitGuardian discovered 474 leaked GitHub App private keys still active. Learn how exposed GitHub App private keys threaten organizations like the CDC.
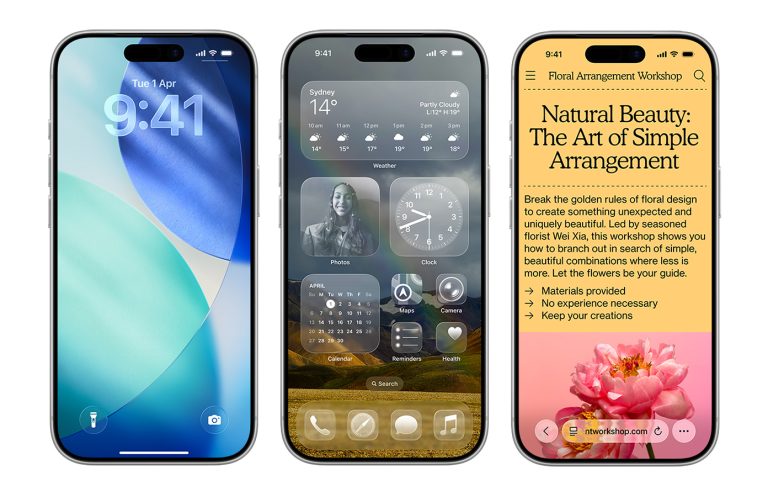
Apple Introduces the iOS 27 Auto Lock Feature iOS 27 Auto Lock feature securing a snatched iPhone and protecting user data
  • Technology

Apple Introduces the iOS 27 Auto Lock Feature

Do Son September 23, 2026 0

Discover how the new iOS 27 Auto Lock feature protects your iPhone. This advanced anti-theft security automatically locks snatched devices to secure data.
Trump Mandates Super Intelligence to Replace AI Terminology Donald Trump announcing super intelligence mandate at a press conference
  • Technology

Trump Mandates Super Intelligence to Replace AI Terminology

Do Son September 23, 2026 0

Discover the new Trump super intelligence mandate. The US government will replace the term artificial intelligence, sparking debate across the tech industry.
MemTensor MemOS Compromise Exposes AI Developer Secrets Diagram showing the MemTensor MemOS compromise details and how the MemTensor MemOS compromise affects developers
  • Malware

MemTensor MemOS Compromise Exposes AI Developer Secrets

Do Son September 23, 2026 0

Discover the critical MemTensor MemOS compromise details. This MemTensor MemOS compromise targets AI developers via malicious npm and PyPI packages.
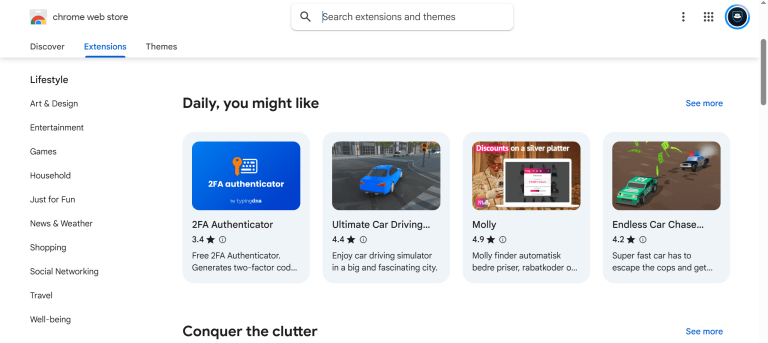
Chrome Extension Popups Freeze for macOS Users Chrome extension popup freeze bug on macOS delaying 1Password and other extension windows
  • Technology

Chrome Extension Popups Freeze for macOS Users

Do Son September 23, 2026 0

A Chrome extension popup freeze bug on macOS delays 1Password and other extensions by minutes. Google has flagged it high priority but has no fix yet.
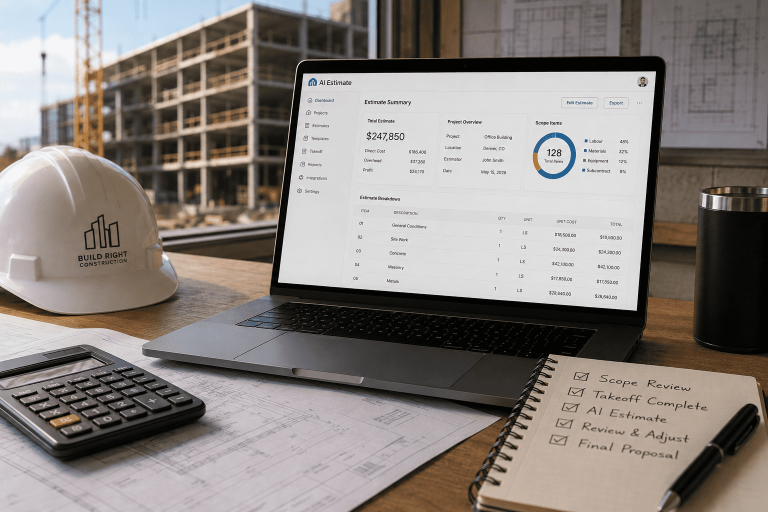
How Contractors Can Choose AI Estimating Software Without Getting Distracted By Hype d
  • Technique

How Contractors Can Choose AI Estimating Software Without Getting Distracted By Hype

Do Son September 23, 2026 0

Learn how contractors can compare AI estimating software based on workflow fit, scope clarity, pricing control, proposal quality, and real ROI.
Android May Let You Unlock a Forgotten PIN With Google Android 17 Unlock with Google Account feature recovering a forgotten PIN without a factory reset
  • Android

Android May Let You Unlock a Forgotten PIN With Google

Do Son September 23, 2026 0

Android 17 QPR2 Beta 5 code hints at an Unlock with Google Account feature to recover a forgotten PIN without a factory reset. Here is how it may work.
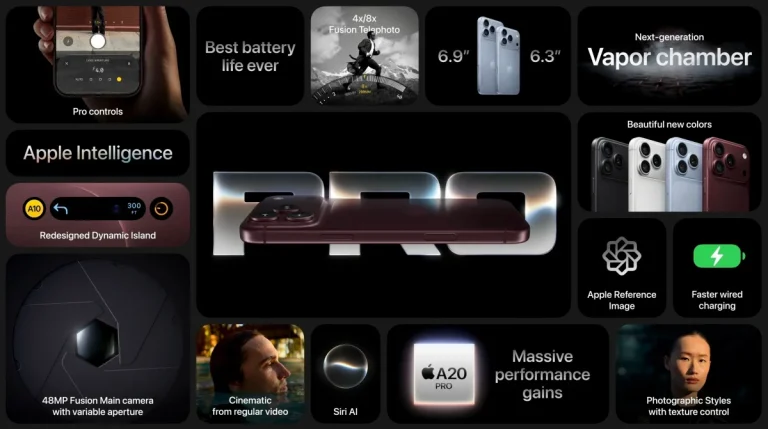
iPhone 18 Pro Face ID Failures Trigger System Restarts iPhone 18 Pro Max Face ID error screen and system crash illustration
  • Technology

iPhone 18 Pro Face ID Failures Trigger System Restarts

Do Son September 23, 2026 0

Discover why the iPhone 18 Pro Face ID fails and causes system restarts. Learn how to avoid this iOS 27 bug when accessing password-protected apps.
SideCopy APT Campaign Targets Academic Institutions CoreRAT malware decoy PDF used in Core Werewolf phishing attack on Russian defense targets
  • Cybercriminals

SideCopy APT Campaign Targets Academic Institutions

Do Son September 23, 2026 0

The SideCopy APT campaign deploys custom RATs. Learn how the SideCopy APT campaign malware exploits mshta to target academic and government networks.
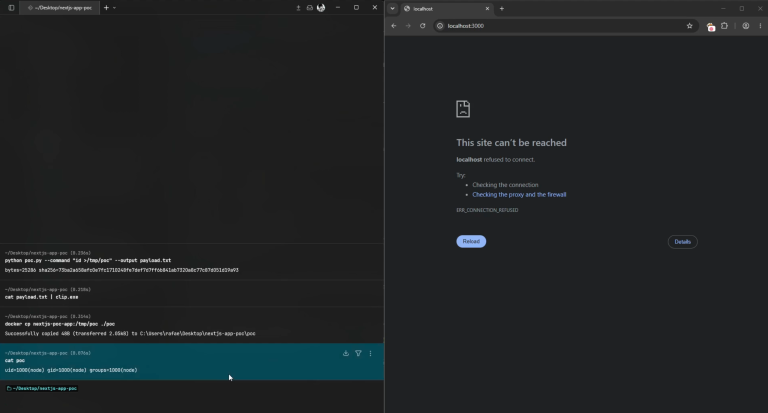
Critical Next.js RCE Vulnerability Fixed in Version 16.3.6 Diagram illustrating the critical Next.js RCE vulnerability in image generation
  • Vulnerability Report

Critical Next.js RCE Vulnerability Fixed in Version 16.3.6

Do Son September 23, 2026 0

Vercel fixed a critical Next.js RCE vulnerability in image generation. Update to patch this Next.js RCE vulnerability and secure your apps.
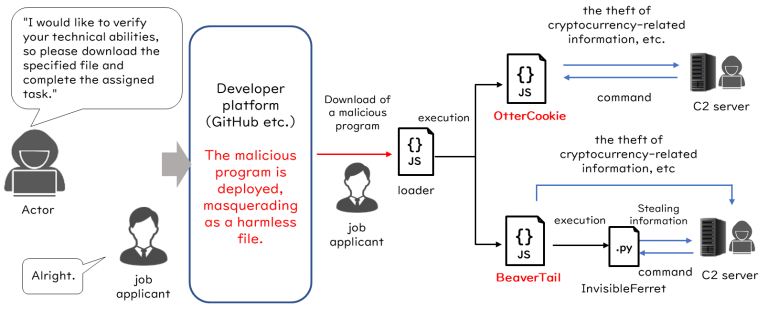
The WaterPlum Cyber Actor Group Targets Global IT Professionals A diagram detailing the North Korean WaterPlum cyber actor group infection chain
  • Cybercriminals

The WaterPlum Cyber Actor Group Targets Global IT Professionals

Do Son September 23, 2026 0

Discover how the North Korean WaterPlum cyber actor group uses fake job interviews to steal crypto and infiltrate networks globally.
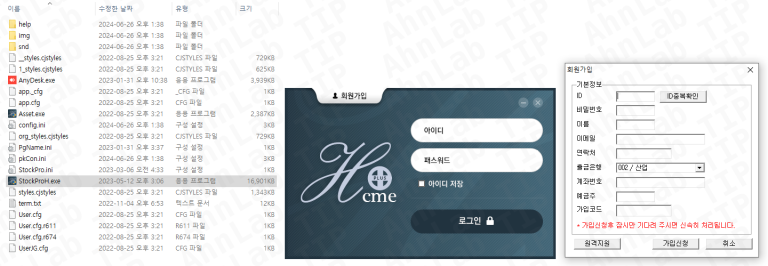
KRSID Ransomware Targets Private HTS Investment Platforms KRSID ransomware targeting private HTS malware victims
  • Malware

KRSID Ransomware Targets Private HTS Investment Platforms

Do Son September 23, 2026 0

Fraudulent investment groups are using the UBP Asset private HTS malware to distribute KRSID ransomware. Learn how to protect your trading accounts today.
Critical IBM FTM Vulnerabilities Expose Financial Systems to Attack Diagram showing critical IBM FTM vulnerabilities and authentication bypass risks
  • Vulnerability Report

Critical IBM FTM Vulnerabilities Expose Financial Systems to Attack

Do Son September 23, 2026 0

IBM patched critical IBM FTM vulnerabilities in Financial Transaction Manager. Learn how these IBM FTM vulnerabilities impact systems and update immediately.
Critical HPE ALE Vulnerabilities Allow Complete Server Takeover Diagram illustrating critical HPE ALE vulnerabilities and system takeover risks
  • Vulnerability Report

Critical HPE ALE Vulnerabilities Allow Complete Server Takeover

Do Son September 23, 2026 0

Critical HPE ALE vulnerabilities threaten enterprise networks. Update HPE ALE vulnerabilities now to prevent unauthorized access and remote code execution.
Critical IBM DataStage Vulnerabilities Threaten Cloud Environments Diagram illustrating the impact of IBM DataStage vulnerabilities
  • Vulnerability Report

Critical IBM DataStage Vulnerabilities Threaten Cloud Environments

Do Son September 23, 2026 0

IBM DataStage vulnerabilities expose cloud environments to RCE and DoS. Upgrade Cloud Pak for Data to version 5.4 patch 7 immediately.
Chrome 154 Release Patches 108 Security Vulnerabilities Graphic highlighting the Chrome 154 security fixes and 108 security vulnerabilities patched
  • Vulnerability Report

Chrome 154 Release Patches 108 Security Vulnerabilities

Do Son September 23, 2026 0

Google Chrome 154 patches 108 security vulnerabilities, including critical memory corruption flaws. Update your browser immediately to stay secure.
SolarWinds Observability Vulnerabilities Enable Remote Code Execution Diagram detailing SolarWinds Observability vulnerabilities and CVE-2026-28324 execution flow
  • Vulnerability Report

SolarWinds Observability Vulnerabilities Enable Remote Code Execution

Do Son September 23, 2026 0

SolarWinds Observability vulnerabilities allow RCE via CVE-2026-28324. Update to version 2026.2.3 to secure your monitoring infrastructure today.
D-Link DAP-1360 Vulnerability Details and PoC Disclosed Diagram of the D-Link DAP-1360 vulnerability CVE-2026-95675 execution flow
  • Vulnerability Report

D-Link DAP-1360 Vulnerability Details and PoC Disclosed

Do Son September 23, 2026 0

Technical details and a PoC for the D-Link DAP-1360 vulnerability (CVE-2026-95675) are public. Learn how this unauthenticated flaw impacts legacy routers.
NVIDIA Patches Critical Vulnerabilities in Infrastructure Controller Diagram showing critical NVIDIA Infrastructure Controller vulnerabilities and CVE-2026-65113
  • Vulnerability Report

NVIDIA Patches Critical Vulnerabilities in Infrastructure Controller

Do Son September 22, 2026 0

NVIDIA patched critical NVIDIA Infrastructure Controller vulnerabilities across Linux builds. Learn how CVE-2026-65113 impacts systems and update now.
Microsoft Disrupts EvilTokens Cybercrime Platform Disrupting EvilTokens cybercrime platform infrastructure and the EvilTokens cybercrime platform portal
  • Cybercriminals

Microsoft Disrupts EvilTokens Cybercrime Platform

Do Son September 22, 2026 0

Microsoft led a coalition disrupting EvilTokens cybercrime platform. Learn how the EvilTokens cybercrime platform used AI and device code phishing.
Exploited BIG-IP APM Vulnerability Allows Remote Code Execution Diagram detailing the exploited BIG-IP APM vulnerability and CVE-2026-94127 flow
  • Vulnerability Report

Exploited BIG-IP APM Vulnerability Allows Remote Code Execution

Do Son September 22, 2026 0

An exploited BIG-IP APM vulnerability tracked as CVE-2026-94127 allows RCE attacks. Secure your BIG-IP APM vulnerability deployments with new F5 hotfixes.
Critical ManageEngine ADSelfService Plus Vulnerability Fixed Diagram of the ManageEngine ADSelfService Plus vulnerability affecting the GINA client
  • Vulnerability Report

Critical ManageEngine ADSelfService Plus Vulnerability Fixed

Do Son September 22, 2026 0

A critical ManageEngine ADSelfService Plus vulnerability (CVE-2026-74849) allows system compromise. Update to build 7001 to secure your endpoints.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121491CVSS 9.0
    The Fiber Admin WordPress plugin before 4.0.1 does not validate or escape a request header before writing it...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119516CVSS 9.8
    Deserialization of Untrusted Data vulnerability in Mamunur Rashid Radius Booking — Booking Calendar for Appointments & Services radius-booking...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124059CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this vulnerability is the function setWiFiWdsAddConfig...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.