Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Exploited Check Point VPN Vulnerability Hit in the Wild Diagram of the exploited Check Point VPN vulnerability affecting gateways
  • Vulnerability Report

Exploited Check Point VPN Vulnerability Hit in the Wild

Do Son September 22, 2026 0

An exploited Check Point VPN vulnerability allows remote code execution. Patch this Check Point VPN vulnerability now to block active in-the-wild attacks.
CVE-2026-87902: Critical WordPress RCE Flaw Fixed in Version 7.1.2 Diagram detailing the critical WordPress RCE vulnerability tracked as CVE-2026-87902
  • Vulnerability Report

CVE-2026-87902: Critical WordPress RCE Flaw Fixed in Version 7.1.2

Do Son September 22, 2026 0

WordPress 7.1.2 patches a critical WordPress RCE vulnerability (CVE-2026-87902). Update your site to prevent conditional remote code execution.
Wild Exploitation Of CVE-2026-93616 Check Point Management Server Lets Attackers Execute Arbitrary Scripts hacked-2
  • Vulnerability Report

Wild Exploitation Of CVE-2026-93616 Check Point Management Server Lets Attackers Execute Arbitrary Scripts

Do Son September 22, 2026 0

A critical exploited Check Point Management vulnerability (CVE-2026-93616) allows attackers to execute arbitrary scripts. Secure your servers now.
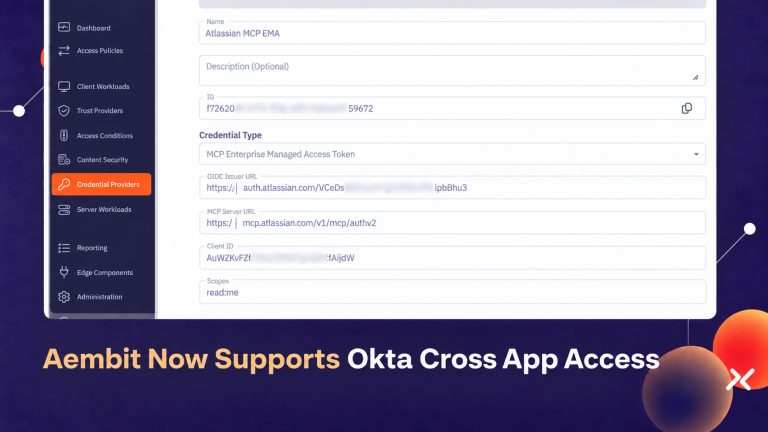
Aembit Launches Support for Okta Cross App Access, Extending Enterprise Identity Controls to AI Agents xaa_1790023632b9zu5nUa3S
  • Press Release

Aembit Launches Support for Okta Cross App Access, Extending Enterprise Identity Controls to AI Agents

cybernewswire September 22, 2026 0
Silver Spring, Maryland, USA, 22nd September 2026, CyberNewswire
Read More Read more about Aembit Launches Support for Okta Cross App Access, Extending Enterprise Identity Controls to AI Agents
Windows File History Bug Disrupts Data Backups Windows File History bug error screen and backup failure warning
  • Windows

Windows File History Bug Disrupts Data Backups

Do Son September 22, 2026 0

Discover how the recent September update caused a critical Windows File History bug. Learn about backup failures and how to protect your essential data now.
Amazon Blocks Meta Muse AI Assistant Amazon blocks Meta Muse AI shopping cart warning screen
  • Technology

Amazon Blocks Meta Muse AI Assistant

Do Son September 22, 2026 0

Discover why Amazon blocks Meta Muse AI from automated shopping. Learn about the security concerns, negotiation breakdowns, and advertising revenue impacts.
MovieReaper Malware Spreads via Compromised Torrents The MovieReaper malware torrent attacks infection chain
  • Malware

MovieReaper Malware Spreads via Compromised Torrents

Do Son September 22, 2026 0

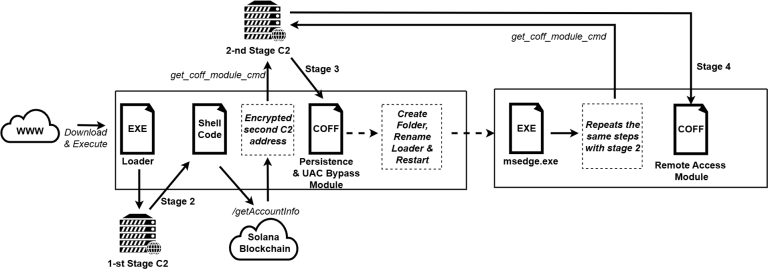
Learn how the MovieReaper malware compromises torrents. Experts warn that MovieReaper malware torrent attacks use Solana blockchain for command and control.
Actively Exploited Veeam Agent Vulnerability PoC Disclosed Diagram explaining the actively exploited Veeam Agent vulnerability and CVE-2026-32996
  • Vulnerability Report

Actively Exploited Veeam Agent Vulnerability PoC Disclosed

Do Son September 22, 2026 0

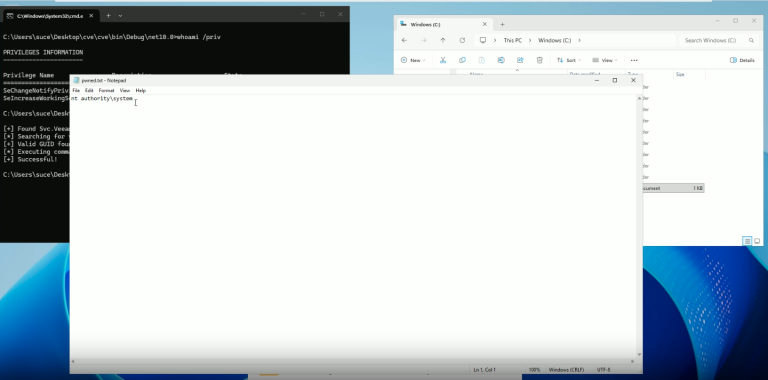
A critical exploited Veeam Agent vulnerability (CVE-2026-32996) is under active attack. Public PoC exploit code has been disclosed. Update systems now.

Operation RapidRust APT36 Campaign Targets Governments Half-click exploits chain showing webmail zero-days used by TA488 and TA458 against Zimbra, SOGo and Roundcube mailservers
  • Cybercriminals

Operation RapidRust APT36 Campaign Targets Governments

Do Son September 22, 2026 0

Explore how the Operation RapidRust APT36 malware campaign by Zscaler ThreatLabz exposes new tools like RUSTYSHADE and RUSTYMOVE targeting governments.
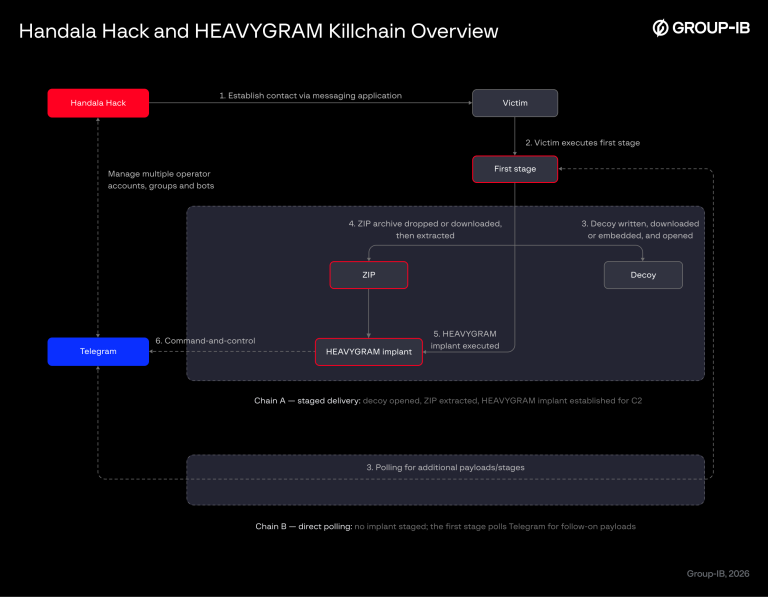
HEAVYGRAM Malware Abuses Telegram for Cyberespionage Diagram of Iranian HEAVYGRAM malware illustrating how HEAVYGRAM malware compromises endpoints
  • Malware

HEAVYGRAM Malware Abuses Telegram for Cyberespionage

Do Son September 22, 2026 0

Group-IB uncovered Iranian HEAVYGRAM malware campaigns. The HEAVYGRAM malware abuses Telegram channels for command execution and data theft.
Exploited VeloCloud Vulnerability CVE-2026-93952 Hits 10 Network diagram of the exploited VeloCloud vulnerability tracked as CVE-2026-93952
  • Vulnerability Report

Exploited VeloCloud Vulnerability CVE-2026-93952 Hits 10

Do Son September 22, 2026 0

An exploited VeloCloud vulnerability with a 10.0 CVSS score hits Arista appliances. Patch the critical VeloCloud vulnerability to stop active attacks.
OpenAI Races to Counter Grok Bot and Meta’s Muse OpenAI developing personal AI agent features to counter SpaceXAI Grok Bot and Meta Muse
  • Technology

OpenAI Races to Counter Grok Bot and Meta’s Muse

Do Son September 22, 2026 0

OpenAI is building a personal AI agent to counter SpaceXAI's Grok Bot and Meta's Muse, hiring the OpenClaw creator to lead its Codex Bot effort.
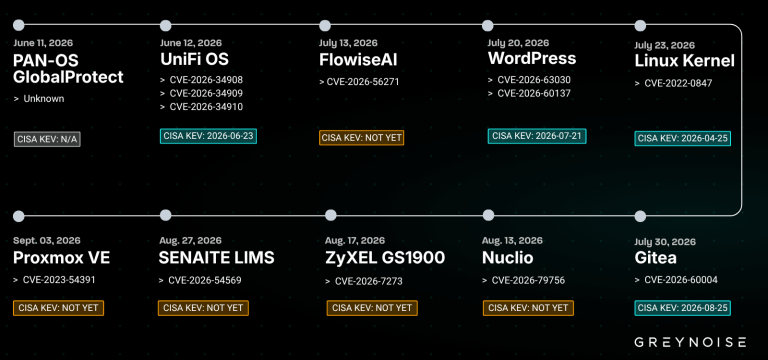
Kapibala WordPress Exploitation Attacks Hit Governments Diagram showing Kapibala WordPress exploitation attacks and Kapibala WordPress exploitation timeline
  • Cybercriminals

Kapibala WordPress Exploitation Attacks Hit Governments

Do Son September 22, 2026 0

New Kapibala WordPress exploitation attacks steal records. GreyNoise warns that Kapibala WordPress exploitation hits governments.
X Content Farm Lawsuit Targets Engagement Fraud X content farm lawsuit and creator revenue fraud investigation
  • Technology

X Content Farm Lawsuit Targets Engagement Fraud

Do Son September 22, 2026 0

Discover the details of the X content farm lawsuit. Elon Musk's social network takes legal action to recover $278,000 lost to creator revenue fraud.
DPC Imposes Massive GDPR Penalty on Google Google location data fine announcement building
  • Technology

DPC Imposes Massive GDPR Penalty on Google

Do Son September 22, 2026 0

Discover why the DPC hit Google with a 403 million euro location data fine for GDPR violations, marking a major turning point for tech privacy standards.
D-Link DIR-822A Vulnerabilities Details and PoC Disclosed Diagram of critical D-Link DIR-822A vulnerabilities and D-Link DIR-822A vulnerabilities buffer overflow flaws
  • Vulnerability Report

D-Link DIR-822A Vulnerabilities Details and PoC Disclosed

Do Son September 22, 2026 0

Public PoC exploit details emerge for critical D-Link DIR-822A vulnerabilities. Learn how these D-Link DIR-822A vulnerabilities impact unpatched devices.
Pega Platform SAML Authentication Bypass: Critical 9.5 Flaw Patched Pega Platform SAML authentication bypass advisory showing critical and high severity SSO vulnerabilities and patch remediation
  • Vulnerability Report

Pega Platform SAML Authentication Bypass: Critical 9.5 Flaw Patched

Do Son September 22, 2026 0

Pega patched a SAML authentication bypass in Pega Platform, rated Critical 9.5 and High 7.0. No CVE, no known compromise. See affected versions and fixes.
Exploited Zyxel Switch Vulnerability Added to CISA KEV Graphic showing an exploited Zyxel switch vulnerability tracked as CVE-2026-7273
  • Vulnerability Report

Exploited Zyxel Switch Vulnerability Added to CISA KEV

Do Son September 22, 2026 0

CISA warned of an exploited Zyxel switch vulnerability in GS1900 devices. Patch the Zyxel switch vulnerability now to prevent network compromise.
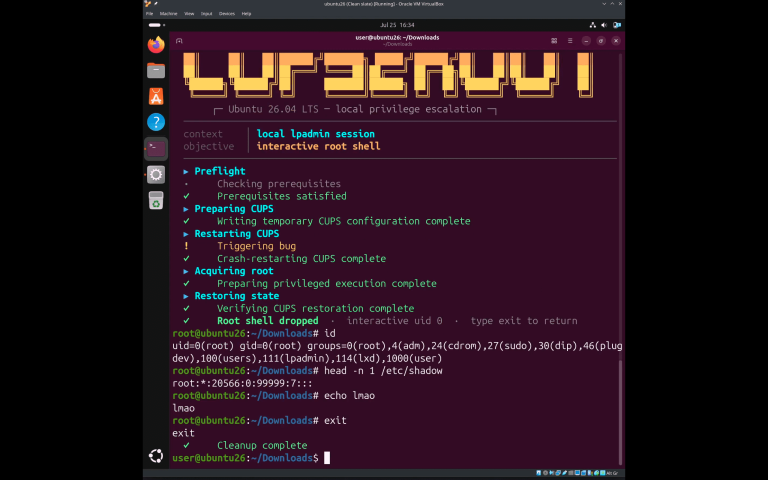
cups2root: Public PoC Exploit Escalates lpadmin to Root on CUPS cups2root CUPS privilege escalation 0-day exploit chain escalating lpadmin group to root shell on Ubuntu Linux
  • Vulnerability Report

cups2root: Public PoC Exploit Escalates lpadmin to Root on CUPS

Do Son September 22, 2026 0

A public PoC exploit, cups2root, chains a CUPS privilege escalation to take lpadmin users to root. No CVE or patch yet. See the mechanism and mitigations.
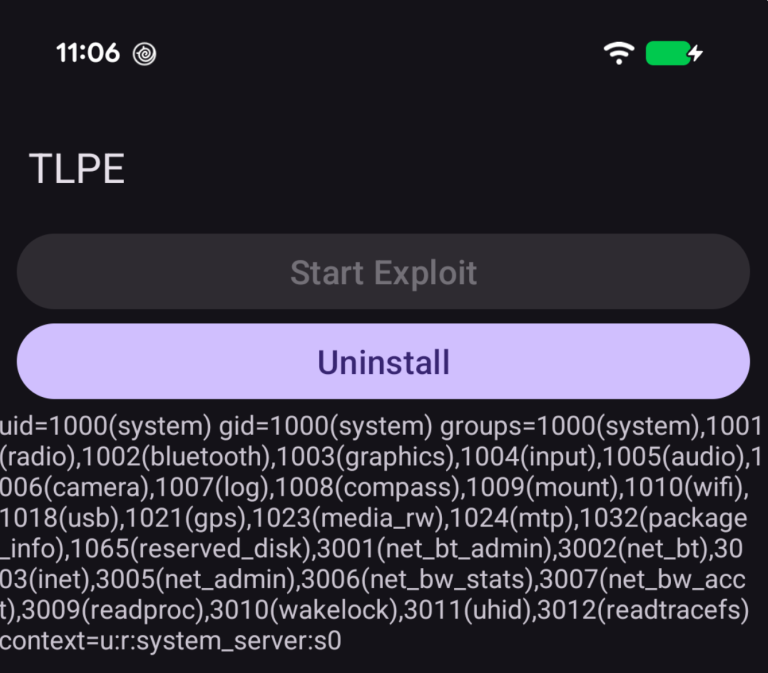
Public PoC Disclosed for Android Telecom Vulnerability CVE-2026-49881 Diagram illustrating the exploitation flow of Android Telecom Vulnerability CVE-2026-49881
  • Vulnerability Report

Public PoC Disclosed for Android Telecom Vulnerability CVE-2026-49881

Do Son September 22, 2026 0

A critical Android Telecom vulnerability (CVE-2026-49881) allows remote code execution. Read the analysis and learn how to secure your device today.
Five Network Headaches a DNS Appliance Solves in Under 30 Days AISelect_20260922_071849_Docs
  • Technique

Five Network Headaches a DNS Appliance Solves in Under 30 Days

Do Son September 22, 2026 0
If you are operating a business in the US, you will likely face several networking challenges. Some...
Read More Read more about Five Network Headaches a DNS Appliance Solves in Under 30 Days
Qualcomm and Google Unveil the Revolutionary Googlebook Snapdragon X Elite Googlebook rendering with Gemini AI
  • Technology

Qualcomm and Google Unveil the Revolutionary Googlebook

Do Son September 21, 2026 0

Discover the new Snapdragon X Elite Googlebook by Dell and HP. Experience native Android gaming, seamless cross-device synergy, and advanced Gemini AI today.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121491CVSS 9.0
    The Fiber Admin WordPress plugin before 4.0.1 does not validate or escape a request header before writing it...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119516CVSS 9.8
    Deserialization of Untrusted Data vulnerability in Mamunur Rashid Radius Booking — Booking Calendar for Appointments & Services radius-booking...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124059CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this vulnerability is the function setWiFiWdsAddConfig...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.