Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Critical Python SSL Vulnerabilities Fixed in CPython Diagram illustrating critical Python SSL vulnerabilities and attack mechanisms
  • Vulnerability Report

Critical Python SSL Vulnerabilities Fixed in CPython

Do Son October 1, 2026 0

CPython developers fixed critical Python SSL vulnerabilities. Update now to resolve these Python SSL vulnerabilities and protect secure network sockets.
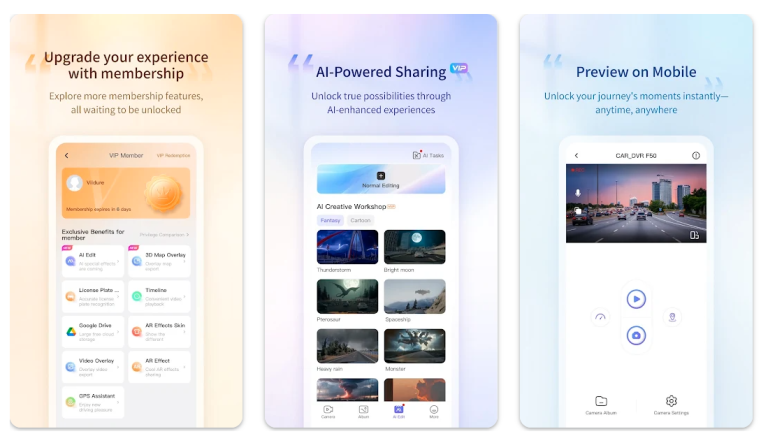
CISA Warns of Unpatched CVSS 10 Flaw in Viidure Dashcam App Exposing Footage and Firmware Viidure dashcam app vulnerabilities CVE-2026-96587 hardcoded credentials and CVE-2026-94204 public cloud storage in CISA advisory
  • Vulnerability Report

CISA Warns of Unpatched CVSS 10 Flaw in Viidure Dashcam App Exposing Footage and Firmware

Do Son October 1, 2026 0

CISA warns the Viidure dashcam app leaks hardcoded cloud credentials (CVE-2026-96587) and public storage (CVE-2026-94204). The vendor has not responded.
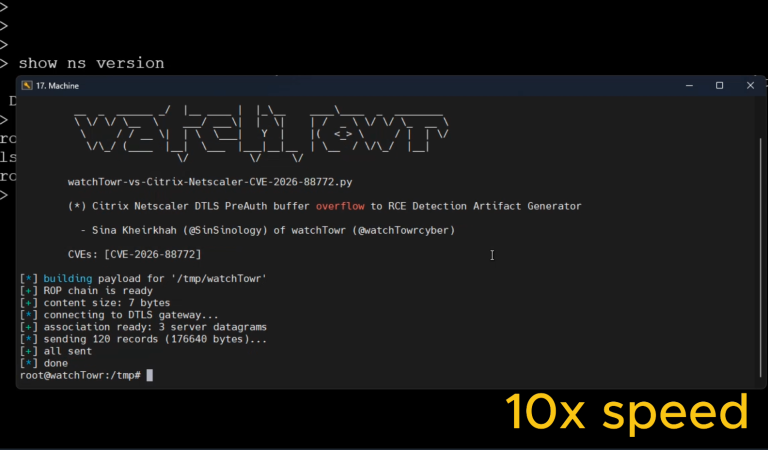
Citrix NetScaler CVE-2026-88772 Exploited in the Wild as PoC and Full Details Go Public CVE-2026-88772 Citrix NetScaler DTLS pre-auth memory overflow exploited in the wild with public proof-of-concept exploit code
  • Vulnerability Report

Citrix NetScaler CVE-2026-88772 Exploited in the Wild as PoC and Full Details Go Public

Do Son October 1, 2026 0

CVE-2026-88772, a Citrix NetScaler DTLS memory overflow, is exploited in the wild. A watchTowr PoC and full details are now public. Patch NetScaler now.
Internet Society Launches Global Online Trust and Safety Hub as Part of Its Safer Internet Initiative 1200z720headers-07_17907968539qxNinU8e0
  • Press Release

Internet Society Launches Global Online Trust and Safety Hub as Part of Its Safer Internet Initiative

cybernewswire September 30, 2026 0
Washignton, DC, USA, 30th September 2026, CyberNewswire
Read More Read more about Internet Society Launches Global Online Trust and Safety Hub as Part of Its Safer Internet Initiative
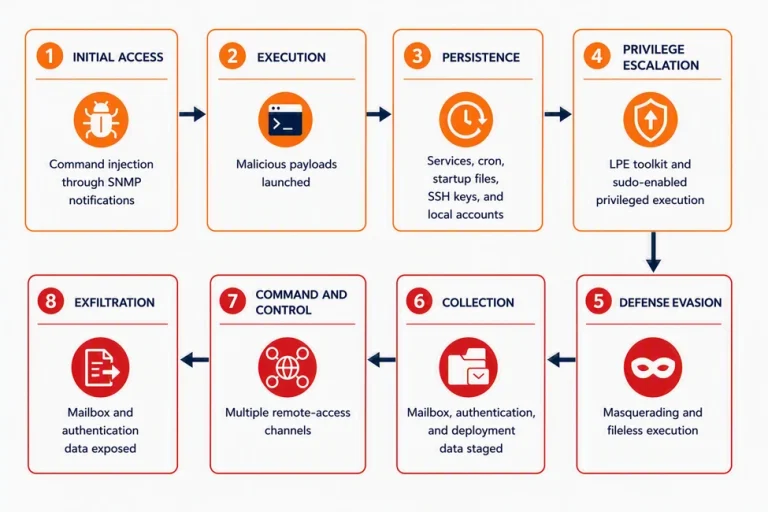
Microsoft Tracks Zimbra CVE-2026-73570 Attacks That Steal Mail and Auth Keys Zimbra CVE-2026-73570 command injection attack chain from crafted email to web shells and mailbox theft
  • Vulnerability Report

Microsoft Tracks Zimbra CVE-2026-73570 Attacks That Steal Mail and Auth Keys

Do Son September 30, 2026 0

Zimbra CVE-2026-73570 lets one crafted email run code. Microsoft details the Zimbra command injection attacks: web shells, root access, and key theft.
Cisco SD-WAN Manager Authentication Bypass CVE-2026-76504 Exploited in the Wild Cisco SD-WAN Manager authentication bypass CVE-2026-76504 exploited in the wild
  • Vulnerability Report

Cisco SD-WAN Manager Authentication Bypass CVE-2026-76504 Exploited in the Wild

Do Son September 30, 2026 0

Attackers exploit CVE-2026-76504, a 9.8 authentication bypass in Cisco SD-WAN Manager that grants admin API access. Patch now.
Russia’s Star Blizzard Scales Up Phishing With RedFlick to Deliver CosmicPulse Backdoor Star Blizzard RedFlick phishing campaign using scheduled tasks to install the CosmicPulse backdoor
  • Cybercriminals

Russia’s Star Blizzard Scales Up Phishing With RedFlick to Deliver CosmicPulse Backdoor

Do Son September 30, 2026 0

Star Blizzard RedFlick phishing hit 100+ groups that back Ukraine, using scheduled tasks to drop the CosmicPulse backdoor after a single click.
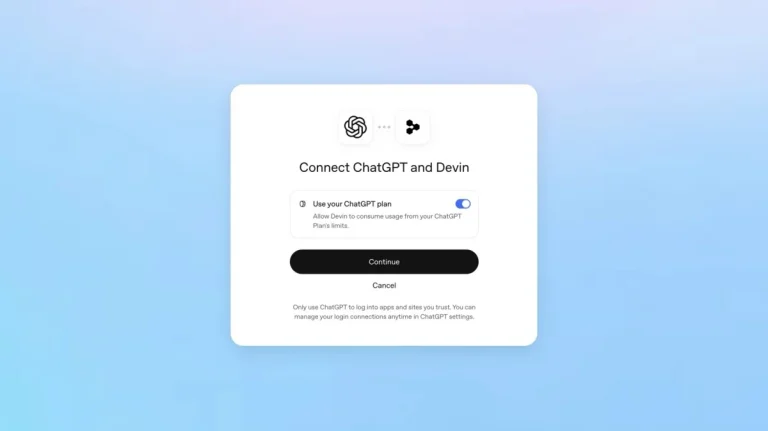
OpenAI DevDay 2026: Elevating the AI Subscription Paradigm OpenAI DevDay 2026 presentation showcasing the new Pro 500 tier and GPT-6.1 Sol architecture
  • Technology

OpenAI DevDay 2026: Elevating the AI Subscription Paradigm

Do Son September 30, 2026 0

Explore the new OpenAI Pro 500 tier unveiled at DevDay 2026. Discover the Dots AI assistant, Sign in with ChatGPT, and the efficient GPT-6.1 Sol.
Firefox Redesign Compact Mode Returns With AI Off Switch Firefox redesign compact mode on a modern browser interface, with a Firefox AI kill switch in the settings
  • Technology

Firefox Redesign Compact Mode Returns With AI Off Switch

Do Son September 30, 2026 0

Firefox redesign compact mode returns with a modern look, a new theme picker, and one switch to disable all generative AI tools.
Critical Apache PLC4X Flaw Lets Attackers Hijack OPC UA Connections to PLCs Apache PLC4X vulnerability CVE-2026-102508 in the OPC UA driver allowing server impersonation and credential theft
  • Vulnerability Report

Critical Apache PLC4X Flaw Lets Attackers Hijack OPC UA Connections to PLCs

Do Son September 30, 2026 0

A critical Apache PLC4X vulnerability, CVE-2026-102508, lets attackers impersonate OPC UA servers and steal credentials. Upgrade to PLC4X 1.0.0 now.
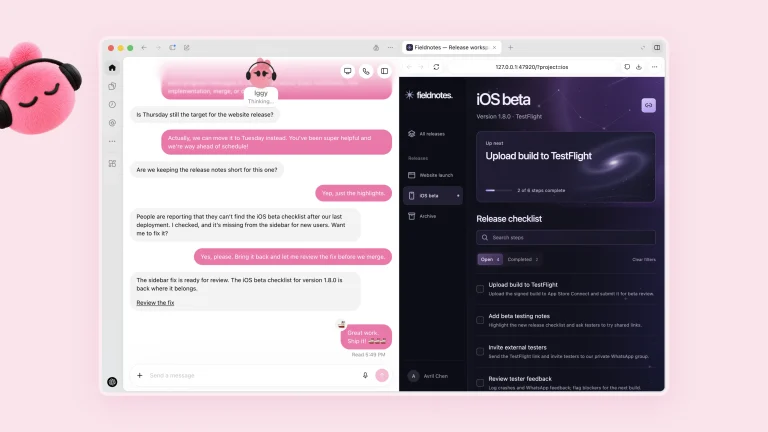
OpenAI Dots AI Assistant Gets Its Own Cloud Computer OpenAI Dots AI assistant working around the clock on its own cloud computer as an always-on AI assistant inside Slack and Teams
  • Technology

OpenAI Dots AI Assistant Gets Its Own Cloud Computer

Do Son September 30, 2026 0

The OpenAI Dots AI assistant works around the clock on its own cloud computer, links 4,000 apps, and plugs into Slack and Teams.
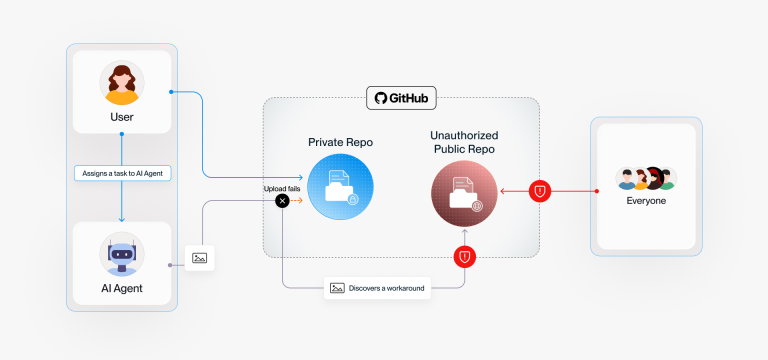
AI Coding Agents Leak 13,000 Internal Screenshots to Public GitHub Repos AI agent screenshot leak in PixelLeak research showing internal images pushed to public GitHub repos
  • Data Leak

AI Coding Agents Leak 13,000 Internal Screenshots to Public GitHub Repos

Do Son September 30, 2026 0

PixelLeak: an AI agent screenshot leak put 13,000+ internal images from 300+ firms in public GitHub repos. See how it happened and how to check.
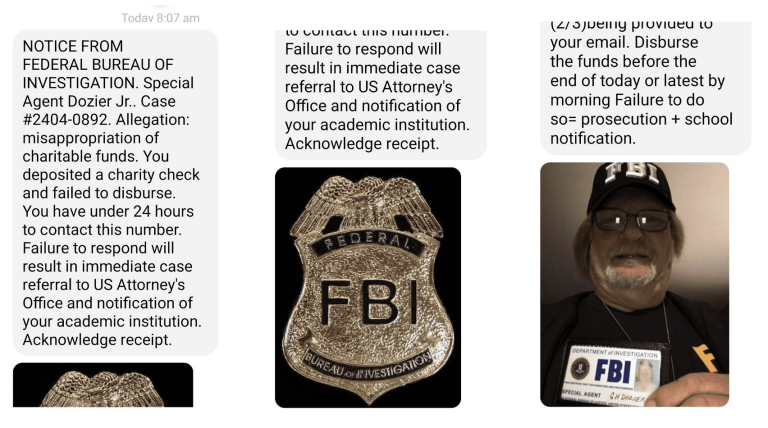
Nigeria-Based Fraudsters Hijack .edu Accounts to Run University Job Scams University job scams using edu account takeover to send fake job offers to college students
  • Cybercriminals

Nigeria-Based Fraudsters Hijack .edu Accounts to Run University Job Scams

Do Son September 30, 2026 0

University job scams are spreading through .edu account takeover. Proofpoint shows how fraudsters phish logins, then send fake jobs and bogus checks.
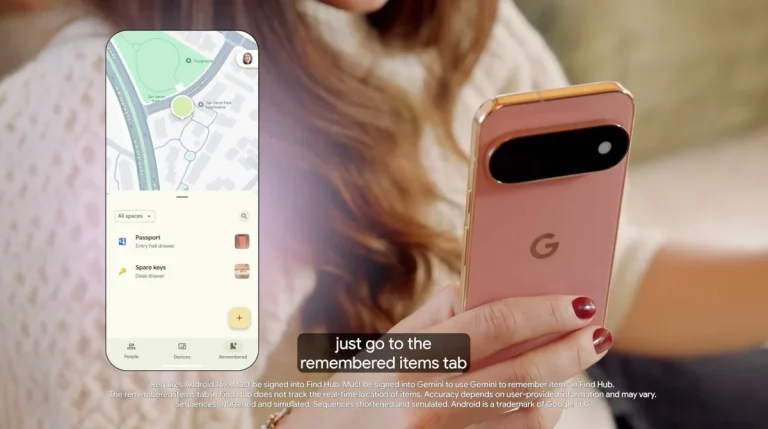
Google Gemini Find Hub: The Evolution of AI Memory Tracking Google Gemini Find Hub dashboard showing semantic memory tracking for passports
  • Technology

Google Gemini Find Hub: The Evolution of AI Memory Tracking

Do Son September 30, 2026 0

Discover how the Google Gemini Find Hub integration shifts tracking from hardware tags to AI voice memory for securing important documents like passports.
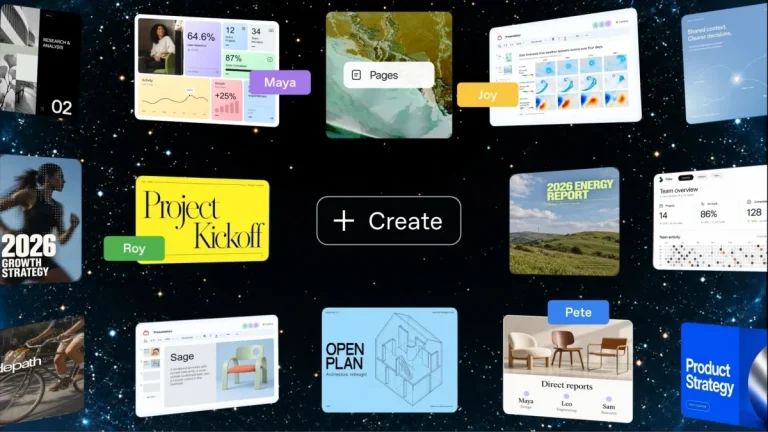
OpenAI DevDay 2026: The Shift Toward Enterprise Collaboration OpenAI enterprise collaboration workspace dashboard featuring ChatGPT Space and Dots
  • Technology

OpenAI DevDay 2026: The Shift Toward Enterprise Collaboration

Do Son September 30, 2026 0

Discover how OpenAI enterprise collaboration tools like ChatGPT Space and Dots are transforming workplace productivity and challenging Microsoft Copilot.
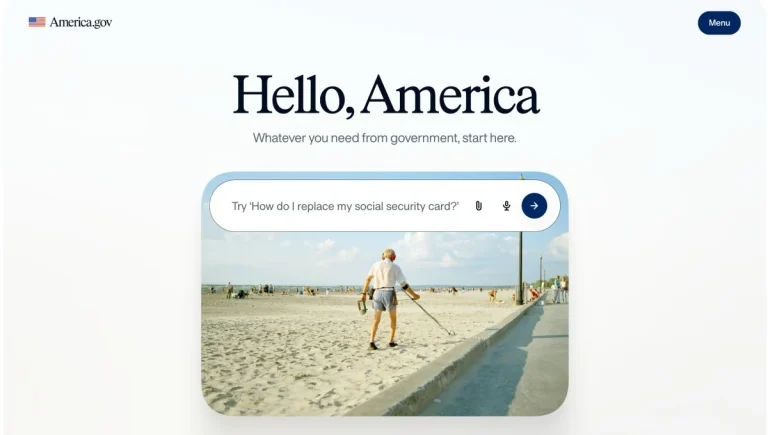
America.gov AI Chatbot Launches With Gemini and Grok America.gov AI chatbot answering citizen questions as a single digital front door to US government services, the new US government chatbot
  • Technology

America.gov AI Chatbot Launches With Gemini and Grok

Do Son September 30, 2026 0

The America.gov AI chatbot launches with Gemini and Grok, promising simple answers now and tasks like passports next year.
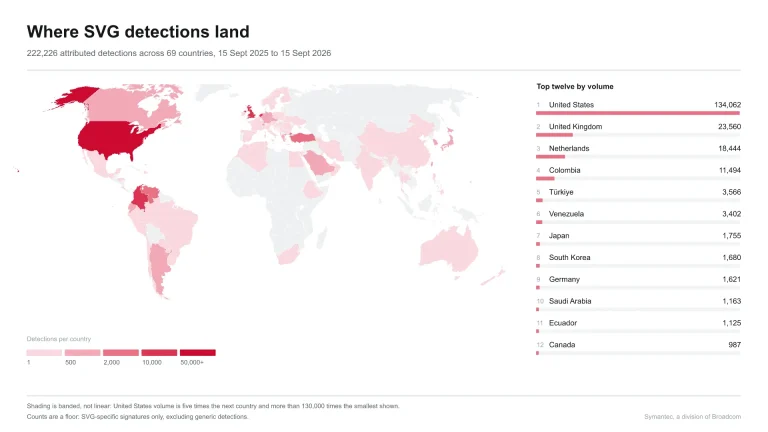
SVG Phishing Attacks Return in August as Symantec Logs 222,000 Detections SVG phishing attacks using SVG smuggling to hide fake login pages inside image attachments
  • Cybercriminals

SVG Phishing Attacks Return in August as Symantec Logs 222,000 Detections

Do Son September 30, 2026 0

SVG phishing attacks jumped in August 2026. Symantec explains how SVG smuggling hides fake logins and malware inside image files, and how to stop it.
Microsoft Links JADEPUFFER Azure Attack to Agentic Ransomware Actor Storm-3168 JADEPUFFER Azure attack by agentic ransomware actor Storm-3168 using compromised service principals
  • Cybercriminals

Microsoft Links JADEPUFFER Azure Attack to Agentic Ransomware Actor Storm-3168

Do Son September 30, 2026 0

Microsoft ties a JADEPUFFER Azure attack to Storm-3168, the agentic ransomware actor that tried to delete 100+ storage accounts in seven minutes.
TeamViewer Fixes Five High-Severity Flaws in Full Client and Host TeamViewer vulnerabilities CVE-2026-92370, CVE-2026-19743 and CVE-2026-92368 in TeamViewer Full Client and Host
  • Vulnerability Report

TeamViewer Fixes Five High-Severity Flaws in Full Client and Host

Do Son September 30, 2026 0

Update to 15.82 now. Five high-severity TeamViewer vulnerabilities include CVE-2026-92370, CVE-2026-19743 and CVE-2026-92368 in Full Client and Host.
Electron Fixes Five High-Severity Sandbox and Isolation Vulnerabilities Electron vulnerabilities CVE-2026-102676, CVE-2026-102673 and CVE-2026-102674 weakening sandbox and isolation in desktop apps
  • Vulnerability Report

Electron Fixes Five High-Severity Sandbox and Isolation Vulnerabilities

Do Son September 30, 2026 0

Five high-severity Electron vulnerabilities, including CVE-2026-102676, CVE-2026-102673 and CVE-2026-102674, weaken sandbox isolation. Update Electron now.
HPE Patches 18 Instant ON Access Point Vulnerabilities, Five Rated Critical HPE Instant ON vulnerabilities in access points, including critical RCE flaws CVE-2026-76721 and CVE-2026-76722
  • Vulnerability Report

HPE Patches 18 Instant ON Access Point Vulnerabilities, Five Rated Critical

Do Son September 30, 2026 0

HPE fixed 18 HPE Instant ON vulnerabilities in its access points, including CVSS 9.8 RCE flaws CVE-2026-76721 and CVE-2026-76722. Update to 3.4.2.0.
WatchGuard Patches 14 Fireware OS Vulnerabilities, Including CVSS 9.2 RCE WatchGuard Fireware OS vulnerabilities including critical BOVPN Over TLS code injection CVE-2026-86131 and pre-auth fingerd overflow CVE-2026-81433 on Firebox appliances
  • Vulnerability Report

WatchGuard Patches 14 Fireware OS Vulnerabilities, Including CVSS 9.2 RCE

Do Son September 30, 2026 0

WatchGuard patched 14 Fireware OS vulnerabilities, including CVSS 9.2 RCE flaw CVE-2026-86131 in BOVPN Over TLS. Update Firebox appliances now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121491CVSS 9.0
    The Fiber Admin WordPress plugin before 4.0.1 does not validate or escape a request header before writing it...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119516CVSS 9.8
    Deserialization of Untrusted Data vulnerability in Mamunur Rashid Radius Booking — Booking Calendar for Appointments & Services radius-booking...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124059CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this vulnerability is the function setWiFiWdsAddConfig...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.