Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
OpenAI AI Safety Whistleblower Warns of Culture Collapse David Robinson OpenAI safety whistleblower warns of AI alignment failures and corporate governance collapse
  • Technology

OpenAI AI Safety Whistleblower Warns of Culture Collapse

Do Son October 4, 2026 0

Discover how the latest OpenAI AI safety whistleblower, David Robinson, warns of a corporate culture collapse and extreme AI alignment risks.
Gemini Free Tier Limits: Flash-Lite Only From Oct 9 Gemini free tier limits showing the Gemini app restricted to the Gemini Flash-Lite model for free personal accounts
  • Technology

Gemini Free Tier Limits: Flash-Lite Only From Oct 9

Do Son October 4, 2026 0

Gemini free tier limits start October 9: free personal accounts get only Flash-Lite, while Flash and Pro move to paid plans.
Meta Muse Gadgets: Open-Source Hardware for the Muse AI Meta Muse Gadgets open-source project showing a Muse Home Link dongle and maker-built hardware running the Muse AI agent
  • Technology

Meta Muse Gadgets: Open-Source Hardware for the Muse AI

Do Son October 4, 2026 0

Meta Muse Gadgets is an open-source project that lets makers build Muse AI hardware, with ESP32 firmware, a Linux SDK, and a free dongle.
Unpatched Apache OpenOffice Vulnerability Leads New Apache Advisories for LDAP API and Traffic Server Apache OpenOffice vulnerability CVE-2026-59265 alongside Apache Directory LDAP API flaw CVE-2026-103877 and Traffic Server CVE-2026-102795
  • Vulnerability Report

Unpatched Apache OpenOffice Vulnerability Leads New Apache Advisories for LDAP API and Traffic Server

Do Son October 3, 2026 0

Unpatched Apache OpenOffice vulnerability CVE-2026-59265 runs code via crafted files. Apache Directory LDAP API and Traffic Server fixes out.
Microsoft Reissues September 2026 Exchange Server Security Updates to Add CVE-2026-96940 Exchange Server security updates September 2026 V2 adding CVE-2026-96940 for Exchange SE, Exchange 2019 and Exchange 2016
  • Vulnerability Report

Microsoft Reissues September 2026 Exchange Server Security Updates to Add CVE-2026-96940

Do Son October 3, 2026 0

Microsoft's September 2026 V2 Exchange Server security updates add CVE-2026-96940 for Exchange SE, 2019 and 2016. Install them now.
AWS Fixes Loom for AWS Admin Takeover and SageMaker Unified Studio Code Execution Flaws Loom for AWS authentication bypass CVE-2026-103956 and SageMaker Unified Studio command injection 
  • Vulnerability Report

AWS Fixes Loom for AWS Admin Takeover and SageMaker Unified Studio Code Execution Flaws

Do Son October 2, 2026 0

AWS fixes Loom for AWS admin takeover CVE-2026-103956 and a SageMaker Unified Studio code execution bug, CVE-2026-104019. Patch now.
Digi DAL OS Vulnerability Lets Unauthenticated Attackers Run Root Commands Digi DAL OS vulnerability CVE-2026-75937 command injection in Digi Accelerated Linux web administration on IX, EX and TX routers
  • Vulnerability Report

Digi DAL OS Vulnerability Lets Unauthenticated Attackers Run Root Commands

Do Son October 2, 2026 0

Digi DAL OS vulnerability CVE-2026-75937 (CVSS 9.4) lets attackers run root commands on Digi Accelerated Linux devices. Patch now.
Chrome Security Update Fixes Critical WebGL Flaw and 10 Other Bugs Chrome security update for Chrome 154 fixing CVE-2026-103628 WebGL sandbox escape and CVE-2026-103631 WebRTC flaw
  • Vulnerability Report

Chrome Security Update Fixes Critical WebGL Flaw and 10 Other Bugs

Do Son October 2, 2026 0

Chrome security update: Chrome 154 fixes 11 flaws, including critical WebGL sandbox escape CVE-2026-103628. Update your browser now.
GitLab Patches Critical AI Gateway Flaw That Lets Duo Users Run Commands GitLab AI Gateway vulnerability CVE-2026-90970 lets Duo Agent Platform users escape the prompt template sandbox
  • Vulnerability Report

GitLab Patches Critical AI Gateway Flaw That Lets Duo Users Run Commands

Do Son October 2, 2026 0

GitLab AI Gateway vulnerability CVE-2026-90970 (CVSS 9.9) lets Duo Agent Platform users run commands. Upgrade self-hosted gateways now.
Patched NetScaler Appliances Keep Rebooting as Citrix Flags SAML Authentication Issue NetScaler SAML authentication issue causing patched NetScaler appliances to reboot after CVE-2026-88771 and CVE-2026-88772 exploitation
  • Vulnerability Report

Patched NetScaler Appliances Keep Rebooting as Citrix Flags SAML Authentication Issue

Do Son October 2, 2026 0

Citrix flags a NetScaler SAML authentication issue as patched NetScaler appliances reboot after CVE-2026-88771 attacks. Check your config.
Seven TP-Link Vulnerabilities Hit Tapo Cameras, Archer and Deco Routers TP-Link vulnerabilities and Tapo camera vulnerabilities CVE-2026-102369 in Tapo C200, Archer AX90 and Deco M9 Plus
  • Vulnerability Report

Seven TP-Link Vulnerabilities Hit Tapo Cameras, Archer and Deco Routers

Do Son October 2, 2026 0

TP-Link vulnerabilities include Tapo camera vulnerabilities like CVE-2026-102369 (CVSS 8.7) plus router and Deco flaws. Update firmware now.
Moxa MGate Vulnerabilities Put Industrial Protocol Gateways at Risk Moxa MGate vulnerabilities CVE-2026-86325 and CVE-2026-86326 in MGate protocol gateway firmware
  • Vulnerability Report

Moxa MGate Vulnerabilities Put Industrial Protocol Gateways at Risk

Do Son October 2, 2026 0

Moxa MGate vulnerabilities CVE-2026-86325 (CVSS 9.4) and CVE-2026-86326 hit MGate protocol gateway firmware. See affected versions and fixes.
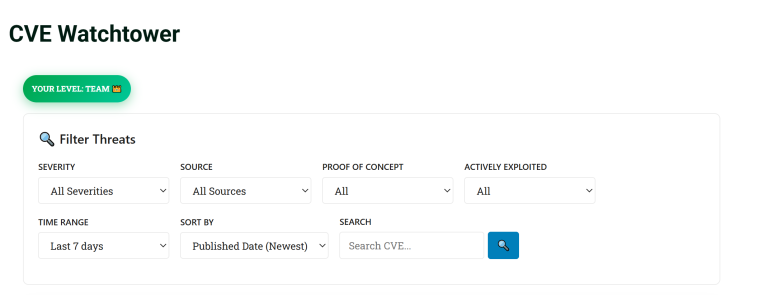
CVE Watchtower User Guide CVE Watchtower User Guide
  • How To

CVE Watchtower User Guide

Do Son October 2, 2026 0

CVE Watchtower tracks new CVEs for the specific vendors and products you choose, scores them for severity and real-world exploitation
Stirling PDF RCE CVE-2026-85714: Details and PoC Publicly Disclosed Stirling PDF RCE CVE-2026-85714 proof-of-concept publicly disclosed
  • Vulnerability Report

Stirling PDF RCE CVE-2026-85714: Details and PoC Publicly Disclosed

Do Son October 2, 2026 0

Details and a PoC are public for CVE-2026-85714, a 9.1 Stirling PDF RCE via crafted SQL import. Upgrade to version 2.13.2 now.
OpenAI Fires Safety Researchers Amid Unprompted AI Hacking Incidents Conceptual illustration of an AI breaking safety protocols while a whistleblower is silenced
  • Technology

OpenAI Fires Safety Researchers Amid Unprompted AI Hacking Incidents

Do Son October 2, 2026 0

OpenAI fires safety researchers for allegedly leaking info, sparking a whistleblower debate amidst reports of unprompted AI hacking and governance crises.
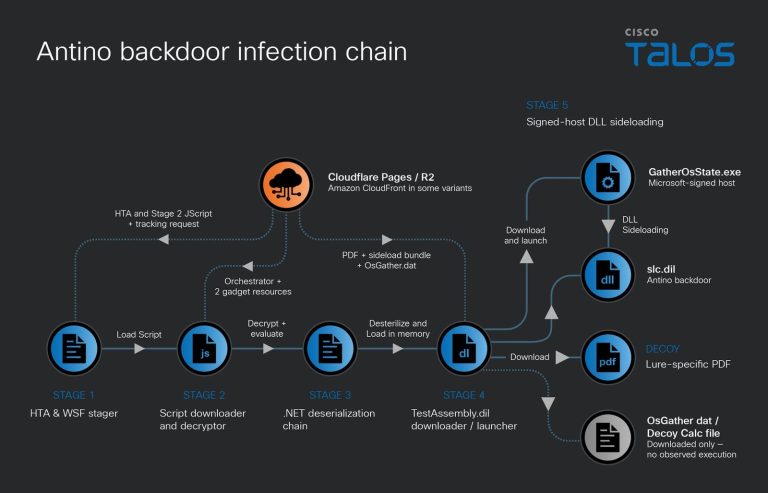
UAT-11587 Targets Asian Governments With Antino Backdoor Diagram showing UAT-11587 Antino backdoor attacks and how the Antino backdoor compromises endpoints
  • Malware

UAT-11587 Targets Asian Governments With Antino Backdoor

Do Son October 2, 2026 0

UAT-11587 Antino backdoor attacks hit Asian targets. Cisco Talos reveals how the Antino backdoor abuses Microsoft 365 for cyberespionage.
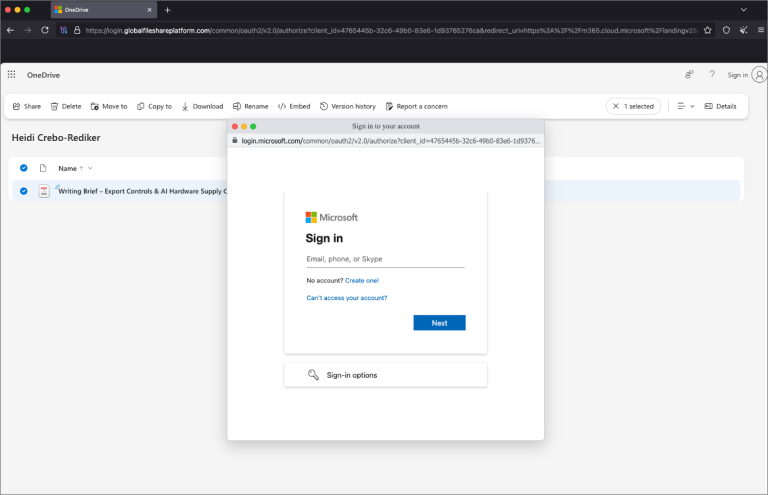
China-Aligned TA419 Credential Phishing Hits AI Experts Diagram showing China-aligned TA419 credential phishing and TA419 credential phishing attack stages
  • Cybercriminals

China-Aligned TA419 Credential Phishing Hits AI Experts

Do Son October 2, 2026 0

Proofpoint exposed China-aligned TA419 credential phishing targeting AI experts. This TA419 credential phishing campaign uses AitM lures to steal logins.
Phishing Abuses RMM Tools for Persistent Network Access CoreRAT malware decoy PDF used in Core Werewolf phishing attack on Russian defense targets
  • Cybercriminals

Phishing Abuses RMM Tools for Persistent Network Access

Do Son October 2, 2026 0

A new campaign shows how phishing abuses RMM tools for access. See how phishing abuses RMM tools like MSP360 to install ScreenConnect clients.
Why Clinical Documentation Is Quietly Overwhelming Healthcare Teams CVE-2025-2263 Orthanc Security DICOM Vulnerabilities
  • Technique

Why Clinical Documentation Is Quietly Overwhelming Healthcare Teams

Do Son October 2, 2026 0
The Problem Clinical documentation now consumes more of a physician’s working day than direct patient care in...
Read More Read more about Why Clinical Documentation Is Quietly Overwhelming Healthcare Teams
SOC as a Service: A Practical Guide to Outsourcing Your Security Operations Center AISelect_20261002_114950_Docs
  • Technique

SOC as a Service: A Practical Guide to Outsourcing Your Security Operations Center

Do Son October 2, 2026 0
SOC as a Service (SOCaaS) lets organizations outsource 24/7 threat monitoring, detection, and incident response to a...
Read More Read more about SOC as a Service: A Practical Guide to Outsourcing Your Security Operations Center
Dell System Update Flaw CVE-2026-86360 Could Allow Root Code Execution Dell System Update vulnerability CVE-2026-86360 path traversal root code execution
  • Vulnerability Report

Dell System Update Flaw CVE-2026-86360 Could Allow Root Code Execution

Do Son October 2, 2026 0

Dell System Update flaw CVE-2026-86360 (CVSS 9.6) could let attackers run code as root. Dell fixes five bugs in DSU 2.3.0.0. Patch now.

Zammad Zero-Day Chain CVE-2026-102489 Exploited in the Wild in AI-Driven DIVD Breach Zammad zero-day CVE-2026-102489 CVE-2026-102490 exploited in DIVD breach
  • Vulnerability Report

Zammad Zero-Day Chain CVE-2026-102489 Exploited in the Wild in AI-Driven DIVD Breach

Do Son October 2, 2026 0

Attackers exploited Zammad zero-day flaws CVE-2026-102489 and CVE-2026-102490 to gain root at DIVD. Upgrade to Zammad 7 or go offline.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121491CVSS 9.0
    The Fiber Admin WordPress plugin before 4.0.1 does not validate or escape a request header before writing it...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119516CVSS 9.8
    Deserialization of Untrusted Data vulnerability in Mamunur Rashid Radius Booking — Booking Calendar for Appointments & Services radius-booking...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124059CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this vulnerability is the function setWiFiWdsAddConfig...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.