Massive GitHub Malware Campaign Targets Gamers and Software Pirates with Redox Stealer Malware Massive GitHub Malware Campaign Targets Gamers and Software Pirates with Redox Stealer Do Son March 3, 2025 0 Read More Read more about Massive GitHub Malware Campaign Targets Gamers and Software Pirates with Redox Stealer
Flaws in Rancher (CVE-2025-23388 & CVE-2025-23389) Expose Kubernetes Environments to Attacks Vulnerability Flaws in Rancher (CVE-2025-23388 & CVE-2025-23389) Expose Kubernetes Environments to Attacks Do Son March 3, 2025 0 Read More Read more about Flaws in Rancher (CVE-2025-23388 & CVE-2025-23389) Expose Kubernetes Environments to Attacks
Black Basta and Cactus Ransomware Groups Weaponize BackConnect Malware Malware Black Basta and Cactus Ransomware Groups Weaponize BackConnect Malware Do Son March 3, 2025 0 Read More Read more about Black Basta and Cactus Ransomware Groups Weaponize BackConnect Malware
CVE-2025-0289: Paragon Partition Manager Flaw Exploited in BYOVD Ransomware Attacks Vulnerability CVE-2025-0289: Paragon Partition Manager Flaw Exploited in BYOVD Ransomware Attacks Do Son March 3, 2025 0 Read More Read more about CVE-2025-0289: Paragon Partition Manager Flaw Exploited in BYOVD Ransomware Attacks
Qualcomm’s March 2025 Security Bulletin Addresses Critical Flaws Across Multiple Products Vulnerability Qualcomm’s March 2025 Security Bulletin Addresses Critical Flaws Across Multiple Products Do Son March 3, 2025 0 Read More Read more about Qualcomm’s March 2025 Security Bulletin Addresses Critical Flaws Across Multiple Products
Goodbye Spam: Google’s Shielded Email for Android Arrives Technology Goodbye Spam: Google’s Shielded Email for Android Arrives Do Son March 3, 2025 0 Read More Read more about Goodbye Spam: Google’s Shielded Email for Android Arrives
Android Updates: 7 Years Now? Honor Joins Google, Samsung Android Technology Android Updates: 7 Years Now? Honor Joins Google, Samsung Do Son March 3, 2025 0 Read More Read more about Android Updates: 7 Years Now? Honor Joins Google, Samsung
Meta’s AI Push: From Llama to Chatbot, Subscription Model Coming Technology Meta’s AI Push: From Llama to Chatbot, Subscription Model Coming Do Son March 3, 2025 0 Read More Read more about Meta’s AI Push: From Llama to Chatbot, Subscription Model Coming
Bitdefender Premium Security Review: The Ultimate All-In-One Security & Privacy Fortress Reviews Bitdefender Premium Security Review: The Ultimate All-In-One Security & Privacy Fortress Do Son March 3, 2025 0 Read More Read more about Bitdefender Premium Security Review: The Ultimate All-In-One Security & Privacy Fortress
CCleaner Review: Breathe New Life into Your Aging PC – Is It Still Relevant in 2025? Reviews CCleaner Review: Breathe New Life into Your Aging PC – Is It Still Relevant in 2025? Do Son March 3, 2025 0 Read More Read more about CCleaner Review: Breathe New Life into Your Aging PC – Is It Still Relevant in 2025?
McAfee+ Premium Review: All-Around Protection for Your Digital Life – But Is It the Best? Reviews McAfee+ Premium Review: All-Around Protection for Your Digital Life – But Is It the Best? Do Son March 3, 2025 0 Read More Read more about McAfee+ Premium Review: All-Around Protection for Your Digital Life – But Is It the Best?
Pentest-Tools.com Review: Your All-in-One Platform for Streamlined Penetration Testing and Vulnerability Management Reviews Pentest-Tools.com Review: Your All-in-One Platform for Streamlined Penetration Testing and Vulnerability Management Do Son March 3, 2025 0 Read More Read more about Pentest-Tools.com Review: Your All-in-One Platform for Streamlined Penetration Testing and Vulnerability Management
Bitdefender GravityZone Small Business Security Review: Enterprise-Grade Protection Without the Enterprise Headache Reviews Bitdefender GravityZone Small Business Security Review: Enterprise-Grade Protection Without the Enterprise Headache Do Son March 3, 2025 0 Read More Read more about Bitdefender GravityZone Small Business Security Review: Enterprise-Grade Protection Without the Enterprise Headache
10 New Vulnerabilities Found in MediaTek Chipsets Vulnerability 10 New Vulnerabilities Found in MediaTek Chipsets Do Son March 3, 2025 0 Read More Read more about 10 New Vulnerabilities Found in MediaTek Chipsets
Windows Hyper-V Zero-Day CVE-2025-21333: PoC Drops, SYSTEM Access Exposed Vulnerability Windows Hyper-V Zero-Day CVE-2025-21333: PoC Drops, SYSTEM Access Exposed Do Son March 2, 2025 0 Read More Read more about Windows Hyper-V Zero-Day CVE-2025-21333: PoC Drops, SYSTEM Access Exposed
CVE-2025-27154: Spotipy Vulnerability Exposes Spotify Auth Tokens Vulnerability CVE-2025-27154: Spotipy Vulnerability Exposes Spotify Auth Tokens Do Son March 2, 2025 0 Read More Read more about CVE-2025-27154: Spotipy Vulnerability Exposes Spotify Auth Tokens
Extreme Networks Addresses Critical Security Vulnerabilities in HiveOS Vulnerability Extreme Networks Addresses Critical Security Vulnerabilities in HiveOS Do Son March 2, 2025 0 Read More Read more about Extreme Networks Addresses Critical Security Vulnerabilities in HiveOS
Webmin Vulnerability Allows Bypassing of SSL Certificate Authentication Vulnerability Webmin Vulnerability Allows Bypassing of SSL Certificate Authentication Do Son March 2, 2025 0 Read More Read more about Webmin Vulnerability Allows Bypassing of SSL Certificate Authentication
Lotus Blossom Hackers Target Southeast Asia with Sagerunex Backdoor Cyber Security Malware Lotus Blossom Hackers Target Southeast Asia with Sagerunex Backdoor Do Son March 2, 2025 0 Read More Read more about Lotus Blossom Hackers Target Southeast Asia with Sagerunex Backdoor
Arista EOS Devices Vulnerable to Unauthorized Data Access and Configuration Changes (CVE-2025-1259 & CVE-2025-1260) Vulnerability Arista EOS Devices Vulnerable to Unauthorized Data Access and Configuration Changes (CVE-2025-1259 & CVE-2025-1260) Do Son March 2, 2025 0 Read More Read more about Arista EOS Devices Vulnerable to Unauthorized Data Access and Configuration Changes (CVE-2025-1259 & CVE-2025-1260)
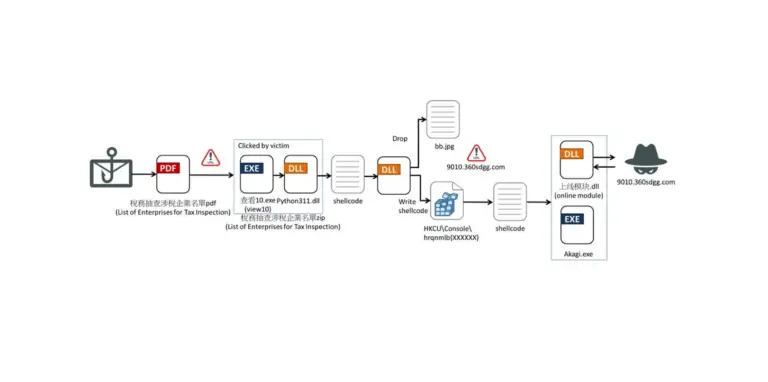
Phishing Campaign Delivers Winos 4.0: Keyloggers, UAC Bypass, and More Malware Phishing Campaign Delivers Winos 4.0: Keyloggers, UAC Bypass, and More Do Son March 2, 2025 0 Read More Read more about Phishing Campaign Delivers Winos 4.0: Keyloggers, UAC Bypass, and More
CVE-2024-47051 (CVSS 9.1): Critical RCE and File Deletion Flaws Expose 200,000+ Organizations Vulnerability CVE-2024-47051 (CVSS 9.1): Critical RCE and File Deletion Flaws Expose 200,000+ Organizations Do Son March 2, 2025 0 Read More Read more about CVE-2024-47051 (CVSS 9.1): Critical RCE and File Deletion Flaws Expose 200,000+ Organizations

 Do Son