Skip to content
October 6, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
ScreamedJungle Campaign Steals Browser Fingerprints from 115+ Sites Browser fingerprint
  • Cyber Security

ScreamedJungle Campaign Steals Browser Fingerprints from 115+ Sites

Do Son February 23, 2025 0
Read More Read more about ScreamedJungle Campaign Steals Browser Fingerprints from 115+ Sites
North Korean APT-C-28 Expands Cyber Espionage Campaign APT-C-28
  • Cyber Security

North Korean APT-C-28 Expands Cyber Espionage Campaign

Do Son February 23, 2025 0
Read More Read more about North Korean APT-C-28 Expands Cyber Espionage Campaign
GhostSocks Malware: A New Cyber Threat Leveraging SOCKS5 Backconnect for Evasion GhostSocks malware
  • Malware

GhostSocks Malware: A New Cyber Threat Leveraging SOCKS5 Backconnect for Evasion

Do Son February 23, 2025 0
Read More Read more about GhostSocks Malware: A New Cyber Threat Leveraging SOCKS5 Backconnect for Evasion
Apple Halts iCloud Advanced Data Protection in the UK After Government Demands Backdoor Access macOS Monterey vulnerability Apple Advanced Data Protection
  • Technology

Apple Halts iCloud Advanced Data Protection in the UK After Government Demands Backdoor Access

Do Son February 23, 2025 0
Read More Read more about Apple Halts iCloud Advanced Data Protection in the UK After Government Demands Backdoor Access
ChromeUpdate & DriverEasy: North Korea’s New macOS Cyber Espionage Tools North Korean Laptop Farm DPRK Insider Threat North Korea WMD Cyber Funding, Australia Sanctions Insider threat, North Korean hackers Kimsuky, cyber-espionage NPM Malware, North Korea Cyber-espionage North Korea, Remote IT Job Scam Laptop Farm - DriverEasy - Kimsuky Watering Hole Attack
  • Malware

ChromeUpdate & DriverEasy: North Korea’s New macOS Cyber Espionage Tools

Do Son February 23, 2025 0
Read More Read more about ChromeUpdate & DriverEasy: North Korea’s New macOS Cyber Espionage Tools
Moxa PT Switches Vulnerable to CVE-2024-9404 Denial-of-Service Attack Moxa Hard-Coded Credentials, Critical JWT Bypass CVE-2024-9137 and CVE-2024-9139 - CVE-2024-12297 CVE-2024-7695 CVE-2024-9404 CVE-2024-12297 CVE-2025-0415
  • Vulnerability

Moxa PT Switches Vulnerable to CVE-2024-9404 Denial-of-Service Attack

Do Son February 23, 2025 0
Read More Read more about Moxa PT Switches Vulnerable to CVE-2024-9404 Denial-of-Service Attack
Russia-Linked Threat Actors Exploiting Signal Messenger to Eavesdrop on Sensitive Communications Signal Messenger threat
  • Cyber Security
  • Malware

Russia-Linked Threat Actors Exploiting Signal Messenger to Eavesdrop on Sensitive Communications

Do Son February 23, 2025 0
Read More Read more about Russia-Linked Threat Actors Exploiting Signal Messenger to Eavesdrop on Sensitive Communications
Exim Mail Transfer Agent Vulnerable to Remote SQL Injection (CVE-2025-26794), PoC Published CVE-2025-26794 Exim SQL Injection, Heap Buffer Overflow
  • Vulnerability

Exim Mail Transfer Agent Vulnerable to Remote SQL Injection (CVE-2025-26794), PoC Published

Do Son February 23, 2025 0
Read More Read more about Exim Mail Transfer Agent Vulnerable to Remote SQL Injection (CVE-2025-26794), PoC Published
CVE-2024-37361 (CVSS 9.9): Critical Vulnerability in Pentaho Business Analytics Server NTLM Vulnerabilities, CVE-2024-43451 CVE-2024-37361 - RESURGE Malware
  • Vulnerability

CVE-2024-37361 (CVSS 9.9): Critical Vulnerability in Pentaho Business Analytics Server

Do Son February 22, 2025 0
Read More Read more about CVE-2024-37361 (CVSS 9.9): Critical Vulnerability in Pentaho Business Analytics Server
LummaC2 Malware Masquerading as Total Commander Crack to Infect Windows Users LummaC2 Malware
  • Malware

LummaC2 Malware Masquerading as Total Commander Crack to Infect Windows Users

Do Son February 22, 2025 0
Read More Read more about LummaC2 Malware Masquerading as Total Commander Crack to Infect Windows Users
DDoS Attacks Surge During World Economic Forum (WEF) World Economic Forum DDoS attacks
  • Cyber Security

DDoS Attacks Surge During World Economic Forum (WEF)

Do Son February 22, 2025 0
Read More Read more about DDoS Attacks Surge During World Economic Forum (WEF)
CVE-2024-56000 (CVSS 9.8): Account Takeover Flaw in KLEO WordPress Theme CVE-2024-56000
  • Vulnerability

CVE-2024-56000 (CVSS 9.8): Account Takeover Flaw in KLEO WordPress Theme

Do Son February 21, 2025 0
Read More Read more about CVE-2024-56000 (CVSS 9.8): Account Takeover Flaw in KLEO WordPress Theme
Bloody Wolf Cybercrime Group Evolves Tactics, Expands Targets Phishing letter
  • Cyber Security

Bloody Wolf Cybercrime Group Evolves Tactics, Expands Targets

Do Son February 21, 2025 0
Read More Read more about Bloody Wolf Cybercrime Group Evolves Tactics, Expands Targets
Publicly Disclosed Exploits Put D-Link DIR-823 Users in Danger – No Security Fixes D-Link DIR-823 vulnerabiity
  • Vulnerability

Publicly Disclosed Exploits Put D-Link DIR-823 Users in Danger – No Security Fixes

Do Son February 21, 2025 0
Read More Read more about Publicly Disclosed Exploits Put D-Link DIR-823 Users in Danger – No Security Fixes
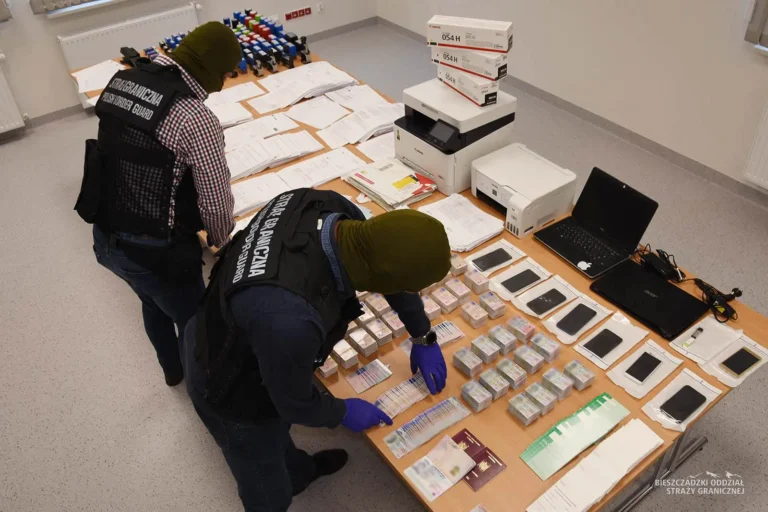
Europol Cracks Down on European Document Forgery and Smuggling Ring Criminal group
  • Cyber Security

Europol Cracks Down on European Document Forgery and Smuggling Ring

Do Son February 21, 2025 0
Read More Read more about Europol Cracks Down on European Document Forgery and Smuggling Ring
Apple’s Spyware Detection: Only 50% Effective? Pegasus spyware sample
  • Malware

Apple’s Spyware Detection: Only 50% Effective?

Do Son February 21, 2025 0
Read More Read more about Apple’s Spyware Detection: Only 50% Effective?
ChatGPT Hits 400 Million Weekly Users ChatGPT active user
  • Technology

ChatGPT Hits 400 Million Weekly Users

Do Son February 21, 2025 0
Read More Read more about ChatGPT Hits 400 Million Weekly Users
Apple C2 Modem: Next-Gen 5G in the Works? Apple C2 modem Apple Product Roadmap, iPhone 17
  • Technology

Apple C2 Modem: Next-Gen 5G in the Works?

Do Son February 21, 2025 0
Read More Read more about Apple C2 Modem: Next-Gen 5G in the Works?
Amazon Appstore on Android to Shut Down in 2025: What It Means for Users and Developers Amazon Appstore Android
  • Technology

Amazon Appstore on Android to Shut Down in 2025: What It Means for Users and Developers

Do Son February 20, 2025 0
Read More Read more about Amazon Appstore on Android to Shut Down in 2025: What It Means for Users and Developers
Google Releases PoC for CVE-2025-0110 Command Injection in PAN-OS Firewalls CVE-2024-5921 - CVE-2025-0103 CVE-2025-0110 PoC
  • Vulnerability

Google Releases PoC for CVE-2025-0110 Command Injection in PAN-OS Firewalls

Do Son February 20, 2025 0
Read More Read more about Google Releases PoC for CVE-2025-0110 Command Injection in PAN-OS Firewalls
CVE-2025-23115 & CVE-2025-23116: Hackers Can Hijack Ubiquiti UniFi Protect Cameras CVE-2025-23115 & CVE-2025-23116
  • Vulnerability

CVE-2025-23115 & CVE-2025-23116: Hackers Can Hijack Ubiquiti UniFi Protect Cameras

Do Son February 20, 2025 0
Read More Read more about CVE-2025-23115 & CVE-2025-23116: Hackers Can Hijack Ubiquiti UniFi Protect Cameras
CVE-2025-0111 & CVE-2025-23209: Palo Alto Firewalls and Craft CMS Under Active Attack Ivanti EPMM Vulnerability CVE-2026-1340 CISA KEV Catalog CVE-2026-21385 CISA KEV Update CVE-2008-0015 CISA KEV, Array Networks Command Injection CVE-2025-0111 & CVE-2025-23209 CISA, Known Exploited Vulnerabilities
  • Vulnerability

CVE-2025-0111 & CVE-2025-23209: Palo Alto Firewalls and Craft CMS Under Active Attack

Do Son February 20, 2025 0
Read More Read more about CVE-2025-0111 & CVE-2025-23209: Palo Alto Firewalls and Craft CMS Under Active Attack
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-88779CVSS 8.7
    Vulnerability in NetScaler ADC and NetScaler Gateway. This issue affects ADC: before 14.1-73.41, before 13.1-64.28, before 14.1-73.41 FIPS,...
    Admin intelCISA KEV📅 Added to KEV: Oct 4, 2026📅 Updated: Oct 4, 2026
  • CVE-2026-102490CVSS 8.5
    All versions of Zammad including the latest alpha enable the local zammad user to escalate privileges to root.
    Admin intelCISA KEV📅 Added to KEV: Oct 2, 2026📅 Updated: Oct 2, 2026
  • CVE-2026-102489CVSS 8.7
    Zammad versions 6.3.0 to 6.5.4 are vulnerable a session hijack vulnerability that leads to remote code execution as...
    Admin intelCISA KEV📅 Added to KEV: Oct 2, 2026📅 Updated: Oct 2, 2026
  • CVE-2026-100382CVSS 10.0
    Improper Neutralization of Special Elements used in an OS Command (\'OS Command Injection\') vulnerability in Wikimedia Foundation Mediawiki...
    Admin intel📅 Updated: Oct 1, 2026
  • CVE-2026-104286CVSS 9.8
    An improper limitation of a pathname to a restricted directory ('path traversal') vulnerability in Fortinet FortiMail 8.0.0 through...
    CISA KEV📅 Added to KEV: Oct 1, 2026
  • CVE-2026-76504CVSS 9.8
    A vulnerability in the API session-based authentication management of Cisco Catalyst SD-WAN Manager could allow an unauthenticated, remote...
    Admin intelCISA KEV📅 Added to KEV: Sep 30, 2026📅 Updated: Sep 30, 2026
  • CVE-2026-86950CVSS 8.8
    An out-of-bounds write issue was addressed with improved bounds checking. This issue is fixed in iOS 26.7.1 and...
    Admin intelCISA KEV📅 Added to KEV: Sep 29, 2026📅 Updated: Sep 29, 2026
  • CVE-2026-88772
    Memory overflow vulnerability leading to remote code execution or denial of service.
    Admin intelCISA KEV📅 Added to KEV: Sep 27, 2026📅 Updated: Sep 27, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-104019CVSS 9.3
    OS command injection in the Studio Space startup validation script in Amazon SageMaker Distribution 2.x before 2.14.12, 3.x...
    📅 Updated: Oct 6, 2026
  • CVE-2026-105778CVSS 9.4
    A vulnerability has been found in Tenda AC5 02.03.01.111_multi. Affected by this issue is some unknown functionality of...
    📅 Updated: Oct 6, 2026
  • CVE-2026-105794CVSS 9.1
    MsQuic is a cross-platform C implementation of the IETF QUIC protocol exposed to C, C++, C#, and Rust....
    📅 Updated: Oct 6, 2026
  • CVE-2026-105851CVSS 9.3
    Payload is a free and open source headless content management system. In versions from 3.0.0 before 3.90.0 and...
    📅 Updated: Oct 6, 2026
  • CVE-2026-87830CVSS 9.1
    In the StAX streaming WS-SecurityPolicy validator, certain relative or unsupported XPath expressions can be converted into paths that...
    📅 Updated: Oct 6, 2026
  • CVE-2026-89238CVSS 9.1
    WSS4J EncryptedHeader child confusion could promote an attacker-controlled plaintext element as the decrypted header, leading to incorrect confidentiality...
    📅 Updated: Oct 6, 2026
  • CVE-2026-94293CVSS 9.3
    An unauthenticated remote attacker can modify Asset Administration Shell submodel data via PATCH requests and can read all...
    📅 Updated: Oct 6, 2026
  • CVE-2026-88424CVSS 9.8
    FineAdmin v1.0 was discovered to contain a SQL injection vulnerability via the field/order parameter at ButtonService.GetListByFilter(). This vulnerability...
    📅 Updated: Oct 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.