Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Google Launches Cloud WAN for Secure, High-Performance Enterprise Networking Cloud WAN Google Cloud
  • Technology

Google Launches Cloud WAN for Secure, High-Performance Enterprise Networking

Do Son April 9, 2025 0

Google introduces Cloud WAN, a fully managed backbone network service, providing secure and reliable connectivity for enterprises. Learn how it leverages Google's global infrastructure for enhanced performance and reduced costs.

Google Introduces Agent2Agent Protocol for Cross-Platform AI Agent Interoperability Agent2Agent Agentspace
  • Technology

Google Introduces Agent2Agent Protocol for Cross-Platform AI Agent Interoperability

Do Son April 9, 2025 0

Google launches the Agent2Agent (A2A) protocol, an open-source standard for cross-platform AI agent interoperability, and enhances Agentspace with new development tools and an AI Agent Marketplace. Learn how this enables seamless multi-cloud AI collaboration.

Google’s Vertex AI Introduces Lyria Text-to-Music and Enhanced Generative AI Tools Lyria Vertex AI
  • Technology

Google’s Vertex AI Introduces Lyria Text-to-Music and Enhanced Generative AI Tools

Do Son April 9, 2025 0

Google launches Lyria, a text-to-music model on Vertex AI, alongside enhanced Veo 2, Imagen 3, and Chirp 3 tools. Discover how these advancements unify image, video, voice, and music generation in a single platform.

Google Workspace Introduces Workspace Flows and AI Enhancements Google Arkansas Investment, AI Data Center Google, privacy fine Ecosia Google Chrome Alphabet Earnings, AI Growth Google Hydropower, AI Data Centers Google Breakup Antitrust Workspace Flows Google Workspace Google remote work, return to office
  • Technology

Google Workspace Introduces Workspace Flows and AI Enhancements

Do Son April 9, 2025 0

Google launches Workspace Flows for AI-powered workflow automation and integrates Gemini across Workspace with enhanced Docs, Sheets, and Meet features. Learn how these updates streamline productivity and collaboration.

Google Launches Gemini 2.5 Flash for Fast, Cost-Effective AI on Vertex AI Gemini 2.5 Flash Vertex AI Gemini 2.5 Flash, AI model
  • Technology

Google Launches Gemini 2.5 Flash for Fast, Cost-Effective AI on Vertex AI

Do Son April 9, 2025 0

Google introduces Gemini 2.5 Flash, a fast and cost-effective AI model on Vertex AI, designed for low latency and efficient performance in applications like virtual assistants and real-time summarization. Discover its dynamic reasoning and optimization tools.

Amazon Unveils Nova Sonic: A Unified Model for Natural Voice AI Interactions Amazon AI, Carbon Footprint Nova Sonic, speech AI Amazon Nova
  • Technology

Amazon Unveils Nova Sonic: A Unified Model for Natural Voice AI Interactions

Do Son April 9, 2025 0

Amazon introduces Nova Sonic, an advanced foundation model that unifies speech understanding and generation to deliver lifelike, emotionally aware AI conversations.
Critical Vulnerabilities: CISA Alerts to Windows CLFS and Gladinet CentreStack Threats CISA KEV Update Versa Concerto Vulnerability KEV Catalog Vulnerability Patch CVE-2025-30406
  • Vulnerability

Critical Vulnerabilities: CISA Alerts to Windows CLFS and Gladinet CentreStack Threats

Do Son April 9, 2025 0

CISA has added critical vulnerabilities affecting Windows CLFS (CVE-2025-29824) and Gladinet CentreStack (CVE-2025-30406) to its Known Exploited Vulnerabilities Catalog. Learn about the threats and the urgent need to apply patches.Sources and related content

Windows CLFS Zero-Day Exploited to Deploy Ransomware CLFS zero-day Ransomware attack
  • Malware
  • Vulnerability

Windows CLFS Zero-Day Exploited to Deploy Ransomware

Do Son April 9, 2025 0

Microsoft reports active exploitation of a Windows CLFS zero-day (CVE-2025-29824) to escalate privileges and deploy ransomware. Learn about the attacks, the threat actors involved, and how to mitigate the risk.

Siemens Security Alert: Critical Vulnerabilities in SENTRON 7KT PAC1260 Data Manager Siemens RTLS, CVE-2025-40746 CVE-2024-22040 - SINEC Security Monitor Siemens Security Advisory SENTRON 7KT PAC1260
  • Vulnerability

Siemens Security Alert: Critical Vulnerabilities in SENTRON 7KT PAC1260 Data Manager

Do Son April 9, 2025 0

Siemens ProductCERT issued a security advisory detailing critical vulnerabilities in the SENTRON 7KT PAC1260 Data Manager. The flaws could allow remote attackers to execute code, bypass authentication, and more.

Kibana Code Injection Vulnerability: Prototype Pollution Threat (CVE-2024-12556) CVE-2024-43707 Kibana vulnerability Prototype pollution CVE-2025-25014
  • Vulnerability

Kibana Code Injection Vulnerability: Prototype Pollution Threat (CVE-2024-12556)

Do Son April 9, 2025 0

A vulnerability (CVE-2024-12556) in Kibana allows code injection via prototype pollution, file upload, and path traversal. Upgrade to the latest version or disable the integration assistant to mitigate this high-severity security risk.
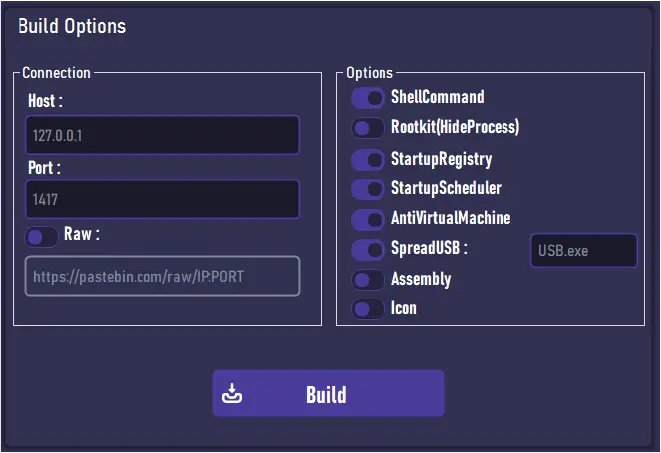
Neptune RAT: Advanced Malware Targets Windows with Destructive Capabilities Neptune RAT, Remote Access Trojan
  • Malware

Neptune RAT: Advanced Malware Targets Windows with Destructive Capabilities

Do Son April 9, 2025 0

CYFIRMA researchers discovered Neptune RAT, an advanced Remote Access Trojan targeting Windows. Learn about its destructive features, evasion techniques, and distribution methods.

Chrome Update Fixes High-Severity “Use After Free” Vulnerability Chrome update Security vulnerability
  • Vulnerability

Chrome Update Fixes High-Severity “Use After Free” Vulnerability

Do Son April 9, 2025 0

The latest Chrome update addresses a high-severity "use after free" vulnerability in Site Isolation (CVE-2025-3066). Learn about the security risk and the importance of updating your Chrome browser

Rogue RDP: Abusing RDP for File Theft and Espionage GUI
  • Cyber Security

Rogue RDP: Abusing RDP for File Theft and Espionage

Do Son April 9, 2025 0

Attackers are using "Rogue RDP" techniques, abusing RemoteApp and resource redirection to steal files and conduct espionage

Microsoft April 2025 Patch Tuesday: Critical Security Updates and Zero-Day Exploits Microsoft Patch Tuesday fixes disclosed zero day vulnerabilities Windows Wormable Exploit April 2026 Patch Tuesday Microsoft Patch Tuesday Zero-Day Vulnerabilities Microsoft, Patch Tuesday CVE-2025-55234 CVE-2024-43573 and CVE-2024-43572 Microsoft Patch Tuesday Security Vulnerabilities
  • Vulnerability
  • Windows

Microsoft April 2025 Patch Tuesday: Critical Security Updates and Zero-Day Exploits

Do Son April 9, 2025 0

Microsoft's April 2025 Patch Tuesday addresses 134 vulnerabilities, including a zero-day under active exploitation. This update covers critical RCE flaws in Windows, Office, and more

Inaba Denki Sangyo Wi-Fi AP Units Affected by Critical Vulnerabilities Vonets WiFi Bridge Inaba Denki Sangyo Wi-Fi vulnerability
  • Vulnerability

Inaba Denki Sangyo Wi-Fi AP Units Affected by Critical Vulnerabilities

Do Son April 9, 2025 0

JPCERT/CC reports multiple vulnerabilities in Inaba Denki Sangyo Wi-Fi AP units, including command injection and authentication issues

Vidar Stealer Hides in Legitimate BGInfo Tool Vidar Stealer, malware, BGInfo
  • Malware

Vidar Stealer Hides in Legitimate BGInfo Tool

Do Son April 9, 2025 0

Vidar Stealer malware is distributed by masquerading as BGInfo.exe, exploiting expired signatures and file discrepancies to evade detection

SourceForge Used to Distribute ClipBanker Trojan and Cryptocurrency Miner ClipBanker Trojan
  • Malware

SourceForge Used to Distribute ClipBanker Trojan and Cryptocurrency Miner

Do Son April 9, 2025 0

Attackers are using SourceForge to distribute malware, including a ClipBanker Trojan and a cryptocurrency miner, disguised as a Microsoft Office enhancement suite.

Grandoreiro Trojan Resurges in Phishing Attacks Grandoreiro, banking trojan, phishing
  • Malware

Grandoreiro Trojan Resurges in Phishing Attacks

Do Son April 9, 2025 0

The Grandoreiro banking trojan is being spread through phishing campaigns. Learn about the attack methods and how to stay safe.

Apache mod_auth_openidc Vulnerability Exposes Protected Content mod_auth_openidc, Apache security
  • Vulnerability

Apache mod_auth_openidc Vulnerability Exposes Protected Content

Do Son April 9, 2025 0

A security flaw in Apache's mod_auth_openidc module can expose protected web content to unauthenticated users. Patch or mitigate to secure your server

Malicious VSCode Extensions Caught Mining Crypto with XMRig VSCode extensions, cryptomining
  • Malware

Malicious VSCode Extensions Caught Mining Crypto with XMRig

Do Son April 9, 2025 0

Ten popular Visual Studio Code extensions were found secretly installing XMRig miners, exploiting users’ CPUs for unauthorized cryptomining.

Fortinet: Critical Unverified Password Change Flaw in FortiSwitch Fortinet Vulnerability CVE-2024-48887
  • Vulnerability

Fortinet: Critical Unverified Password Change Flaw in FortiSwitch

Do Son April 8, 2025 0

Fortinet has addressed a critical vulnerability (CVE-2024-48887) in FortiSwitch that allows unauthenticated attackers to change admin passwords. Upgrade to the latest version to secure your devices.

Europol Operation Dismantles Major Euro Counterfeiting Ring Euro Counterfeiting Europol
  • Cybercriminals

Europol Operation Dismantles Major Euro Counterfeiting Ring

Do Son April 8, 2025 0

A Europol-supported operation dismantled a major criminal group producing counterfeit euro banknotes. The investigation spanned multiple countries and resulted in arrests and the seizure of fake currency and production facilities.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-123218CVSS 9.8
    IBM Aspera Faspex 5.0.0 through 5.0.19 could allow an authorized user to craft a specific message to bypass...
    CISA KEV📅 Added to KEV: Nov 9, 2026📅 Updated: Nov 10, 2026
  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-89126CVSS 10.0
    SAP Web Dispatcher does not sufficiently validate certain network input processed by an internal component. An unauthenticated attacker...
    📅 Updated: Nov 10, 2026
  • CVE-2026-89119CVSS 9.6
    SAP Web Dispatcher and SAP NetWeaver Application Server ABAP (Internet Communication Manager) do not perform sufficient request validation...
    📅 Updated: Nov 10, 2026
  • CVE-2026-89103CVSS 10.0
    SAP Gateway activates the default Access Control List with high privileges allowing categorization of external attacker as internal...
    📅 Updated: Nov 10, 2026
  • CVE-2026-76964CVSS 10.0
    SAP NetWeaver Application Server ABAP does not sufficiently validate certain network input processed by an internal component. An...
    📅 Updated: Nov 10, 2026
  • CVE-2026-76965CVSS 9.9
    SAP NetWeaver Application Server ABAP and ABAP Platform does not perform necessary authorization checks for certain internal functionality....
    📅 Updated: Nov 10, 2026
  • CVE-2026-120017CVSS 10.0
    SAP NetWeaver AS ABAP and ABAP Platform does not perform sufficient verification of incoming authentication assertions under certain...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.