Skip to content
September 25, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Veeam Releases Patch for High-Risk SSRF Vulnerability CVE-2025-23082 in Azure Backup Solution CVE-2024-29212 - CVE-2025-23082 Veeam Backup & Replication CVE-2025-59470
  • Vulnerability

Veeam Releases Patch for High-Risk SSRF Vulnerability CVE-2025-23082 in Azure Backup Solution

Do Son January 15, 2025 0
Read More Read more about Veeam Releases Patch for High-Risk SSRF Vulnerability CVE-2025-23082 in Azure Backup Solution
CVE-2023-37936 (CVSS 9.6): Urgent Patch Needed for FortiSwitch Vulnerability FortiSandbox Vulnerability Unauthenticated RCE FortiClient EMS Vulnerability CVE-2026-21643 FortiClient EMS Vulnerability CVE-2026-21643 CVE-2023-34992 - CVE-2023-37936 Fortinet Vulnerabilities CVE-2025-64155
  • Vulnerability

CVE-2023-37936 (CVSS 9.6): Urgent Patch Needed for FortiSwitch Vulnerability

Do Son January 15, 2025 0
Read More Read more about CVE-2023-37936 (CVSS 9.6): Urgent Patch Needed for FortiSwitch Vulnerability
Millions Stolen: North Korea Hackers Target Blockchain Industry Google Play, Crypto Wallets Cryptocurrency Thefts
  • Cyber Security

Millions Stolen: North Korea Hackers Target Blockchain Industry

Do Son January 14, 2025 0
Read More Read more about Millions Stolen: North Korea Hackers Target Blockchain Industry
CVE-2024-12084 (CVSS 9.8) – Code Execution Risk: Rsync Vulnerability Demands Immediate Patching CVE-2024-12084
  • Vulnerability

CVE-2024-12084 (CVSS 9.8) – Code Execution Risk: Rsync Vulnerability Demands Immediate Patching

Do Son January 14, 2025 0
Read More Read more about CVE-2024-12084 (CVSS 9.8) – Code Execution Risk: Rsync Vulnerability Demands Immediate Patching
“PlugX” Malware Deleted from Thousands of Computers in Global Operation Seedworm Espionage Campaign 2026 ChromElevator Stealer DLL Sideloading SIM Swapping Crypto Theft Lazarus Comebacker, Aerospace Espionage Delete PlugX Malware
  • Malware
  • Vulnerability

“PlugX” Malware Deleted from Thousands of Computers in Global Operation

Do Son January 14, 2025 0
Read More Read more about “PlugX” Malware Deleted from Thousands of Computers in Global Operation
Ivanti Endpoint Manager Patches Critical Security Vulnerabilities CVE-2023-38036 - CVE-2024-10811
  • Vulnerability

Ivanti Endpoint Manager Patches Critical Security Vulnerabilities

Do Son January 14, 2025 0
Read More Read more about Ivanti Endpoint Manager Patches Critical Security Vulnerabilities
CVE-2025-0147: Zoom Fixes High-Severity Security Flaw CVE-2025-0147
  • Vulnerability

CVE-2025-0147: Zoom Fixes High-Severity Security Flaw

Do Son January 14, 2025 0
Read More Read more about CVE-2025-0147: Zoom Fixes High-Severity Security Flaw
Malicious npm Packages Exploit Developer Tools with Hidden Kill Switch Kill Switch
  • Malware

Malicious npm Packages Exploit Developer Tools with Hidden Kill Switch

Do Son January 14, 2025 0
Read More Read more about Malicious npm Packages Exploit Developer Tools with Hidden Kill Switch
Fortinet FortiGate Firewalls Targeted in Sophisticated Campaign Exploiting Management Interfaces Weaver E-cology RCE CVE-2026-22679 CVE-2026-20127 Cisco SD-WAN Exploitation AI-Driven Cyberattack ARXON Malware React Server Components Vulnerability CVE-2025-55182 FortiWeb Auth Bypass, Unauthenticated Admin Takeover RayInitiator Bootkit, LINE VIPER CVE-2025-59689 Department of the Treasury cybersecurity - CVE-2025-0108 PoC CVE-2025-31103 Dior Data Breach SK Telecom data breach, long-term intrusion
  • Cyber Security
  • Vulnerability

Fortinet FortiGate Firewalls Targeted in Sophisticated Campaign Exploiting Management Interfaces

Do Son January 14, 2025 0
Read More Read more about Fortinet FortiGate Firewalls Targeted in Sophisticated Campaign Exploiting Management Interfaces
Over 5,000 WordPress Sites Infected in WP3.XYZ Malware Attack WP3.XYZ Malware Attack
  • Malware

Over 5,000 WordPress Sites Infected in WP3.XYZ Malware Attack

Do Son January 14, 2025 0
Read More Read more about Over 5,000 WordPress Sites Infected in WP3.XYZ Malware Attack
Chrome 132 Arrives: 16 Security Fixes in Latest Stable Release Chrome 132
  • Vulnerability

Chrome 132 Arrives: 16 Security Fixes in Latest Stable Release

Do Son January 14, 2025 0
Read More Read more about Chrome 132 Arrives: 16 Security Fixes in Latest Stable Release
Microsoft’s January 2025 Patch Tuesday Fixes 159 Vulnerabilities, Including 10 Critical and 8 Zero-Days Driver Cleanup CVE-2024-49138 - December Patch Tuesday Windows update errors, Windows update troubleshooting
  • Vulnerability
  • Windows

Microsoft’s January 2025 Patch Tuesday Fixes 159 Vulnerabilities, Including 10 Critical and 8 Zero-Days

Do Son January 14, 2025 0
Read More Read more about Microsoft’s January 2025 Patch Tuesday Fixes 159 Vulnerabilities, Including 10 Critical and 8 Zero-Days
SimpleHelp Urgents to Patch Critical Security Vulnerabilities Screenshot 2025-01-14 222456
  • Vulnerability

SimpleHelp Urgents to Patch Critical Security Vulnerabilities

Do Son January 14, 2025 0
Read More Read more about SimpleHelp Urgents to Patch Critical Security Vulnerabilities
Multi-Layered Attack: Formbook Stealer Bypasses Detection with Memory-Based Execution macOS malware 2024 XCSSET
  • Malware

Multi-Layered Attack: Formbook Stealer Bypasses Detection with Memory-Based Execution

Do Son January 14, 2025 0
Read More Read more about Multi-Layered Attack: Formbook Stealer Bypasses Detection with Memory-Based Execution
Active Exploitation of CVE-2024-55591 (CVSS 9.6): FortiOS and FortiProxy Under Threat BeyondTrust Vulnerability CVE-2026-1731 UPBIT $369M Hack CVE-2024-55591 Ivanti VPN vulnerability, cyber espionage
  • Vulnerability

Active Exploitation of CVE-2024-55591 (CVSS 9.6): FortiOS and FortiProxy Under Threat

Do Son January 14, 2025 0
Read More Read more about Active Exploitation of CVE-2024-55591 (CVSS 9.6): FortiOS and FortiProxy Under Threat
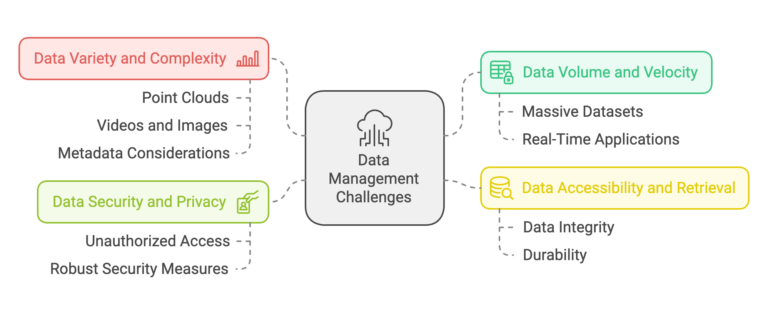
How to Store Computer Vision Data Effectively data-vision
  • Technique

How to Store Computer Vision Data Effectively

Do Son January 14, 2025 0
Read More Read more about How to Store Computer Vision Data Effectively
Biden’s AI Chip Export Restrictions: A Strategic Move to Counter Global Tech Threats Bad Likert Judge - Artificial Intelligence Diffusion
  • Technology

Biden’s AI Chip Export Restrictions: A Strategic Move to Counter Global Tech Threats

Do Son January 14, 2025 0
Read More Read more about Biden’s AI Chip Export Restrictions: A Strategic Move to Counter Global Tech Threats
Critical SAP Flaws Revealed: CVE-2025-0070 and CVE-2025-0066 with CVSS 9.9 Demand Immediate Action SAP Security Patches CVE-2026-27685 SAP Security Update CVE-2026-0488 CVE-2024-47578 - CVE-2025-0070 and CVE-2025-0066
  • Vulnerability

Critical SAP Flaws Revealed: CVE-2025-0070 and CVE-2025-0066 with CVSS 9.9 Demand Immediate Action

Do Son January 14, 2025 0
Read More Read more about Critical SAP Flaws Revealed: CVE-2025-0070 and CVE-2025-0066 with CVSS 9.9 Demand Immediate Action
Linux Kernel Privilege Escalation Vulnerability (CVE-2024-27397) Exploited: PoC Released CrackArmor AppArmor Vulnerabilities Linux Kernel UAF, Privilege Escalation PoC CVE-2024-27397 PoC
  • Linux
  • Vulnerability

Linux Kernel Privilege Escalation Vulnerability (CVE-2024-27397) Exploited: PoC Released

Do Son January 13, 2025 0
Read More Read more about Linux Kernel Privilege Escalation Vulnerability (CVE-2024-27397) Exploited: PoC Released
Zyxel Urges Patch Application for Privilege Escalation Vulnerability (CVE-2024-12398) CVE-2022-43389 - CVE-2024-12398 Zyxel UPnP Vulnerability CVE-2025-13942
  • Vulnerability

Zyxel Urges Patch Application for Privilege Escalation Vulnerability (CVE-2024-12398)

Do Son January 13, 2025 0
Read More Read more about Zyxel Urges Patch Application for Privilege Escalation Vulnerability (CVE-2024-12398)
CISA Warns of Active Exploitation of Critical Flaws in BeyondTrust and Qlik Sense GUARDIANWALL MailSuite Exploit CVE-2026-32661 FileZen Vulnerability CVE-2026-25108 Ivanti EPMM Vulnerability Dormant Backdoor Fortinet Authentication Bypass CVE-2026-24858 VMware vCenter Server Flaw CVE-2025-21590
  • Vulnerability

CISA Warns of Active Exploitation of Critical Flaws in BeyondTrust and Qlik Sense

Do Son January 13, 2025 0
Read More Read more about CISA Warns of Active Exploitation of Critical Flaws in BeyondTrust and Qlik Sense
Kernel Modules and Malicious Commands: Anatomy of the sysinitd Rootkit sysinitd rootkit
  • Linux
  • Malware

Kernel Modules and Malicious Commands: Anatomy of the sysinitd Rootkit

Do Son January 13, 2025 0
Read More Read more about Kernel Modules and Malicious Commands: Anatomy of the sysinitd Rootkit
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📧

Email Delivery
Get threat intel straight to your inbox.

♾️

Unlimited Vendors
Track every technology in your stack.

🚨

All New CVE Alerts
Be the first to know about new flaws.

⚙️

Custom EPSS Threshold
Filter noise, focus on real risks.

💬

Slack & Teams Webhook
Integrate directly into your SecOps.

🚫

100% Ad-Free
Enjoy an uninterrupted reading experience.

$7/mo
Subscribe Now

🚨 Active Exploits in the Wild

  • CVE-2026-5430CVSS 10.0
    The JWT authentication mechanism accepts tokens signed with algorithms other than those explicitly configured or supported. This allows...
    CISA KEV📅 Added to KEV: Sep 24, 2026
  • CVE-2026-71362CVSS 9.1
    Adobe Commerce is affected by an Incorrect Authorization vulnerability that could result in privilege escalation. An attacker could...
    CISA KEV📅 Added to KEV: Sep 24, 2026
  • CVE-2026-48842CVSS 8.1
    Roundcube Webmail 1.6.x before 1.6.16 and 1.7.x before 1.7.1 has Pre-authentication SQL injection in the virtuser_query plugin via...
    Admin intel📅 Updated: Sep 23, 2026
  • CVE-2026-87902
    Unauthenticated path traversal in page-template resolution leading to conditional RCE An unauthenticated attacker can make get_page_template() page-template resolution...
    Admin intel📅 Updated: Sep 23, 2026
  • CVE-2026-94127CVSS 9.8
    When a BIG-IP APM access policy and an OAuth profile is configured on a virtual server, specific malicious...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
  • CVE-2026-85102CVSS 9.8
    Improper certificate trust validation during VPN negotiation in Check Point Quantum Security Gateway may allow an unauthenticated remote...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
  • CVE-2026-93616CVSS 9.8
    A directory traversal and file upload vulnerability allows an unauthenticated attacker to upload and execute arbitrary scripts on...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
  • CVE-2026-93952CVSS 10.0
    VeloCloud Orchestrator (VCO) on-prem has a security issue where this issue may allow a remote attacker to access...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-97413CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: RDMA/rtrs-srv: Fix integer underflow in process_read and process_write...
    📅 Updated: Sep 25, 2026
  • CVE-2026-93228CVSS 9.1
    In the Linux kernel, the following vulnerability has been resolved: svcrdma: Reject Write/Reply chunks with segcount 0 A...
    📅 Updated: Sep 25, 2026
  • CVE-2026-93207CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: SUNRPC: Zero rpc_gss_wire_cred at svcauth_gss_decode_credbody() entry svcauth_gss_decode_credbody() writes...
    📅 Updated: Sep 25, 2026
  • CVE-2026-93577CVSS 9.9
    GitLab has remediated an issue in GitLab CE/EE affecting all versions from 19.2 before 19.2.7, 19.3 before 19.3.3,...
    📅 Updated: Sep 25, 2026
  • CVE-2026-89078CVSS 9.9
    GitLab has remediated an issue in GitLab CE/EE affecting all versions from 19.2 before 19.2.7, 19.3 before 19.3.3,...
    📅 Updated: Sep 25, 2026
  • CVE-2026-71362CVSS 9.1
    Adobe Commerce is affected by an Incorrect Authorization vulnerability that could result in privilege escalation. An attacker could...
    CISA KEV📅 Added to KEV: Sep 24, 2026📅 Updated: Sep 25, 2026
  • CVE-2026-6928CVSS 9.8
    IBM Concert 1.0.0 through 3.0.0 references or accesses memory after it has been freed. This allows an attacker...
    📅 Updated: Sep 25, 2026
  • CVE-2026-6721CVSS 9.8
    IBM Concert 1.0.0 through 3.0.0 allows an unauthenticated remote attacker can supply specially crafted input that is incorporated...
    📅 Updated: Sep 25, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.