Skip to content
October 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Chrome 132 Arrives: 16 Security Fixes in Latest Stable Release Chrome 132
  • Vulnerability

Chrome 132 Arrives: 16 Security Fixes in Latest Stable Release

Do Son January 14, 2025 0
Read More Read more about Chrome 132 Arrives: 16 Security Fixes in Latest Stable Release
Microsoft’s January 2025 Patch Tuesday Fixes 159 Vulnerabilities, Including 10 Critical and 8 Zero-Days Driver Cleanup CVE-2024-49138 - December Patch Tuesday Windows update errors, Windows update troubleshooting
  • Vulnerability
  • Windows

Microsoft’s January 2025 Patch Tuesday Fixes 159 Vulnerabilities, Including 10 Critical and 8 Zero-Days

Do Son January 14, 2025 0
Read More Read more about Microsoft’s January 2025 Patch Tuesday Fixes 159 Vulnerabilities, Including 10 Critical and 8 Zero-Days
SimpleHelp Urgents to Patch Critical Security Vulnerabilities Screenshot 2025-01-14 222456
  • Vulnerability

SimpleHelp Urgents to Patch Critical Security Vulnerabilities

Do Son January 14, 2025 0
Read More Read more about SimpleHelp Urgents to Patch Critical Security Vulnerabilities
Multi-Layered Attack: Formbook Stealer Bypasses Detection with Memory-Based Execution macOS malware 2024 XCSSET
  • Malware

Multi-Layered Attack: Formbook Stealer Bypasses Detection with Memory-Based Execution

Do Son January 14, 2025 0
Read More Read more about Multi-Layered Attack: Formbook Stealer Bypasses Detection with Memory-Based Execution
Active Exploitation of CVE-2024-55591 (CVSS 9.6): FortiOS and FortiProxy Under Threat BeyondTrust Vulnerability CVE-2026-1731 UPBIT $369M Hack CVE-2024-55591 Ivanti VPN vulnerability, cyber espionage
  • Vulnerability

Active Exploitation of CVE-2024-55591 (CVSS 9.6): FortiOS and FortiProxy Under Threat

Do Son January 14, 2025 0
Read More Read more about Active Exploitation of CVE-2024-55591 (CVSS 9.6): FortiOS and FortiProxy Under Threat
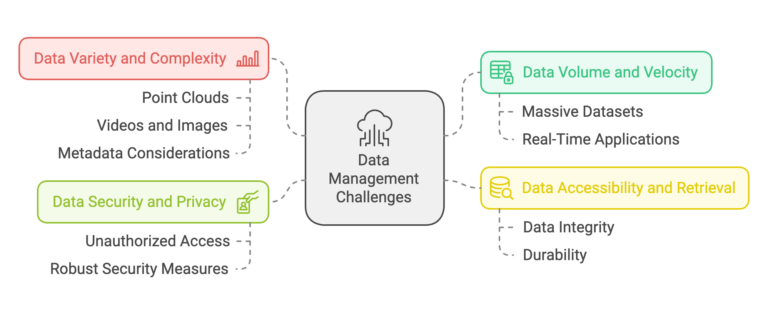
How to Store Computer Vision Data Effectively data-vision
  • Technique

How to Store Computer Vision Data Effectively

Do Son January 14, 2025 0
Read More Read more about How to Store Computer Vision Data Effectively
Biden’s AI Chip Export Restrictions: A Strategic Move to Counter Global Tech Threats Bad Likert Judge - Artificial Intelligence Diffusion
  • Technology

Biden’s AI Chip Export Restrictions: A Strategic Move to Counter Global Tech Threats

Do Son January 14, 2025 0
Read More Read more about Biden’s AI Chip Export Restrictions: A Strategic Move to Counter Global Tech Threats
Critical SAP Flaws Revealed: CVE-2025-0070 and CVE-2025-0066 with CVSS 9.9 Demand Immediate Action SAP Security Patches CVE-2026-27685 SAP Security Update CVE-2026-0488 CVE-2024-47578 - CVE-2025-0070 and CVE-2025-0066
  • Vulnerability

Critical SAP Flaws Revealed: CVE-2025-0070 and CVE-2025-0066 with CVSS 9.9 Demand Immediate Action

Do Son January 14, 2025 0
Read More Read more about Critical SAP Flaws Revealed: CVE-2025-0070 and CVE-2025-0066 with CVSS 9.9 Demand Immediate Action
Linux Kernel Privilege Escalation Vulnerability (CVE-2024-27397) Exploited: PoC Released CrackArmor AppArmor Vulnerabilities Linux Kernel UAF, Privilege Escalation PoC CVE-2024-27397 PoC
  • Linux
  • Vulnerability

Linux Kernel Privilege Escalation Vulnerability (CVE-2024-27397) Exploited: PoC Released

Do Son January 13, 2025 0
Read More Read more about Linux Kernel Privilege Escalation Vulnerability (CVE-2024-27397) Exploited: PoC Released
Zyxel Urges Patch Application for Privilege Escalation Vulnerability (CVE-2024-12398) CVE-2022-43389 - CVE-2024-12398 Zyxel UPnP Vulnerability CVE-2025-13942
  • Vulnerability

Zyxel Urges Patch Application for Privilege Escalation Vulnerability (CVE-2024-12398)

Do Son January 13, 2025 0
Read More Read more about Zyxel Urges Patch Application for Privilege Escalation Vulnerability (CVE-2024-12398)
CISA Warns of Active Exploitation of Critical Flaws in BeyondTrust and Qlik Sense GUARDIANWALL MailSuite Exploit CVE-2026-32661 FileZen Vulnerability CVE-2026-25108 Ivanti EPMM Vulnerability Dormant Backdoor Fortinet Authentication Bypass CVE-2026-24858 VMware vCenter Server Flaw CVE-2025-21590
  • Vulnerability

CISA Warns of Active Exploitation of Critical Flaws in BeyondTrust and Qlik Sense

Do Son January 13, 2025 0
Read More Read more about CISA Warns of Active Exploitation of Critical Flaws in BeyondTrust and Qlik Sense
Kernel Modules and Malicious Commands: Anatomy of the sysinitd Rootkit sysinitd rootkit
  • Linux
  • Malware

Kernel Modules and Malicious Commands: Anatomy of the sysinitd Rootkit

Do Son January 13, 2025 0
Read More Read more about Kernel Modules and Malicious Commands: Anatomy of the sysinitd Rootkit
Microsoft Unveils CVE-2024-44243: A macOS System Integrity Protection Bypass Through Kernel Extensions CVE-2024-44243
  • Vulnerability

Microsoft Unveils CVE-2024-44243: A macOS System Integrity Protection Bypass Through Kernel Extensions

Do Son January 13, 2025 0
Read More Read more about Microsoft Unveils CVE-2024-44243: A macOS System Integrity Protection Bypass Through Kernel Extensions
APT28’s New Espionage Campaign Uses Double-Tap Infection Chain BingX cyberattack FortiGate SSO Attacks Firewall Config Theft
  • Cyber Security
  • Malware

APT28’s New Espionage Campaign Uses Double-Tap Infection Chain

Do Son January 13, 2025 0
Read More Read more about APT28’s New Espionage Campaign Uses Double-Tap Infection Chain
CVE-2024-56511: Critical Authentication Bypass Vulnerability in DataEase CVE-2024-56511
  • Vulnerability

CVE-2024-56511: Critical Authentication Bypass Vulnerability in DataEase

Do Son January 13, 2025 0
Read More Read more about CVE-2024-56511: Critical Authentication Bypass Vulnerability in DataEase
CVE-2024-41787 (CVSS 9.8): Critical IBM DOORS Next Flaw Enables Remote Code Execution IBM CCA Vulnerability CVE-2025-13375 IBM Anthropic Partnership, AI Software Development watsonx Orchestrate, SQL injection CVE-2024-49803 - CVE-2024-41787 IBM Completes Acquisition HashiCorp
  • Vulnerability

CVE-2024-41787 (CVSS 9.8): Critical IBM DOORS Next Flaw Enables Remote Code Execution

Do Son January 13, 2025 0
Read More Read more about CVE-2024-41787 (CVSS 9.8): Critical IBM DOORS Next Flaw Enables Remote Code Execution
Unauthenticated Attackers Can Exploit Junos Vulnerabilities (CVE-2025-21598 & CVE-2025-21599) Junos OS Evolved CVE-2026-21902 Juniper Security Director, Critical Vulnerability Junos OS vulnerabilities - CVE-2025-21598 & CVE-2025-21599
  • Vulnerability

Unauthenticated Attackers Can Exploit Junos Vulnerabilities (CVE-2025-21598 & CVE-2025-21599)

Do Son January 13, 2025 0
Read More Read more about Unauthenticated Attackers Can Exploit Junos Vulnerabilities (CVE-2025-21598 & CVE-2025-21599)
LummaC2 Infostealer Malware Spreads via Crack Programs and Phishing LummaC2 Infostealer
  • Malware

LummaC2 Infostealer Malware Spreads via Crack Programs and Phishing

Do Son January 13, 2025 0
Read More Read more about LummaC2 Infostealer Malware Spreads via Crack Programs and Phishing
Opportunities and Challenges of Leveraging AI in Software Development AI in Software Development
  • Technique

Opportunities and Challenges of Leveraging AI in Software Development

Do Son January 13, 2025 0
Read More Read more about Opportunities and Challenges of Leveraging AI in Software Development
New macOS Exploit Revealed: PoC for CVE-2024-54498 Breaks Sandbox Security CVE-2024-54498 PoC
  • Vulnerability

New macOS Exploit Revealed: PoC for CVE-2024-54498 Breaks Sandbox Security

Do Son January 12, 2025 0
Read More Read more about New macOS Exploit Revealed: PoC for CVE-2024-54498 Breaks Sandbox Security
0-Click Vulnerability in Samsung S24 Devices: PoC Releases for CVE-2024-49415 CVE-2024-49415
  • Vulnerability

0-Click Vulnerability in Samsung S24 Devices: PoC Releases for CVE-2024-49415

Do Son January 12, 2025 0
Read More Read more about 0-Click Vulnerability in Samsung S24 Devices: PoC Releases for CVE-2024-49415
Aviatrix Controller RCE CVE-2024-50603 Exploited in the Wild: Cryptojacking and Backdoors Deployed CRussian Market, "Fly" (Flyded) hange Healthcare Cyberattack - CVE-2024-50603 Exploit
  • Vulnerability

Aviatrix Controller RCE CVE-2024-50603 Exploited in the Wild: Cryptojacking and Backdoors Deployed

Do Son January 12, 2025 0
Read More Read more about Aviatrix Controller RCE CVE-2024-50603 Exploited in the Wild: Cryptojacking and Backdoors Deployed
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-94504CVSS 7.2
    Ninja Forms 3.15.3 stores an anonymous non-RTE textarea value and renders it without safe HTML encoding in the...
    Admin intel📅 Updated: Oct 7, 2026
  • CVE-2026-93836CVSS 7.2
    The WPC Product Bundles for WooCommerce plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the \'qty\'...
    Admin intel📅 Updated: Oct 7, 2026
  • CVE-2026-21589CVSS 9.3
    This is a vulnerability in Bitbucket Data Center, Confluence Data Center, Jira Service Management Data Center, Jira Software...
    Admin intel📅 Updated: Oct 7, 2026
  • CVE-2026-61500CVSS 9.3
    Rejetto HFS 3.0.0 through 3.2.0 derives its session-cookie signing key from the non-cryptographic Math.random() generator and discloses outputs...
    Admin intel📅 Updated: Oct 7, 2026
  • CVE-2026-88779CVSS 8.7
    Vulnerability in NetScaler ADC and NetScaler Gateway. This issue affects ADC: before 14.1-73.41, before 13.1-64.28, before 14.1-73.41 FIPS,...
    Admin intelCISA KEV📅 Added to KEV: Oct 4, 2026📅 Updated: Oct 4, 2026
  • CVE-2026-102490CVSS 8.5
    All versions of Zammad including the latest alpha enable the local zammad user to escalate privileges to root.
    Admin intelCISA KEV📅 Added to KEV: Oct 2, 2026📅 Updated: Oct 2, 2026
  • CVE-2026-102489CVSS 8.7
    Zammad versions 6.3.0 to 6.5.4 are vulnerable a session hijack vulnerability that leads to remote code execution as...
    Admin intelCISA KEV📅 Added to KEV: Oct 2, 2026📅 Updated: Oct 2, 2026
  • CVE-2026-100382CVSS 10.0
    Improper Neutralization of Special Elements used in an OS Command (\'OS Command Injection\') vulnerability in Wikimedia Foundation Mediawiki...
    Admin intel📅 Updated: Oct 1, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-105324CVSS 9.2
    An HTTP header injection vulnerability in start-page-loader.cgi of ADM allows an unauthenticated remote attacker to read arbitrary files...
    📅 Updated: Oct 7, 2026
  • CVE-2026-79796CVSS 9.8
    Vulnerabilities have been identified in the affected interface of ClearPass Policy Manager that could potentially allow an unauthenticated...
    📅 Updated: Oct 7, 2026
  • CVE-2026-76464CVSS 9.6
    As part of Cisco's ongoing commitment to proactive security and product quality, the Cisco networking engineering team has...
    📅 Updated: Oct 7, 2026
  • CVE-2026-51862CVSS 9.1
    DB-GPT 0.8.0 contains directory traversal in skill_upload (packages/dbgpt-app/src/dbgpt_app/openapi/api_v1/agentic_data_api.py:40). A remote attacker can use the validated exploitation path to...
    📅 Updated: Oct 7, 2026
  • CVE-2026-51869CVSS 9.8
    DB-GPT v0.8.0 sandbox API silently falls back to LocalRuntime and executes code on host.
    📅 Updated: Oct 7, 2026
  • CVE-2026-76501CVSS 9.8
    A vulnerability in the Segment Routing over IPv6 (SRv6) Operation, Administration, and Maintenance (OAM) feature of Cisco NX-OS...
    📅 Updated: Oct 7, 2026
  • CVE-2026-76500CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality, the Cisco Application Policy Infrastructure Controller...
    📅 Updated: Oct 7, 2026
  • CVE-2026-102255CVSS 10.0
    A Pre-authentication SSRF vulnerability exists in the SMA1000 Appliance Work Place interface due to an unintended alternate access...
    📅 Updated: Oct 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.