Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Bitdefender GravityZone Small Business Security Review: Enterprise-Grade Protection Without the Enterprise Headache Bit
  • Reviews

Bitdefender GravityZone Small Business Security Review: Enterprise-Grade Protection Without the Enterprise Headache

Do Son March 3, 2025 0

Is Bitdefender GravityZone Small Business Security right for your company? Read the full review to find enterprise-level protection.

10 New Vulnerabilities Found in MediaTek Chipsets MediaTek Modem Vulnerabilities, January 2026 Security Bulletin MediaTek Vulnerabilities, Chipset Security CVE-2024-20103 & CVE-2024-20100 - CVE-2024-20154 - February 2025 Product Security Bulletin
  • Vulnerability

10 New Vulnerabilities Found in MediaTek Chipsets

Do Son March 3, 2025 0

Three vulnerabilities are flagged with a High severity rating: CVE-2025-20644, CVE-2025-20645, and CVE-2025-20646.

Windows Hyper-V Zero-Day CVE-2025-21333: PoC Drops, SYSTEM Access Exposed CVE-2025-21333 PoC exploit
  • Vulnerability

Windows Hyper-V Zero-Day CVE-2025-21333: PoC Drops, SYSTEM Access Exposed

Do Son March 2, 2025 0

Explore the CVE-2025-21333 PoC exploit revealing a zero-day vulnerability in Windows Hyper-V that allows SYSTEM privilege escalation.

CVE-2025-27154: Spotipy Vulnerability Exposes Spotify Auth Tokens Spotify data leak, Anna’s Archive CVE-2025-27154
  • Vulnerability

CVE-2025-27154: Spotipy Vulnerability Exposes Spotify Auth Tokens

Do Son March 2, 2025 0

Explore CVE-2025-27154 and its implications for Spotipy users. Learn how the vulnerability affects authentication security.

Extreme Networks Addresses Critical Security Vulnerabilities in HiveOS CVE-2025-27227
  • Vulnerability

Extreme Networks Addresses Critical Security Vulnerabilities in HiveOS

Do Son March 2, 2025 0

Extreme Networks has recently released security advisories to address three critical vulnerabilities affecting its IQ Engine (HiveOS) product line.
Webmin Vulnerability Allows Bypassing of SSL Certificate Authentication webmin authentication vulnerability
  • Vulnerability

Webmin Vulnerability Allows Bypassing of SSL Certificate Authentication

Do Son March 2, 2025 0

Webmin users must address the authentication vulnerability. Find out how it affects SSL and why you need to upgrade your system.

Lotus Blossom Hackers Target Southeast Asia with Sagerunex Backdoor Lotus Blossom group - Sagerunex backdoor
  • Cyber Security
  • Malware

Lotus Blossom Hackers Target Southeast Asia with Sagerunex Backdoor

Do Son March 2, 2025 0

Explore the Lotus Blossom group's persistent cyber attacks and learn how they utilize the Sagerunex backdoor for espionage.

Arista EOS Devices Vulnerable to Unauthorized Data Access and Configuration Changes (CVE-2025-1259 & CVE-2025-1260) (CVE-2025-1259 & CVE-2025-1260) Arista EOS CVE-2024-12378
  • Vulnerability

Arista EOS Devices Vulnerable to Unauthorized Data Access and Configuration Changes (CVE-2025-1259 & CVE-2025-1260)

Do Son March 2, 2025 0

Explore CVE-2025-1259 & CVE-2025-1260 and its impact on Arista EOS software vulnerabilities. Learn how unauthorized access could occur.
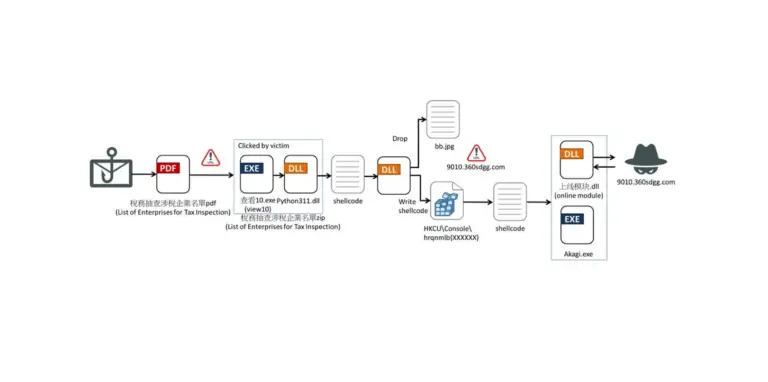
Phishing Campaign Delivers Winos 4.0: Keyloggers, UAC Bypass, and More Winos 4.0 malware
  • Malware

Phishing Campaign Delivers Winos 4.0: Keyloggers, UAC Bypass, and More

Do Son March 2, 2025 0

Explore the rise of Winos 4.0 malware targeting Taiwanese companies via phishing emails from the National Taxation Bureau.

CVE-2024-47051 (CVSS 9.1): Critical RCE and File Deletion Flaws Expose 200,000+ Organizations CVE-2024-47051
  • Vulnerability

CVE-2024-47051 (CVSS 9.1): Critical RCE and File Deletion Flaws Expose 200,000+ Organizations

Do Son March 2, 2025 0

Learn about CVE-2024-47051, a severe security vulnerability threatening Mautic users through Remote Code Execution and file deletion.

New Stealthy Backdoor “Squidoor” Linked to Chinese Threat Actor Squidoor backdoor
  • Cyber Security
  • Malware

New Stealthy Backdoor “Squidoor” Linked to Chinese Threat Actor

Do Son March 2, 2025 0

Explore Squidoor, the stealthy backdoor targeting organizations in Southeast Asia and South America. Stay informed on cybersecurity.

Critical LDAP Injection Flaw in IBM TXSeries for Multiplatforms CVE-2022-46337
  • Vulnerability

Critical LDAP Injection Flaw in IBM TXSeries for Multiplatforms

Do Son March 2, 2025 0

Learn about CVE-2022-46337 and its critical impact on IBM TXSeries. Discover recommended fixes and mitigation strategies.
3.2 Million Users Exposed by Malicious Browser Extensions Amazon Ads Blocker Affiliate Link Hijacking Malicious browser extensions
  • Malware

3.2 Million Users Exposed by Malicious Browser Extensions

Do Son March 2, 2025 0

Uncover the dangers of malicious browser extensions that threaten 3.2 million users and compromise browser security.

CVE-2025-27554 (CVSS 9.9): Critical Flaw Found in ToDesktop Electron App Bundler CVE-2025-27554
  • Vulnerability

CVE-2025-27554 (CVSS 9.9): Critical Flaw Found in ToDesktop Electron App Bundler

Do Son March 1, 2025 0

Explore CVE-2025-27554, a vulnerability in ToDesktop that allows unauthorized updates and command execution on build servers.

Fake CAPTCHA Phishing Campaign Impacts Over 1,150 Organizations Fake CAPTCHA Phishing Campaign
  • Malware

Fake CAPTCHA Phishing Campaign Impacts Over 1,150 Organizations

Do Son March 1, 2025 0

Learn about Fake CAPTCHA Phishing scams that target users through convincing PDFs. Protect your credit card information now.

Cellebrite Spyware Bypasses Android Lock Screens with Zero-Day Flaws Donot APT Group - Android zero-day
  • Android
  • Vulnerability

Cellebrite Spyware Bypasses Android Lock Screens with Zero-Day Flaws

Do Son March 1, 2025 0

Uncover the details of the Android zero-day vulnerabilities exploited by Cellebrite. Stay informed about security updates now.

CVE-2024-53675: PoC Exploit Released for HPE Insight RS XML Injection Flaw CVE-2024-53675 PoC exploit
  • Vulnerability

CVE-2024-53675: PoC Exploit Released for HPE Insight RS XML Injection Flaw

Do Son March 1, 2025 0

Robin's proof-of-concept (PoC) exploit demonstrates CVE-2024-53675 by hosting a malicious DTD file and sending a crafted payload

HostedScan Review: Proactive Vulnerability Management for a Bulletproof Digital Presence HostedScan Review
  • Reviews

HostedScan Review: Proactive Vulnerability Management for a Bulletproof Digital Presence

Do Son March 1, 2025 0

Explore our HostedScan review and discover how this platform offers automated security scanning to protect your business.

NordVPN Review: Your Shield in the Digital Wild West – Is It Worth the Hype? Windows-en-VPN
  • Reviews

NordVPN Review: Your Shield in the Digital Wild West – Is It Worth the Hype?

Do Son March 1, 2025 0

Is NordVPN the right choice for you? Read my detailed NordVPN Review to find out how it enhances your internet security.

NordPass Review: Effortless Password Security for a Stress-Free Digital Life NordPass Review
  • Reviews

NordPass Review: Effortless Password Security for a Stress-Free Digital Life

Do Son March 1, 2025 0

Read our comprehensive NordPass Review to find out why it stands out as a top choice for password management solutions.

Skype Paid Services to Shut Down—Users Must Migrate to Microsoft Teams by May 5 Skype Paid Services
  • Technology

Skype Paid Services to Shut Down—Users Must Migrate to Microsoft Teams by May 5

Do Son February 28, 2025 0

Explore the changes in Skype paid services and how they affect new users and existing subscribers after the transition.

CVE-2025-27110: ModSecurity Vulnerability Leaves Web Applications Exposed libmodsecurity3 Denial of Service WAF Security Vulnerability CVE-2025-27110 ModSecurity vulnerability, JSON DoS
  • Vulnerability

CVE-2025-27110: ModSecurity Vulnerability Leaves Web Applications Exposed

Do Son February 28, 2025 0

Understand the implications of CVE-2025-27110 on web application security and how it may allow attacks to bypass defenses.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-61949CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in Bookly Bookly bookly-responsive-appointment-booking-tool allows...
    📅 Updated: Nov 10, 2026
  • CVE-2026-13312CVSS 9.9
    A vulnerability that could allow an attacker to compromise a system.
    📅 Updated: Nov 10, 2026
  • CVE-2026-72868CVSS 9.9
    Dokploy is a free, self-hostable Platform as a Service (PaaS). Prior to 0.29.13, apps/dokploy/server/api/routers/destination.ts interpolates the accessKey, secretAccessKey,...
    📅 Updated: Nov 10, 2026
  • CVE-2026-6715CVSS 9.8
    IBM Concert 1.0 through 3.0.1.1 allows an attacker can supply crafted input that is incorporated into an operating...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17403CVSS 9.0
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to gain full...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17402CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17392CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to gain...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.