Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Cisco Warns of DoS Vulnerability in Nexus 3000 and 9000 Series Switches (CVE-2025-20111) Cisco CCX RCE and Java RMI Flaw CVE-2024-20458 - CVE-2025-20111 Cisco Smart Licensing Utility Flaw
  • Vulnerability

Cisco Warns of DoS Vulnerability in Nexus 3000 and 9000 Series Switches (CVE-2025-20111)

Do Son February 26, 2025 0

Learn how CVE-2025-20111 impacts Cisco Nexus switches. This vulnerability could lead to remote denial of service attacks.

CVE-2025-20029: Command Injection Flaw Discovered in F5 BIG-IP System, PoC Releases CVE-2025-20029
  • Vulnerability

CVE-2025-20029: Command Injection Flaw Discovered in F5 BIG-IP System, PoC Releases

Do Son February 26, 2025 0

Explore CVE-2025-20029, the command injection vulnerability in F5 BIG-IP that affects multiple versions of the system.

Phishing Attacks Targeting Higher Education Institutions on the Rise phishing-3390518_1280
  • Cyber Security

Phishing Attacks Targeting Higher Education Institutions on the Rise

Do Son February 26, 2025 0

Explore the rise of education phishing attacks targeting U.S. universities. Learn about common methods used by cybercriminals.

Material Theme Banned: Millions of VS Code Users Affected malicious Material Theme
  • Malware

Material Theme Banned: Millions of VS Code Users Affected

Do Son February 26, 2025 0

Learn about the removal of the malicious Material Theme from Visual Studio Marketplace due to the presence of harmful code.

CVE-2025-0514: LibreOffice Flaw Could Allow Unintentional Execution of Malicious Files CVE-2023-0950 & CVE-2025-0514
  • Vulnerability

CVE-2025-0514: LibreOffice Flaw Could Allow Unintentional Execution of Malicious Files

Do Son February 26, 2025 0

Discover the CVE-2025-0514 vulnerability in LibreOffice affecting versions before 24.8.5. Learn how to protect your system.

Weaponized Excel Documents: Ghostwriter’s New Tool of Cyber Espionage Ghostwriter campaign
  • Cyber Security

Weaponized Excel Documents: Ghostwriter’s New Tool of Cyber Espionage

Do Son February 26, 2025 0

Explore the latest Ghostwriter campaign targeting Ukrainian military and government with weaponized Excel documents.

Bybit Heist: $1.4B Ethereum Stolen in Safe{Wallet} Exploit Check Point VPN vulnerability exploited in the wild Check Point VPN exploit CVE-2026-50751 zero-day Checkmarx Breach Supply Chain Attack Ivanti EPMM RCE CVE-2026-1281 Modular DS Vulnerability CVE-2026-23550 D-Link RCE Vulnerability CVE-2026-0625 Christmas 2025 GreyNoise Campaign, Japan-Based Initial Access Broker React2Shell Zero-Day, APT Active Exploitation WordPress vulnerability, authentication bypass FreePBX, zero-day Trend Micro Apex One, Remote Code Execution BitoPro Hack, Crypto Theft UNC5337 - CVE-2022-47945 Safe{Wallet} hack Fortinet vulnerability, CVE-2024-21762, FortiGate attack Balloonfly, Play ransomware Ivanti EPMM CVE-2025-4427 and CVE-2025-4428
  • Cyber Security

Bybit Heist: $1.4B Ethereum Stolen in Safe{Wallet} Exploit

Do Son February 26, 2025 0

Uncover the details of the Safe{Wallet} hack involving Bybit and how hackers accessed the cryptocurrency vault.

“SafetyCore” Exposed: Google’s Secret AI on Your Phone Disable SafetyCore
  • Android
  • Data Leak

“SafetyCore” Exposed: Google’s Secret AI on Your Phone

Do Son February 26, 2025 0

Understand the implications of SafetyCore: Google’s new feature for local image scanning and related privacy concerns.

NVIDIA Issues Security Update for Jetson AGX Orin and IGX Orin to Patch UEFI Vulnerability – CVE-2024-0148 NVIDIA acquisition rumors NVIDIA AI Security AI Framework Vulnerabilities Nvidia 595.76 Hotfix NVIDIA Megatron Bridge vulnerability GPU vs ASIC AI battle NVIDIA Driver Vulnerability CVE-2025-33217 NVIDIA biggest TSMC customer 2026, NVIDIA vs Apple TSMC revenue share NVIDIA CUDA Toolkit CVE-2025-33228 Groq NVIDIA licensing deal, Jonathan Ross acquihire 2025 NeMo Code Injection, AI Framework RCE NVIDIA App Privilege Escalation, CVE-2025-23358 NVIDIA Security Update, DLS Vulnerability CVE-2025-23316 NVIDIA NVDebug, vulnerabilities NVIDIA Driver Vulnerabilities, vGPU Security Nvidia Jetson, UEFI Vulnerabilities CVE-2024-0130 - CVE-2024-0136 CVE-2024-0148 NVIDIA Driver Support, Windows 10 EOL
  • Vulnerability

NVIDIA Issues Security Update for Jetson AGX Orin and IGX Orin to Patch UEFI Vulnerability – CVE-2024-0148

Do Son February 26, 2025 0

NVIDIA's security update resolves CVE-2024-0148, which affects UEFI firmware in Jetson devices. Protect your hardware now.
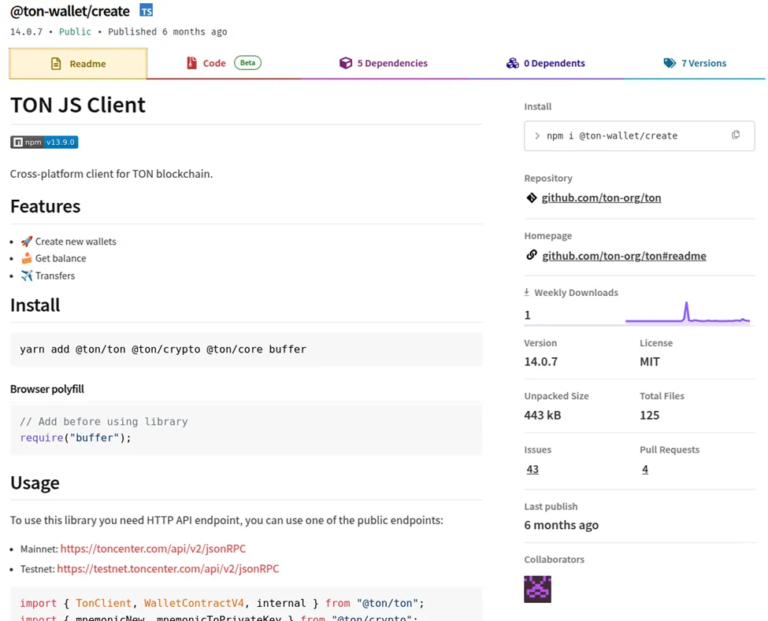
Malicious npm Package Targets TON Wallet Users, Stealing Cryptocurrency Keys TON Wallet
  • Malware

Malicious npm Package Targets TON Wallet Users, Stealing Cryptocurrency Keys

Do Son February 26, 2025 0

Beware of the TON Wallet threat. A malicious npm package has stolen mnemonic phrases from developers in the TON blockchain.

CVE-2025-0475 & CVE-2025-0555: GitLab’s High-Risk Patch Now CVE-2024-4835 CVE-2025-0475 & CVE-2025-0555
  • Vulnerability

CVE-2025-0475 & CVE-2025-0555: GitLab’s High-Risk Patch Now

Do Son February 26, 2025 0

Understand the implications of CVE-2025-0475 & CVE-2025-0555. GitLab warns of severe vulnerabilities requiring immediate action.

Outdated and Unblocked: Legacy Driver Vulnerability Exploited in Widespread Attack Legacy Driver Vulnerability
  • Cyber Security
  • Vulnerability

Outdated and Unblocked: Legacy Driver Vulnerability Exploited in Widespread Attack

Do Son February 26, 2025 0

Uncover the threat of Legacy Driver Vulnerability in cyberattacks. Learn how attackers exploit outdated drivers to bypass security.

Europe & LatAm Alert: Android Trojan TgToxic’s Expanding Attack Android trojan TgToxic
  • Malware

Europe & LatAm Alert: Android Trojan TgToxic’s Expanding Attack

Do Son February 26, 2025 0

Explore the latest updates on TgToxic, the Android banking trojan evolving with enhanced evasion techniques and broader targets.

EncryptHub Exposed: 600+ Targets Hit by LARVA-208 threat actor, LARVA-208, also known as EncryptHub
  • Cyber Security

EncryptHub Exposed: 600+ Targets Hit by LARVA-208

Do Son February 26, 2025 0

Learn about LARVA-208, the new threat actor using sophisticated social engineering tactics like smishing and vishing.

Auto-Color: New Evasive Linux Malware Targeting Governments and Universities XZ backdoor, Docker Hub MIFARE classic backdoor C++/CLI IIS Backdoor
  • Malware

Auto-Color: New Evasive Linux Malware Targeting Governments and Universities

Do Son February 26, 2025 0

Learn about Auto-Color, a stealthy Linux backdoor targeting government and educational institutions across continents.

Quantum Leap: Researchers Achieve Unprecedented Speed and Range in Secure Direct Communication quantum-centric supercomputing, IBM-AMD partnership quantum secure direct communication
  • Technology

Quantum Leap: Researchers Achieve Unprecedented Speed and Range in Secure Direct Communication

Do Son February 26, 2025 0

Explore the groundbreaking advancements in quantum secure direct communication and their impact on secure data transmission.

Silver Fox APT Targets Philips DICOM Viewers in Healthcare Espionage Campaign FortiClient EMS exploitation Cisco FIRESTARTER Backdoor Arcane Door Campaign Dell RecoverPoint Zero-Day UNC6201 Espionage Notepad++ Compromise Supply Chain Attack Magento SessionReaper CVE-2025-54236 ShadowRay 2.0, AI-Generated Malware WordPress Auth Bypass, CVE-2025-5947 Exploited EcoStruxure Vulnerabilities, Industrial Control System UNC5820 - CVE-2014-2120 - CVE-2021-44207
  • Cyber Security

Silver Fox APT Targets Philips DICOM Viewers in Healthcare Espionage Campaign

Do Son February 26, 2025 0

Discover the Healthcare Espionage Campaign by Silver Fox targeting Philips DICOM viewers with malware and keyloggers.

Gemini Code Assist: Google’s AI Coding Power for All Gemini Code Assist Android free electrician training, AI energy demand
  • Technology

Gemini Code Assist: Google’s AI Coding Power for All

Do Son February 25, 2025 0

Explore Gemini Code Assist, the new AI-powered coding assistant by Google, designed to enhance your programming experience.

CVE-2024-12084 & CVE-2024-12085: Rsync Flaws Allow Hackers to Take Over Servers, PoC Published Rsync Vulnerability Use-After-Free CVE-2022-29154 & CVE-2024-12084 CVE-2024-120845 PoC
  • Vulnerability

CVE-2024-12084 & CVE-2024-12085: Rsync Flaws Allow Hackers to Take Over Servers, PoC Published

Do Son February 25, 2025 1

Explore CVE-2024-12084 PoC and learn about critical vulnerabilities in Rsync that could enable remote code execution and data leaks.

SoaPy: A New Tool for Stealthy Active Directory Enumeration via ADWS SoaPy Active Directory Enumeration Tool
  • Open Source Tool

SoaPy: A New Tool for Stealthy Active Directory Enumeration via ADWS

Do Son February 25, 2025 0

Unlock the power of the Active Directory Enumeration Tool with SoaPy, a stealthy solution for AD enumeration from Linux.

CISA Flags Actively Exploited Zimbra (CVE-2023-34192) and Microsoft (CVE-2024-49035) Vulnerabilities CISA KEV Catalog Active Exploitation CVE-2023-33063 - CVE-2023-34192 and CVE-2024-49035
  • Vulnerability

CISA Flags Actively Exploited Zimbra (CVE-2023-34192) and Microsoft (CVE-2024-49035) Vulnerabilities
Do Son February 25, 2025 0

The newly flagged flaws, CVE-2023-34192 and CVE-2024-49035, target widely used platforms, posing significant threats to both public and private sector entities

$500 Bitcoin Demand: LCRYX Ransomware Cripples Windows LCRYX ransomware
  • Malware

$500 Bitcoin Demand: LCRYX Ransomware Cripples Windows

Do Son February 25, 2025 0

Learn about LCRYX ransomware, a malware threat that encrypts files and demands Bitcoin for decryption. Stay informed and protected.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-61949CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in Bookly Bookly bookly-responsive-appointment-booking-tool allows...
    📅 Updated: Nov 10, 2026
  • CVE-2026-13312CVSS 9.9
    A vulnerability that could allow an attacker to compromise a system.
    📅 Updated: Nov 10, 2026
  • CVE-2026-72868CVSS 9.9
    Dokploy is a free, self-hostable Platform as a Service (PaaS). Prior to 0.29.13, apps/dokploy/server/api/routers/destination.ts interpolates the accessKey, secretAccessKey,...
    📅 Updated: Nov 10, 2026
  • CVE-2026-6715CVSS 9.8
    IBM Concert 1.0 through 3.0.1.1 allows an attacker can supply crafted input that is incorporated into an operating...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17403CVSS 9.0
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to gain full...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17402CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17392CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to gain...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.